 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone execution.

PwnKit PoC for Polkit pkexec CVE-2021-4034
Based on the PoC by blasty
blasty-vs-pkexec.c
For PwnKit details see the blog poet at Qualys PwnKit: Local Privilege Escalation Vulnerability Discovered in polkit’s pkexec (CVE-2021-4034)
This repo is a nim based PwnKit PoC. The payload shared library is embedded in the executable, so gcc is not required on the target.
To get set up with a nim enviroment, see HuskyHacks post. Nim on the Attack: Process Injection Using Nim and the Windows API
Issues and PRs welcome.
Clone the repo and run make to create the navipwnkit executable.
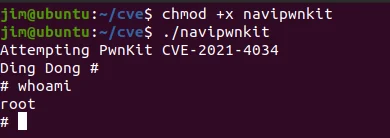
Copy the executable to the target and run to get root.