 mrtuxx/socialpwned
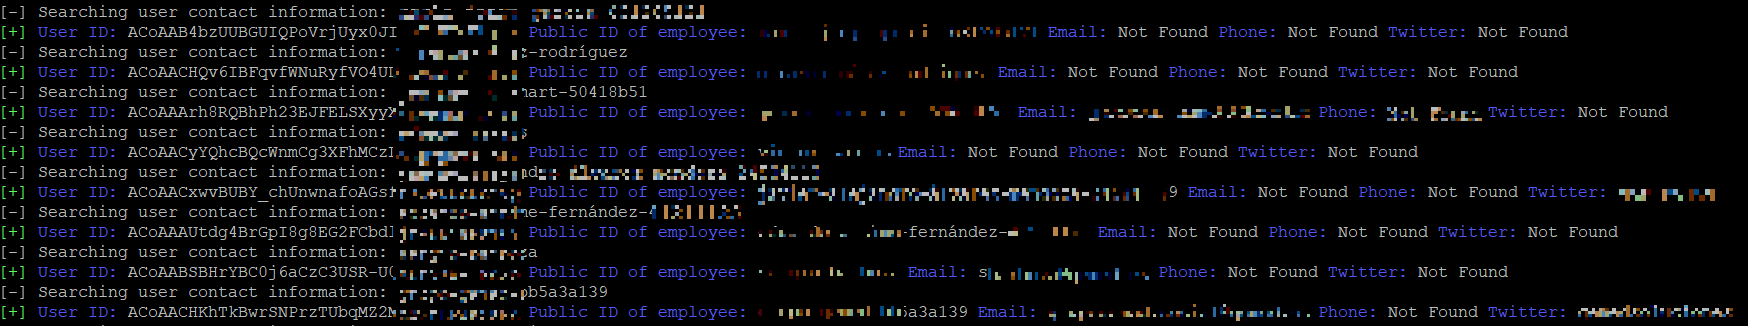
SocialPwned is an OSINT tool that allows to get the emails, from a target, published in social networks such as Instagram, Linkedin and Twitter to find possible credentials leaks in PwnDB or Dehashed and obtain Google account information via GHunt.



SocialPwned is an OSINT tool that allows to get the emails, from a target, published in social networks like Instagram, Linkedin and Twitter to find the possible credential leaks in PwnDB or Dehashed and obtain Google account information via GHunt.
The purpose of this tool is to facilitate the search for vulnerable targets during the phase of Footprinting in an Ethical Hacking. It is common for employees of a company to publish their emails in social networks, either professional or personal, so if these emails have their credentials leaked, it is possible that the passwords found have been reused in the environment to be audited. If it’s not the case, at least you would have an idea of the patterns that follow this target to create the passwords and be able to perform other attacks with a higher level of effectiveness.
SocialPwned uses different modules:
$ service docker start
$ docker pull mrtuxx/socialpwned
$ docker run -v $(pwd)/credentials.json:/socialpwned/credentials.json -v $(pwd)/output:/socialpwned/output -it mrtuxx/socialpwned socialpwned.py --credentials credentials.json --help
NOTE: You will need to have the docker service correctly installed.
The installation of Tor depends on your system. On a Debian:
$ sudo apt-get install tor
$ /etc/init.d/tor start
Clone the repository using Git:
$ git clone https://github.com/MrTuxx/SocialPwned.git
$ cd SocialPwned
$ sudo pip3 install --user --upgrade git+https://github.com/twintproject/twint.git@origin/master#egg=twint
$ sudo pip3 install -r requirements.txt
$ sudo python3 socialpwned.py --credentials credentials.json --help
For the GHunt module to work correctly you must follow these steps:
To make use of the Instagram and Linkedin features you need to have an account created on each of the social networks. The credentials must be indicated in a JSON file:
{
    "instagram":{
        "username":"username",
        "password":"password"
    },
    "linkedin":{
        "email":"email",
        "password":"password"
    },
    "ghunt":{
        "SID":"SID",
        "SSID":"SSID",
        "APISID":"APISID",
        "SAPISID":"SAPISID",
        "HSID":"HSID"
    },
    "dehashed":{
         "email":"email",
         "apikey":"apikey"
    }
}
NOTE: The cookies necessary for the GHunt module to work can be obtained by following the steps explained here.
usage: socialpwned.py [-h] --credentials CREDENTIALS [--pwndb] [--tor-proxy PROXY] [--instagram] [--info QUERY]
                      [--location LOCATION_ID] [--hashtag-ig QUERY] [--target-ig USERNAME] [--search-users-ig QUERY]
                      [--my-followers] [--my-followings] [--followers-ig] [--followings-ig] [--linkedin]
                      [--company COMPANY_ID] [--search-companies QUERY] [--employees] [--my-contacts]
                      [--user-contacts USER_ID] [--search-users-in QUERY] [--target-in USERNAME] [--add-contacts]
                      [--add-a-contact USER_ID] [--twitter] [--limit LIMIT] [--year YEAR] [--since DATE]
                      [--until DATE] [--profile-full] [--all-tw] [--target-tw USERNAME] [--hashtag-tw USERNAME]
                      [--followers-tw] [--followings-tw] [--ghunt] [--email-gh [email protected]] [--dehashed]
                      [--email-dh [email protected]]
If you do a pull of the docker image you should run:
docker run -v $(pwd)/<YOUR CREDENTIALS JSON FILE>:/socialpwned/credentials.json -v $(pwd)/output:/socialpwned/output -it mrtuxx/socialpwned socialpwned.py --credentials credentials.json <COMMANDS>
Keep Linkedin and Instagram sessions in a browser to resolve possible blocks. Interact in a normal way.
Before trying to get all the emails of an organization's employees on Linkedin make sure you have a wide network of contacts, friends in common and some employees added to your network. Many times you can't see a contact's information if they are not in your network.
Try not to perform massive searches to avoid being blocked.
Combine the modules when it is a specific target or will not handle a large amount of information, otherwise it may fail or you will be blocked.
Each time SocialPwned is run, a directory with the following format will be generated:
