
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/mazx0p/cve-2021-41773
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubmazx0p/cve-2021-41773

CVE-2021-41773

Proof-of-concept exploit for CVE-2021-41773, enabling remote code execution and CGI-bin path traversal on Apache HTTP Server 2.4.49. Includes Docker-based vulnerable environment setup and automated exploitation script.

View Repository
114 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-41773

Build Status

I have developed a POC of CVE-2021-41773 , RCE + cgi-bin path traversal

NOTE :

TESTED ON APACHE2 2.4.49

You can pulled vuln Apache2 2.4.49 directly from Docker

$ sudo docker pull blueteamsteve/cve-2021-41773:no-cgid
$ sudo docker run -dit -p 80:80 blueteamsteve/cve-2021-41773:no-cgid
http://localhost:80

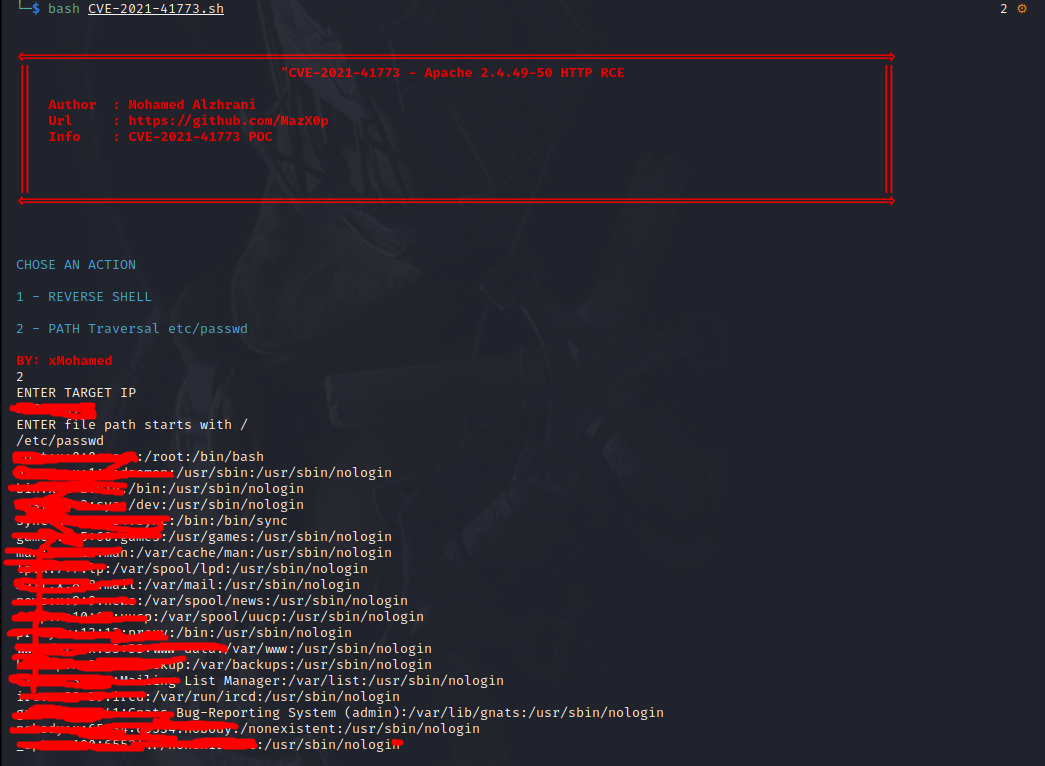
path traversal

poc3

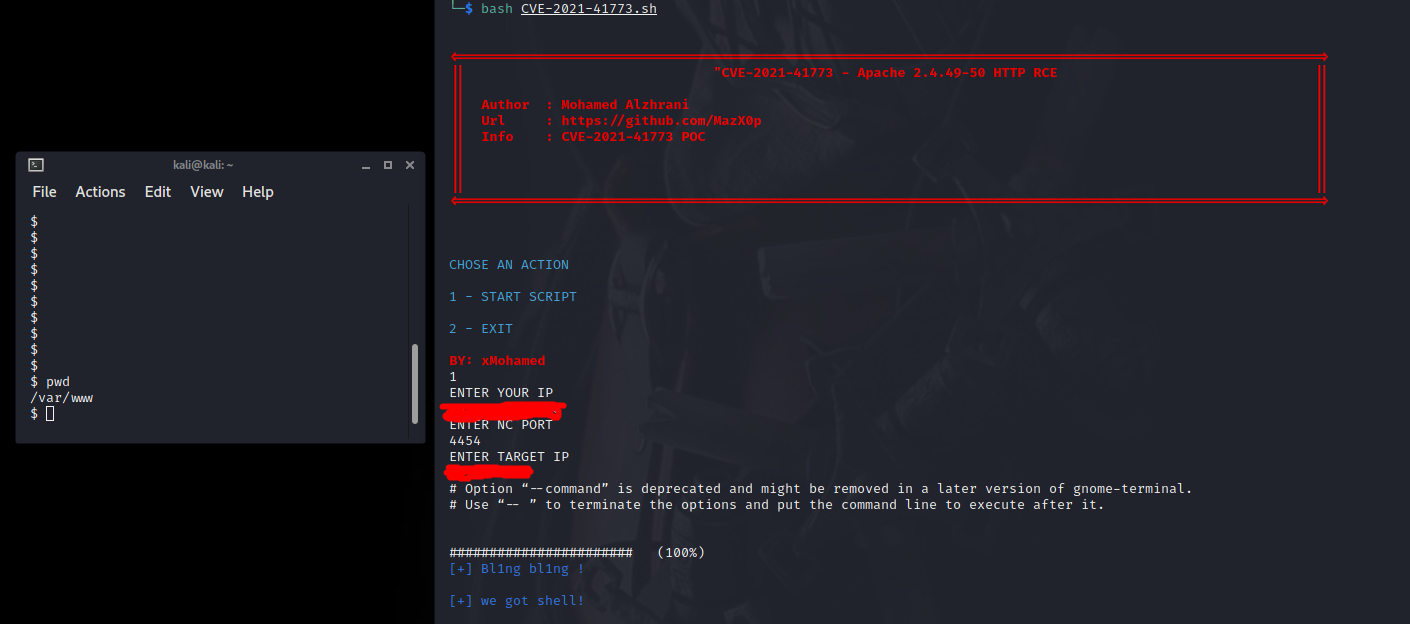
RCE

apache poc

Requirement

  • gnome-terminal

TO Download it:

  • sudo apt-get install gnome-terminal

USAGE

$ git clone https://github.com/MazX0p/CVE-2021-41773.git
$ cd CVE-2021-41773
$ bash CVE-2021-41773.sh
NameREADME
CVECVE
ME!Linkedin

License

MIT

Free Software, Hell Yeah!

Download Tool