
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-1315 — Proof-of-concept PowerShell exploit for CVE-2019-1315, a Windows Error Reporting Manager arbitrary file move elevation of privilege vulnerability, tested on Windows 10 1903. | Kitploit
Tools/GitHubGitHub/mayter/cve-2019-1315
Privilege EscalationVulnerability AnalysisExploitationBinary Exploitation
GitHubmayter/cve-2019-1315

CVE-2019-1315

Proof-of-concept PowerShell exploit for CVE-2019-1315, a Windows Error Reporting Manager arbitrary file move elevation of privilege vulnerability, tested on Windows 10 1903.

View Repository
10476 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Windows Error Reporting Manager arbitrary file move Elevation of Privilege

Details: https://offsec.almond.consulting/windows-error-reporting-arbitrary-file-move-eop.html

You will need the NtApiDotNet library to run it, as well as a valid Report.wer file, both to be placed in the same directory as the poc.ps1 script.

To generate a WER report file, you can run the [Environment]::FailFast('Error') command in PowerShell, and look for the report file in %ProgramData%\Microsoft\Windows\WER\ReportQueue.

The script can be run with the following command:

powershell -exec bypass -C ". .\poc.ps1; Test-Exploit"

Tested on Windows 10 1903.

CVE-2019-1315

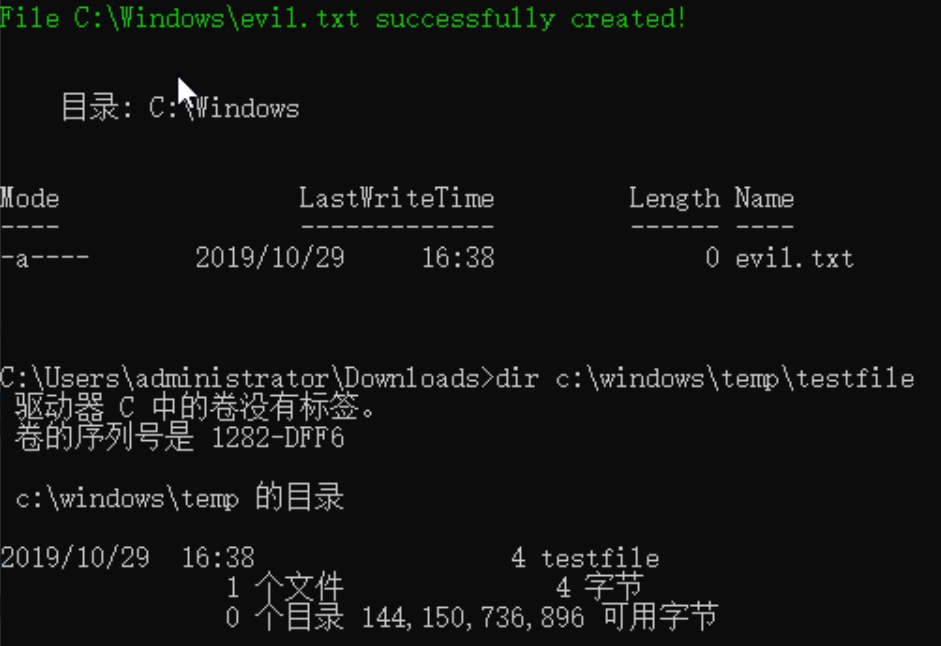
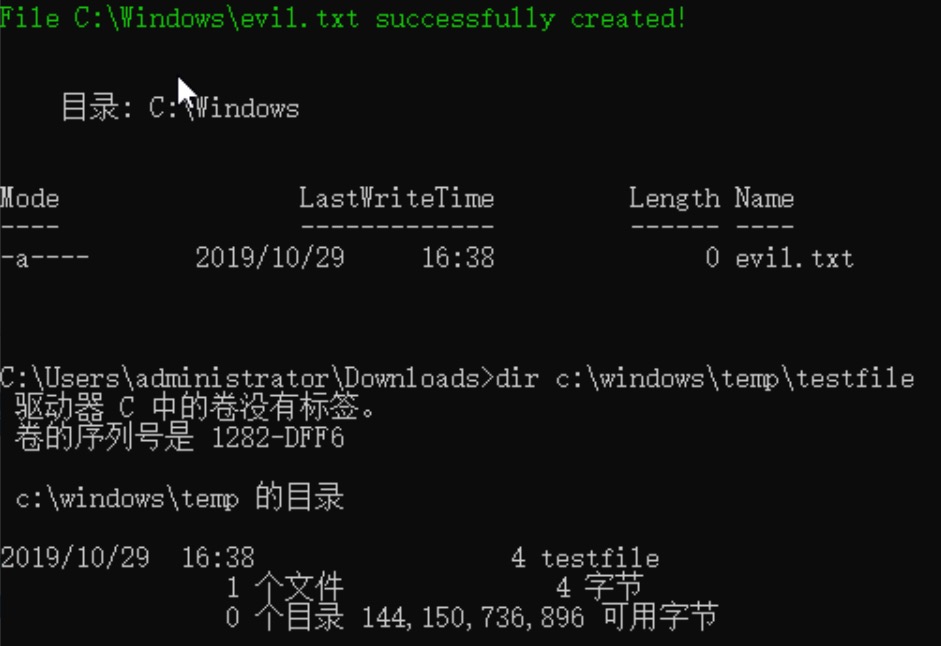
我编译了NtApiDotNet.dll文件。 本地测试成功。

Download Tool