
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-9978 — Docker-based lab environment to simulate and exploit CVE-2019-9978, a remote code execution vulnerability in WordPress Social Warfare plugin versions below 3.5.3. | Kitploit
Tools/GitHubGitHub/mahajian/cve-2019-9978
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubmahajian/cve-2019-9978

CVE-2019-9978

Docker-based lab environment to simulate and exploit CVE-2019-9978, a remote code execution vulnerability in WordPress Social Warfare plugin versions below 3.5.3.

View Repository
82 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2019-9978

WordPress Plugin Social Warfare RCE Vulnerability < 3.5.3 🐞

Minimal simulated from vulnerable plugin and exploit it 🥰

Installation Of Vulnerable Plugin

Install dependencies:

docker-compose build

Start vulnerable and attacker server containers

docker-compose up

or

docker-compose up -d
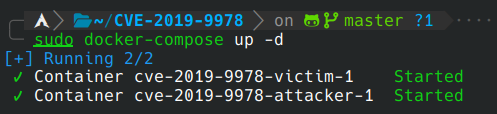
docker-compose up -d

Stop servers

docker-compose down

docker-compose down

Exploit

Install exploit dependencies:

pip install -r requirements.txt

Execute:

python3 exploit.py

exploit

Enjoy 💀

Download Tool