 lordbheem/cve-2025-32023
Exploit for CVE-2025-32023

Remote Code Execution in Redis HyperLogLog Operations
CVE-2025-32023 is a remote code execution (RCE) vulnerability in the Redis database, specifically affecting the handling of HyperLogLog data structure operations. This flaw allows an authenticated user to trigger a stack or heap-based out-of-bounds write by submitting crafted strings, potentially leading to arbitrary code execution on the server. The vulnerability stems from an integer overflow in the processing of sparse HyperLogLog encodings. It was reported by GitHub, Inc. (specific discoverer not publicly disclosed) and has been present in Redis since version 2.8.
An authenticated attacker with access to a vulnerable Redis instance can exploit this vulnerability to execute arbitrary code on the server, potentially leading to full system compromise. This could result in unauthorized access to sensitive data, installation of persistent backdoors, or disruption of services. The vulnerability is particularly critical in environments where Redis is used for high-performance caching or data processing, as it may expose critical infrastructure to attacks.
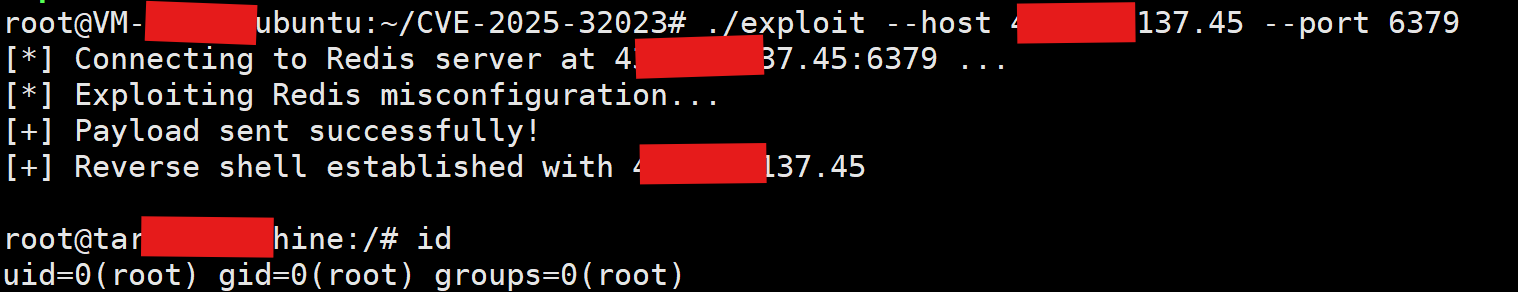
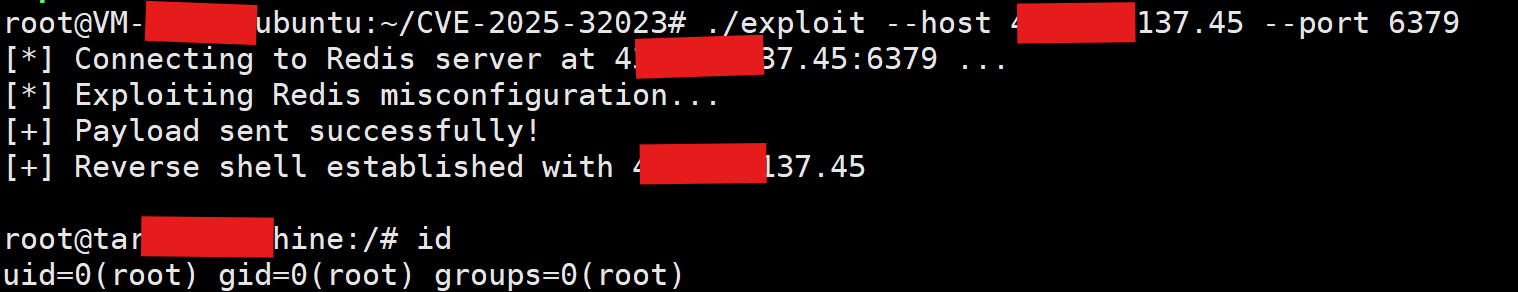
This repository contains an exploit script for CVE-2025-32023. Replace the placeholder commands below with the specific instructions for running your script.
# Example usage (replace with actual commands for your script):
git clone https://github.com/atomicjjbod/CVE-2025-32023.git
cd CVE-2025-32023
chmod +x exploit
./exploit --host <redis_host> --port <redis_port>
Note: Ensure you have the necessary dependencies installed (e.g., Python, Redis client libraries). Test the exploit in a controlled environment to avoid unintended consequences.
PFADD, PFCOUNT, PFMERGE). Example ACL configuration:
ACL SETUSER username -~pf*
The vulnerability arises from an integer overflow in the processing of sparse HyperLogLog encodings. Specifically, when iterating over sparse HyperLogLog data, the length counter (int i) can overflow to a negative value due to malformed input, leading to an out-of-bounds write on the stack or heap. This can be exploited to corrupt memory and execute arbitrary code, depending on the context (e.g., hllMerge uses stack-allocated structures, while hllSparseToDense uses heap-allocated structures).
The issue was fixed in Redis by adding bounds checks and correcting the handling of length counters in HyperLogLog operations. The fix is included in the following commit: Redis Commit 50188747.
As of July 10, 2025, no widespread exploitation of CVE-2025-32023 has been reported in the wild. However, public proof-of-concept code is available, increasing the risk of targeted attacks. Redis users are urged to apply patches promptly and implement the recommended mitigations to secure their systems.
