
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Agent-Tesla-APC-Injection-Token-Manipulation-Registry-Persistence-Analysis — "Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence. Includes NtQueueApcThread, NtProtectVirtualMemory, and full payload extraction." | Kitploit
Tools/GitHubGitHub/kaandemir993/agent-tesla-apc-injection-token-manipulation-registry-persistence-analysis
Privilege EscalationPersistence MechanismsReverse EngineeringData ExfiltrationMalware AnalysisBinary AnalysisLearning & Education
GitHubkaandemir993/agent-tesla-apc-injection-token-manipulation-registry-persistence-analysis

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Agent-Tesla-APC-Injection-Token-Manipulation-Registry-Persistence-Analysis

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence. Includes NtQueueApcThread, NtProtectVirtualMemory, and full payload extraction."

View Repository
32241 month agoNot yet reviewed

1. Native API & APC Injection

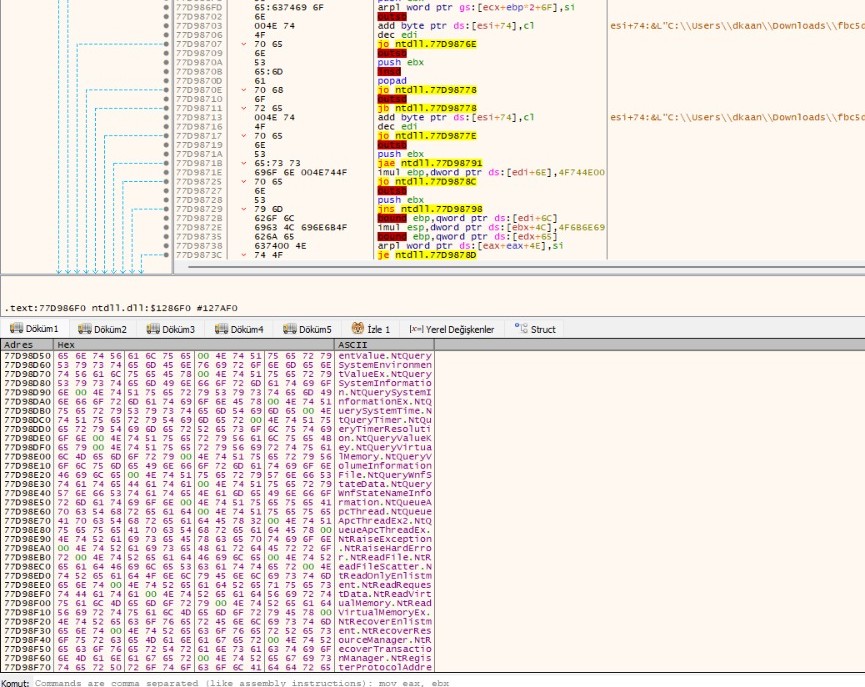
The x64dbg memory dump reveals that Agent Tesla uses Native API (NT API) calls for low-level operations, including APC (Asynchronous Procedure Call) injection.

Key Functions Observed:

  • NtQueueApcThread – Injects code into a target thread via APC.
  • NtReadVirtualMemory – Reads memory from other processes.
  • NtQuerySystemInformation – Collects system information.
  • NtCreateThreadEx (likely present) – Creates threads for execution.
Why This Matters:

  • Evasion: Native APIs bypass user-mode hooks.
  • Injection: APC injection is stealthy and hard to detect.
  • Data Theft: Memory reading allows extraction of credentials and cookies.

Visual Reference:

Agent Tesla Native API & APC Injection x64dbg hex dump showing NtQueueApcThread, NtReadVirtualMemory, and NtQuerySystemInformation.

2. Token Manipulation & Memory Protection

The x64dbg dump reveals that Agent Tesla uses token manipulation and memory protection functions to gain elevated privileges and execute its payload.

Key Functions Observed:

  • NtOpenThreadToken – Opens thread tokens for privilege escalation.
  • NtProtectVirtualMemory – Changes memory page protection for payload execution.
  • NtOpenTimer – Opens timer objects for scheduled tasks.
  • NtPowerInformation – Queries power state (anti-sandbox).
  • NtQueryBootEntry – Retrieves boot information.

Why This Matters:

  • Privilege Escalation: Token manipulation allows the malware to run with higher privileges.
  • Payload Execution: Memory protection changes enable code injection.
  • Evasion: Anti-sandbox techniques help avoid detection.

Visual Reference:

Agent Tesla Token Manipulation & Memory Protection x64dbg hex dump showing NtOpenThreadToken, NtProtectVirtualMemory, and NtOpenTimer.

3. Process/Thread Termination & Driver Management

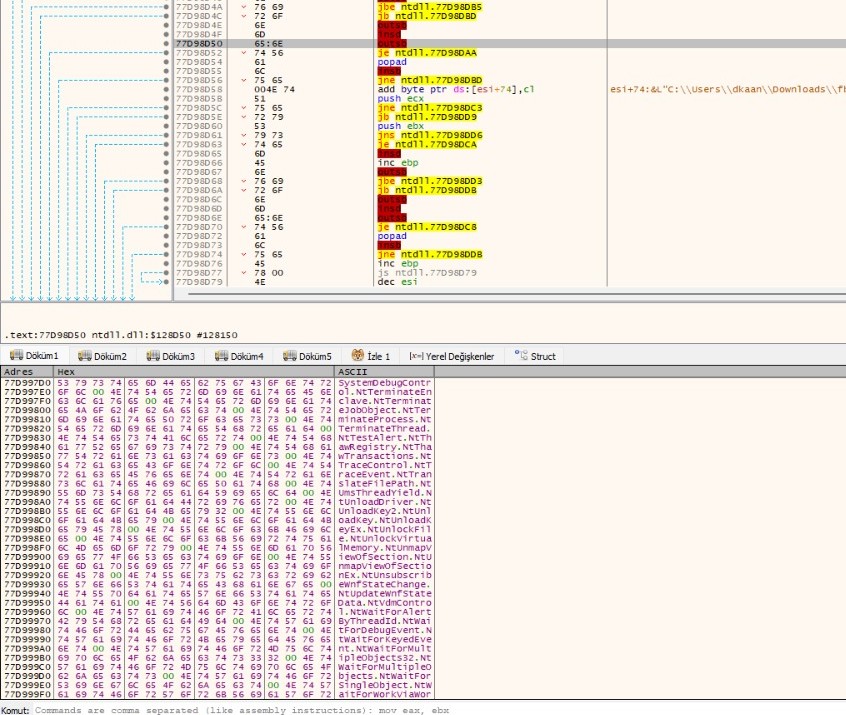
The x64dbg dump reveals that Agent Tesla can terminate processes and threads, as well as load/unload kernel drivers.

Key Functions Observed:

  • NtTerminateProcess – Terminates processes (e.g., EDR/AV).
  • NtTerminateThread – Terminates threads.
  • NtUnloadDriver – Unloads a kernel driver.
  • NtUnmapViewOfSection – Unmaps memory sections (cleans traces).
  • NtWaitForSingleObject – Synchronizes thread/process operations.
Why This Matters:

  • EDR/AV Termination: The malware can disable security tools.
  • Driver Management: Loading/unloading drivers indicates deep system access.
  • Trace Cleaning: Unmapping memory sections helps evade detection.

Visual Reference:

Agent Tesla Process Termination & Driver Management x64dbg hex dump showing NtTerminateProcess, NtUnloadDriver, and NtUnmapViewOfSection.

4. Payload – Clipboard, File & Memory Management

The .text section of the memory dump contains the full payload of Agent Tesla, confirming its capabilities as a comprehensive info-stealer.

Key API Categories:

  • Clipboard Stealing: OpenClipboard, SetClipboardData, EmptyClipboard
  • Window & UI Manipulation: CreateWindowExW, ShowWindow, SetWindowTextW
  • File System Access: DeleteFileW, FindFirstFileW, ReadFile
  • Memory & DLL Management: GlobalAlloc, LoadLibraryExW, GetModuleHandleW
  • Graphics & Display: CreateFontIndirectW, CreateBrushIndirect, SelectObject

Why This Matters:

  • Data Theft: The APIs cover clipboard, files, and system information.
  • Evasion: By loading DLLs dynamically, the malware avoids static detection.
  • Comprehensive Control: The malware can read, write, delete, and execute files, as well as manage processes and threads.

Visual Reference:

Agent Tesla Payload – Clipboard, File & Memory APIs Binary Ninja view of the .text section showing the full list of Windows APIs used by Agent Tesla.

5. Registry, Token & COM Operations

The extended payload list reveals Agent Tesla's ability to manipulate the Windows Registry, manage tokens, and interact with COM objects.

Key API Categories:

  • Registry: RegOpenKeyExW, RegSetValueExW, RegDeleteKeyW – Persistence and configuration.
  • Token Manipulation: OpenProcessToken, AdjustTokenPrivileges – Privilege escalation.
  • COM/OLE: CoCreateInstance, OleInitialize – Windows system interaction.
  • Shell: SHFileOperationW, ShellExecuteExW, SHBrowseForFolderW – File and folder operations.

Why This Matters:

  • Persistence: Registry manipulation allows the malware to run on startup.
  • Privilege Escalation: Token manipulation enables higher system access.
  • System Interaction: COM and Shell operations allow deep system control.

Visual Reference:

Agent Tesla Registry, Token & COM APIs Binary Ninja view showing Registry, Token, and COM-related APIs.

Conclusion

This analysis uncovered Agent Tesla, a .NET-based info-stealer that combines advanced injection techniques, token manipulation, and registry persistence.

Key Takeaways:

  • APC Injection: Uses NtQueueApcThread for stealthy process injection.
  • Token Manipulation: Employs NtOpenThreadToken and AdjustTokenPrivileges for privilege escalation.
  • Registry Persistence: RegSetValueExW for startup persistence.
  • Payload Extraction: The .text section contained a comprehensive API list, confirming its info-stealer nature.

Detection Recommendations:

  • Monitor for NtQueueApcThread and NtReadVirtualMemory calls.
  • Watch for NtOpenThreadToken and AdjustTokenPrivileges for privilege escalation attempts.
  • Detect RegSetValueExW and RegOpenKeyExW from unusual processes.
  • Monitor .text sections for large API lists (e.g., USER32.dll, KERNEL32.dll, ADVAPI32.dll).

Sample Download

The analyzed Agent Tesla sample is available on MalwareBazaar for those who wish to conduct their own analysis:

🔗 Agent Tesla Sample on MalwareBazaar

Tools Used: x64dbg, Binary Ninja, Process Hacker

Download Tool