

Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32种协议(ICMP\NBT\DNS\MAC\SMB\WMI\SSH\HTTP\HTTPS\Exchange\mssql\FTP\RDP)或方法快速获取目标网络存活主机IP、计算机名、工作组、共享资源、网卡地址、操作系统版本、网站、子域名、中间件、开放服务、路由器、交换机、数据库、打印机等,大量高危漏洞检测模块MS17010、Zimbra、Exchange
 k8gege/ladon



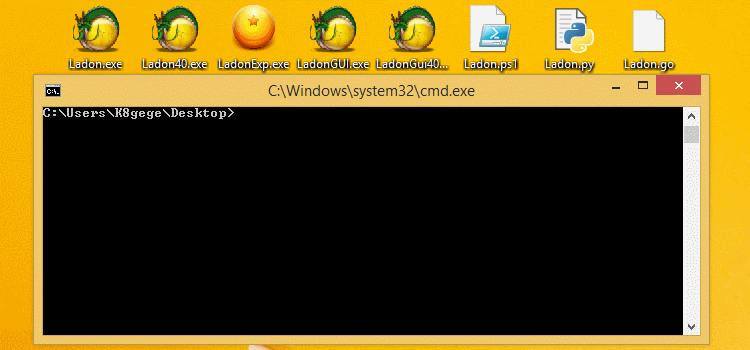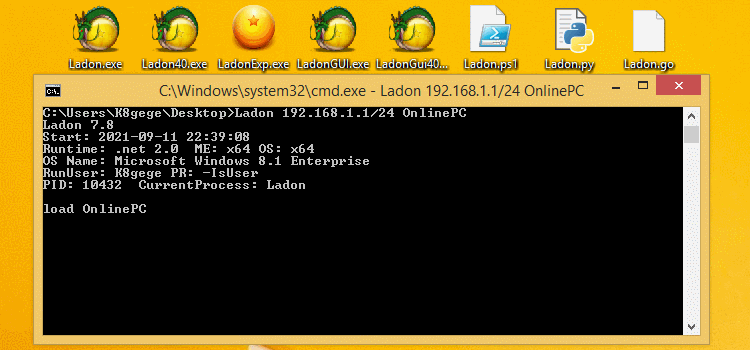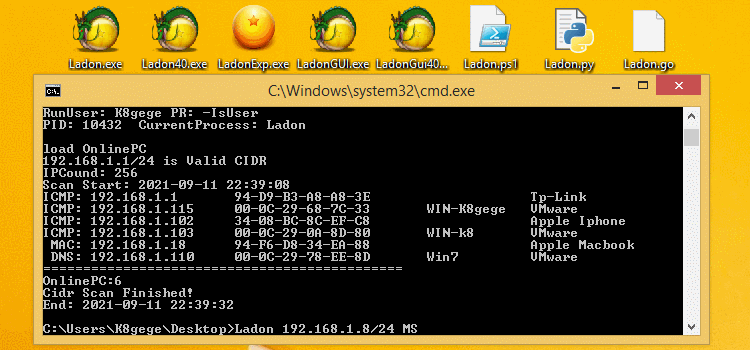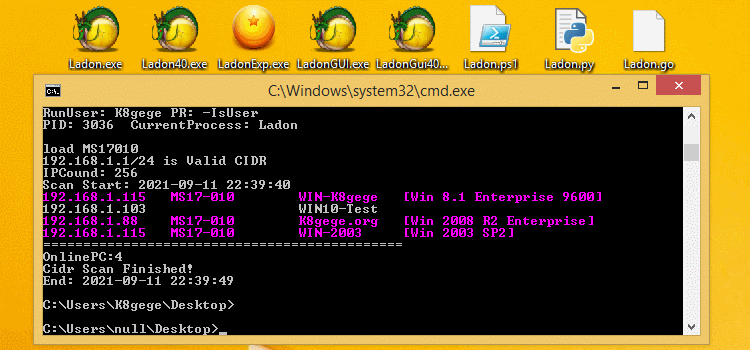
Ladon is a large-scale intranet penetration scanner, domain penetration, and lateral movement tool, featuring PowerShell modules, Cobalt Strike plugins, memory loading, and fileless scanning. It includes port scanning, service identification, network asset detection, password auditing, high-risk vulnerability detection, vulnerability exploitation, password retrieval, and one-click GetShell. It supports batch scanning of A/B/C segments and cross-subnet scanning, as well as URL, host, and domain list scanning. Version 12.2 includes 262 functional modules, with the network asset detection module supporting 30+ protocols (ICMP, NBT, DNS, MAC, SMB, WMI, SSH, HTTP, HTTPS, Exchange, MSSQL, FTP, RDP) and methods to quickly obtain target network live host IPs, computer names, workgroups, shared resources, MAC addresses, OS versions, websites, subdomains, middleware, open services, routers, switches, databases, printers, and more. It detects 16+ high-risk vulnerabilities including Cisco, Zimbra, Exchange, DrayTek, MS17010, SMBGhost, Weblogic, ActiveMQ, Tomcat, Struts2 series, Printer, etc. Password auditing covers 25+ types including databases (MySQL, Oracle, MSSQL), FTP, SSH, VNC, Windows (LDAP, SMB/IPC, NBT, WMI, SmbHash, WmiHash, Winrm), BasicAuth, Tomcat, Weblogic, Rar, etc. Remote command execution includes smbexec, wmiexe, psexec, atexec, sshexec, webshell. The web fingerprint identification module can recognize 135+ items (web applications, middleware, script types, page types). Local privilege escalation includes 21+ methods such as SweetPotato, BadPotato, EfsPotato, BypassUAC. It is highly customizable with plugin POC support for .NET assemblies, DLLs (C#/Delphi/VC), PowerShell, etc. It supports calling any external programs or commands via configuration INI files. The EXP generator can create vulnerability POC/EXP to quickly extend scanning capabilities. Ladon supports Cobalt Strike plugin-based memory loading for fileless scanning in intranet lateral movement.
https://github.com/k8gege/Ladon/releases https://k8gege.org/Download
### 使用简单

虽然Ladon功能丰富多样,但使用却非常简单,任何人都能轻易上手<br>
只需一或两个参数就可用90%的功能,一个模块相当于一个新工具

### 运行环境

#### Windows

Ladon可在安装有.net 2.0及以上版本Win系统中使用(Win7后系统自带.net)<br>
如Cmd、PowerShell、远控Cmd、WebShell等,以及Cobalt Strike内存加载使用<br>
Ladon.ps1完美兼容Win7-Win11/2025 PowerShell,不看版本远程加载无文件渗透

#### 全平台LadonGo支持Linux、Mac、Arm、MIPS
全平台:Linux、MacOS、Windows、路由器、网络设备等OS系统<br>
https://github.com/k8gege/LadonGo

### 奇葩条件

实战并不那么顺利,有些内网转发后很卡或无法转发,只能将工具上传至目标<br>
有些马可能上传两三M的程序都要半天甚至根本传不了,PY的几十M就更别想了<br>
Ladon采用C#研发,程序体积很小500K左右,即便马不行也能上传500K程序吧<br>
还不行也可PowerShell远程内存加载,这点是PY或GO编译的大程序无法比拟的

### 宗旨

一条龙服务,为用户提供一个简单易用、功能丰富、高度灵活的扫描工具

### 特色

扫描流量小<br>
程序体积小<br>
功能丰富强大<br>
程序简单易用<br>
插件支持多种语言<br>
跨平台(Win/Kali/Ubuntu)等<br>
支持Cobalt Strike插件化<br>
支持PowerShell无文件渗透<br>
Exp生成器可一键生成Poc<br>
多版本适用各种环境

### 程序参数功能

1  支持指定IP扫描<br>
2  支持指定域名扫描<br>
3  支持指定机器名扫描<br>
4  支持指定C段扫描(ip/24)<br>
5  支持指定B段扫描(ip/16)<br>
6  支持指定A段扫描(ip/8)<br>
7  支持指定URL扫描<br>
8  支持批量IP扫描(ip.txt)<br>
9  支持批量C段扫描(ip24.txt)<br>
10 支持批量C段扫描(ipc.txt)<br>
11 支持批量B段扫描(ip16.txt)<br>
12 支持批量URL扫描(url.txt)<br>
13 支持批量域名扫描(domain.txt)<br>
14 支持批量机器名扫描(host.txt)<br>
15 支持批量国家段扫描(cidr.txt)<br>
16 支持批量字符串列表(str.txt)<br>
17 支持主机帐密列表(check.txt)<br>
18 支持用户密码列表(userpass.txt)<br>
19 支持指定范围C段扫描<br>
20 支持参数加载自定义DLL(仅限C#)<br>
21 支持参数加载自定义EXE(仅限C#)<br>
22 支持参数加载自定义INI配置文件<br>
23 支持参数加载自定义PowerShell<br>
24 支持自定义程序(系统命令或第三方程序即任意语言开发的程序或脚本)<br>
25 插件(支持多种语言C#/Delphi/Golang/Python/VC/PowerShell)<br>
26 支持Cobalt Strike(beacon命令行下扫描目标内网或跳板扫描外网目标)<br>
27 支持CIDR格式IP扫描,如100.64.0.0/10,192.168.1.1/20等<br>
28 INI配置支持自定义程序密码爆破<br>

### 简明使用教程

Ladon 简明使用教程 完整文档: http://k8gege.org/Ladon <br>
Excel模块功能文档: http://k8gege.org/Ladon/wiki.xlsx <br>
支持Cmd、Cobalt Strike、PowerShell等内存加载<br>
Windows版本: .Net、Cobalt Strike、PowerShell<br>
全系统版本:GO(全平台)、Python(理论上全平台)<br>
PS: Study方便本地学习使用,完整功能请使用CMD

### BypassEDR扫描

默认扫描速度很快,有些WAF或EDR防御很强<br>
设置几线程都有可能20分钟左右就不能扫了<br>
bypassEDR模拟人工访问,绕过速度检测策略<br>

扫描速度较慢,追求速度的愣头青不要使用<br>```Bash
Ladon 10.1.2.8/24 MS17010 bypassEDR
密码爆破相关模块暂不支持bypassEDR参数
例子:扫描目标10.1.2段是否存在MS17010漏洞
单线程:```Bash
Ladon 10.1.2.8/24 MS17010 t=1
80 threads:```Bash
Ladon noping 10.1.2.8/24 MS17010 t=80
Under high-intensity protection, set the scanning thread lower, F single thread
```Bash
Ladon 10.1.2.8/24 MS17010 f=1
### 002 Socks5 Proxy Scanning
Example: Using 8 threads to scan target segment 10.1.2 for MS17010 vulnerability<br>```Bash
Ladon noping 10.1.2.8/24 MS17010 t=8
详见:http://k8gege.org/Ladon/proxy.html
PS:代理工具不支持Socks5,所以必须加noping参数扫描
不管是Frp还是其它同类工具,最主要是Proxifier等工具不支持ICMP协议
因为Ladon默认先用ICMP探测存活后,才使用对应模块测试
所以代理环境下得禁ping扫描,系统ping使用的就是ICMP协议
CIDR格式:不只是/24/16/8(所有)```Bash Ladon 192.168.1.8/24 扫描模块 Ladon 192.168.1.8/16 扫描模块 Ladon 192.168.1.8/8 扫描模块
Letter format: only C segment, B segment, A segment, sorted in order.```Bash
Ladon 192.168.1.8/c 扫描模块
Ladon 192.168.1.8/b 扫描模块
Ladon 192.168.1.8/a 扫描模块
Ladon 192.168.1.50-192.168.1.200 ICMP
#### ICMP probe live hosts from 1.30 to 50.80```Bash
Ladon 192.168.1.30-192.168.50.80 ICMP
TXT格式
Ladon ip24.txt ICMP Ladon ipc.txt ICMP
##### 005 ICMP Batch Scan B-Segment List for Live Hosts```Bash
Ladon ip16.txt ICMP
Ladon cidr.txt ICMP
##### 007 ICMP Batch Scan for Domain Liveness```Bash
Ladon domain.txt ICMP
Ladon host.txt ICMP
##### 009 WhatCMS batch recognition of CMS, Banner, SSL certificate, title, can identify unknown CMS, routers, printers, network devices, cameras, etc.```Bash
Ladon 192.168.1.8 WhatCMS   扫描IP
Ladon 192.168.1.8/24 WhatCMS   扫描C段
Ladon 192.168.1.8/C WhatCMS   扫描C段
Ladon 192.168.1.8/B WhatCMS   扫描B段
Ladon 192.168.1.8/A WhatCMS   扫描A段
Ladon IP.TXT WhatCMS   扫描IP列表
Ladon IP24.TXT WhatCMS   扫描C段列表
Ladon IP16.TXT WhatCMS   扫描B段列表
Ladon cidr.TXT WhatCMS   扫描整个国家IP段列表
禁PING扫描<br>
Ladon noping 192.168.1.8 WhatCMS   扫描IP
Ladon noping 192.168.1.8/24 WhatCMS   扫描C段
Ladon url.txt DraytekPoc
##### 011 Batch Decrypt Base64 Passwords```Bash
Ladon str.txt DeBase64

