CVE-2024-8856
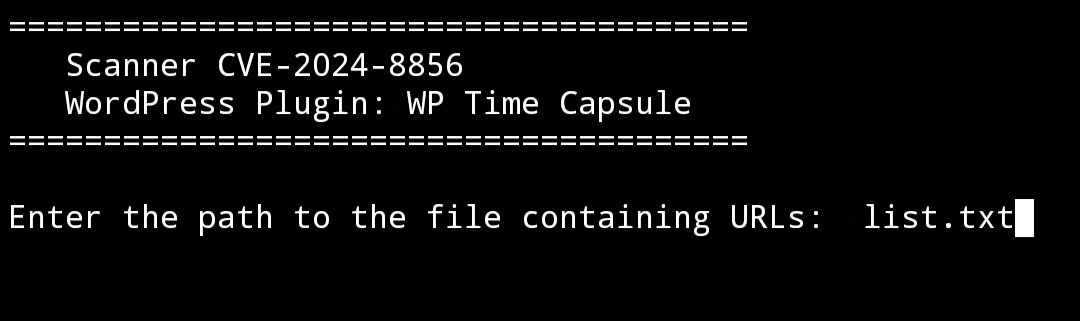
This tool scans WordPress websites for vulnerabilities in the WP Time Capsule plugin related to CVE-2024-8856.
It identifies plugin versions below "1.22.22" as vulnerable and logs results to "vuln.txt".
Simple and efficient, it helps security researchers and admins detect and address risks quickly.
Features
- Scans a list of URLs to detect vulnerabilities in the WP Time Capsule plugin related to CVE-2024-8856.
- Identifies plugin versions below 1.22.22 as vulnerable (e.g., 1.22.21, 1.22.20).
- Uses Python libraries such as "requests" to send HTTP requests and check for plugin versions.
- Supports multithreading to speed up the scanning process across multiple sites simultaneously.
- Displays scan results with the vulnerability status: vulnerable or not vulnerable based on the version.
- The found vulnerable sites are saved to a result file ("vuln.txt")
Buy Coffee :
- Bitcoin $: 14nXhmRiQx5joCXFTdR8ydm3T8et7MFDXC

How To Run?
- Download and install Python from the official Python website: https://www.python.org.
- Install the required modules using the command:
pip install requests.
- Run the script with:
python file.py.
- Provide a list of sites (e.g., url.txt) as input.
Disclaimer !!!
I have written the disclaimer on the cover of Jenderal92. You can check it HERE !!!
 jenderal92/cve-2024-8856

