 iaga-team/iaga-sentinel
Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a hash-chained append-log, and supports EU AI Act Article 12 record-keeping and Annex IV documentation.

The EU AI Act conformity evidence layer for AI agents.
Cryptographically signed, replay-verifiable evidence of every action an agent routes through it, structured to support AI Act Article 12 record-keeping and Annex IV documentation.


Documentation · Setup in one prompt · Quickstart · Autonomous agent setup · Community vs Enterprise · Who we are · License
Built in the EU by three founders (French, German, Italian) and research-validated, not marketing-validated: peer-reviewed at AISEC 2026, Marrakech.
Paste this to your coding agent. It reads AGENTS.md and does the rest — builds the binary, derives your rules, asks you to approve them, starts the server, connects itself over MCP, and makes two live calls you watch land in the dashboard.
copy the repo here https://github.com/IAGA-TEAM/IAGA-Sentinel and follow the AGENTS.MD STEP BY STEP
It stops and waits for you twice: once to approve the rules it will enforce, once to confirm you can see the calls.
Getting out is as easy as getting in, and it shows you what it will do before it does it.
.\scripts\uninstall.ps1          # dry run: lists exactly what it would remove
.\scripts\uninstall.ps1 -Yes     # remove the install
The .sh twin takes --yes. It refuses to run while a governed process
is still up, and it keeps your signing key unless you explicitly ask otherwise —
delete that and every receipt you have ever exported becomes permanently unverifiable.
There is no account to close, no daemon left behind, and no telemetry: the whole install is
a database, a policy file and a key you own.
AI agents touch the shell, the filesystem, databases, third-party APIs, and secrets. When a regulator, an auditor, or your own DPO asks you to prove what an agent did, and to prove the record was not altered after the fact, most teams have nothing to show. IAGA Sentinel produces that proof: it sits next to your agent stack (HTTP sidecar, MCP proxy, or iaga run) and turns every governance verdict into an Ed25519-signed receipt linked into a hash-chained append-log, verifiable offline, with reproducible verdicts (deterministic under fixed risk weights) and replay-based drift detection. The record is structured to support EU AI Act Article 12 record-keeping and to help produce the Annex IV technical documentation a high-risk system needs.
[!IMPORTANT] IAGA Sentinel governs in the loop and seals hard. Verdicts are computed before an action proceeds; with
iaga runa blocked process never starts and an allowed one is confined directly — secrets scrubbed from its environment, no core dumps, no privilege escalation, reaped with its parent. The signed evidence and the offline replay are real and verifiable now, from a clean checkout. Kernel-level confinement (eBPF/LSM syscall and network mediation) is the Enterprise tier and is not in this open build:iaga kernel statusreports the posture honestly, and every receipt carriesis_authoritative: false. We do not market enforcement we do not provide.
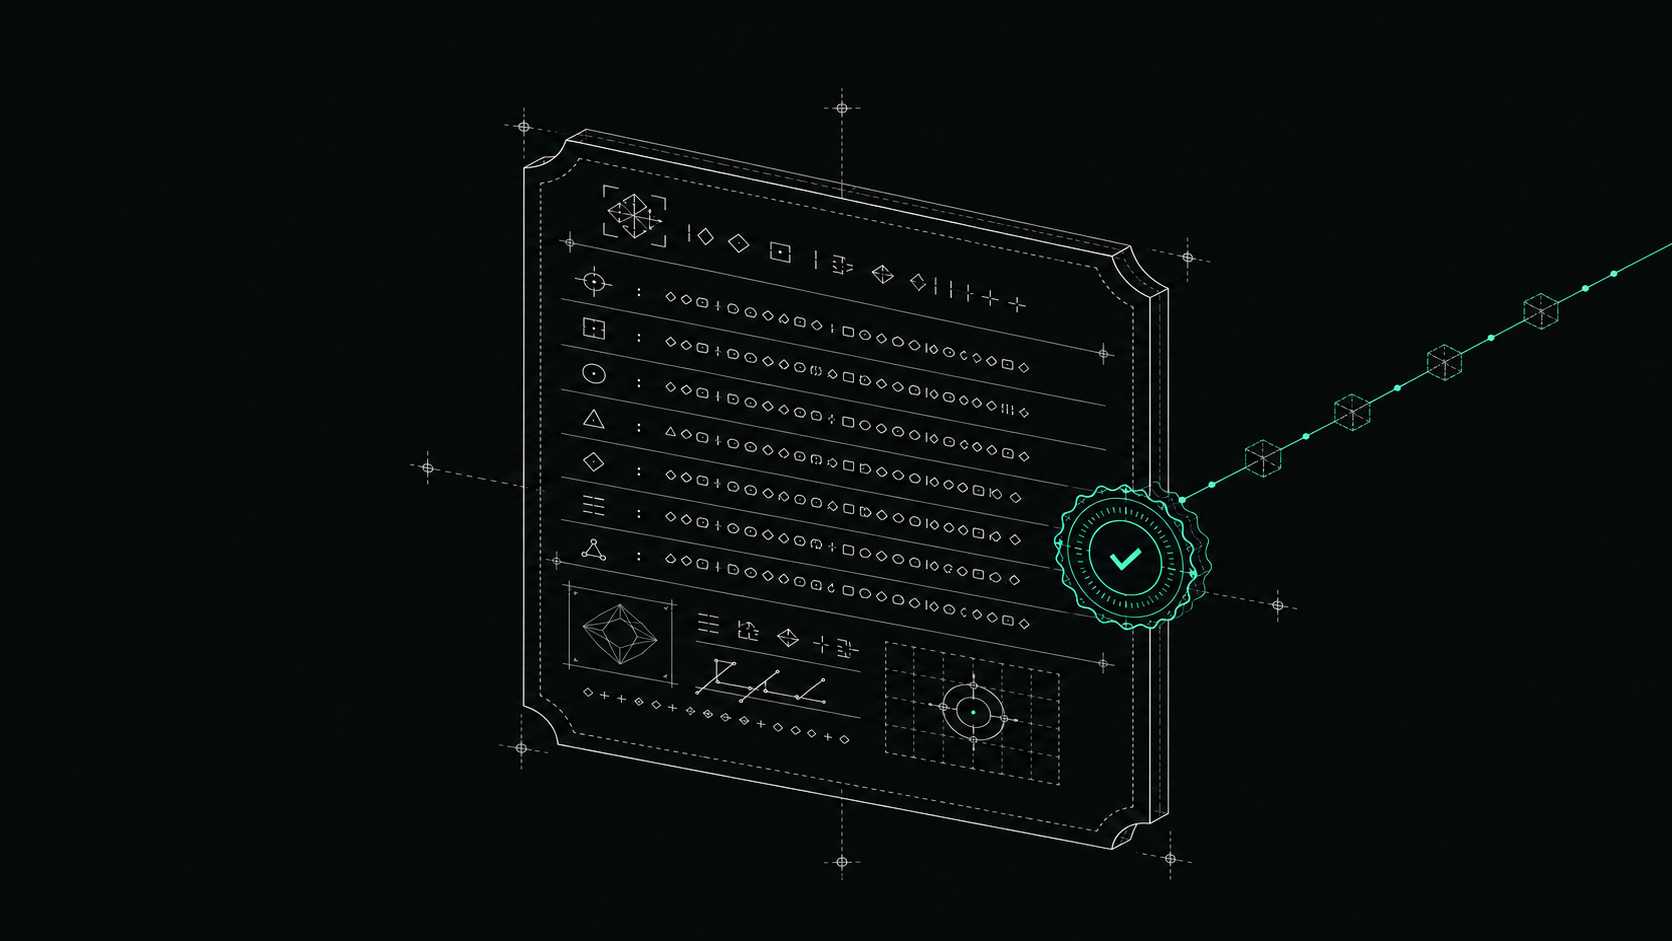
Every governance verdict becomes a signed receipt, sealed with Ed25519 and linked into the hash-chained log.
What makes it different:
iaga-verify binary: no server, no network, no trust in IAGA required.is_authoritative: false), not buried in a footnote.Fastest look. Build the image from the shipped Dockerfile and run it with demo data already
seeded — no Rust toolchain on your machine, the builder stage carries it:
docker build -t iaga-sentinel:local .
docker run -p 127.0.0.1:4010:4010 -e IAGA_SENTINEL_OPEN_MODE=true \
  iaga-sentinel:local serve --seed-demo
# Open mode makes every unauthenticated caller an implicit ADMIN while no API key exists, so
# publish on loopback only — otherwise /v1/audit, the signed decision log, is readable by the
# whole LAN. Pin the publish, not IAGA_SENTINEL_HOST: binding the container to its own loopback
# would make the published port unreachable.
[!NOTE] There is no published image yet.
ghcr.io/iaga-team/iaga-sentineldoes not resolve: the package is private and the tag push fails at manifest time with a403, for organisation-side reasons documented in.github/workflows/docker.yml. Until that is settled, build locally as above, or usecargo installbelow. The last publicly published image isghcr.io/edoardobambini/iaga-sentinel:v1.8.1— seven releases behind (1.9.0, 1.9.1, 1.9.2, 2.0.0, 2.0.1, 2.0.2, 2.1.0); do not evaluate this release with it.
The operator dashboard is at http://localhost:4010/. Send it an agent action and it decides, scores the risk, and mints a signed receipt:
