
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
snmpwn — An SNMPv3 User Enumerator and Attack tool | Kitploit

Tools/GitHubGitHub/hatlord/snmpwn
Password AttacksInformation GatheringNetwork SecurityPenetration Testing
GitHubhatlord/snmpwn

snmpwn

An SNMPv3 User Enumerator and Attack tool

View Repository
26844306 years agoReviewed by Kitploit
Share

SNMPwn is an SNMPv3 user enumerator and attack tool. It is a legitimate security tool designed to be used by security professionals and penetration testers against hosts you have permission to test. It takes advantage of the fact that SNMPv3 systems will respond with "Unknown user name" when an SNMP user does not exist, allowing us to cycle through large lists of users to find the ones that do.

What does it do?

  • Checks that the hosts you provide are responding to SNMP requests.
  • Enumerates SNMP users by testing each in the list you provide. Think user brute forcing.
  • Attacks the server with the enumerated accounts and your list of passwords and encryption passwords. No need to attack the entire list of users, only live accounts.
  • Attacks all the different protocol types:
    • No auth no encryption (noauth)
    • Authentication, no encryption (authnopriv)
    • Authentication and encryption (All types supported, MD5, SHA, DES, AES) - (authpriv)

Notes for usage

Built for and tested on Kali Linux 2.x rolling. Should work on any Linux platform but does not work currently on Mac OSX, but will when I get around to it. This is due to the stdout messages for snmpwalk on OSX being different. This script basically wraps snmpwalk. The version of snmpwalk I used was 5.7.3.

Install

git clone https://github.com/hatlord/snmpwn.git
cd snmpwn
gem install bundler  
bundle install
./snmpwn.rb

Built for Ruby 2.3.x. Older versions of Ruby may work, but older than 1.9 may not.

Run

You need to provide the script a list of users, a hosts list, a password list and an encryption password list. Basic users.txt and passwords.txt files are included. You could use passwords.txt for your encryption list also. I would recommend generating one specific to the organisation you are pen testing. The command line options are available via --help as always and should be clear enough. The only ones I would make specific comment on are: --showfail - This will show you all password attack attempts, both successful and failed. It clutters the console output though, so if you do not choose this option you will get a spinning progress indicator instead. --timeout - This is the timeout in milliseconds for the command response, which in this case is snmpwalk. It is set to 0.3 by default, which is 300 milliseconds. If you are testing hosts across a slow link you are going to want to extend this. I wouldn't personally go lower than 300 or results may become unreliable.

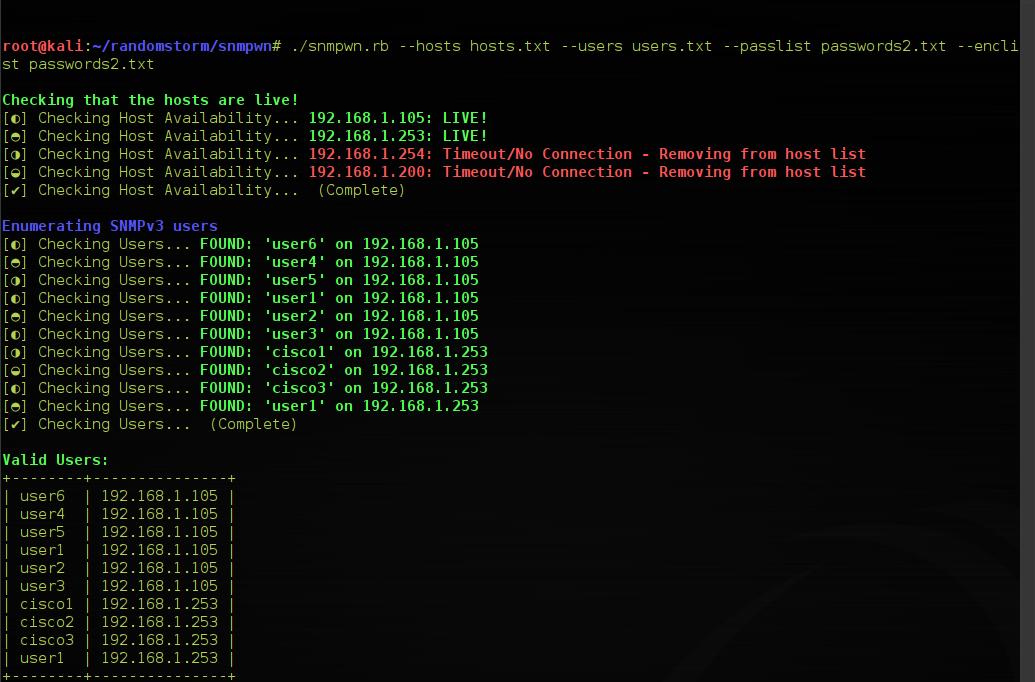
./snmpwn.rb --hosts hosts.txt --users users.txt --passlist passwords.txt --enclist passwords.txt
Screengrabs

User Enumeration

User Enumeration

Password Attacks

Password Attacks

Summary of results

Summary

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →