
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
HackSysExtremeVulnerableDriver — HackSys Extreme Vulnerable Driver (HEVD) - Windows & Linux | Kitploit
Tools/GitHubGitHub/hacksysteam/hacksysextremevulnerabledriver
Vulnerability AnalysisLearning & EducationBinary ExploitationLabs & Practice
GitHubhacksysteam/hacksysextremevulnerabledriver

HackSysExtremeVulnerableDriver

HackSys Extreme Vulnerable Driver (HEVD) - Windows & Linux

View Repository
Website
3.1k584801 year agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

HackSys Extreme Vulnerable Driver

           ooooo   ooooo oooooooooooo oooooo     oooo oooooooooo.   
           `888'   `888' `888'     `8  `888.     .8'  `888'   `Y8b  
            888     888   888           `888.   .8'    888      888 
            888ooooo888   888oooo8       `888. .8'     888      888 
            888     888   888    "        `888.8'      888      888 
            888     888   888       o      `888'       888     d88' 
           o888o   o888o o888ooooood8       `8'       o888bood8P'   

Black Hat Arsenal Appveyor Build Status GitHub all Releases Twitter Follow Mastodon Follow Discord Server

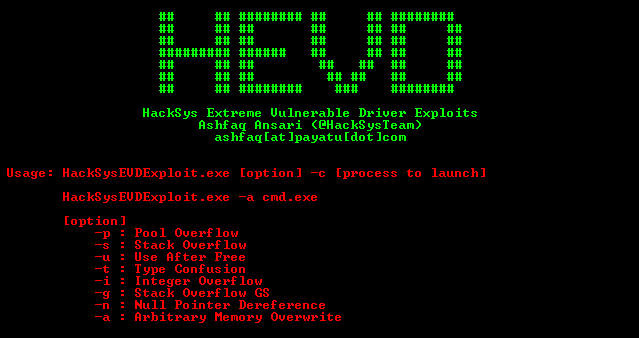
The HackSys Extreme Vulnerable Driver (HEVD) is a Windows Kernel driver that is intentionally vulnerable. It has been developed for security researchers and enthusiasts to improve their skills in kernel-level exploitation.

HEVD offers a range of vulnerabilities, from simple stack buffer overflows to more complex issues such as use-after-free, pool buffer overflows, and race conditions. This allows researchers to explore exploitation techniques for each implemented vulnerability.

Black Hat Arsenal 2016

  • Presentation
  • White Paper

Blog Post

  • http://www.payatu.com/hacksys-extreme-vulnerable-driver/

External Exploits

  • https://github.com/wetw0rk/Exploit-Development/tree/master/HEVD-Exploits
  • https://github.com/sam-b/HackSysDriverExploits
  • https://github.com/sizzop/HEVD-Exploits
  • https://github.com/badd1e/bug-free-adventure
  • https://github.com/FuzzySecurity/HackSysTeam-PSKernelPwn
  • https://github.com/theevilbit/exploits/tree/master/HEVD
  • https://github.com/GradiusX/HEVD-Python-Solutions
  • http://pastebin.com/ALKdpDsF
  • https://github.com/Cn33liz/HSEVD-StackOverflow
  • https://github.com/Cn33liz/HSEVD-StackOverflowX64
  • https://github.com/Cn33liz/HSEVD-StackCookieBypass
  • https://github.com/Cn33liz/HSEVD-ArbitraryOverwrite
  • https://github.com/Cn33liz/HSEVD-ArbitraryOverwriteGDI
  • https://github.com/Cn33liz/HSEVD-StackOverflowGDI
  • https://github.com/Cn33liz/HSEVD-ArbitraryOverwriteLowIL
  • https://github.com/mgeeky/HEVD_Kernel_Exploit
  • https://github.com/tekwizz123/HEVD-Exploit-Solutions
  • https://github.com/FULLSHADE/Windows-Kernel-Exploitation-HEVD
  • https://github.com/w4fz5uck5/3XPL01t5/tree/master/OSEE_Training

External Blog Posts

  • https://wetw0rk.github.io/posts/0x00-introduction-to-windows-kernel-exploitation/
  • https://wetw0rk.github.io/posts/0x00-introducci%C3%B3n-a-windows-kernel-explotaci%C3%B3n/
  • https://wetw0rk.github.io/posts/0x01-killing-windows-kernel-mitigations/
  • https://wetw0rk.github.io/posts/0x01-mat%C3%A1ndo-windows-kernel-mitigaciones/
  • https://wetw0rk.github.io/posts/0x02-introduction-to-windows-kernel-uafs/
  • https://wetw0rk.github.io/posts/0x02-introducci%C3%B3n-a-windows-kernel-uafs/
  • https://wetw0rk.github.io/posts/0x03-approaching-the-modern-windows-kernel-heap/
  • https://wetw0rk.github.io/posts/0x03-acerc%C3%A1ndose-al-heap-moderno-del-windows-kernel/
  • https://wetw0rk.github.io/posts/0x04-writing-what-where-in-the-kernel/
  • https://wetw0rk.github.io/posts/0x04-escribiendo-que-donde-en-el-kernel/
  • https://wetw0rk.github.io/posts/0x05-introduction-to-windows-kernel-type-confusion-vulnerabilities/
  • https://wetw0rk.github.io/posts/0x05-introducci%C3%B3n-a-windows-kernel-type-confusion-vulnerabilidades/
  • https://wetw0rk.github.io/posts/0x06-approaching-modern-windows-kernel-type-confusions/
  • https://wetw0rk.github.io/posts/0x06-acerc%C3%A1ndose-a-windows-kernel-type-confusions-modernos/
  • https://wetw0rk.github.io/posts/0x07-introduction-to-windows-kernel-race-conditions/
  • https://wetw0rk.github.io/posts/0x07-introducci%C3%B3n-a-windows-kernel-race-conditions/
  • https://wetw0rk.github.io/posts/0x08-modern-windows-kernel-race-conditions/
  • https://wetw0rk.github.io/posts/0x08-race-conditions-moderno-del-windows-kernel/
  • https://wetw0rk.github.io/posts/0x09-return-of-the-stack-overflow/
  • https://wetw0rk.github.io/posts/0x09-el-regreso-del-stack-overflow/
  • http://niiconsulting.com/checkmate/2016/01/windows-kernel-exploitation/
  • http://samdb.xyz/2016/01/16/intro_to_kernel_exploitation_part_0.html
  • http://samdb.xyz/2016/01/17/intro_to_kernel_exploitation_part_1.html
  • http://samdb.xyz/2016/01/18/intro_to_kernel_exploitation_part_2.html
  • http://samdb.xyz/2017/06/22/intro_to_kernel_exploitation_part_3.html
  • https://sizzop.github.io/2016/07/05/kernel-hacking-with-hevd-part-1.html
  • https://sizzop.github.io/2016/07/06/kernel-hacking-with-hevd-part-2.html
  • https://sizzop.github.io/2016/07/07/kernel-hacking-with-hevd-part-3.html
  • https://sizzop.github.io/2016/07/08/kernel-hacking-with-hevd-part-4.html
  • https://www.fuzzysecurity.com/tutorials/expDev/14.html
  • https://www.fuzzysecurity.com/tutorials/expDev/15.html
  • https://www.fuzzysecurity.com/tutorials/expDev/16.html
  • https://www.fuzzysecurity.com/tutorials/expDev/17.html
  • https://www.fuzzysecurity.com/tutorials/expDev/18.html
  • https://www.fuzzysecurity.com/tutorials/expDev/19.html
  • https://www.fuzzysecurity.com/tutorials/expDev/20.html
  • http://dokydoky.tistory.com/445
  • https://hshrzd.wordpress.com/2017/05/28/starting-with-windows-kernel-exploitation-part-1-setting-up-the-lab/
  • https://hshrzd.wordpress.com/2017/06/05/starting-with-windows-kernel-exploitation-part-2/
  • https://hshrzd.wordpress.com/2017/06/22/starting-with-windows-kernel-exploitation-part-3-stealing-the-access-token/
  • https://osandamalith.com/2017/04/05/windows-kernel-exploitation-stack-overflow/
  • https://osandamalith.com/2017/06/14/windows-kernel-exploitation-arbitrary-overwrite/
  • https://osandamalith.com/2017/06/22/windows-kernel-exploitation-null-pointer-dereference/
  • http://dali-mrabet1.rhcloud.com/windows-kernel-exploitation-arbitrary-memory-overwrite-hevd-challenges/
  • https://blahcat.github.io/2017/08/31/arbitrary-write-primitive-in-windows-kernel-hevd/
  • https://klue.github.io/blog/2017/09/hevd_stack_gs/
  • https://glennmcgui.re/introduction-to-windows-kernel-exploitation-pt-1/
  • https://glennmcgui.re/introduction-to-windows-kernel-driver-exploitation-pt-2/
  • https://kristal-g.github.io/2021/02/07/HEVD_StackOverflowGS_Windows_10_RS5_x64.html
  • https://kristal-g.github.io/2021/02/20/HEVD_Type_Confusion_Windows_10_RS5_x64.html
  • https://wafzsucks.medium.com/hacksys-extreme-vulnerable-driver-arbitrary-write-null-new-solution-7d45bfe6d116
  • https://wafzsucks.medium.com/how-a-simple-k-typeconfusion-took-me-3-months-long-to-create-a-exploit-f643c94d445f
  • https://mdanilor.github.io/posts/hevd-0/
  • https://mdanilor.github.io/posts/hevd-1/
  • https://mdanilor.github.io/posts/hevd-2/
  • https://mdanilor.github.io/posts/hevd-3/
  • https://mdanilor.github.io/posts/hevd-4/
Download Tool