 gyoisamurai/gyoithon
GyoiThon is a growing penetration test tool using Machine Learning.


Japanese page is here.
The new GyoiThon (version 0.0.4) can list up your subdomain facing on the internet. And if the subdomain is published as a Web service, then GyoiThon executes a health check that a non-destructive vulnerability assessment.
| Note |
|---|
| New function uses a Google custom search API. So if you use a new function, then you have to prepare a API key of Google Custom search. |
domain_list.csv is following:"Domain Name"
mbsd.jp
And you execute following command.
root@kali:~/GyoiThon# python3 gyoithon.py -i --domain_list
As a result, you get a list of sundomains associated with the specified domain.
| Index | Domain | Sub-Domain | IP Address | Access Status (http) | Location (http) | Access Status (https) | Location (https) | Whois records |
|---|---|---|---|---|---|---|---|---|
| 1 | mbsd.jp | mbsd.jp | ['40.115.251.148'] | 301 | https://www.mbsd.jp/ | 301 | https://www.mbsd.jp/ | *** |
| 2 | mbsd.jp | www.mbsd.jp | ['40.115.251.148'] | 301 | https://www.mbsd.jp/ | 200 | - | - |
| 3 | mbsd.jp | www2.mbsd.jp | ['40.115.251.148'] | 301 | https://www.mbsd.jp/ | 200 | - | - |
root@kali:~/GyoiThon# python3 gyoithon.py -i --domain_list --through_health_check --safety
As a result, you get a list of subdomains and assessment report.
| Index | Domain | Sub-Domain | IP Address | Access Status (http) | Location (http) | Access Status (https) | Location (https) | Whois records | Assessment results |
|---|---|---|---|---|---|---|---|---|---|
| 1 | mbsd.jp | mbsd.jp | ['40.115.251.148'] | 301 | https://www.mbsd.jp/ | 301 | https://www.mbsd.jp/ | *** | *** |
| 2 | mbsd.jp | www.mbsd.jp | ['40.115.251.148'] | 301 | https://www.mbsd.jp/ | 200 | - | - | *** |
| 3 | mbsd.jp | www2.mbsd.jp | ['40.115.251.148'] | 301 | https://www.mbsd.jp/ | 200 | - | - | *** |
GyoiThon is Intelligence Gathering tool for Web Server.
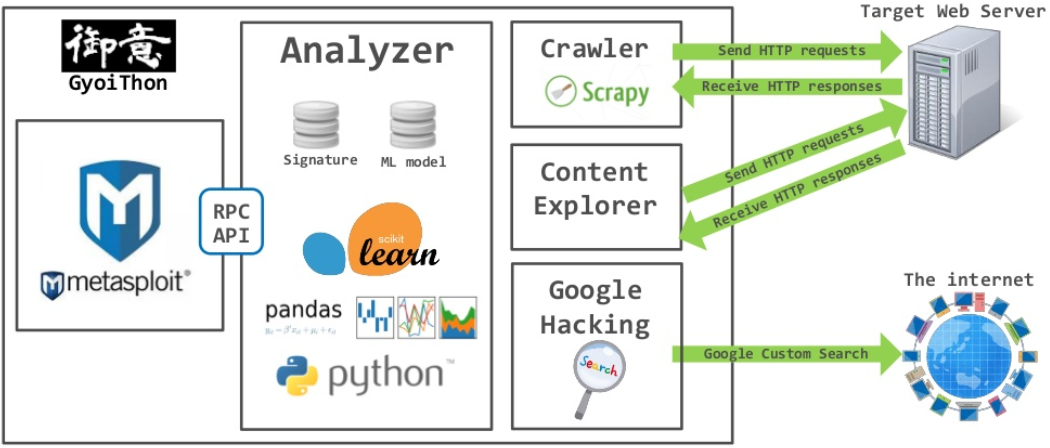
GyoiThon execute remote access to target Web server and identifies product operated on the server such as CMS, Web server software, Framework, Programming Language etc,. And, it can execute exploit modules to identified products using Metasploit. GyoiThon fully automatically execute above action.
GyoiThon's main features are following.
Remote access/Fully automatic
GyoiThon can fully automatically gather the information of target Web server using only remote access. You only execute GyoiThon once for your operation.
Non-destructive test
GyoiThon can gather information of target Web server using only normally access.
But, when you use a part of option, GyoiThon execute abnormally access such as sending exploit modules.
Gathering various information
GyoiThon has various intelligence gathering engines such as Web crawler, Google Custom Search API, Censys, explorer of default contents, examination of cloud services etc,. By analyze gathered information using strings pattern matching and machine learning, GyoiThon can identify product/version/CVE number operated on the target web server, unnecceary html comments/debug messages, login page etc,.
Examination of real vulnerability
GyoiThon can execute exploit modules to identified products using Metasploit.
As a result, it can examine real vulnerability of target web server.

| Note |
|---|
| If you are interested, please use them in an environment under your control and at your own risk. |
root@kali:~# git clone https://github.com/gyoisamurai/GyoiThon.git
root@kali:~# apt-get update
root@kali:~# apt-get install python3-pip
root@kali:~# cd GyoiThon
root@kali:~/GyoiThon# pip3 install -r requirements.txt
root@kali:~/GyoiThon# apt install python3-tk
config.ini.By using default mode without option and combination of several options, GyoiThon can gather various information of target web server.
usage:
    .\gyoithon.py [-s] [-m] [-g] [-e] [-c] [-p] [-l --log_path=<path>] [--no-update-vulndb]
    .\gyoithon.py [-d --category=<category> --vendor=<vendor> --package=<package>]
    .\gyoithon.py [-i]
    .\gyoithon.py -h | --help
options:
    -s   Optional : Examine cloud service.
    -m   Optional : Analyze HTTP response for identify product/version using Machine Learning.
    -g   Optional : Google Custom Search for identify product/version.
    -e   Optional : Explore default path of product.
    -c   Optional : Discover open ports and wrong ssl server certification using Censys.
    -p   Optional : Execute exploit module using Metasploit.
    -l   Optional : Analyze log based HTTP response for identify product/version.
    -d   Optional : Development of signature and train data.
    -i   Optional : Explore relevant FQDN with the target FQDN.
    -h --help     Show this help message and exit.
host.txt.host.txt.protocol FQDN(or IP address) Port Crawling_root_path.https gyoithon.example.com 443 /
If you want to indicate multiple target information, you have to write below.
https gyoithon.example.com 443 /
http 192.168.220.129 80 /vicnum/
https www.example.com 443 /catalog/
| Note |
|---|
You insert / at the beginning and end of Root Path. |
