 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API keys, .env and config files and more

A GitHub Action that analyses your source code for secrets, credentials, API keys, server and database hostnames/URLS, and a lot more! When you add this to GitHub Actions we will analyze your source code to make sure there is no sensitive data in your commit. See below for the specific types of credentials and files we scan for.
name: Example SecureStack Secrets Analysis GitHub Action
on: push
jobs:
  security:
    runs-on: ubuntu-latest
    steps:
      - name: Checkout repo for running secrets analysis within workflow
        id: checkout
        uses: actions/[email protected]
        with:
          fetch-depth: 0
      - name: Secrets Analysis Step
        id: secrets
        uses: SecureStackCo/[email protected]
        with:
          securestack_api_key: ${{ secrets.SECURESTACK_API_KEY }}
          securestack_app_id: ${{ secrets.SECURESTACK_APP_ID }}
          severity: critical
          flags: '-d 1'
NOTE - to understand possible values for the action input flags, run the SecureStack cli locally:
$ bloodhound-cli code --help
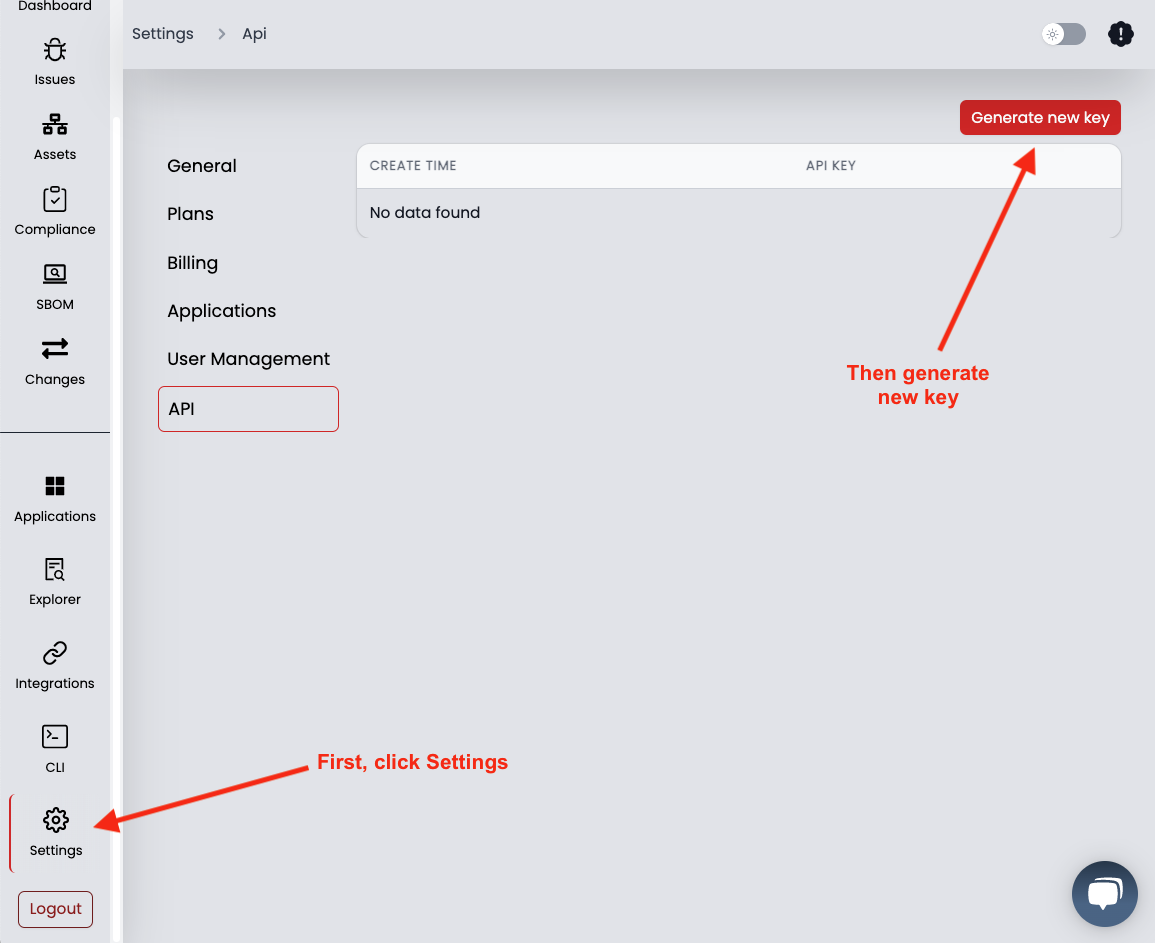

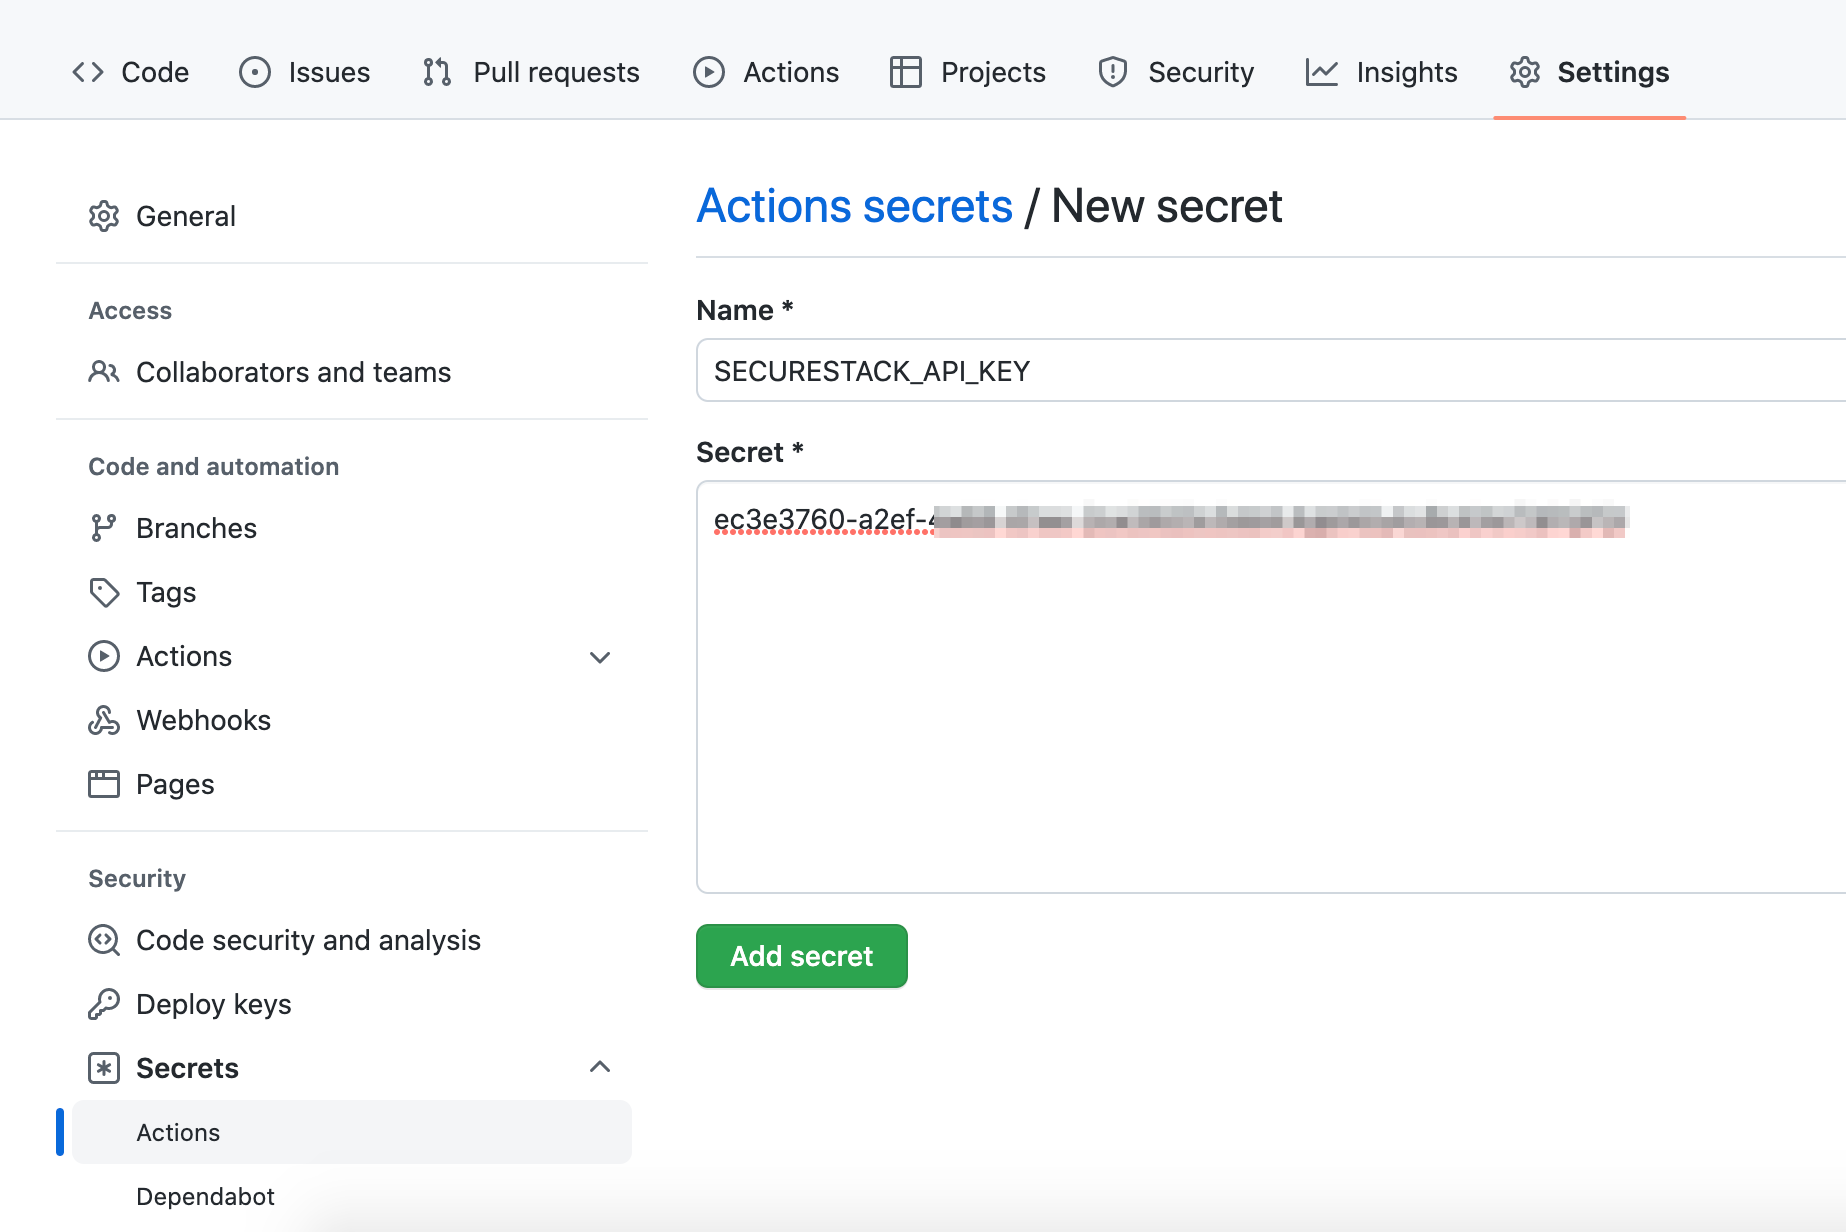
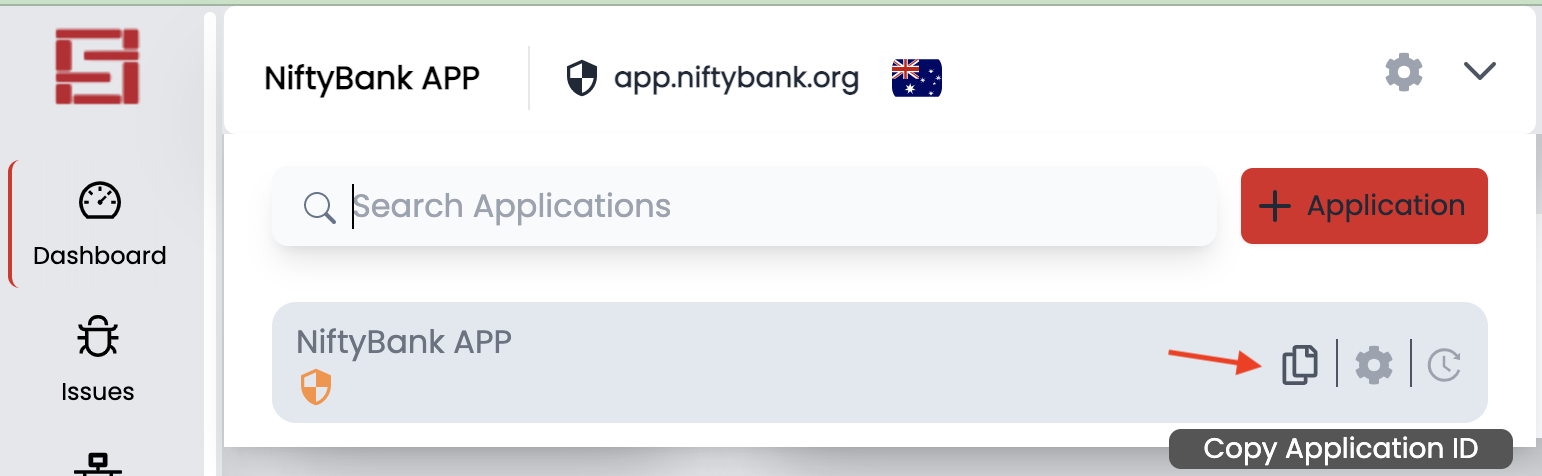


You can view the analysis output right in the GitHub Action workflow output
You can run a local secrets analysis with our bloodhound-cli :
bloodhound-cli code -s -d 1 -a <app_id>
You can interact with the analysis output in the SecureStack SaaS 
Coming soon!
Made with 💜 by SecureStack
